 boredhackerblog/teamcity-cve-2026-63077-pcap
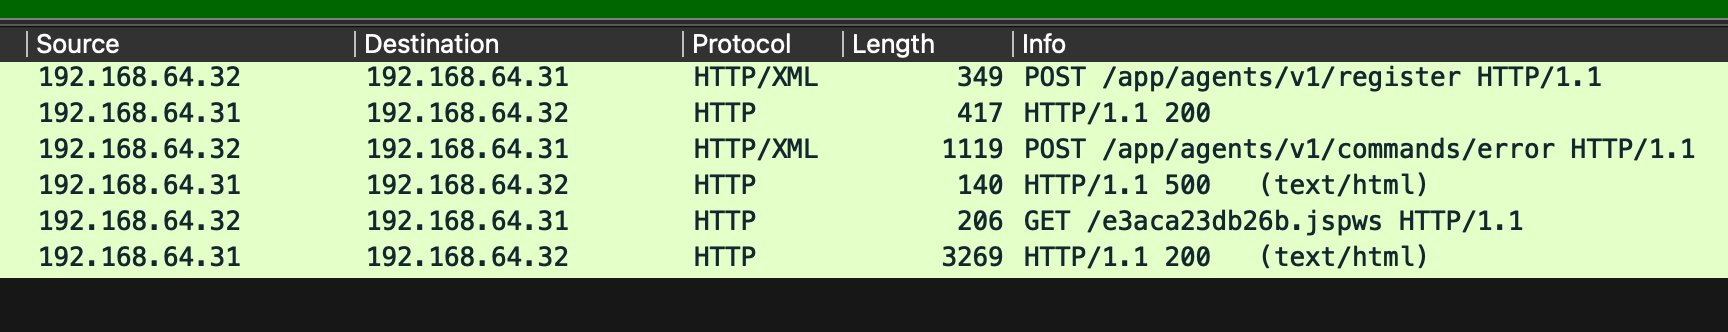
teamcity teamcity-CVE-2026-63077 Ausnutzung pcap

teamcity teamcity-CVE-2026-63077 Ausnutzung pcap
info: https://blog.jetbrains.com/teamcity/2026/07/cve-2026-63077/
https://www.rapid7.com/blog/post/ra-unauthenticated-rce-in-jetbrains-teamcity-cve-2026-63077/
Ziel: teamcity server 2025.11.3 (docker) 192.168.64.31 Port 8111
Exploit: https://github.com/sfewer-r7/CVE-2026-63077 - ausgeführt von 192.168.64.32 mit Befehl zum curl webhook.site
pcap könnte nützlich sein zum Testen von Suricata-Regeln.