Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Einreichen
ToolsExploitsBlog
Einreichen

Hacking-, PenTest- und Cybersicherheits-Tools für Ihr Sicherheitsarsenal!

Kitploit ist ein Verzeichnis von Hacking-, Cybersicherheits- und Pentesting-Tools. Entdecken Sie die neuesten Projekt-Updates, um Schwachstellen zu finden, Systeme zu analysieren, Tests zu automatisieren und Ihre Sicherheit zu stärken.

FeedsKontaktDatenschutz© 2026 Kitploit

Tool-Verzeichnis

Kategorien

Alle Kategorien anzeigen
Loading categories
CyberStrikeAI — The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next. | Kitploit
Tools/GitHubGitHub/aipentest/cyberstrikeai
Penetration Testing FrameworksVulnerability ScannersContainer SecurityExploit FrameworksForensicsWeb SecurityNetwork SecurityCloud SecurityCommand and ControlBinary AnalysisAI Security
7.7k1.5k153vor 8 TagenVon Kitploit geprüft
GitHub
aipentest/cyberstrikeai

CyberStrikeAI

The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.
Repository anzeigen

Beliebteste

Alle anzeigen →

Entdecken Sie die meistgenutzten Tools unserer Community.

Alle Tools erkunden

Durchsuchen Sie unsere Tool-Sammlung

Alle Tools anzeigen →
Teilen
Inhalt in der angeforderten Sprache nicht verfügbar. Englische Version wird angezeigt.
CyberStrikeAI Logo

CyberStrikeAI

中文 | English

The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

CyberStrikeAI connects planning, execution, human oversight, evidence, and replay in one auditable workspace. Built in Go, it combines Eino-powered agents, MCP-native tools, RAG knowledge, visual workflows, and attack-chain modeling and analysis for authorized security operations.

Start here: Quick start · Documentation · Security hardening

[!IMPORTANT] Use CyberStrikeAI only on systems you own or are explicitly authorized to test. For shared or production environments, review the security model and hardening guide before enabling high-risk tools, WebShell, or C2 capabilities.

Interface & Integration Preview

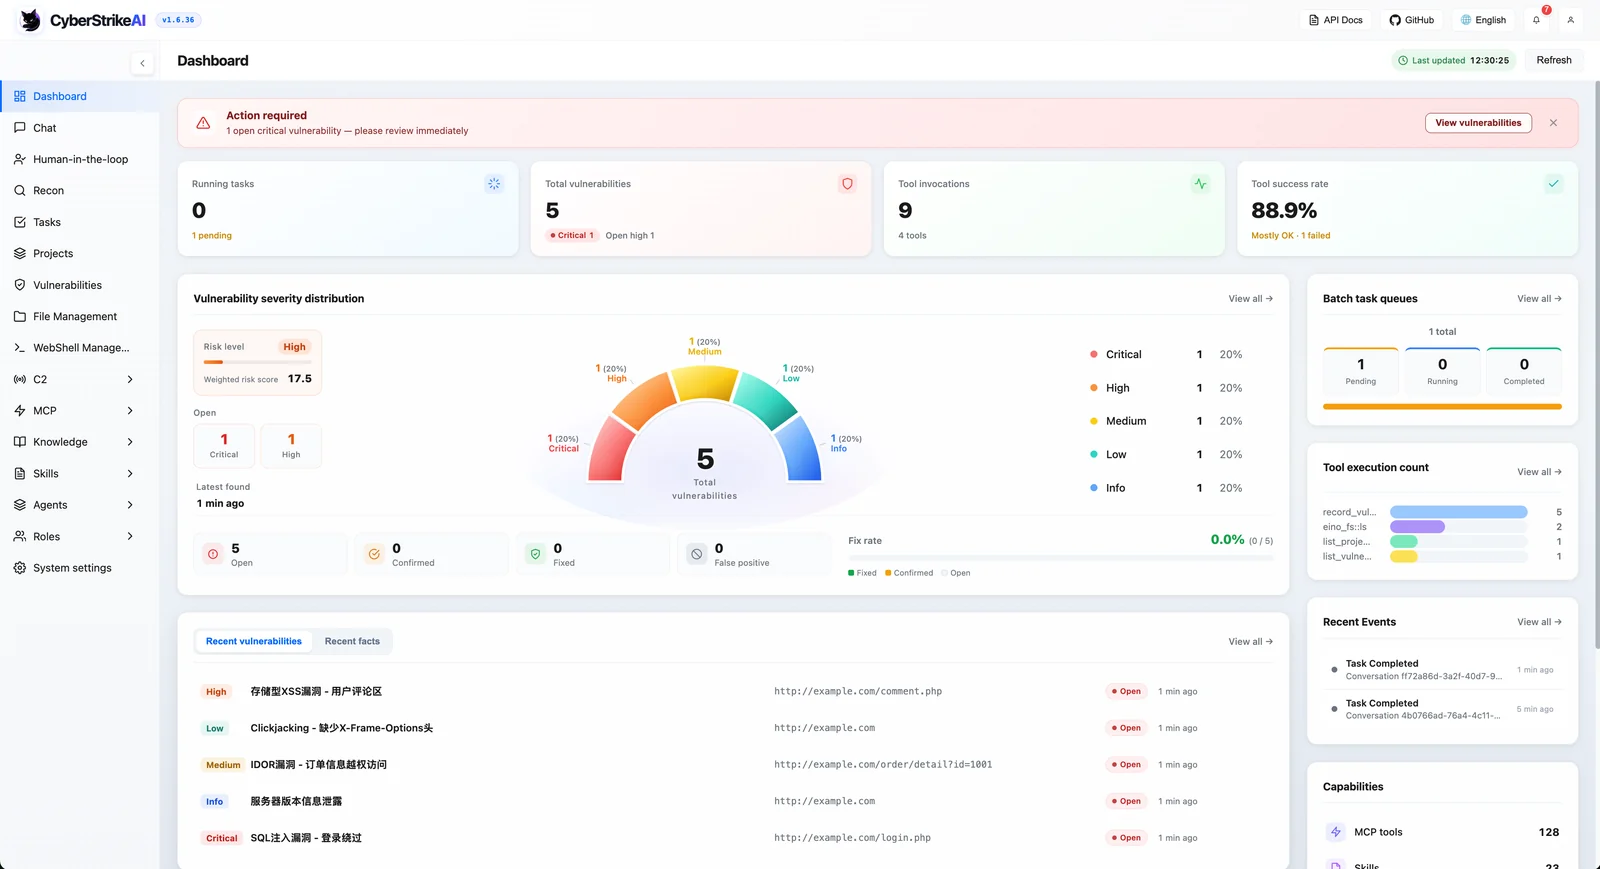
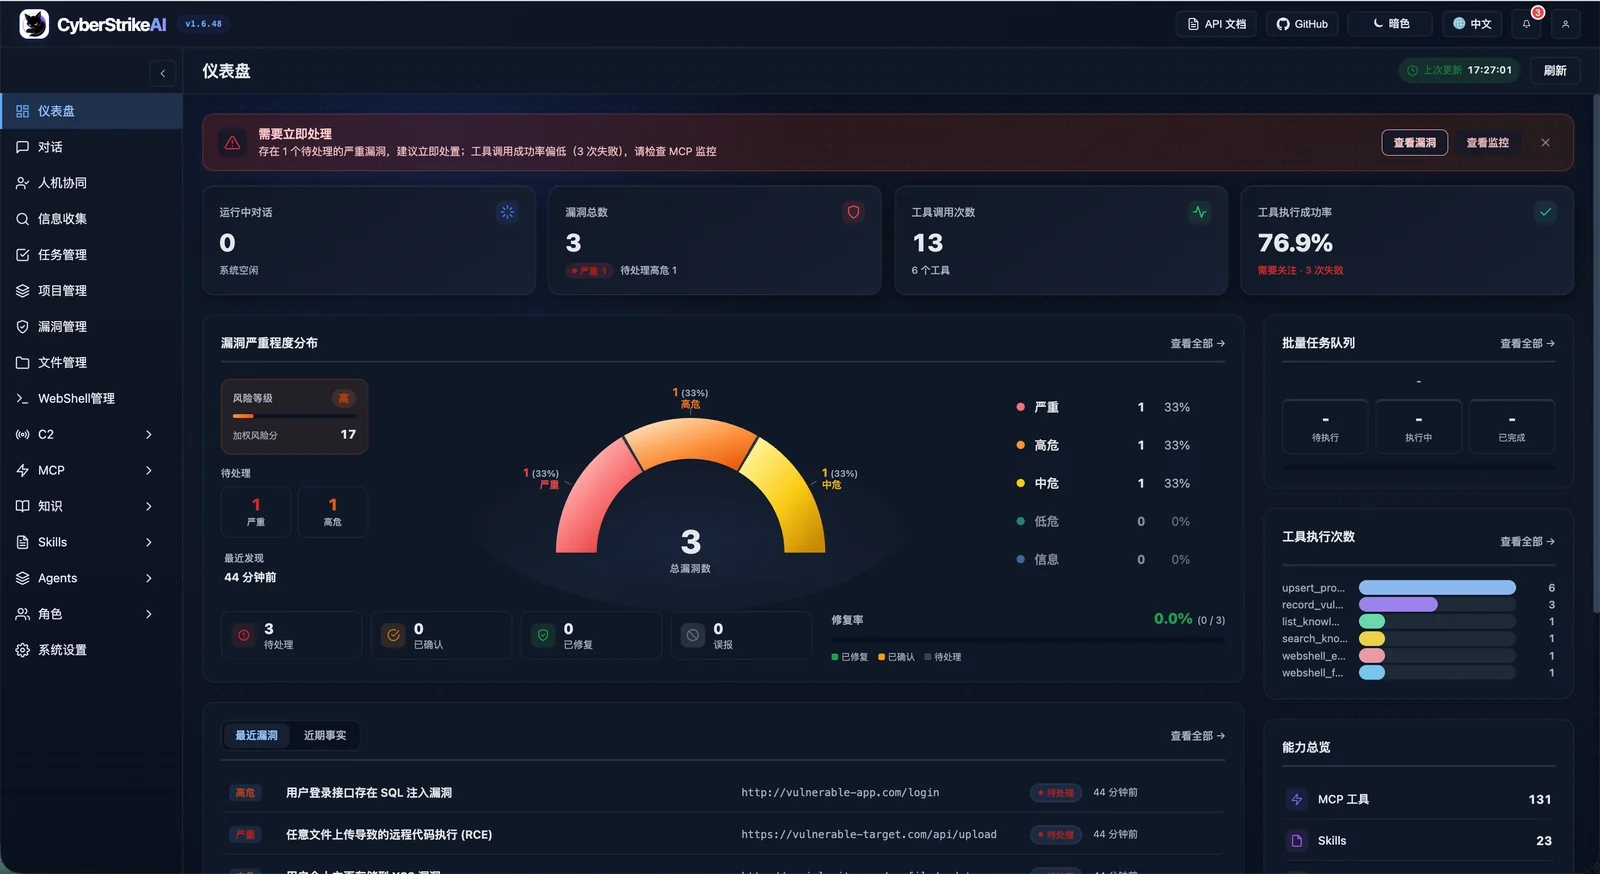
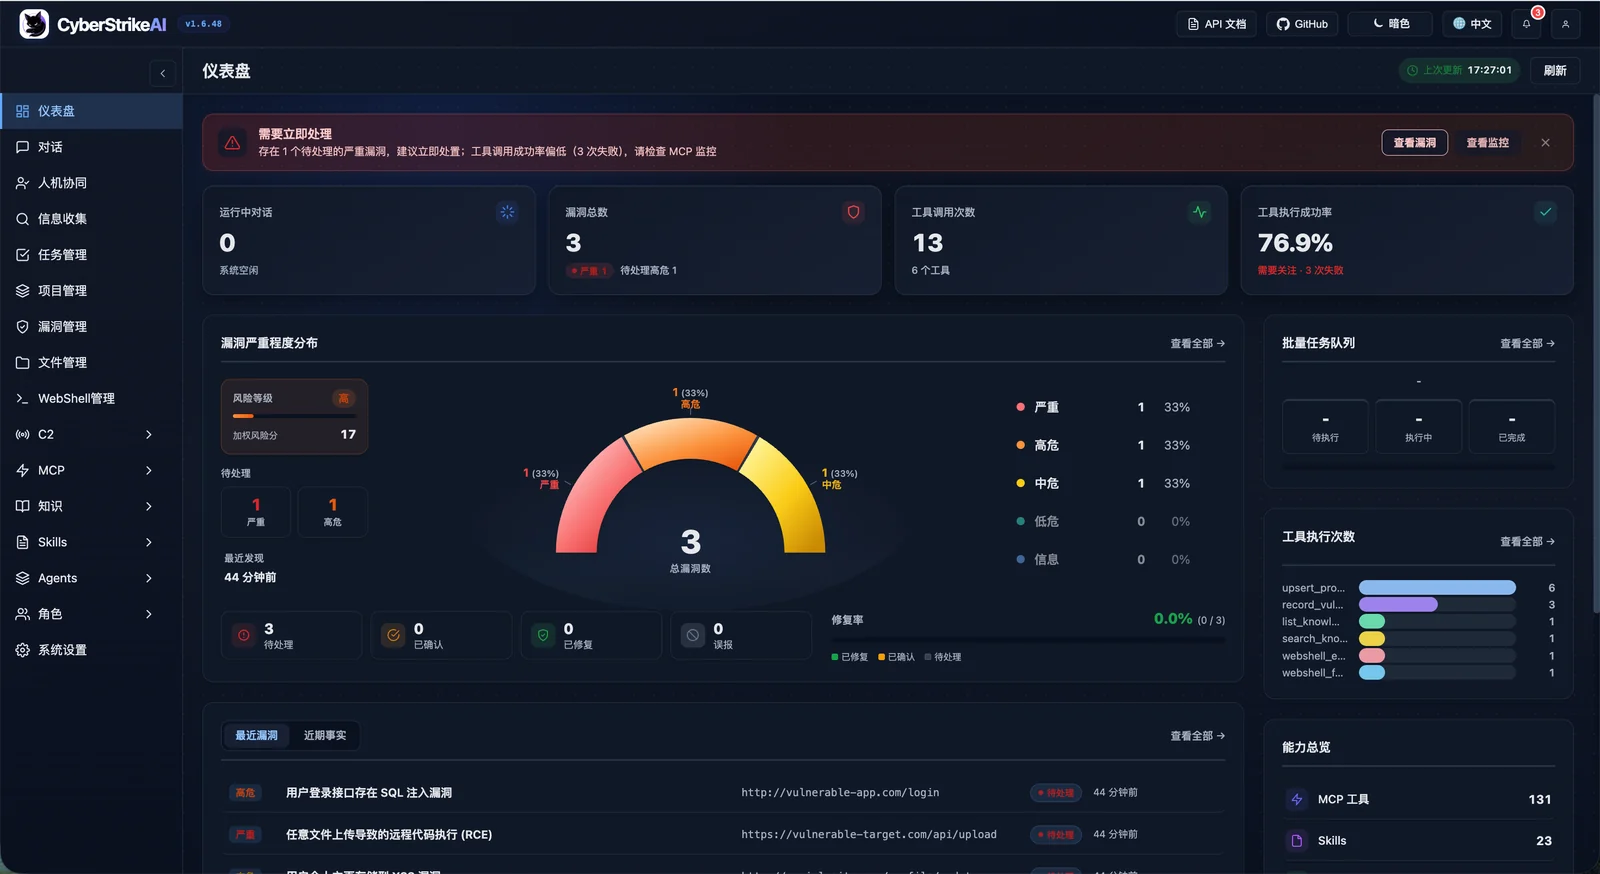
System Dashboard Overview

Light Mode
System Dashboard (Light)
Dark Mode
System Dashboard (Dark)

The dashboard provides a comprehensive overview of system runtime status, security vulnerabilities, tool usage, and knowledge base, helping users quickly understand the platform's core features and current state.

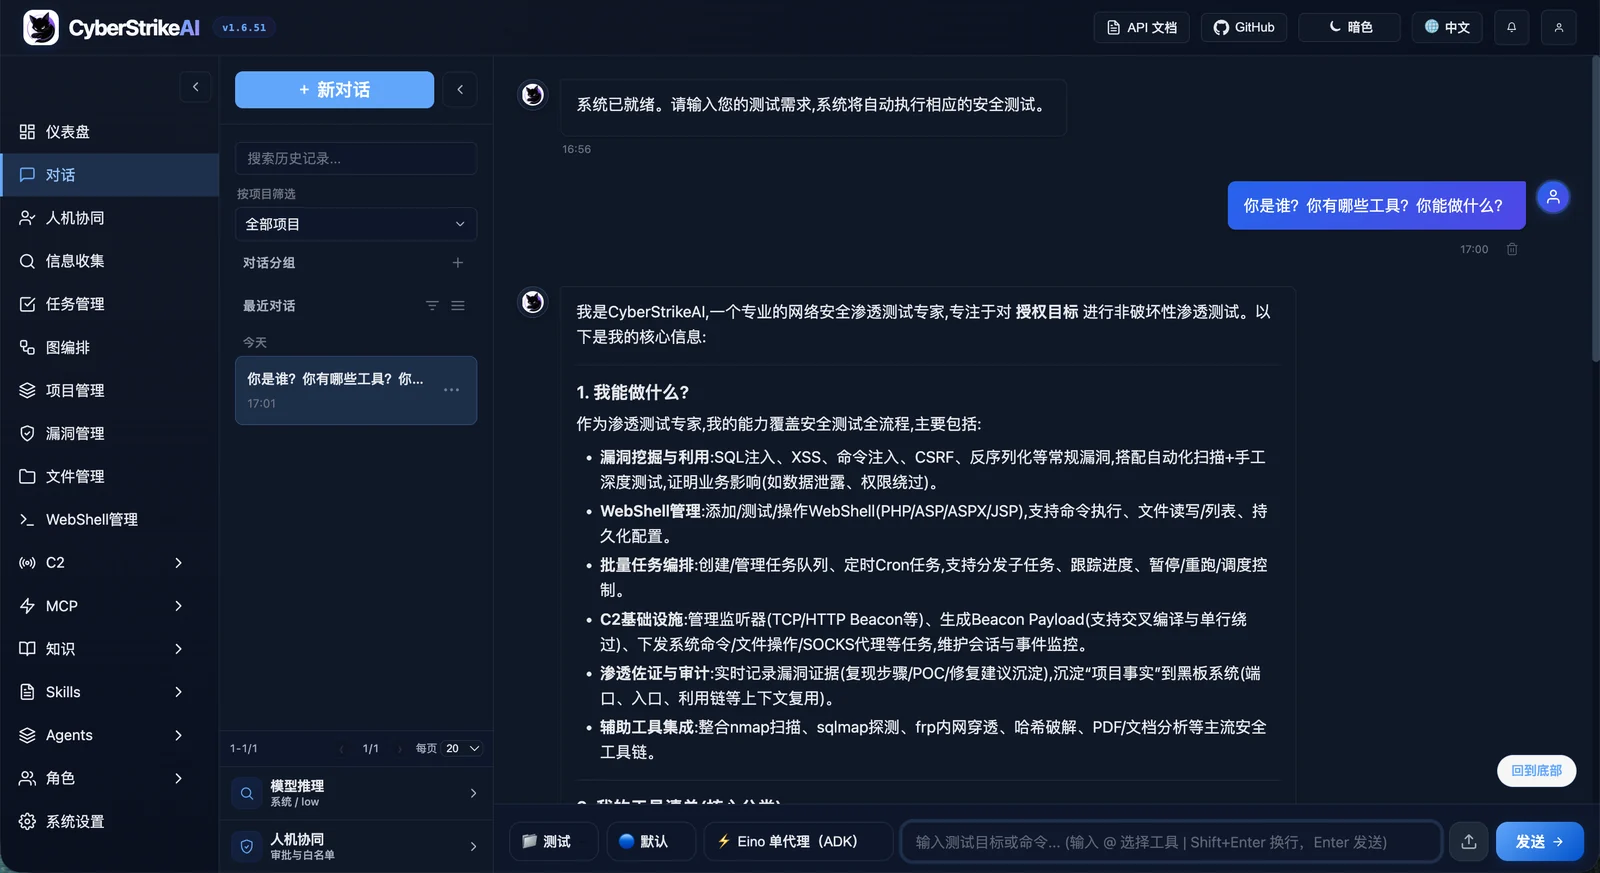
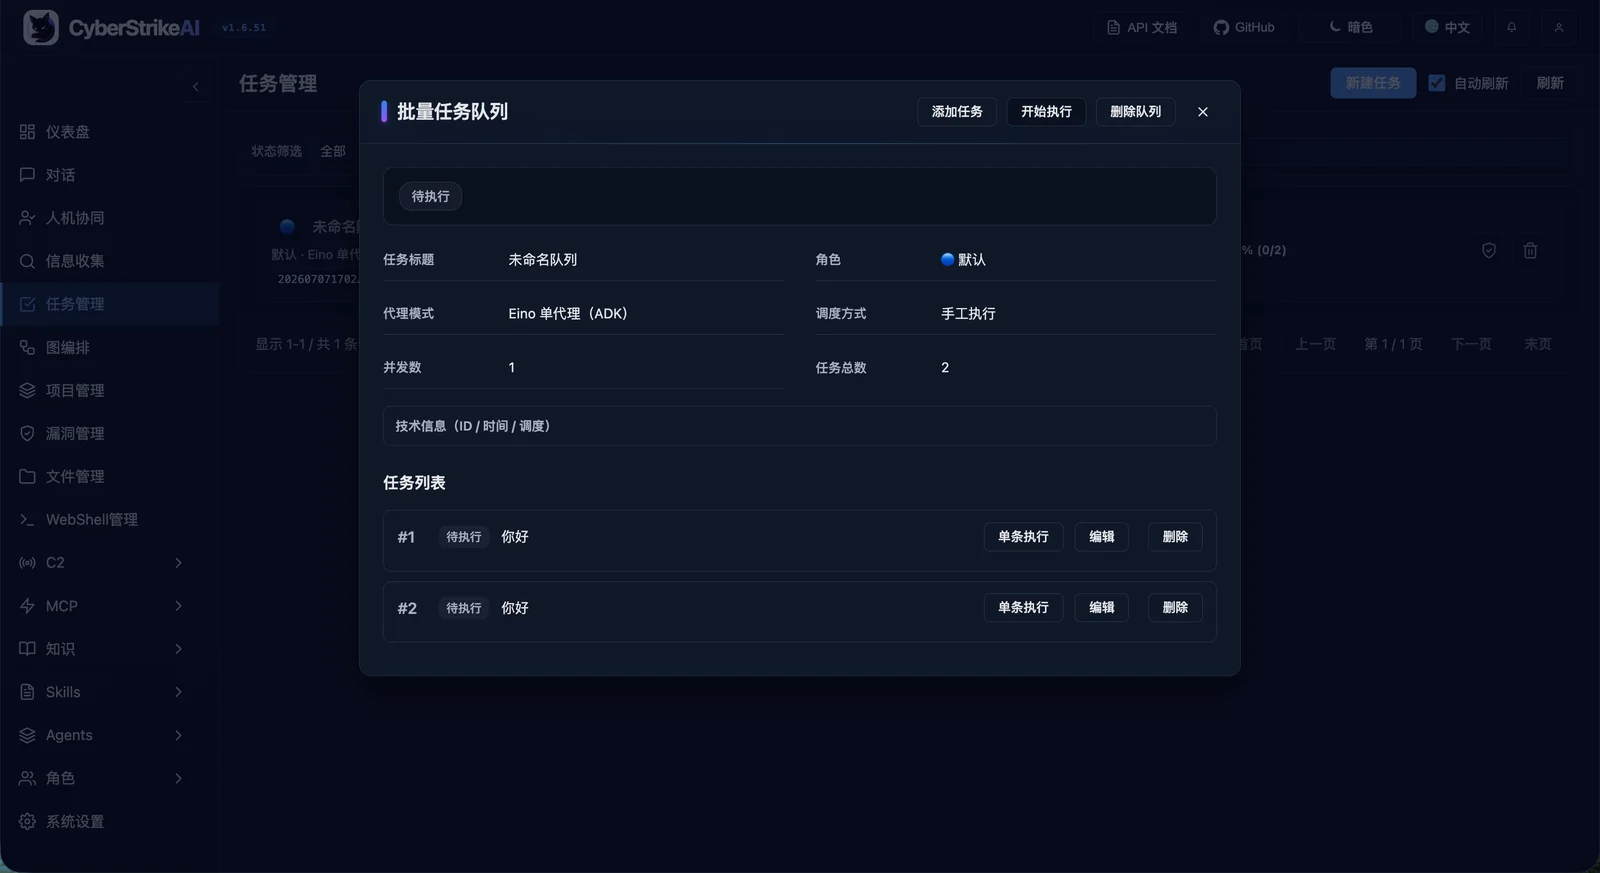
More interface screenshots

Core Features Overview

Web Console
Web Console
Task Management
Task Management
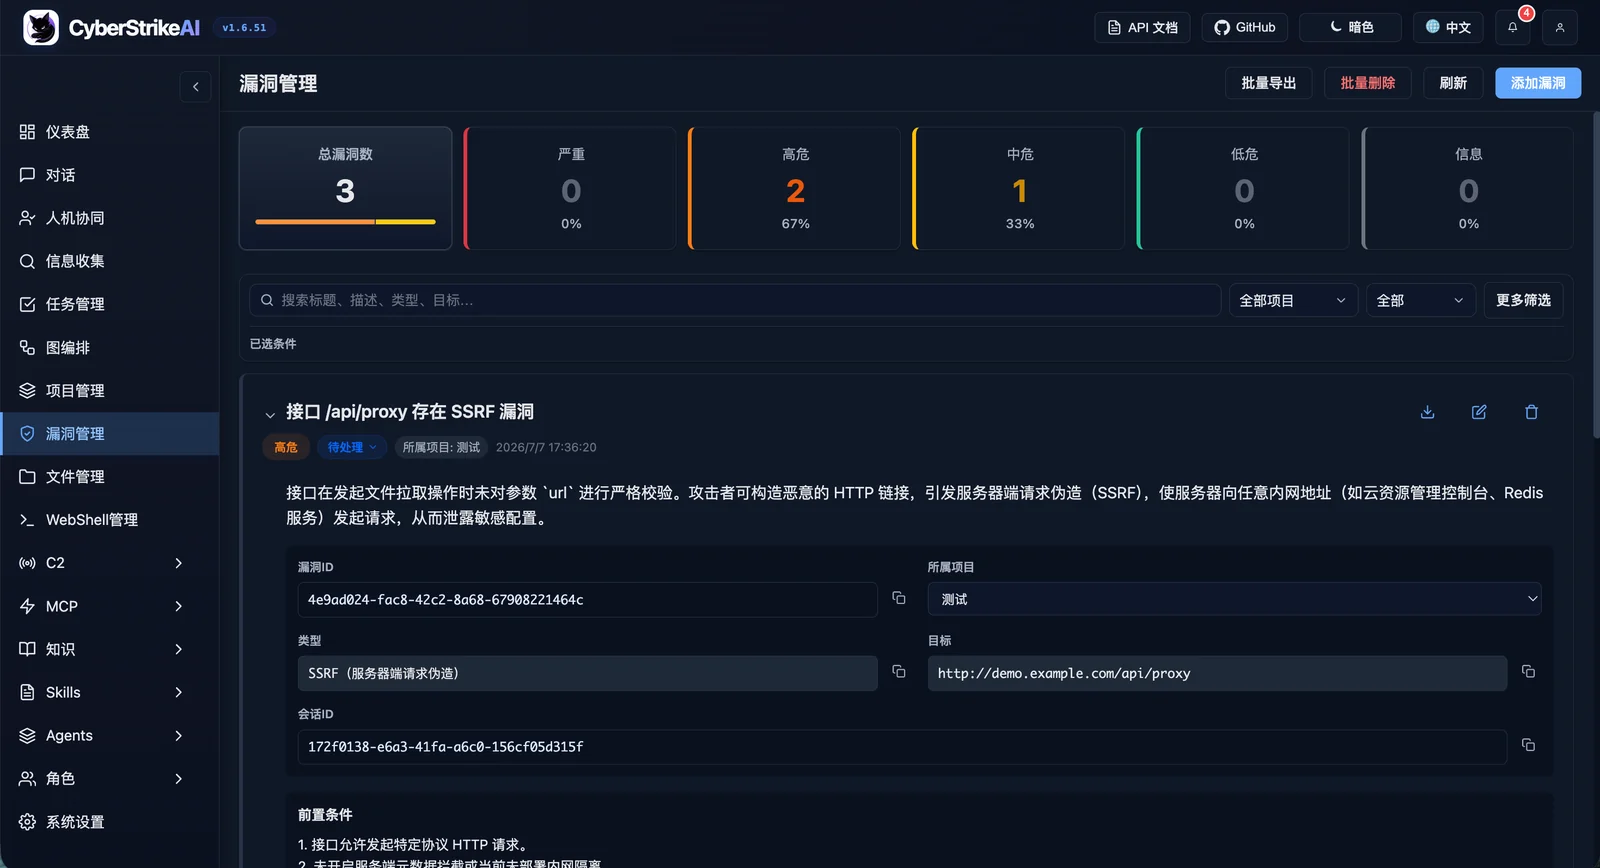
Vulnerability Management
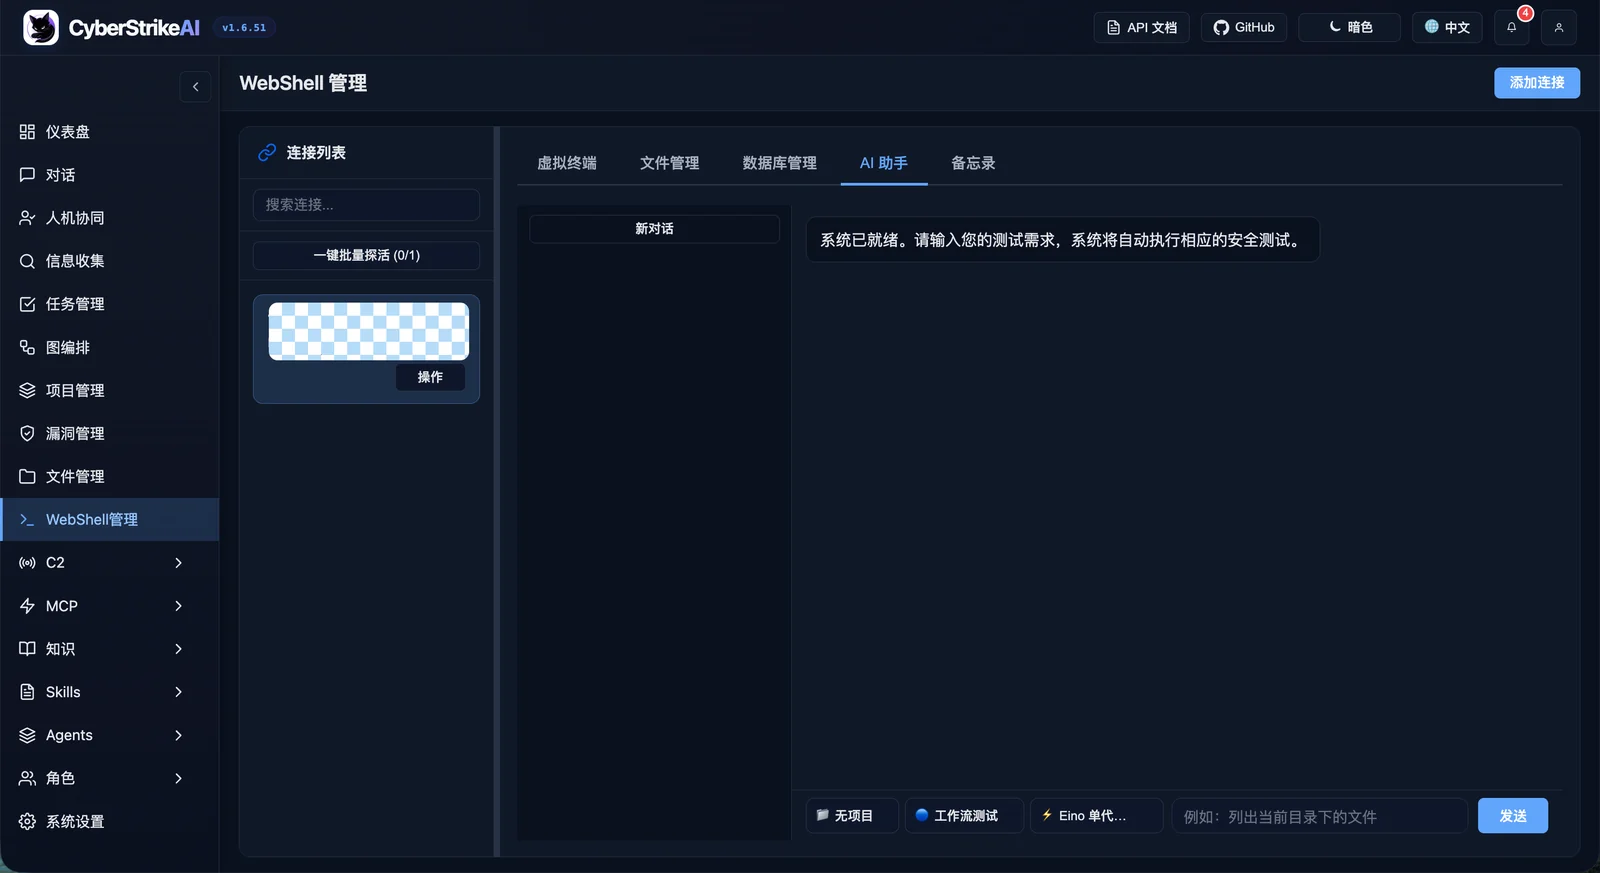
WebShell Management
WebShell Management
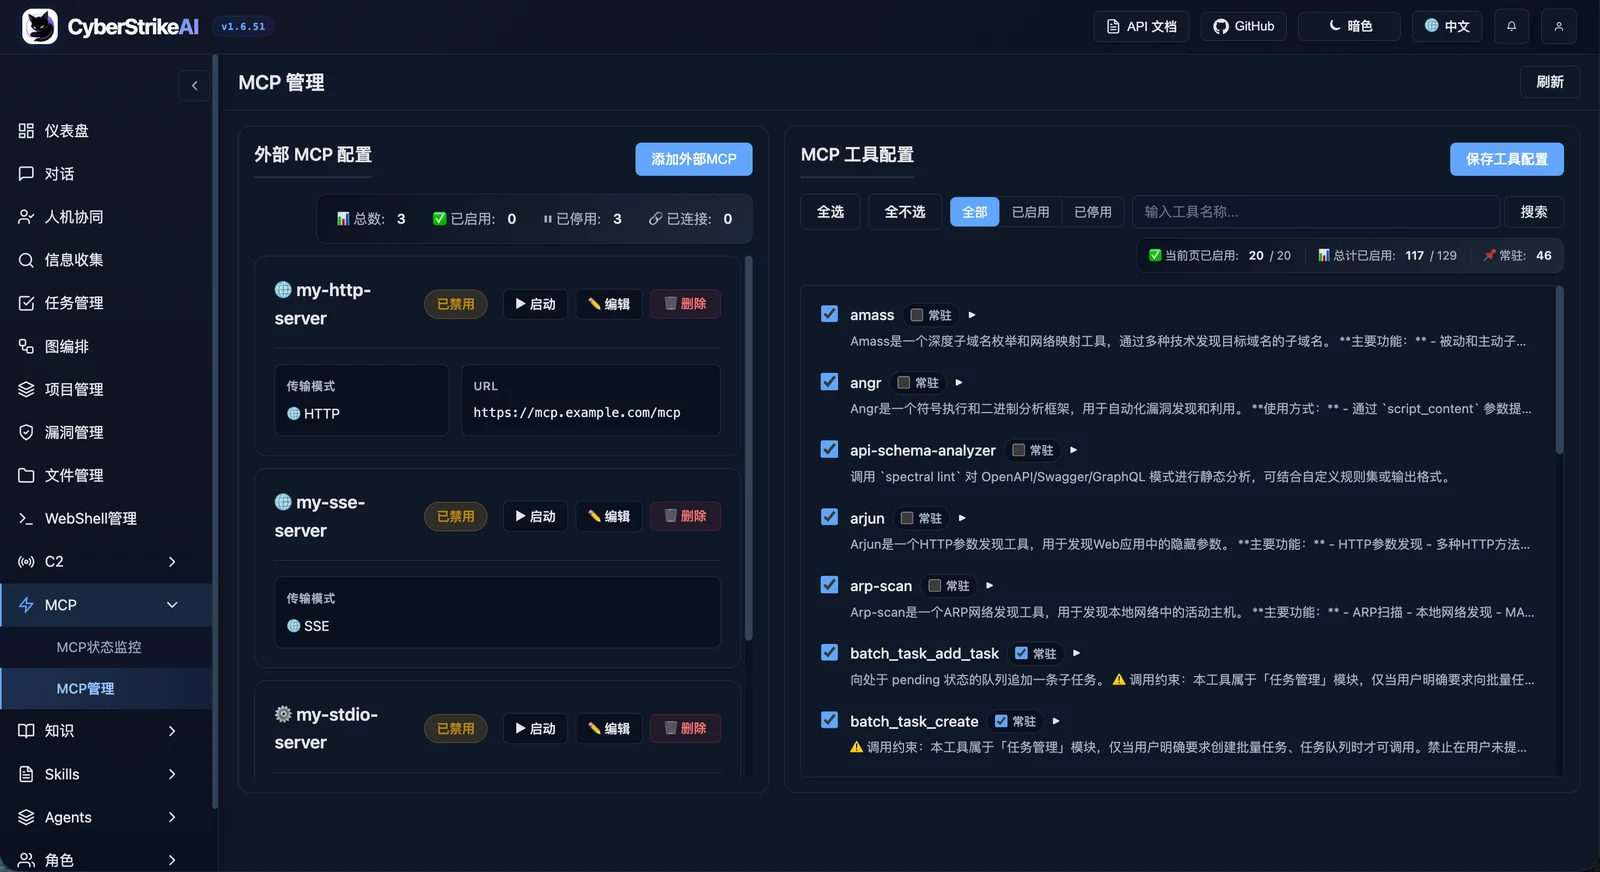
MCP Management
MCP management
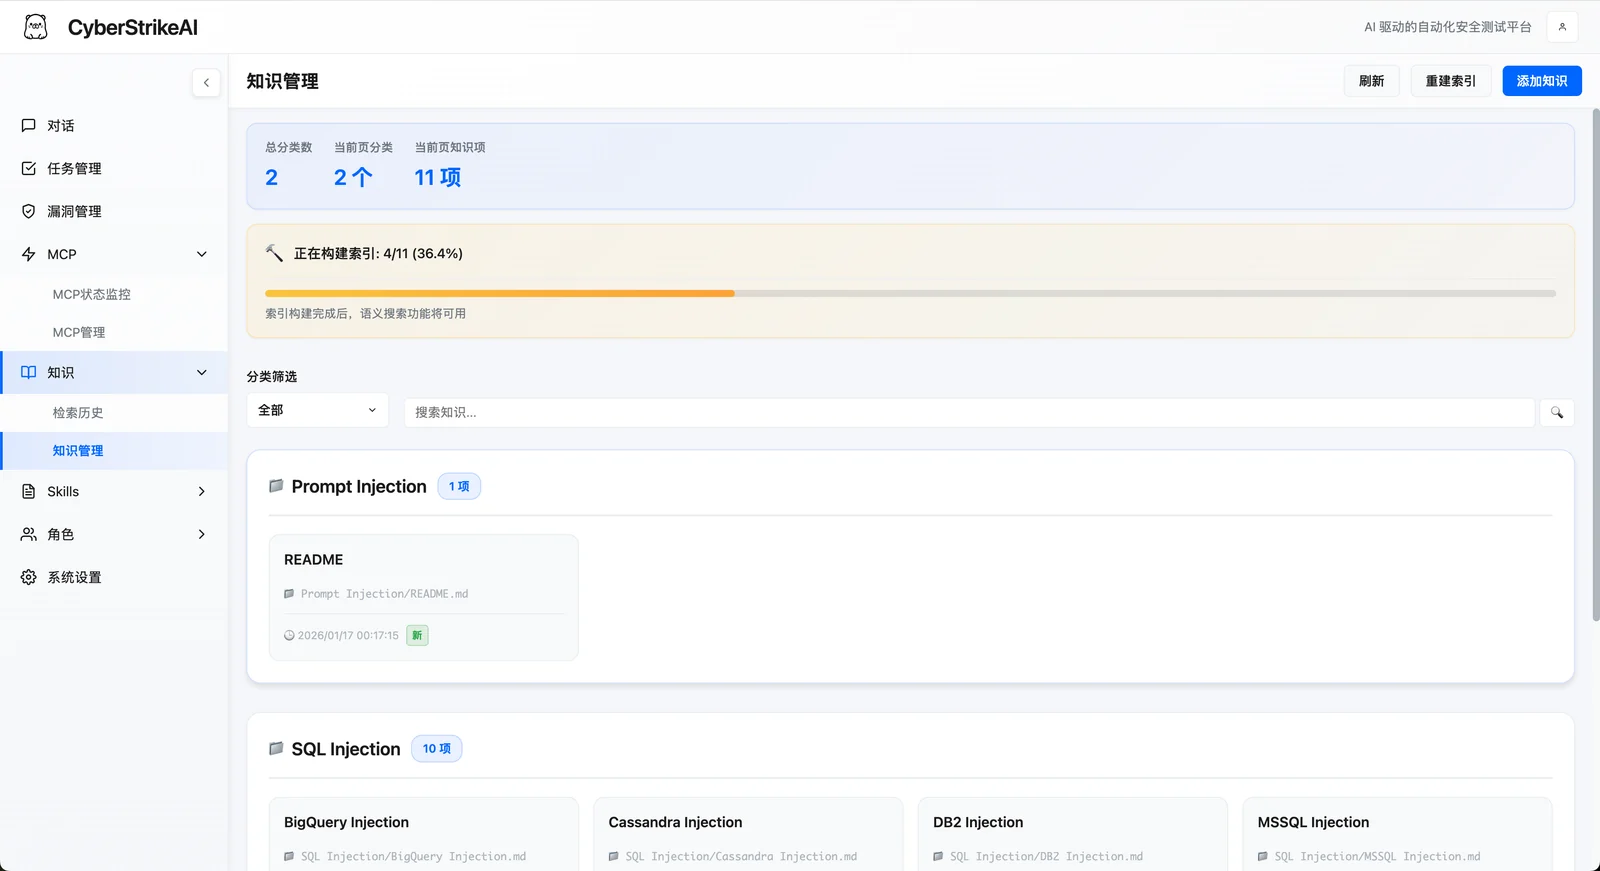
Knowledge Base
Knowledge Base
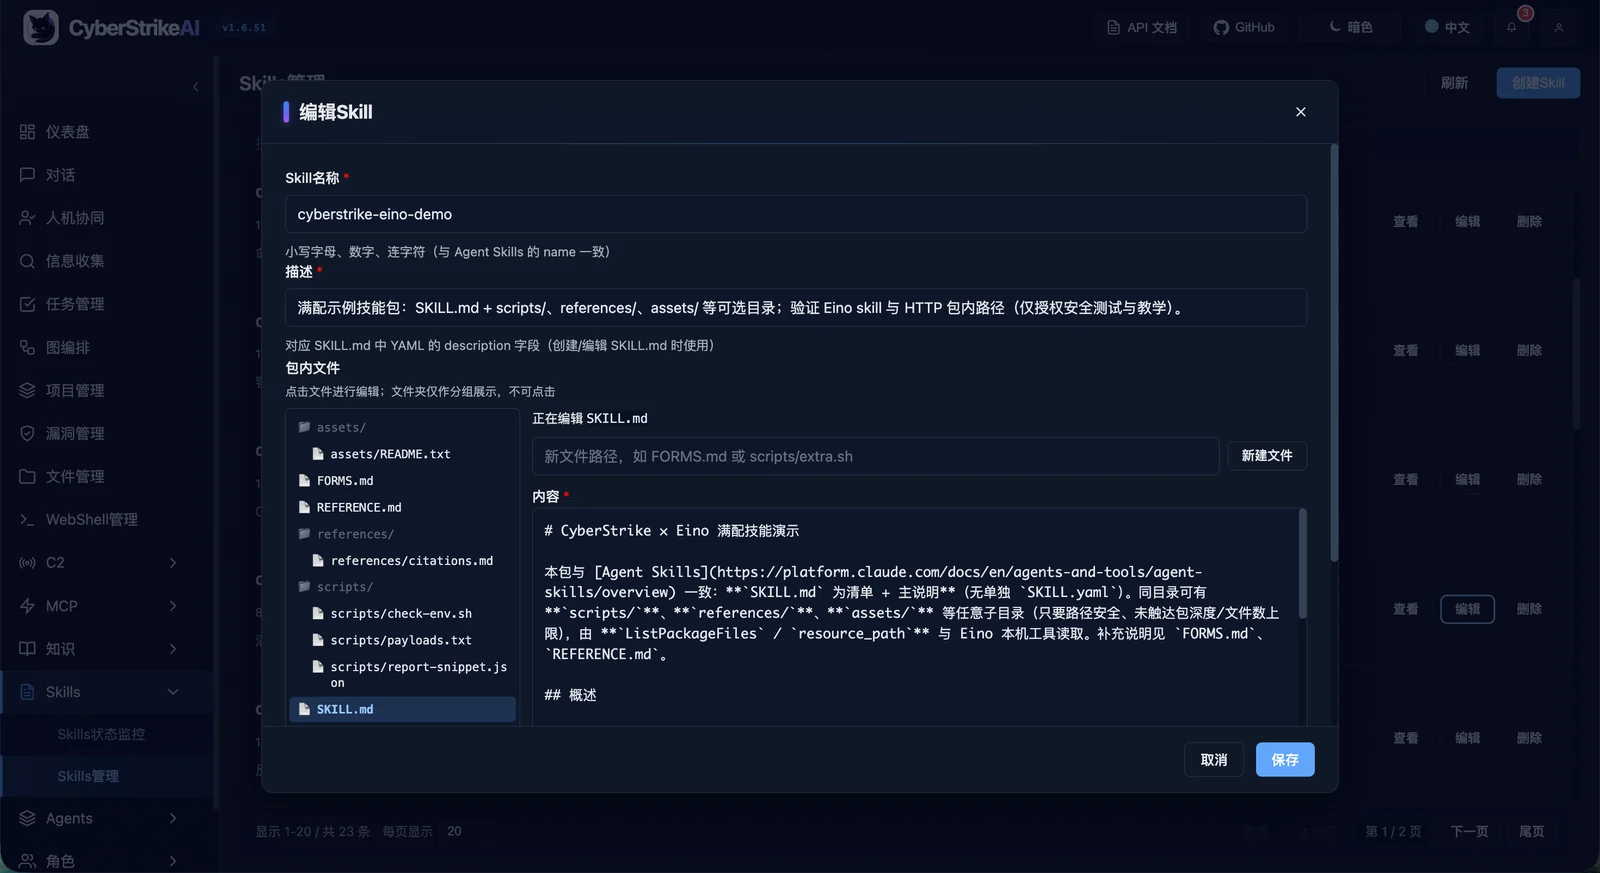
Skills Management
Skills Management
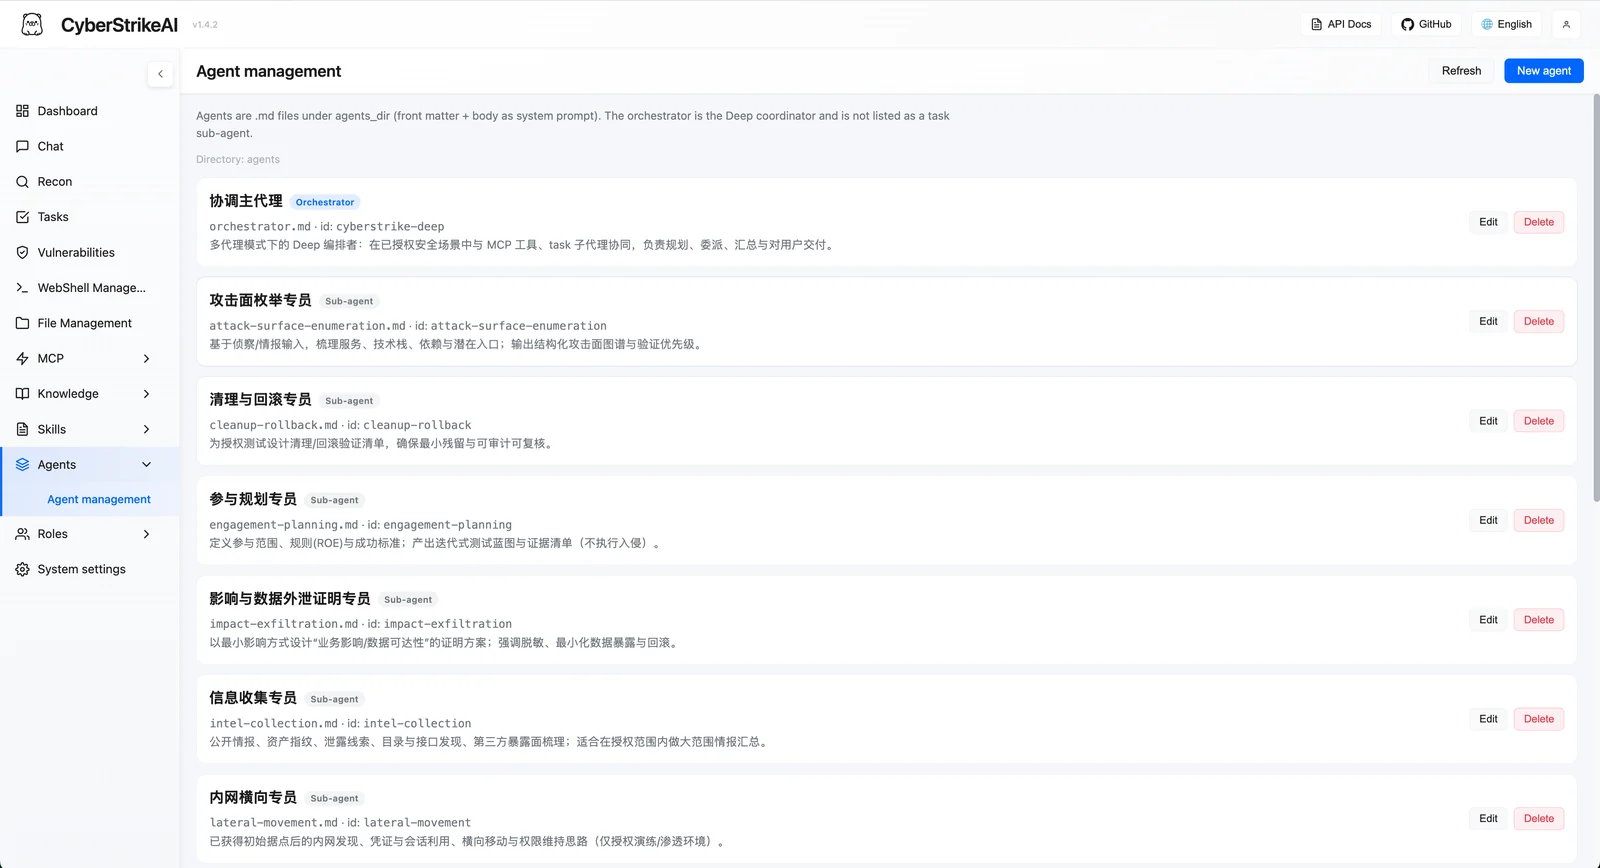
Agent Management
Agent Management
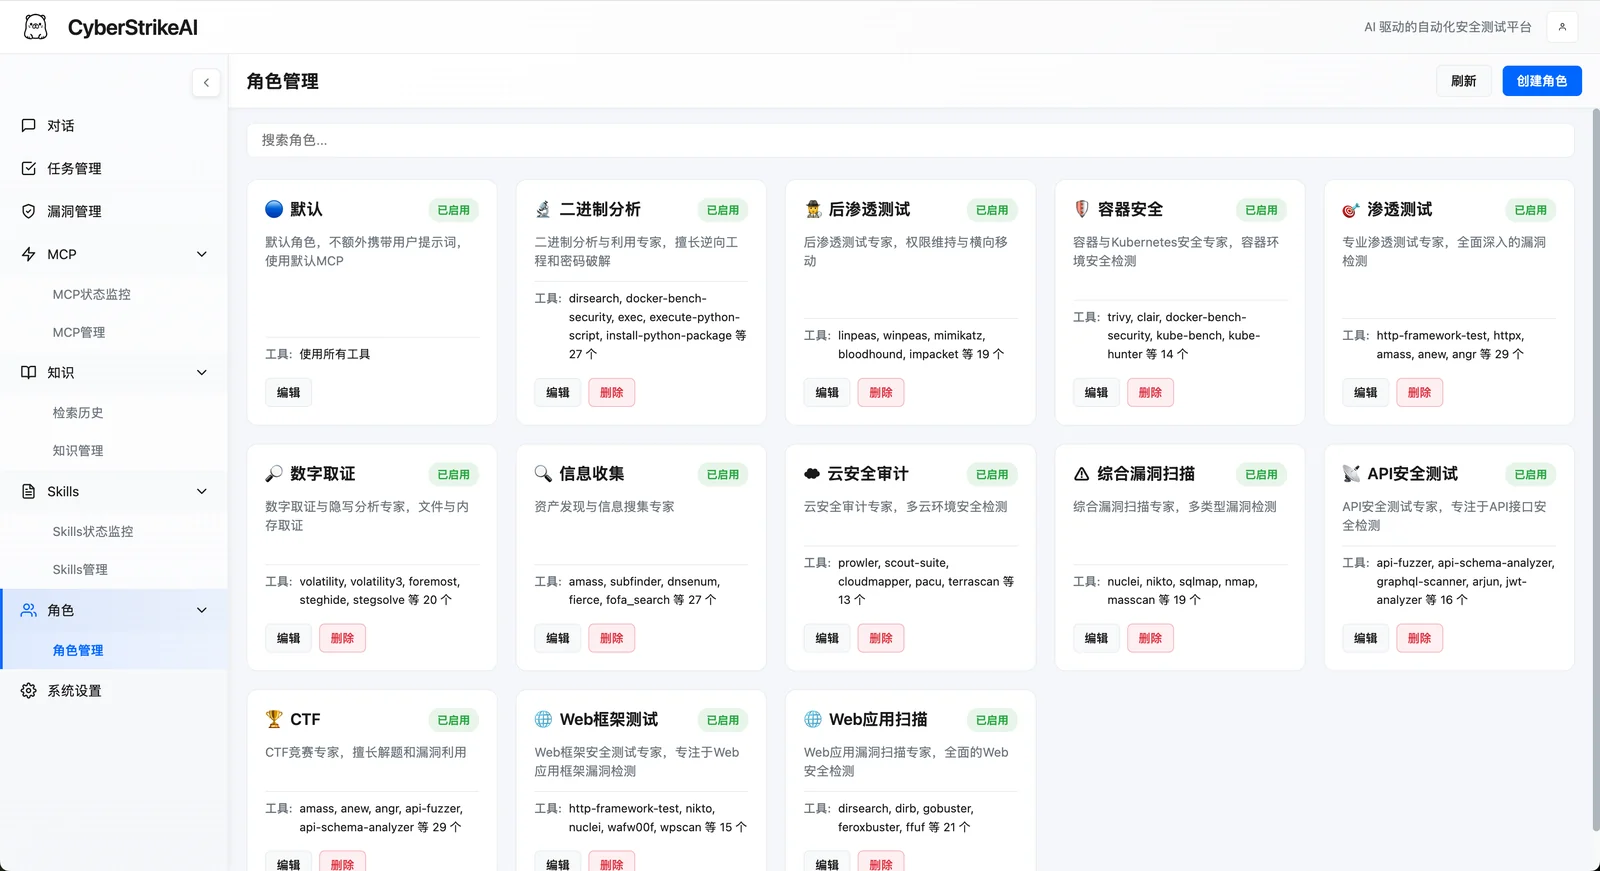
Role Management
Role Management
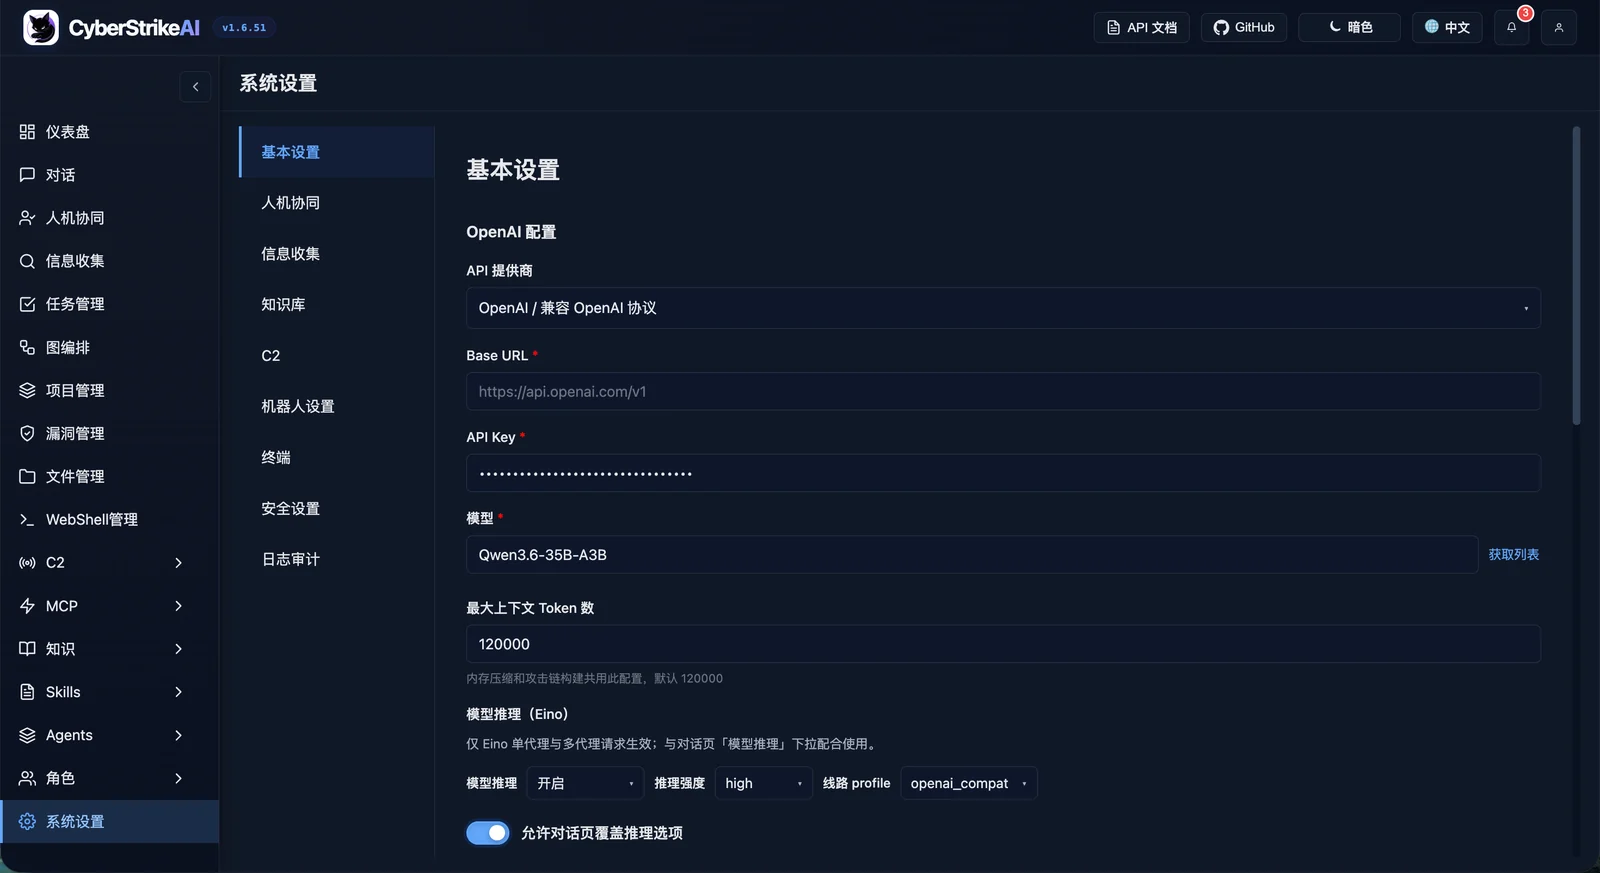
System Settings
System settings
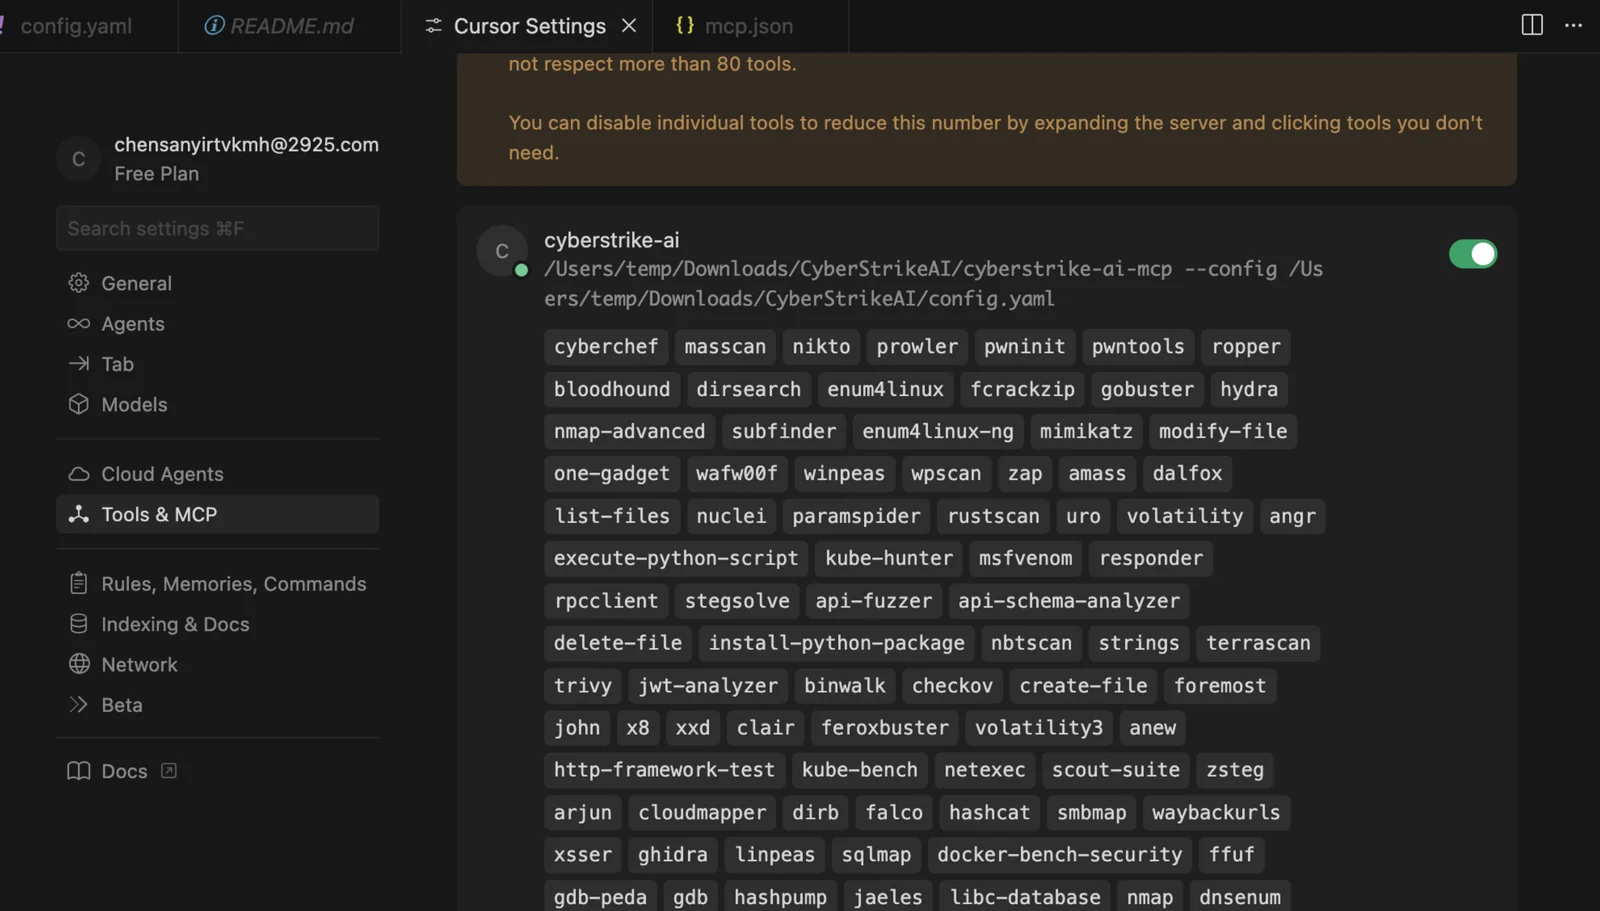
MCP stdio Mode
MCP stdio mode
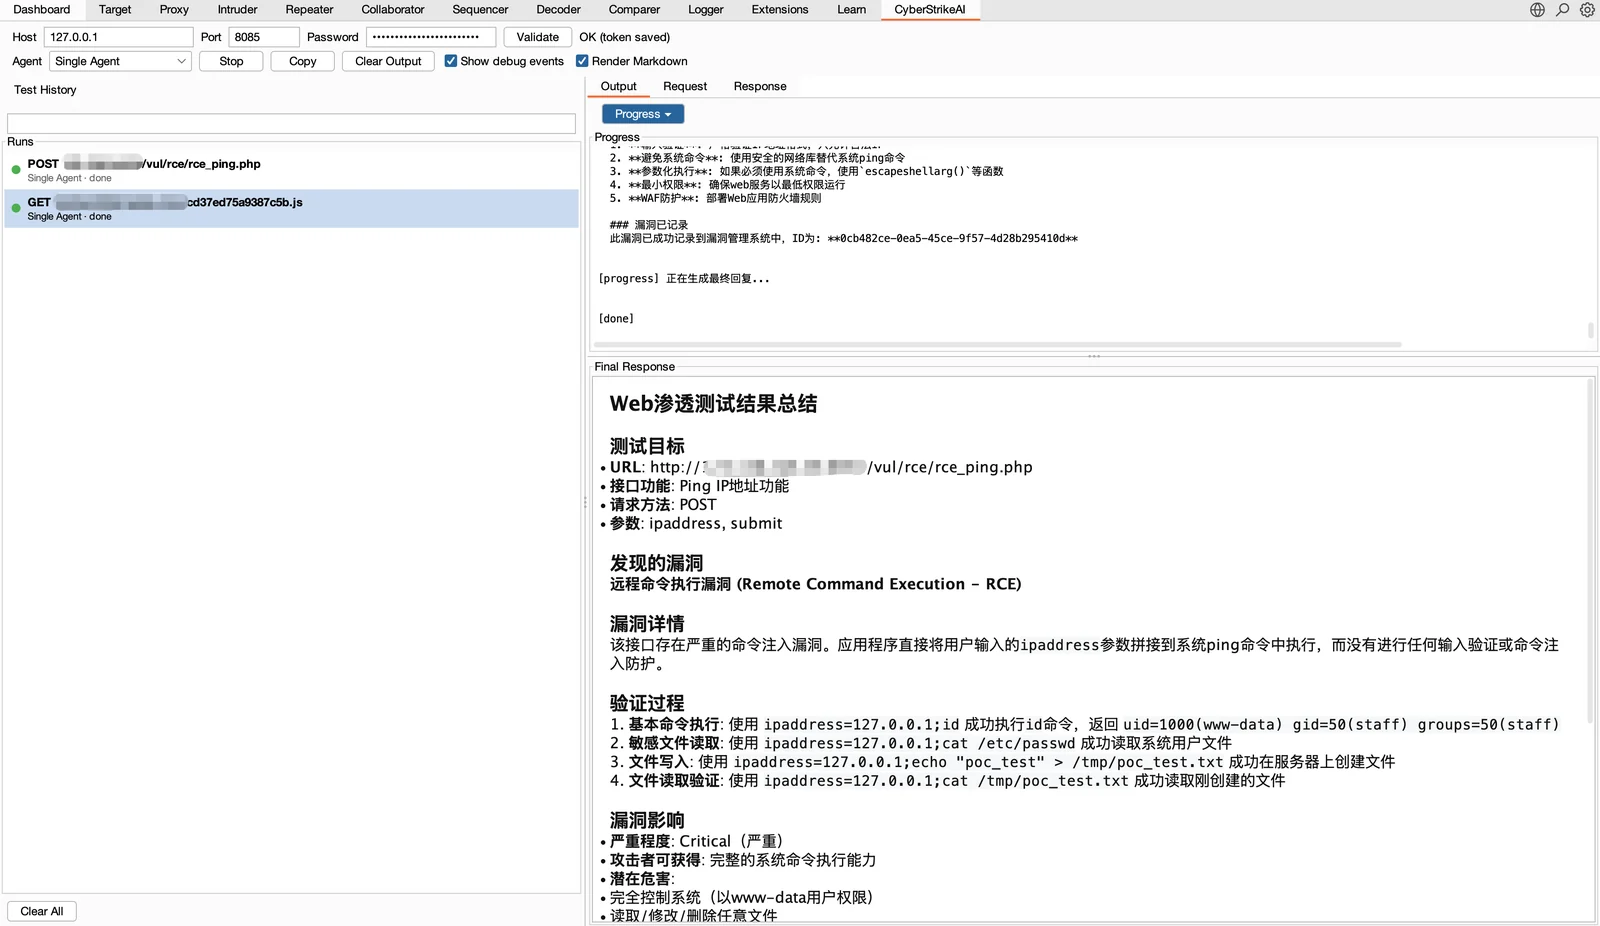
Burp Suite Plugin
Burp Suite plugin

Highlights

Agents and orchestration

  • 🤖 Agentic execution translates natural-language intent into governed, auditable security actions.
  • 🧩 Eino orchestration supports single-agent execution plus Deep, Plan-Execute, and Supervisor multi-agent modes.
  • 🔀 Graph workflows combine Agents, tools, conditions, approvals, and outputs into reusable flows.
  • 🎭 Role-based testing provides focused prompts and tool policies for common security scenarios.

Tools and knowledge

Tool herunterladen