Skip to content
KitploitKITPLOIT
أدواتعمليات الاستغلالالمدونة
Log in
إرسال
أدواتعمليات الاستغلالالمدونة
إرسال

أدوات الاختراق واختبار الاختراق والأمن السيبراني لترسانتك الأمنية!

Kitploit هو دليل لأدوات الاختراق والأمن السيبراني واختبار الاختراق. اكتشف آخر تحديثات المشاريع للعثور على الثغرات وتحليل الأنظمة وأتمتة الاختبارات وتعزيز أمنك.

الخلاصاتاتصالالخصوصية© 2026 Kitploit

دليل الأدوات

الفئات

عرض جميع الفئات
Loading categories
أدوات/GitHubGitHub/sia-iotechnology/kittysploit-framework
OSINT (Open Source Intelligence)Penetration Testing FrameworksReconnaissanceExploit FrameworksWeb Proxies & InterceptionDebuggersPost-ExploitationCommand and ControlRed TeamingPayload DevelopmentAI Security
5939873منذ 4 أيامتمت المراجعة من قبل Kitploit
مشاركة
GitHub
sia-iotechnology/kittysploit-framework

Kittysploit-framework

Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,....
عرض المستودعالموقع الإلكتروني
المحتوى غير متوفر باللغة المطلوبة. عرض النسخة الإنجليزية.
KittySploit logo

KittySploit

Exploitation and post-exploitation framework — one console.

Recon, scanning, exploits, interactive sessions, and post-exploitation across 60+ session connectors (shell, browser, databases, cloud, IoT/ICS, and more).
Python License Discord GitHub stars

Installation · Quick start · Full guide · Website

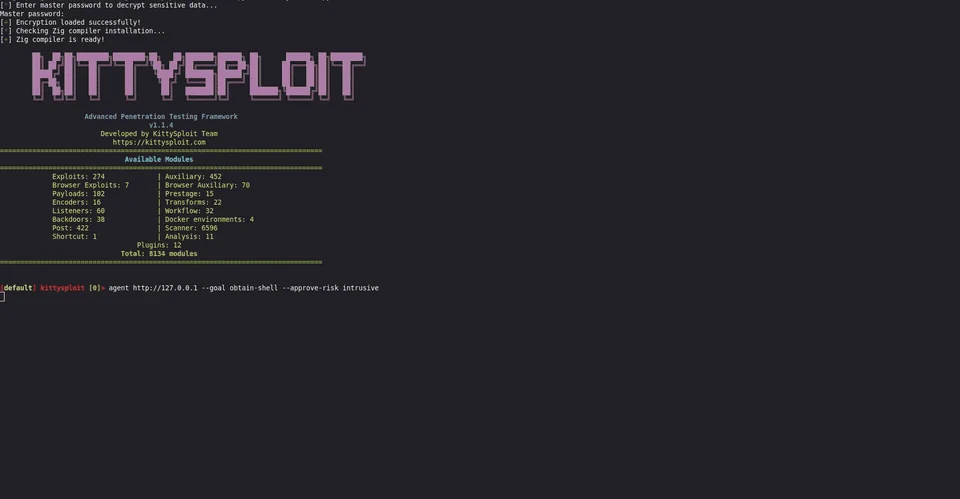
KittySploit — console, exploitation, and sessions

At a glance

StepWhat KittySploit does
1. FindWeb, network, cloud, and service scanners and recon
2. ExploitExploit modules, chains, and optional local-LLM agent
3. Post-exploit60+ session connectors — loot, pivot, persistence, enumeration

Everything stays in one console: modules, listeners, payloads, built-in C2, and reporting.

Use only on targets you own or are explicitly authorized to test.

Why KittySploit?

Typical stacks split the scanner, exploit framework, C2, and notes across different tools.

KittySploit brings them together: exploit to get a session, then run post-exploitation without switching apps.

Post-exploitation connector examples: Linux/Windows shell, browser (JS session), SSH, MySQL/PostgreSQL/Redis/MongoDB, SMB, FTP, Kubernetes, AWS/GCP/Azure, PHP webshell, WinRM, LDAP, BLE, MQTT, Modbus, BACnet, ONVIF, and more.

Module scale (approximate): thousands of scanners/auxiliary modules, 700+ exploits, 400+ post modules.

Installation

Linux and macOS

git clone https://github.com/SIA-IOTechnology/Kittysploit-framework.git
cd Kittysploit-framework
./install/install.sh
python3 kittyconsole.py

One-line install:

curl -fsSL https://raw.githubusercontent.com/SIA-IOTechnology/Kittysploit-framework/main/install/install-standalone.sh | bash

Windows

git clone https://github.com/SIA-IOTechnology/Kittysploit-framework.git
cd Kittysploit-framework
install\install.bat
python kittyconsole.py

Quick start

kittysploit> doctor
kittysploit> search cve:2024 type:exploit
kittysploit> use exploits/multi/http/...
kittysploit> run

kittysploit> sessions -l
kittysploit> sessions -i 1
kittysploit> search type:post platform:windows

Automated web mission (authorized lab):

kittysploit> agent https://lab.local

Shell goal on an internal lab:

kittysploit> agent http://192.168.56.10 \
  --profile internal-lab \
  --goal obtain-shell \
  --approve-risk intrusive \
  --shell-hunter

Use --plan-only or --dry-run to preview without intrusive actions.

Core features

  • Exploitation — search / use / run, payloads, listeners, exploit queues
  • Sessions and C2 — shells, callbacks, pivots, multi-session management
  • Post-exploitation — modules per session type (gather, manage, pivot, loot)
  • Agent (optional) — local LLM (Ollama), mission profiles, scope controls
  • Automation — CLI, API/RPC, and MCP for IDE or scripted workflows

Agent profiles, compound evidence, environment variables, and cookbooks are in USAGE.md.

Ecosystem

ProjectPurpose
KittyProxyHTTP capture and analysis
KittyCosmicGraphical interface
KittyOsintVisual OSINT
KittyProtocolProtocol analysis
KittyV8DebuggerV8 debugging

Demo video · Site and marketplace · Wiki

Community

  • Discord
  • Issues
  • Liberapay

The project is still evolving — validate in a lab before production engagements.

Acknowledgments

Thanks to Woody for their contributions.

License

Released under the MIT License.

تنزيل الأداة

الأكثر شعبية

عرض الكل →

اكتشف الأدوات الأكثر استخدامًا من قبل مجتمعنا.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 مجموعة أدوات OSINT المثالية: رسم بياني للتحقيق، وتقييم الثقة، وعائلات الأسماء المستعارة، وخريطة، وخط زمني، وتقارير. 49 وحدة، وأكثر من 400 موقع، دون الحاجة إلى مفاتيح API.

    708
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    # تطبيق GhostLock للتنفيذ بنقرة واحدة (CVE-2026-43499)

    500
  • 3

    ARTEX

    baarai/artex

    منصة اختبار اختراق مستقلة متعددة الوكلاء تعتمد على LLM، مع وكلاء تخطيط وتنفيذ، ومخططات للأصول والاستكشاف، وتسجيل حركة مرور MITM، وإعادة اختبار الثغرات.

    398
  • 4

    redforge

    cybersecurity91/redforge

    مجموعة أدوات الفريق الأحمر في المتصفح مع 102 أداة دون اتصال للاستطلاع، وتوليد الحمولات، وهجمات بيانات الاعتماد، والتشفير، والترميز، وإعداد تقارير المهام.

    341
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    نظام العمل للأمن السيبراني الأصلي بالذكاء الاصطناعي — حيث تتحول النية إلى تنفيذ محكوم، وتصبح الأدلة ذاكرة تشغيلية، وكل عملية تحسن التي تليها.

    259
  • 6

    antifox

    antifox-ai/antifox

    منصة اختبار اختراق متعددة الوكلاء ذاتية التشغيل بالذكاء الاصطناعي تُجري الاستطلاع واكتشاف سطح الهجوم والتحقق من الاستغلال وتسليم تقارير مدعومة بالأدلة.

    257

استكشف جميع الأدوات

تصفح مجموعتنا من الأدوات

عرض جميع الأدوات →