

 projectdiscovery/naabu
ماسح منافذ سريع مكتوب بلغة Go مع التركيز على الموثوقية والبساطة. مصمم لاستخدامه مع أدوات أخرى لاكتشاف سطح الهجوم في مكافآت الثغرات واختبارات الاختراق.



الميزات • التثبيت • الاستخدام • تشغيل naabu • الإعدادات • تكامل NMAP • استبعاد CDN/WAF • Discord
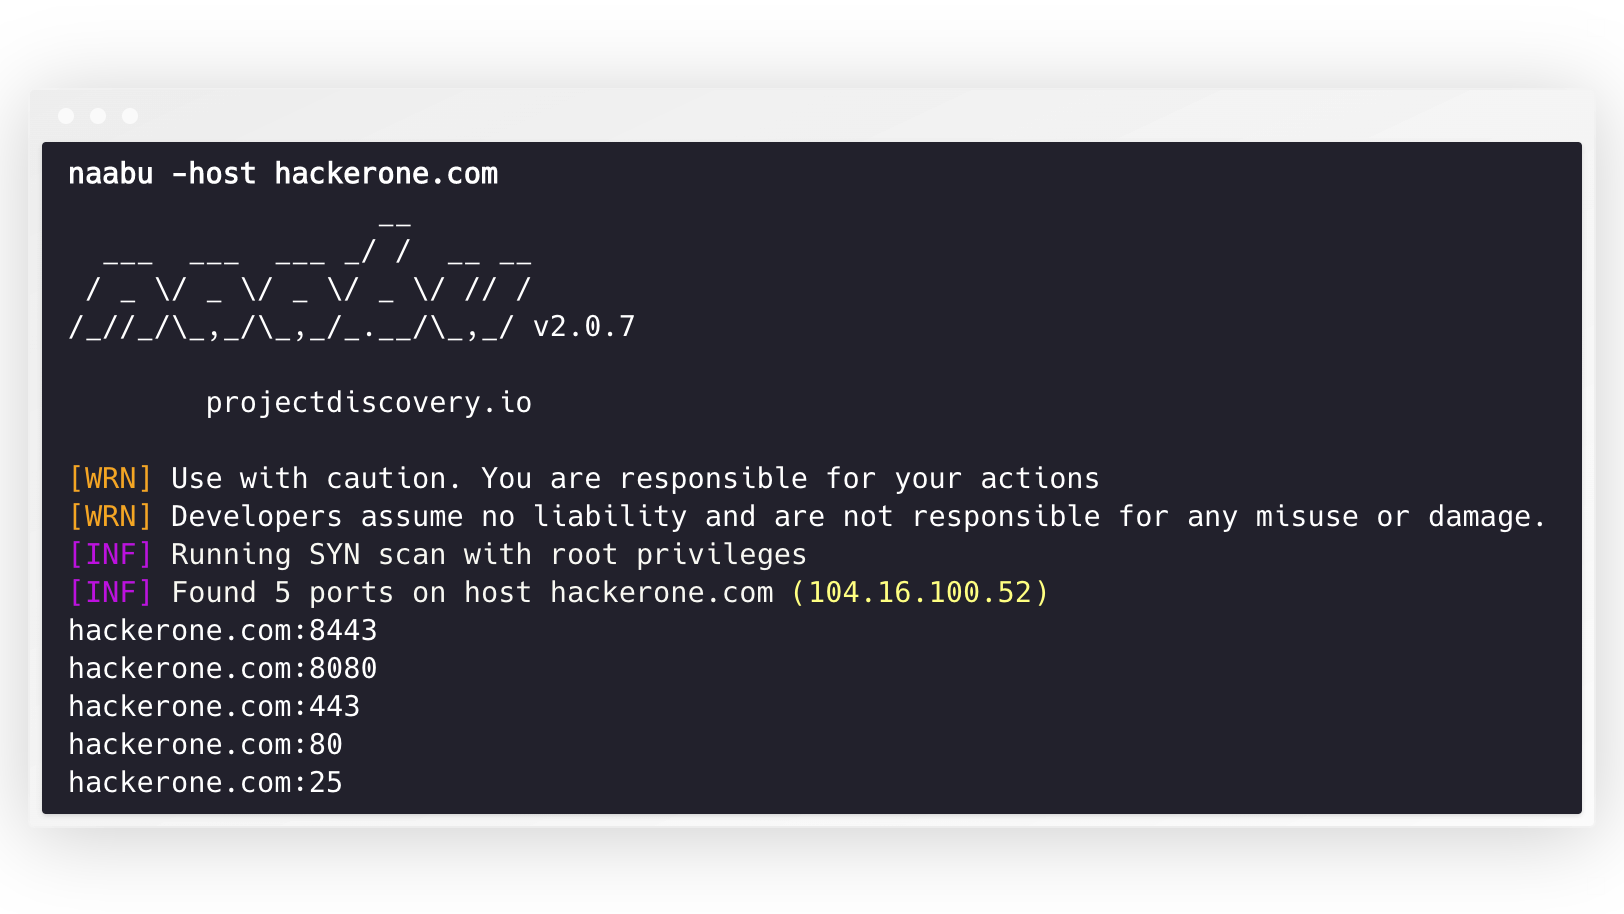
Naabu هي أداة فحص المنافذ مكتوبة بلغة Go تتيح لك تعداد المنافذ الصالحة للمضيفين بطريقة سريعة وموثوقة. إنها أداة بسيطة للغاية تقوم بإجراء فحوصات SYN/CONNECT/UDP سريعة على المضيف/قائمة المضيفين وتسرد جميع المنافذ التي تُرجع ردًا.
naabu -h
سيؤدي هذا إلى عرض المساعدة الخاصة بالأداة. فيما يلي جميع المفاتيح التي تدعمها.
Usage:
  naabu [flags]

Flags:
INPUT:
   -host string[]              hosts to scan ports for (comma-separated)
   -list, -l string            list of hosts to scan ports (file)
   -exclude-hosts, -eh string  hosts to exclude from the scan (comma-separated)
   -exclude-file, -ef string   list of hosts to exclude from scan (file)

PORT:
   -port, -p string            ports to scan (80,443, 100-200)
   -top-ports, -tp string      top ports to scan (default 100) [full,100,1000]
   -exclude-ports, -ep string  ports to exclude from scan (comma-separated)
   -ports-file, -pf string     list of ports to scan (file)
   -port-threshold, -pts int   port threshold to skip port scan for the host
   -exclude-cdn, -ec           skip full port scans for CDN/WAF (only scan for port 80,443)
   -display-cdn, -cdn          display cdn in use

RATE-LIMIT:
   -c int     general internal worker threads (default 25)
   -rate int  packets to send per second (default 1000)

UPDATE:
   -up, -update                 update naabu to latest version
   -duc, -disable-update-check  disable automatic naabu update check

OUTPUT:
   -o, -output string  file to write output to (optional)
   -j, -json           write output in JSON lines format
   -csv                write output in csv format

SERVICES-DISCOVERY:
   -sD, -service-discovery           identify services by port number
   -sV, -service-version             detect service versions using nmap-service-probes
   -sV-fast                          only probe port-hinted services (faster, skips fallback)
   -sV-timeout duration              timeout for service version probes (default 5s)
   -sV-workers int                   number of concurrent service version workers (default 25)
   -sV-probes string                 custom nmap-service-probes file path (auto-detected from local nmap install if empty)
   -uP, -udp-probes                  send protocol-specific payloads on UDP scans using nmap-service-probes

CONFIGURATION:
   -config string                   path to the naabu configuration file (default $HOME/.config/naabu/config.yaml)
   -scan-all-ips, -sa               scan all the IP's associated with DNS record
   -ip-version, -iv string[]        ip version to scan of hostname (4,6) - (default 4,6) (default ["4","6"])
   -scan-type, -s string            type of port scan (SYN/CONNECT) (default "c")
   -source-ip string                source ip and port (x.x.x.x:yyy - might not work on OSX)
   -cp, -connect-payload string    payload to send in CONNECT scans (optional)
   -interface-list, -il             list available interfaces and public ip
   -interface, -i string            network Interface to use for port scan
   -nmap                            invoke nmap scan on targets (nmap must be installed) - Deprecated
   -nmap-cli string                 nmap command to run on found results (example: -nmap-cli 'nmap -sV')
   -r string                        list of custom resolver dns resolution (comma separated or from file)
   -proxy string                    socks5 proxy (ip[:port] / fqdn[:port]
   -proxy-auth string               socks5 proxy authentication (username:password)
   -dns-order string                dns resolution order (p/l/lp/pl) (default "l")
   -sr, -system-resolver            use system DNS as fallback resolver
   -resume                          resume scan using resume.cfg
   -stream                          stream mode (disables resume, nmap, verify, retries, shuffling, etc)
   -passive                         display passive open ports using shodan internetdb api (automatically enables stream mode)
   -irt, -input-read-timeout value  timeout on input read (default 3m0s)
   -no-stdin                        Disable Stdin processing

HOST-DISCOVERY:
   -sn, -host-discovery           Perform Only Host Discovery
   -show-dead                     show hosts that did not respond to host discovery (requires host discovery)
   -Pn, -skip-host-discovery      Skip Host discovery (Deprecated: use -wn/-with-host-discovery instead)
   -wn, -with-host-discovery      Enable Host discovery
   -ps, -probe-tcp-syn string[]   TCP SYN Ping (host discovery needs to be enabled)
   -pa, -probe-tcp-ack string[]   TCP ACK Ping (host discovery needs to be enabled)
   -pe, -probe-icmp-echo          ICMP echo request Ping (host discovery needs to be enabled)
   -pp, -probe-icmp-timestamp     ICMP timestamp request Ping (host discovery needs to be enabled)
   -pm, -probe-icmp-address-mask  ICMP address mask request Ping (host discovery needs to be enabled)
   -arp, -arp-ping                ARP ping (host discovery needs to be enabled)
   -nd, -nd-ping                  IPv6 Neighbor Discovery (host discovery needs to be enabled)
   -rev-ptr                       Reverse PTR lookup for input ips
