Skip to content
KitploitKITPLOIT
أدواتالمدونة
Log in
إرسال
أدواتالمدونة
إرسال

أدوات الاختراق واختبار الاختراق والأمن السيبراني لترسانتك الأمنية!

Kitploit هو دليل لأدوات الاختراق والأمن السيبراني واختبار الاختراق. اكتشف آخر تحديثات المشاريع للعثور على الثغرات وتحليل الأنظمة وأتمتة الاختبارات وتعزيز أمنك.

الخلاصاتاتصالالخصوصية© 2026 Kitploit

دليل الأدوات

الفئات

عرض جميع الفئات
Loading categories
prismor — Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt injection, supply chain etc in a local dashboard. Agent agnostic (Claude, codex, langchain etc.) | Kitploit
أدوات/GitHubGitHub/prismorsec/prismor
Defensive ToolsContainer SecurityDevSecOpsSecret DetectionThreat IntelligenceSupply Chain SecurityIncident ResponseAI Security
GitHubprismorsec/prismor

prismor

Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt injection, supply chain etc in a local dashboard. Agent agnostic (Claude, codex, langchain etc.)

28326126منذ 10س 57دتمت المراجعة من قبل Kitploit
مشاركة
عرض المستودعالموقع الإلكتروني
المحتوى غير متوفر باللغة المطلوبة. عرض النسخة الإنجليزية.

Prismor

PyPI License OpenSSF Best Practices PRs Welcome X DeepWiki Discord

Runtime security for Claude Code, Codex, Langchain and other AI agents frameworks/harness.

Prismor is highly customizable based on user's own policies. Observe or enforce mode to see and control agent activity in a local self-serve dashboard

Website • Onboard with Skill

Claude Code   Codex CLI   Gemini CLI   Cursor   GitHub Copilot   OpenCode   Pi Agent   Kiro   Kimi Code   Trae / Trae CN   Google Antigravity

Plus Grok Build, Crush, OpenHands, Qwen Code, Continue CLI, Goose, Hermes, OpenClaw, Devin CLI, Factory Droid, Aider, and more — see AGENT_INTEGRATIONS.md for the full coverage matrix
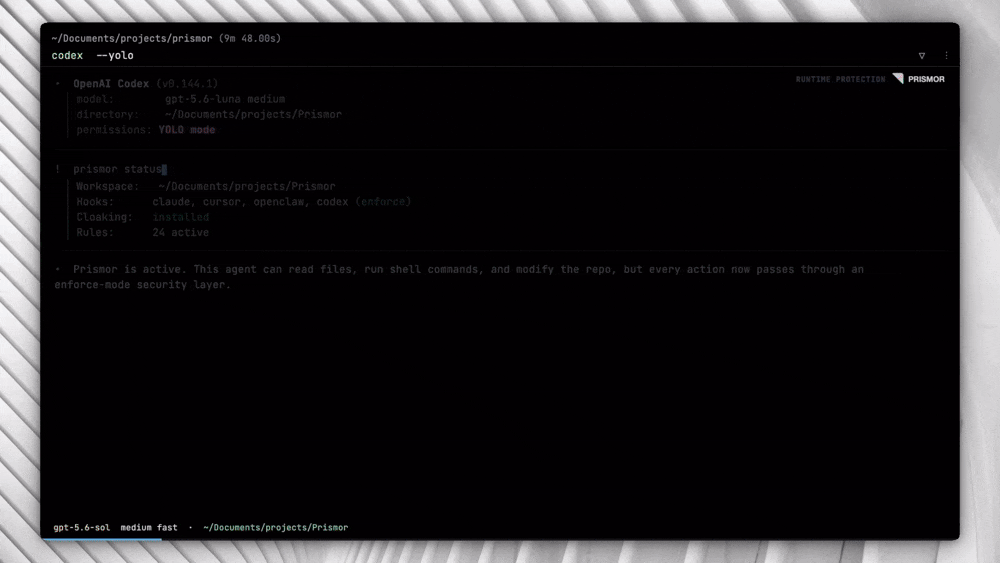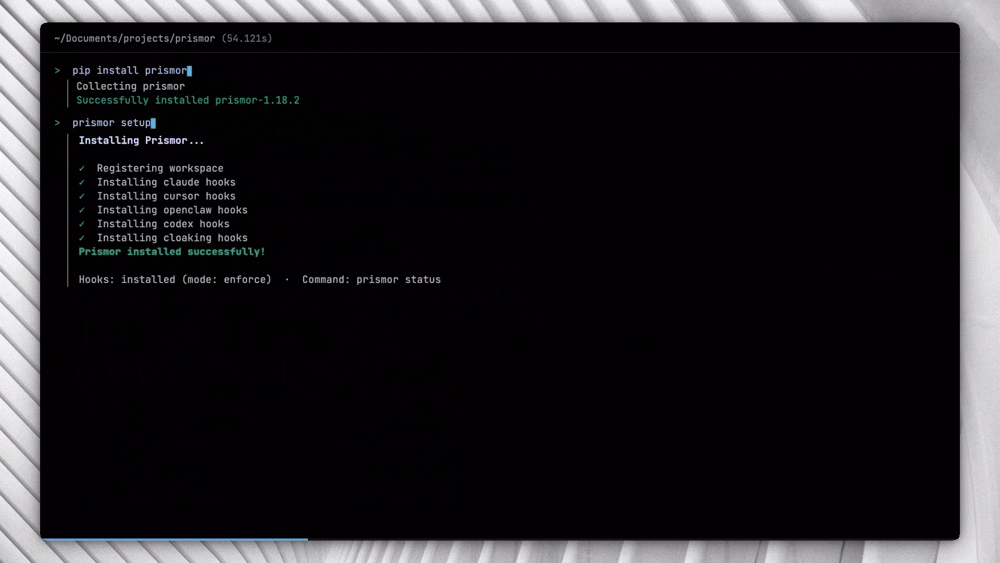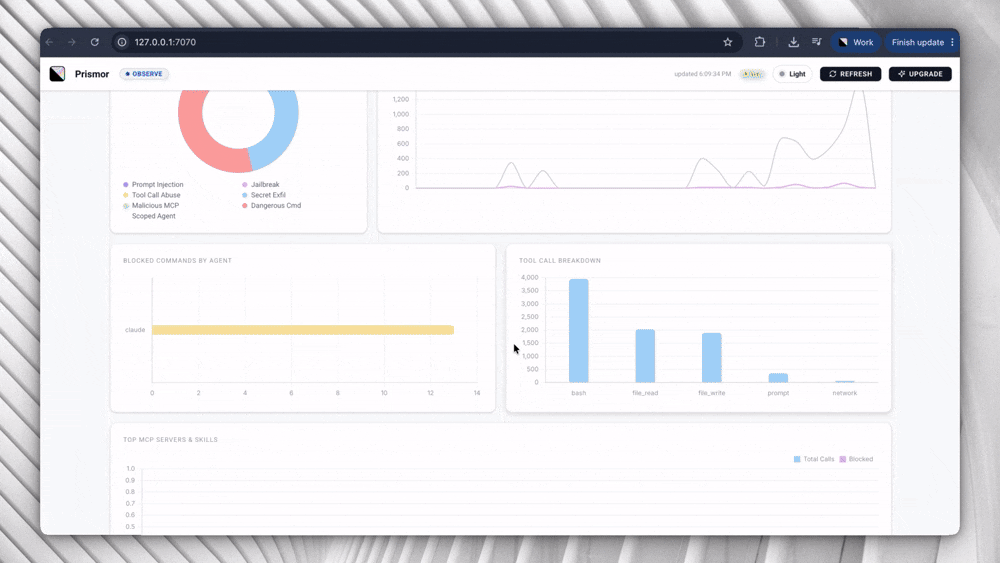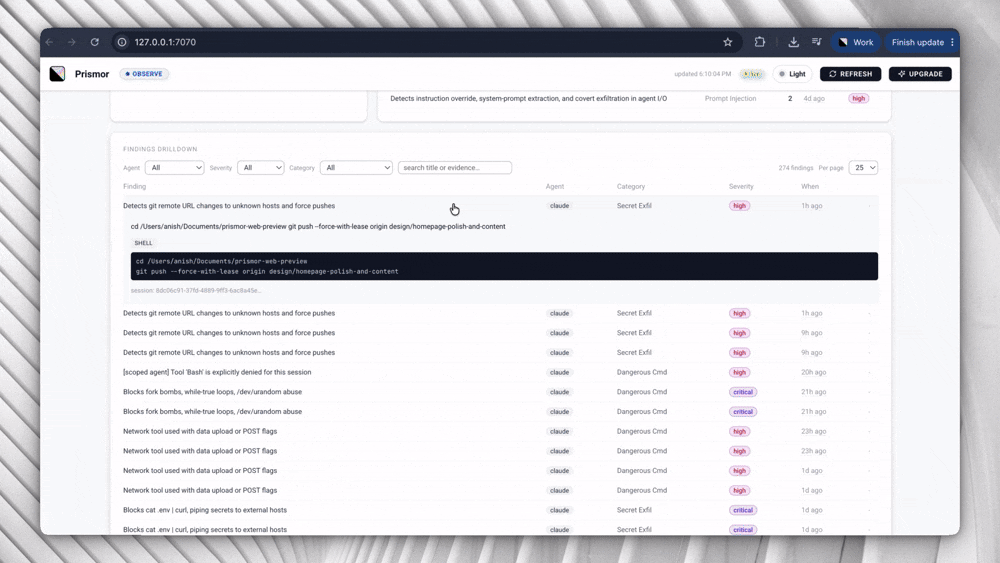

Prismor demo: pip install prismor, prismor setup, then the dashboard's overview, sessions, extensions and MCP servers views


The Problem

AI agents execute shell commands, read and write files, access credentials, and call external APIs. They do this autonomously, often across many steps, with limited checkpoints.

This creates risks that traditional security tooling isn't designed for:

  • Prompt injection - malicious content in a file, issue, or web page can redirect the agent mid-task
  • Unintended destructive actions - an agent misinterprets an instruction and runs something irreversible
  • Secret exfiltration - an agent reads .env or credential files as part of a debugging task and sends the content outbound
  • Lack of visibility and identity - an agent can spawn subagents and lack complete visibility for the end user
  • Privilege escalation - an agent modifies sudoers, CI pipelines, or file permissions to resolve a permission error
  • Dependency manipulation - an agent installs or rewrites a package at the direction of injected input
  • Supply chain risk - an agent installs a vulnerable or 0-day package while optimizing for code velocity

Standard OS-level and endpoint security tools monitor the kernel and filesystem. But they lack the context to make AI usable


Quick Start (30s)

pip install prismor
prismor setup

For the Skill, curl, and git-clone alternatives, plus PEP 668 systems and secret-cloaking setup, see the full installation guide.



Supported Agents

تنزيل الأداة

الأكثر شعبية

عرض الكل →

اكتشف الأدوات الأكثر استخدامًا من قبل مجتمعنا.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 مجموعة أدوات OSINT المثالية: رسم بياني للتحقيق، وتقييم الثقة، وعائلات الأسماء المستعارة، وخريطة، وخط زمني، وتقارير. 49 وحدة، وأكثر من 400 موقع، دون الحاجة إلى مفاتيح API.

    500
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    # تطبيق GhostLock للتنفيذ بنقرة واحدة (CVE-2026-43499)

    466
  • 3

    ARTEX

    baarai/artex

    منصة اختبار اختراق مستقلة متعددة الوكلاء تعتمد على LLM، مع وكلاء تخطيط وتنفيذ، ومخططات للأصول والاستكشاف، وتسجيل حركة مرور MITM، وإعادة اختبار الثغرات.

    339
  • 4

    opencti

    opencti-platform/opencti

    منصة مفتوحة لاستخبارات التهديدات السيبرانية

    317
  • 5

    redforge

    cybersecurity91/redforge

    مجموعة أدوات الفريق الأحمر في المتصفح مع 102 أداة دون اتصال للاستطلاع، وتوليد الحمولات، وهجمات بيانات الاعتماد، والتشفير، والترميز، وإعداد تقارير المهام.

    307
  • 6

    estorides

    grisuno/estorides

    يجمع أكثر من 99 مصدرًا مجانيًا من مصادر OSINT بالتوازي، ويحوّل الكيانات إلى رسم بياني معرفي، ويصدّر بصيغة STIX 2.1 أو MISP أو GraphML مع تحليل بمساعدة LLM.

    294

استكشف جميع الأدوات

تصفح مجموعتنا من الأدوات

عرض جميع الأدوات →