
 msuiche/elegant-bouncer
ELEGANTBOUNCER هي أداة كشف للاستغلالات القائمة على الملفات في الأجهزة المحمولة.


ELEGANTBOUNCER هي أداة كشف لاستغلالات الأجهزة المحمولة القائمة على الملفات.
تستخدم نهجًا مبتكرًا لتحديد التهديدات المتقدمة القائمة على الملفات، مما يلغي الحاجة إلى عينات موجودة في البرية ويتفوق على الطرق التقليدية القائمة على التعبيرات النمطية أو مؤشرات الاختراق (IOCs). في الوقت الحالي، تستهدف بشكل أساسي تحديد الثغرات الأمنية في الأجهزة المحمولة مثل FORCEDENTRY (CVE-2021-30860) وBLASTPASS (CVE-2023-4863، CVE-2023-41064) وTRIANGULATION (CVE-2023-41990).
| اسم التهديد | ثغرات CVE | مدعوم |
|---|---|---|
| FORCEDENTRY | CVE-2021-30860 | ✅ |
| BLASTPASS | CVE-2023-4863، CVE-2023-41064 | ✅ |
| TRIANGULATION | CVE-2023-41990 | ✅ |
| CVE-2025-43300 | CVE-2025-43300 | ✅ |
| CVE-2025-21043 | CVE-2025-21043 | ✅ |
| CVE-2026-32741 | CVE-2026-32741 | ✅ |
| HEIF mask underfill | لا توجد ثغرة CVE (libheif <= 1.21.2) | ✅ |
| CVE-2026-32882 | CVE-2026-32882، CVE-2025-68431 | ✅ |
| CVE-2026-86950 | CVE-2026-86950 | ✅ |

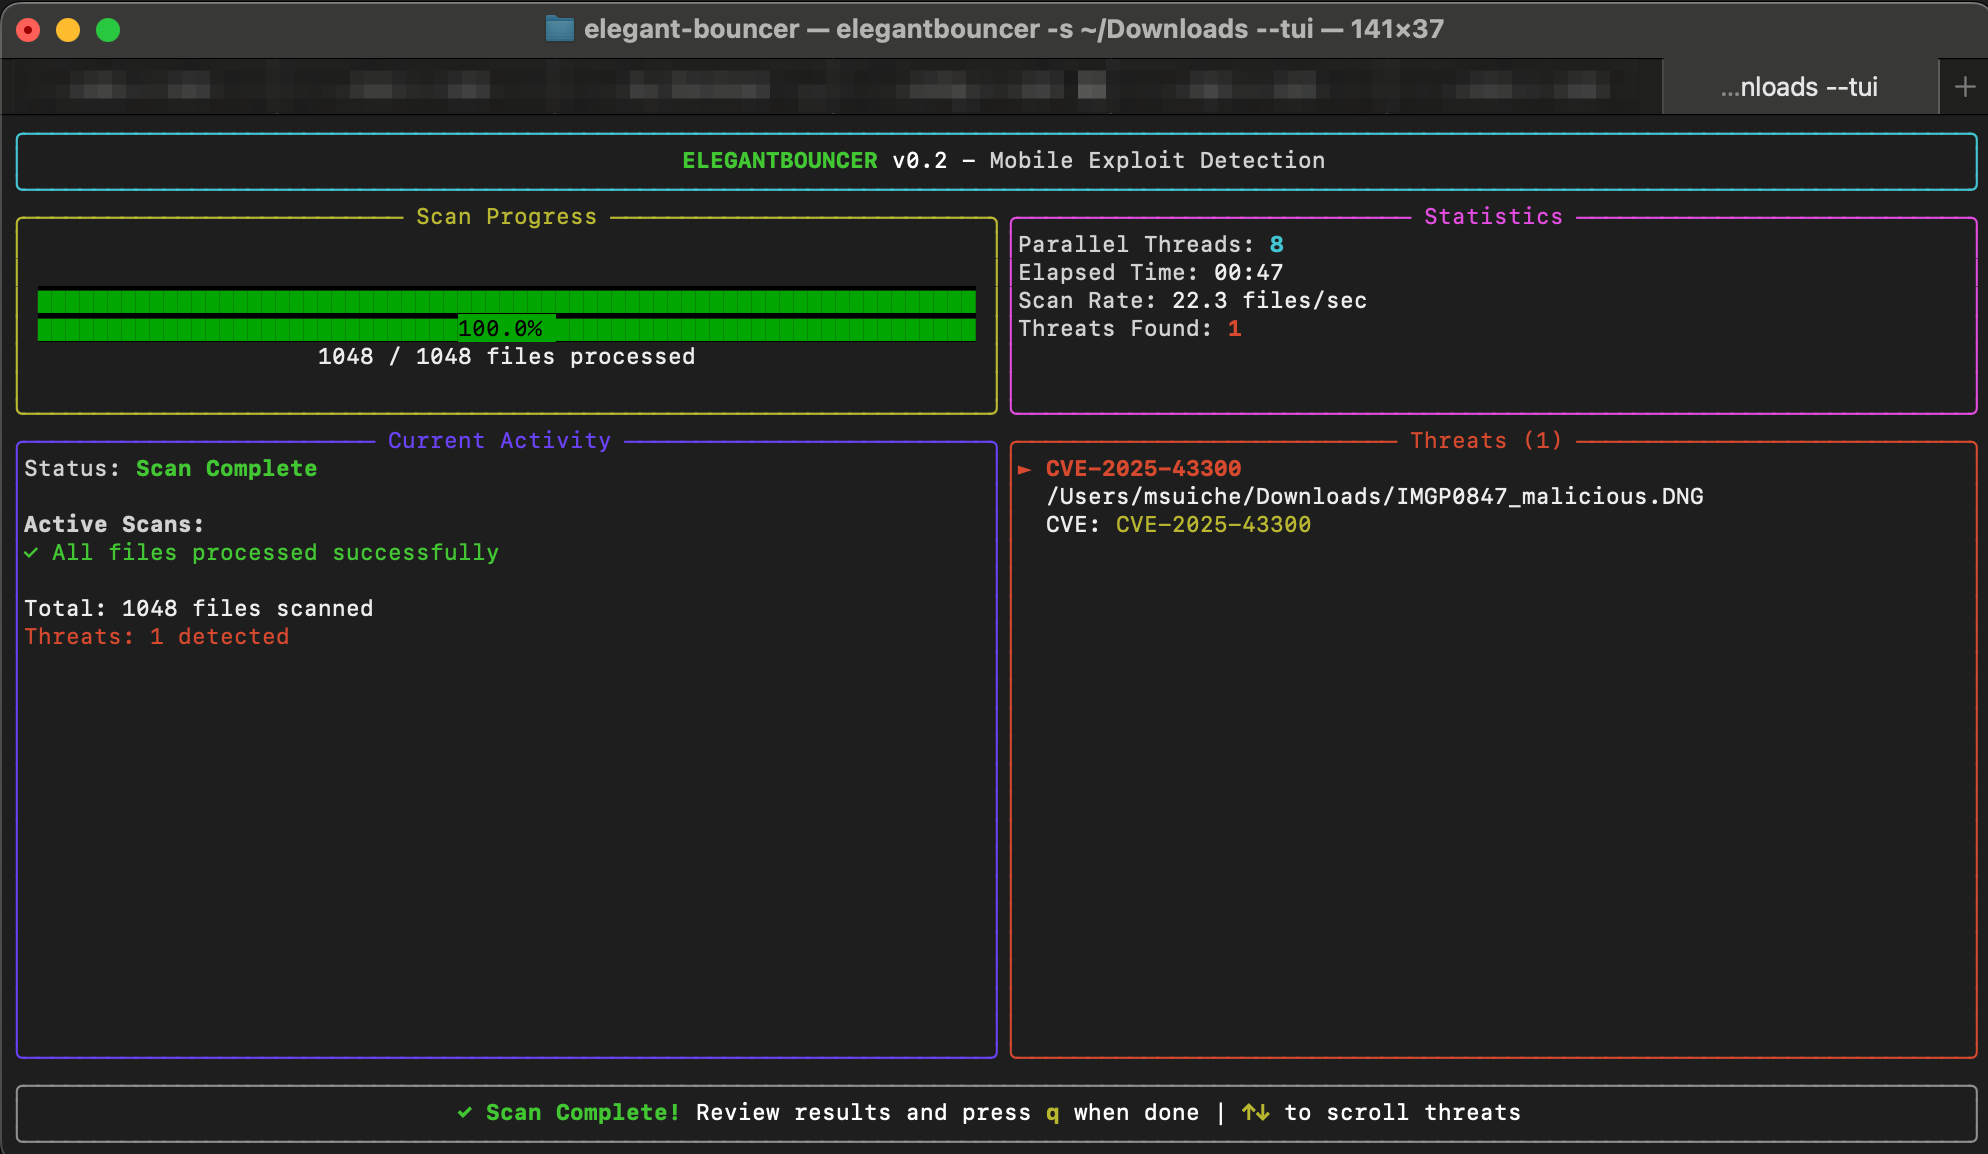
يوفر وضع TUI عرضًا مرئيًا في الوقت الفعلي لعمليات المسح المتوازية، حيث يعرض جميع خيوط العمل النشطة في وقت واحد. قم بتمكينه باستخدام العلامة --tui عند مسح الدلائل.
elegant-bouncer v0.2
ELEGANTBOUNCER Detection Tool
Detection tool for file-based mobile exploits.

A utility designed to detect the presence of known mobile APTs in commonly distributed files.

Usage: elegant-bouncer [OPTIONS] <Input path>

Arguments:
  <Input path>
          Path to the input file or folder

Options:
  -v, --verbose
          Print extra output while parsing

  -s, --scan
          Assess a given file or folder, checking for known vulnerabilities

  -c, --create-forcedentry
          Create a FORCEDENTRY-like PDF

  -r, --recursive
          Recursively scan subfolders

  -m, --messaging
          Scan messaging app databases for attachments (iOS backup format)

  --ios-extract
          Extract/reconstruct iOS backup to readable folder structure

  -o, --output <OUTPUT>
          Output directory for iOS backup extraction

  -f, --force
          Force overwrite of output directory if not empty

  -e, --extensions <EXTENSIONS>
          File extensions to scan (comma-separated, e.g., "pdf,webp,ttf")
          Default: pdf,gif,webp,jpg,jpeg,png,tif,tiff,dng,heic,heif,hif,avif,ttf,otf

  -h, --help
          Print help information (use `-h` for a summary)

  -V, --version
          Print version information
استخدم --scan لتقييم ملف واحد بحثًا عن الثغرات الأمنية المعروفة:
elegantbouncer --scan suspicious_file.pdf
فحص جميع الملفات المدعومة في دليل:
elegantbouncer --scan /path/to/folder
استخدم العلامة -r لفحص جميع المجلدات الفرعية بشكل تكراري:
elegantbouncer --scan /path/to/folder -r
حدد أنواع الملفات التي تريد فحصها باستخدام العلامة -e:
# Scan only PDF and DNG files
elegantbouncer --scan /path/to/folder -e pdf,dng

# Scan only image files recursively
elegantbouncer --scan /path/to/folder -r -e jpg,jpeg,png,webp,gif
بشكل افتراضي، يفحص الأداة الملفات ذات هذه الامتدادات:
عند فحص دليل، توفر الأداة:
[+] Scanning directory: /path/to/documents
[+] Recursive mode enabled
[+] Extensions: pdf, gif, webp, jpg, jpeg, png, tif, tiff, dng, heic, heif, hif, avif, ttf, otf

[1] Scanning: /path/to/documents/invoice.pdf
[2] Scanning: /path/to/documents/photo.jpg
[3] Scanning: /path/to/documents/malicious.webp
  └─ THREAT found: BLASTPASS
[4] Scanning: /path/to/documents/report.pdf
  └─ THREAT found: FORCEDENTRY

[+] Scanned 4 files

[+] Summary Results:
╭────────────────┬───────────────────────────────┬──────────────────────────────────────────────────────────────────────────┬──────────╮
│ name           │ cve_ids                       │ description                                                              │ detected │
├────────────────┼───────────────────────────────┼──────────────────────────────────────────────────────────────────────────┼──────────┤
│ FORCEDENTRY    │ CVE-2021-30860                │ Malicious JBIG2 PDF shared over iMessage                                 │ Yes      │
│ BLASTPASS      │ CVE-2023-4863, CVE-2023-41064 │ Malicious WebP presumably shared over iMessage and other mediums         │ Yes      │
│ TRIANGULATION  │ CVE-2023-41990                │ Maliciously crafted TrueType font embedded in PDFs shared over iMessage  │ No       │
│ CVE-2025-43300 │ CVE-2025-43300                │ Malicious DNG with JPEG Lossless compression exploiting RawCamera.bundle │ No       │
╰────────────────┴───────────────────────────────┴──────────────────────────────────────────────────────────────────────────┴──────────╯

[!] Infected Files Details:
╭────────────────────────────────┬─────────────┬───────────────────────────────╮
│ path                           │ threat_name │ cve_ids                       │
├────────────────────────────────┼─────────────┼───────────────────────────────┤
│ /path/to/documents/report.pdf  │ FORCEDENTRY │ CVE-2021-30860                │
│ /path/to/documents/malicious.webp │ BLASTPASS   │ CVE-2023-4863, CVE-2023-41064 │
╰────────────────────────────────┴─────────────┴───────────────────────────────╯
أعِد بناء نسخة iOS الاحتياطية إلى بنية مجلداتها القابلة للقراءة:
# Extract backup to default location (creates _reconstructed folder)
elegantbouncer --ios-extract /path/to/ios/backup

# Extract to specific output directory
elegantbouncer --ios-extract /path/to/ios/backup -o /path/to/output

# Force overwrite if output directory exists
elegantbouncer --ios-extract /path/to/ios/backup -o /path/to/output --force
افحص نسخة iOS الاحتياطية بحثًا عن مرفقات خبيثة في تطبيقات المراسلة:
# Scan messaging databases (iMessage, WhatsApp, Viber, Signal, Telegram)
elegantbouncer --scan --messaging /path/to/ios/backup






