Skip to content
KitploitKITPLOIT
أدواتالمدونة
Log in
إرسال
أدواتالمدونة
إرسال

أدوات الاختراق واختبار الاختراق والأمن السيبراني لترسانتك الأمنية!

Kitploit هو دليل لأدوات الاختراق والأمن السيبراني واختبار الاختراق. اكتشف آخر تحديثات المشاريع للعثور على الثغرات وتحليل الأنظمة وأتمتة الاختبارات وتعزيز أمنك.

الخلاصاتاتصالالخصوصية© 2026 Kitploit

دليل الأدوات

الفئات

عرض جميع الفئات
Loading categories
agent-bom — AI supply-chain BOM: every agent, MCP server and AI package, and what each one can reach. Open-source scanner and self-hosted control plane for code, containers, cloud and AI. Self-host free; local scans need no account. | Kitploit
أدوات/GitHubGitHub/msaad00/agent-bom
Vulnerability ScannersContainer SecurityCloud SecurityDevSecOpsSecret DetectionThreat IntelligenceSupply Chain SecurityMisconfigurationAI Security
GitHubmsaad00/agent-bom

agent-bom

AI supply-chain BOM: every agent, MCP server and AI package, and what each one can reach. Open-source scanner and self-hosted control plane for code, containers, cloud and AI. Self-host free; local scans need no account.

29788منذ 2 أيامتمت المراجعة من قبل Kitploit
عرض المستودعالموقع الإلكتروني
مشاركة
المحتوى غير متوفر باللغة المطلوبة. عرض النسخة الإنجليزية.

agent-bom — AI supply-chain BOM: supported agents, MCP servers and AI packages, and what each one can reach.

Build PyPI Python 3.11 through 3.14

Apache-2.0 license OpenSSF Scorecard

AI supply-chain BOM: supported agents, MCP servers and AI packages, and what each one can reach.

For AppSec teams and developers who run Claude Code, Cursor, Codex or any MCP client: see which agents, MCP servers, tools and packages are installed, which are vulnerable, and what each one can reach. Local scans need no account.

Quick start · Try in browser · Laptop → team → org · Product tour · Docs

Quick start

From the repository you want to inspect, with uv installed:

uvx agent-bom scan . -f html -o agent-bom-report.html

Open agent-bom-report.html for inventory, findings and fix guidance. Run it again later to see what changed. No MCP configuration in the project? Package findings still apply.

No project handy? uvx agent-bom scan --demo --offline scans a bundled sample. Exit 1 is expected there: the sample trips the security gate. Elsewhere, a non-zero exit can mean a security gate or incomplete assessment; inspect the report and coverage (exit codes, first-run guide).
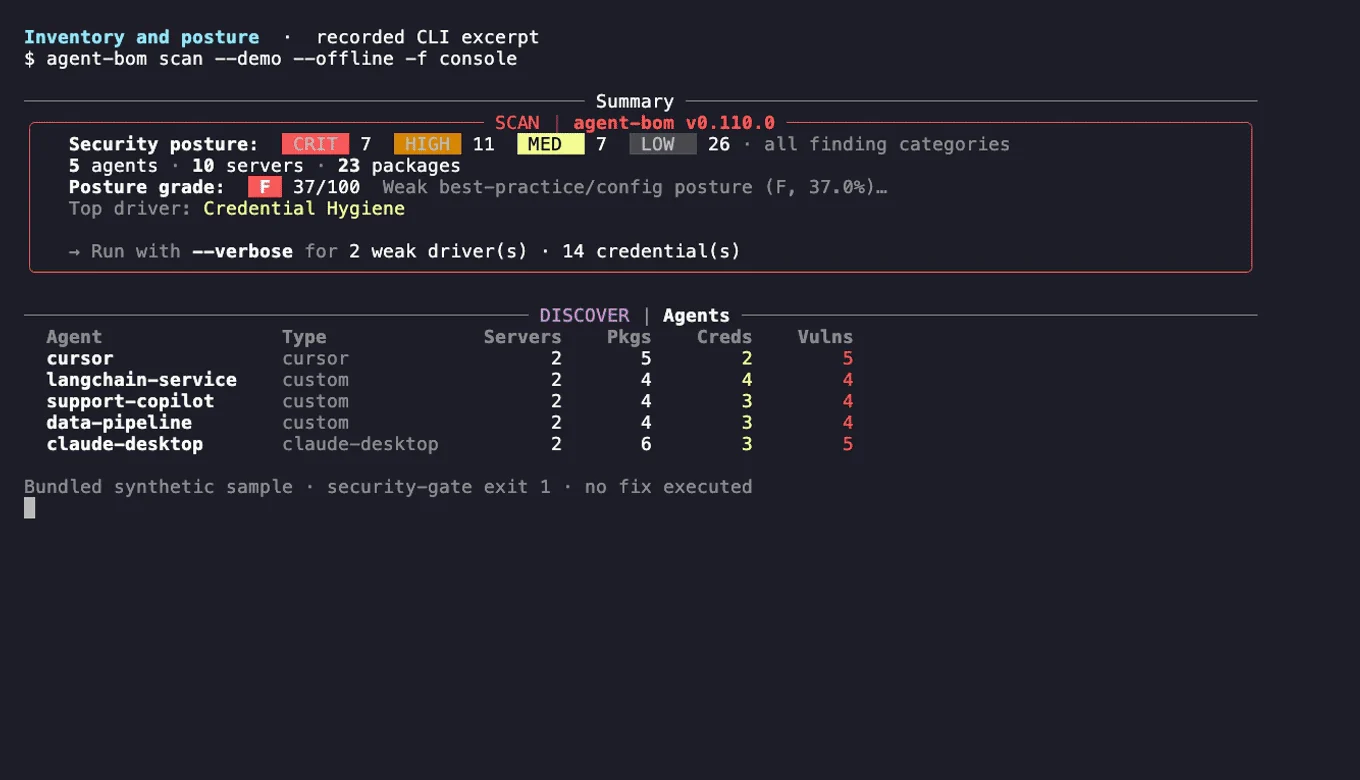
Recorded agent-bom CLI showing sample findings and remediation guidance; no fix executed

What the scan reads and what it does not establish

The scan stays inside this repository: packages, MCP configuration, secrets and personal data, skills and IaC. It does not read agent configuration elsewhere on the machine. Missing evidence is reported as partial, not clean. See what a scan does and does not establish.

From laptop to team to org

  • On your laptop: uvx agent-bom scan . for findings with fixes and a delta on every rescan; claude mcp add agent-bom -- uvx agent-bom mcp server to use agent-bom as a tool inside your coding agent (MCP server, plugins).
  • In your team: uses: koda-ai-studio/agent-bom@v0 on pull requests and a weekly schedule: for a PR gate with a findings comment, SARIF in code scanning and a weekly rescan that catches new CVEs in unchanged code (GitHub Action).
  • Across your org: agent-bom up locally, then Docker Compose or the Helm chart from oci://ghcr.io/koda-ai-studio/charts/agent-bom for retained scans, one graph of agents, MCP servers, packages and credentials, SSO and audit in your own infrastructure (self-host).

All three are free under Apache-2.0 and are adoption paths, not editions. There is no managed cloud offering today; community support runs on GitHub (deployment chooser, support model).

Why an AI supply-chain BOM

A CVE in an AI package, a poisoned tool description or an over-scoped credential matters by what the agent that loads it can reach. A package SBOM stops at packages; agent-bom records the chain, agent → MCP server → tool → package → credential → data, and keeps the evidence for every edge.

Sample production AI environment: Document Intake Agent uses a document-tools MCP server that depends on pillow 9.0.0, linked to KEV-listed CVE-2023-4863; Support Triage Agent uses a ticketing MCP server that references TICKETING_API_KEY, which can access a customer ticket archive

Sample data. What the sample shows

What it covers

Agents and MCP servers, models and AI platforms, dependencies, code, containers and IaC, cloud and data platforms, and a runtime MCP proxy and gateway. Exports are SARIF, CycloneDX, SPDX, JSON and HTML.


Coverage by area
تنزيل الأداة

الأكثر شعبية

عرض الكل →

اكتشف الأدوات الأكثر استخدامًا من قبل مجتمعنا.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 مجموعة أدوات OSINT المثالية: رسم بياني للتحقيق، وتقييم الثقة، وعائلات الأسماء المستعارة، وخريطة، وخط زمني، وتقارير. 49 وحدة، وأكثر من 400 موقع، دون الحاجة إلى مفاتيح API.

    500
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    # تطبيق GhostLock للتنفيذ بنقرة واحدة (CVE-2026-43499)

    466
  • 3

    ARTEX

    baarai/artex

    منصة اختبار اختراق مستقلة متعددة الوكلاء تعتمد على LLM، مع وكلاء تخطيط وتنفيذ، ومخططات للأصول والاستكشاف، وتسجيل حركة مرور MITM، وإعادة اختبار الثغرات.

    339
  • 4

    opencti

    opencti-platform/opencti

    منصة مفتوحة لاستخبارات التهديدات السيبرانية

    317
  • 5

    redforge

    cybersecurity91/redforge

    مجموعة أدوات الفريق الأحمر في المتصفح مع 102 أداة دون اتصال للاستطلاع، وتوليد الحمولات، وهجمات بيانات الاعتماد، والتشفير، والترميز، وإعداد تقارير المهام.

    307
  • 6

    estorides

    grisuno/estorides

    يجمع أكثر من 99 مصدرًا مجانيًا من مصادر OSINT بالتوازي، ويحوّل الكيانات إلى رسم بياني معرفي، ويصدّر بصيغة STIX 2.1 أو MISP أو GraphML مع تحليل بمساعدة LLM.

    294

استكشف جميع الأدوات

تصفح مجموعتنا من الأدوات

عرض جميع الأدوات →