




MemProcFS-Analyzer
MemProcFS-Analyzer.ps1 is a PowerShell script utilized to simplify the usage of MemProcFS and to optimize your memory analysis workflow.
MemProcFS - The Memory Process File System by Ulf Frisk
https://github.com/ufrisk/MemProcFS
Features:
- Fast and easy memory analysis!
- Graphical User Interface (GUI) or Command-Line Interface (CLI)
- Windows PowerShell 5.1 and PowerShell 7 Support
- Easy Configuration via Config.json (e.g. Modules Selection, Process Whitelist, Excel Color Scheme)
- You can mount a memory snapshot (Raw Physical Memory Dump or Microsoft Crash Dump) like a disk image and handle the memory compression feature on Windows
- Auto-Install of MemProcFS, AmcacheParser, AppCompatCacheParser, Elasticsearch, entropy, EvtxECmd, ImportExcel, IPinfo CLI, jq, Kibana, lnk_parser, RECmd, SBECmd, xsv, YARA, and Zircolite
- Auto-Update of MemProcFS, AmcacheParser, AppCompatCacheParser, Elasticsearch, entropy, EvtxECmd (incl. Maps), ImportExcel, IPinfo CLI, jq, Kibana, lnk_parser, RECmd, SBECmd, xsv, YARA, and Zircolite
- Update-Info when there's a new version of ClamAV or a new Dokany File System Library Bundle available
- Pagefile Support
- OS Fingerprinting
- Scan w/ Custom YARA rules (incl. 803 rules by e.g. Chronicle and Elastic Security)
- Multi-Threaded scan w/ ClamAV for Windows (incl. PUA Detection)
- Collection of infected files detected by ClamAV for further analysis (PW: infected)
- Collection of injected modules detected by MemProcFS PE_INJECT for further analysis (PW: infected)
- FindEvil Alerts for Injected Code and Injected Encrypted Payloads (e.g. sleeping Cobalt Strike Beacons)
- Extracting IPv4/IPv6
- IP2ASN Mapping and GeoIP w/ IPinfo CLI → Get your token for free at https://ipinfo.io/signup
- Checking for Suspicious Port Numbers
- Process Tree (TreeView) including complete Process Call Chain (Special thanks to Dominik Schmidt)
- Checking Processes for Unusual Parent-Child Relationships and Number of Instances
- Checking WmiPrvSE.exe for Parent Process Anomalies
- Checking Processes for Unusual User Context
- Checking for Process Path Masquerading and Process Name Masquerading (Damerau Levenshtein Distance)
- Web Browser History (Google Chrome, Microsoft Edge and Firefox)
- Extracting Windows Event Log Files and processing w/ EvtxECmd → Timeline Explorer (EZTools by Eric Zimmerman)
- Event Log Overview
- Processing Windows Event Logs w/ Zircolite - A standalone SIGMA-based detection tool for EVTX (incl. Zircolite Viewer)
- Analyzing extracted Amcache.hve and Amcache SQLite Databases (Inventory*.db) w/ AmcacheParser (EZTools by Eric Zimmerman)
- Analyzing Application Compatibility Cache aka ShimCache w/ AppCompatCacheParser (EZTools by Eric Zimmerman)
- Analyzing Syscache w/ RECmd (EZTools by Eric Zimmerman)
- Analyzing UserAssist Artifacts w/ RECmd (EZTools by Eric Zimmerman)
- Analyzing ShellBags Artifacts w/ RECmd (EZTools by Eric Zimmerman)
- Simple Prefetch View (based on Forensic Timeline)
- Analyzing Auto-Start Extensibility Points (ASEPs) w/ RECmd (EZTools by Eric Zimmerman)
- Analyzing RecentDocs, Office Trusted Document w/ RECmd (EZTools by Eric Zimmerman)
- Analyzing Registry w/ DFIR RECmd Batch File (DFIR Batch File by Andrew Rathbun)
- Analyzing Metadata of Recovered Process Modules (experimental)
- Extracting Windows Shortcut Files (LNK)
- Hunting Malicious Windows Shortcut Files (LNK)
- Integration of PowerShell module ImportExcel by Doug Finke
- CSV output data for analysis w/ Timeline Explorer (e.g. timeline-reverse.csv, findevil.csv, web.csv)
- Collecting Evidence Files (Secure Archive Container → PW: MemProcFS)
- and much more
Download
Download the latest version of MemProcFS-Analyzer from the Releases section.
Usage
Launch Windows PowerShell 5.1 or PowerShell 7 (or Windows PowerShell ISE or Visual Studio Code) as Administrator and open/run MemProcFS-Analyzer.ps1.
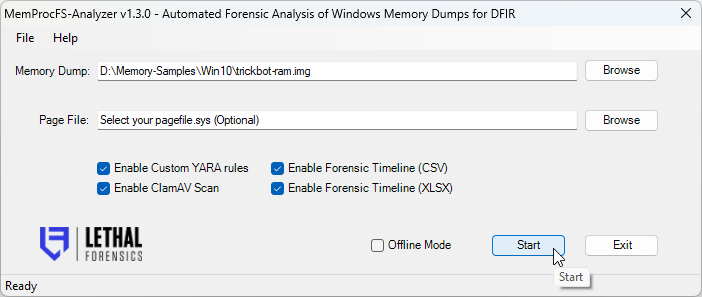
Fig 1: Select your Memory Dump (Raw or Crash Dump) and select your pagefile.sys (Optional)
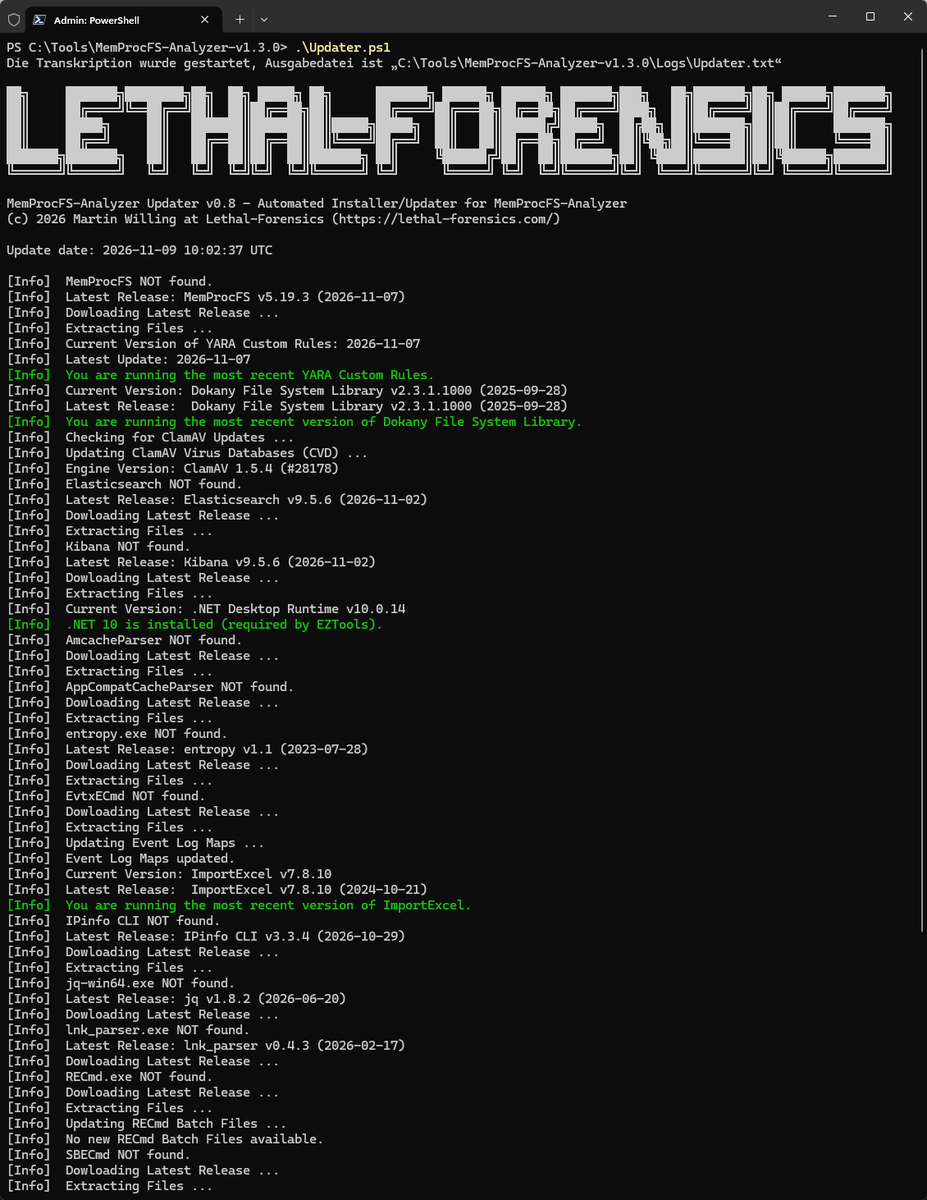
Fig 2: MemProcFS-Analyzer auto-installs dependencies (First Run)
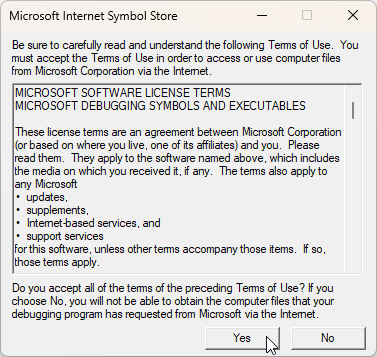
Fig 3: Accept Terms of Use (First Run)
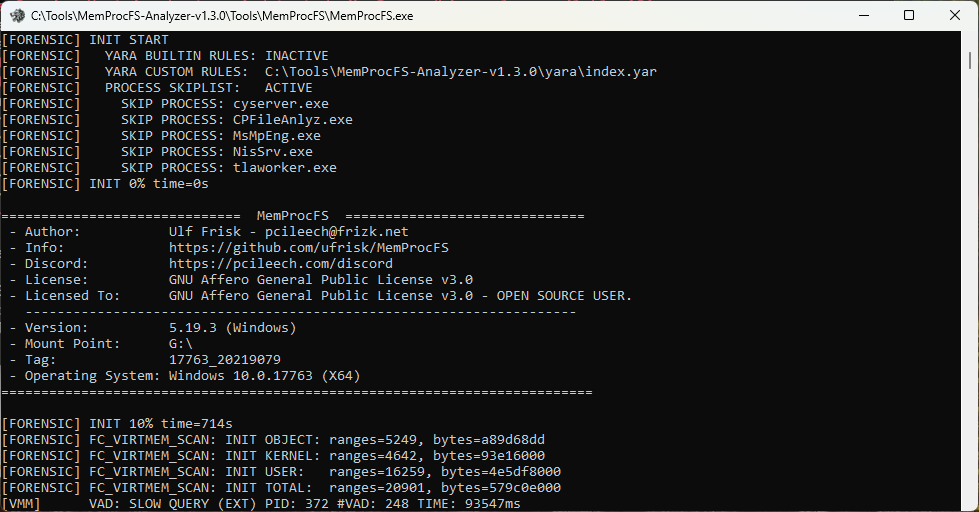
Fig 4: If you find MemProcFS useful, please become a sponsor at: https://github.com/sponsors/ufrisk
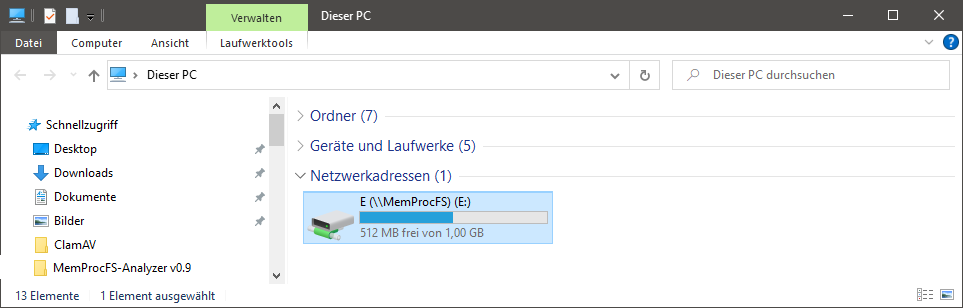
Fig 5: You can investigate the mounted memory dump by exploring drive letter
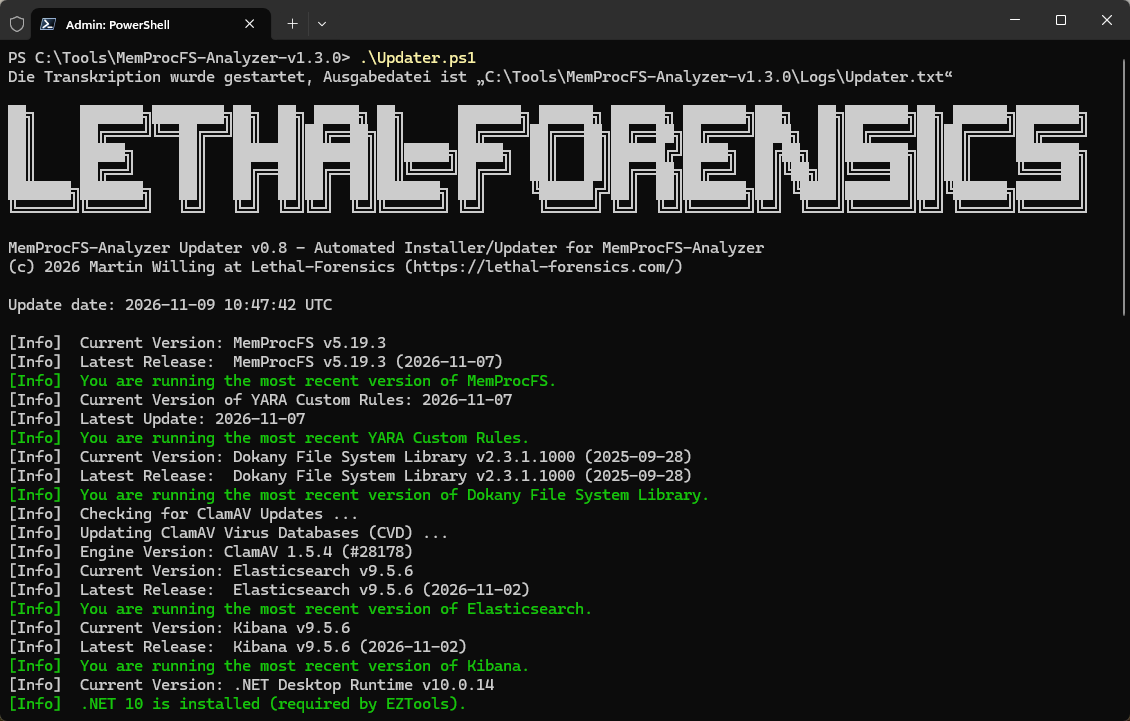
Fig 6: MemProcFS-Analyzer checks for updates (Second Run)

 lethal-forensics/memprocfs-analyzer







