Skip to content
KitploitKITPLOIT
أدواتعمليات الاستغلالالمدونة
Log in
إرسال
أدواتعمليات الاستغلالالمدونة
إرسال

أدوات الاختراق واختبار الاختراق والأمن السيبراني لترسانتك الأمنية!

Kitploit هو دليل لأدوات الاختراق والأمن السيبراني واختبار الاختراق. اكتشف آخر تحديثات المشاريع للعثور على الثغرات وتحليل الأنظمة وأتمتة الاختبارات وتعزيز أمنك.

الخلاصاتاتصالالخصوصية© 2026 Kitploit

دليل الأدوات

الفئات

عرض جميع الفئات
Loading categories
MailAccess — Free email OSINT tool, 2500+ platforms, identity clustering, breach detection. No API keys required. pip install mailaccess | Kitploit
أدوات/GitHubGitHub/katrielmoses/mailaccess
OSINT (Open Source Intelligence)ReconnaissanceVulnerability AnalysisData ExfiltrationForensicsInformation GatheringPenetration TestingSocial EngineeringThreat IntelligenceIdentity & Access Management (IAM)Email Harvesting
31935221منذ يوم واحدتمت المراجعة من قبل Kitploit
مشاركة
GitHub
katrielmoses/mailaccess

MailAccess

Free email OSINT tool, 2500+ platforms, identity clustering, breach detection. No API keys required. pip install mailaccess

عرض المستودع
المحتوى غير متوفر باللغة المطلوبة. عرض النسخة الإنجليزية.

Let's connect
X: @delzynkatriel LinkedIn: /in/katriel-moses

MailAccess: email recon that shows its work

License: MIT Python 3.10+ Docker Compose PyPI version PyPI downloads

mailaccess.pro  ·  Docs  ·  PyPI  ·  Changelog

Open-source email OSINT and email scraper. One email in, every account behind it: 82 modules check 5,300+ platforms, and every finding says how it was found and how sure we are. One domain in, every public email at the company. Run it on your own machine, or use it hosted at mailaccess.pro.


Powered by Netlas: see what runs on every host behind a domain Powered by ipgeolocation.io: IP geolocation and threat intel for every IP Powered by WhoisFreaks: who owned a domain, and what else they registered Partnered with IPBurger: dedicated ISP IPs that stay yours, built for recon Partnered with Mango Proxy: residential IPs that keep big harvests clean

Built for security researchers, OSINT analysts and penetration testers working under authorization. Read DISCLAIMER.md before use.
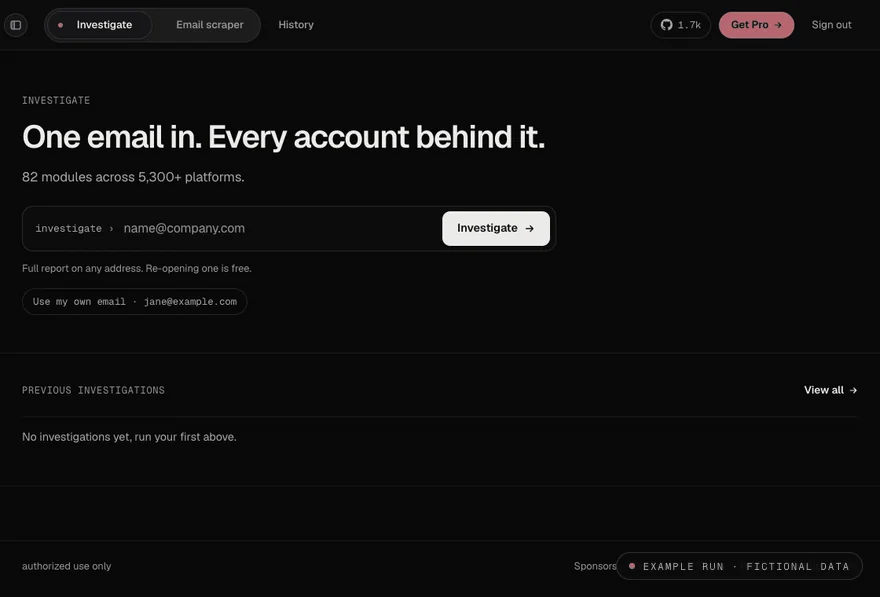
See it run

Example run on the web app: jane@example.com is investigated live, accounts appear as each check returns, then the report opens

Example run with fictional data ([email protected]). The live view, then the report it opens into.

Install

pip install mailaccess
mailaccess investigate [email protected]

Python 3.10+. The CLI starts and stops its backend for each run. Use mailaccess serve for a persistent server, mailaccess[ml] for spaCy name classification, and mailaccess[browser] (then playwright install chromium) for the optional headless-browser checks. Docker and self-hosting: docs/self-hosting.md.

Quick start

mailaccess investigate [email protected]                  # every account behind an email
mailaccess investigate [email protected] -o report.html   # save the report (also .pdf, .md, .json)
mailaccess harvest-emails --domain example.com           # every public email at a domain
mailaccess find-email --name "Jane Doe" --domain example.com
mailaccess login                                         # sign in for your free key
mailaccess doctor                                        # check your setup
mailaccess keys set HIBP_API_KEY your-key                # optional providers
mailaccess upgrade

Pipelines, stdin, JSONL and CI: docs/integrations.md.

What it does

تنزيل الأداة

الأكثر شعبية

عرض الكل →

اكتشف الأدوات الأكثر استخدامًا من قبل مجتمعنا.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 مجموعة أدوات OSINT المثالية: رسم بياني للتحقيق، وتقييم الثقة، وعائلات الأسماء المستعارة، وخريطة، وخط زمني، وتقارير. 49 وحدة، وأكثر من 400 موقع، دون الحاجة إلى مفاتيح API.

    696
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    # تطبيق GhostLock للتنفيذ بنقرة واحدة (CVE-2026-43499)

    499
  • 3

    ARTEX

    baarai/artex

    منصة اختبار اختراق مستقلة متعددة الوكلاء تعتمد على LLM، مع وكلاء تخطيط وتنفيذ، ومخططات للأصول والاستكشاف، وتسجيل حركة مرور MITM، وإعادة اختبار الثغرات.

    396
  • 4

    redforge

    cybersecurity91/redforge

    مجموعة أدوات الفريق الأحمر في المتصفح مع 102 أداة دون اتصال للاستطلاع، وتوليد الحمولات، وهجمات بيانات الاعتماد، والتشفير، والترميز، وإعداد تقارير المهام.

    340
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    نظام العمل للأمن السيبراني الأصلي بالذكاء الاصطناعي — حيث تتحول النية إلى تنفيذ محكوم، وتصبح الأدلة ذاكرة تشغيلية، وكل عملية تحسن التي تليها.

    258
  • 6

    antifox

    antifox-ai/antifox

    منصة اختبار اختراق متعددة الوكلاء ذاتية التشغيل بالذكاء الاصطناعي تُجري الاستطلاع واكتشاف سطح الهجوم والتحقق من الاستغلال وتسليم تقارير مدعومة بالأدلة.

    257

استكشف جميع الأدوات

تصفح مجموعتنا من الأدوات

عرض جميع الأدوات →