
Skip to content
KitploitKITPLOIT
أدواتعمليات الاستغلالالمدونة
Log in
إرسال
أدواتعمليات الاستغلالالمدونة
إرسال

أدوات الاختراق واختبار الاختراق والأمن السيبراني لترسانتك الأمنية!

Kitploit هو دليل لأدوات الاختراق والأمن السيبراني واختبار الاختراق. اكتشف آخر تحديثات المشاريع للعثور على الثغرات وتحليل الأنظمة وأتمتة الاختبارات وتعزيز أمنك.

الخلاصاتاتصالالخصوصية© 2026 Kitploit

دليل الأدوات

الفئات

عرض جميع الفئات
Loading categories
ssh-audit — SSH server & client security auditing (banner, key exchange, encryption, mac, compression, compatibility, security, etc) | Kitploit
أدوات/GitHubGitHub/jtesta/ssh-audit
Vulnerability ScannersNetwork MappingPort ScanningVulnerability AnalysisConfiguration AuditingInformation GatheringNetwork SecurityCryptographyPenetration Testingالأفضل في Network Mapping #13الأفضل في Port Scanning #16
GitHubjtesta/ssh-audit

ssh-audit

SSH server & client security auditing (banner, key exchange, encryption, mac, compression, compatibility, security, etc)

عرض المستودع
4.3k23344منذ 9 أيامتمت المراجعة من قبل Kitploit

الأكثر شعبية

عرض الكل →

اكتشف الأدوات الأكثر استخدامًا من قبل مجتمعنا.

استكشف جميع الأدوات

تصفح مجموعتنا من الأدوات

عرض جميع الأدوات →
مشاركة
المحتوى غير متوفر باللغة المطلوبة. عرض النسخة الإنجليزية.

ssh-audit

License Build Status PRs Welcome

PyPI Downloads Homebrew Downloads Docker Pulls Snap Downloads

Github Sponsors

ssh-audit is a tool for ssh server & client configuration auditing.

jtesta/ssh-audit (v2.0+) is the updated and maintained version of ssh-audit forked from arthepsy/ssh-audit (v1.x) due to inactivity.

  • Features
  • Usage
  • Screenshots
    • Server Standard Audit Example
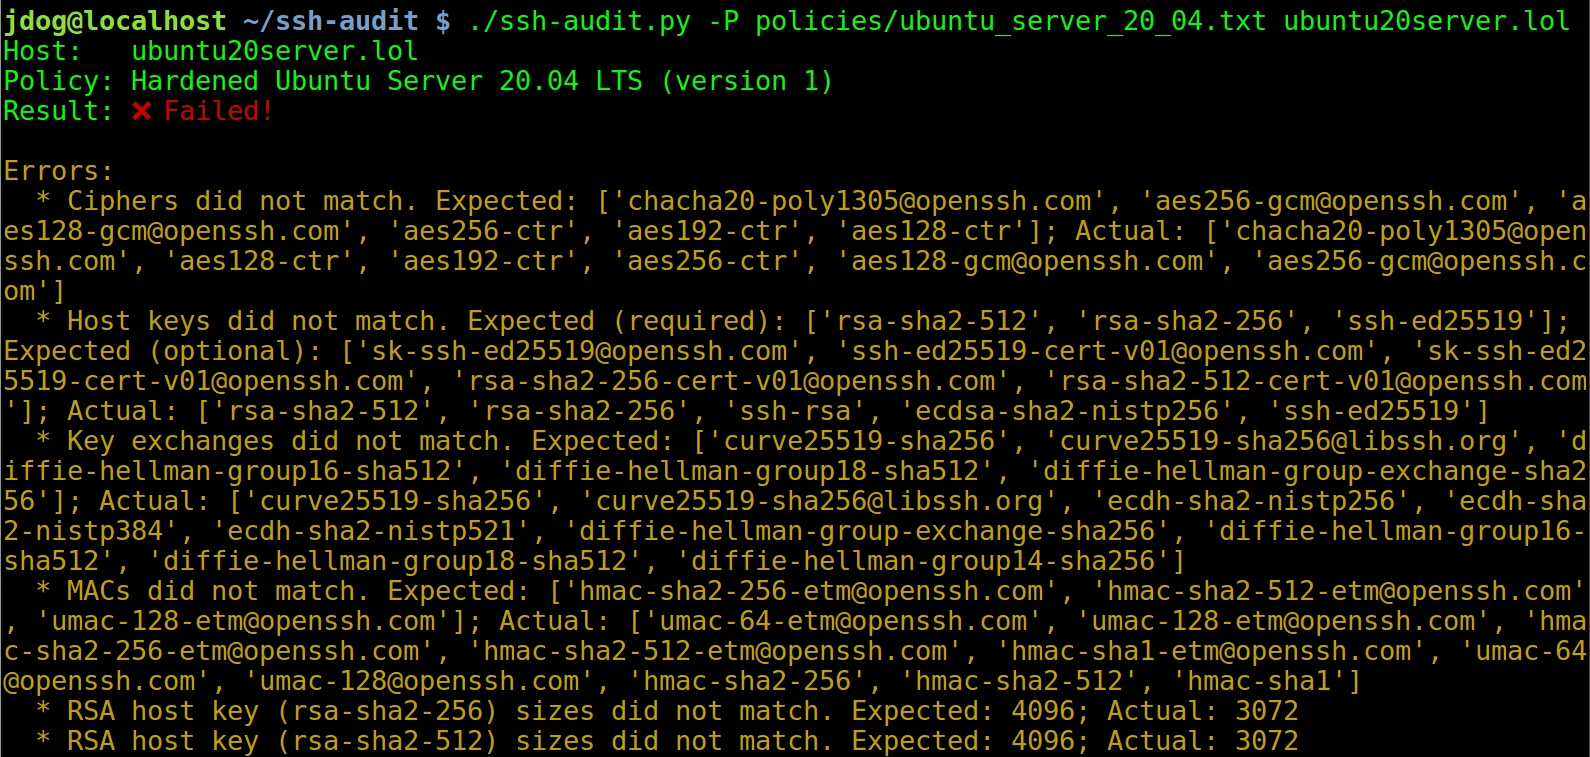
    • Server Policy Audit Example
    • Client Standard Audit Example
  • Hardening Guides
  • Pre-Built Packages
  • Web Front-End
  • ChangeLog

Features

  • analyze SSH both server and client configuration;
  • grab banner, recognize device or software and operating system, detect compression;
  • gather key-exchange, host-key, encryption and message authentication code algorithms;
  • output algorithm security information (available since, removed/disabled, unsafe/weak/legacy, etc);
  • output algorithm recommendations (append or remove based on recognized software version);
  • analyze SSH version compatibility based on algorithm information;
  • historical information from OpenSSH, Dropbear SSH and libssh;
  • policy scans to ensure adherence to a hardened/standard configuration;
  • runs on Linux and Windows;
  • supports Python 3.10 - 3.14;
  • no dependencies

Usage

usage: ssh-audit.py [-h] [-4] [-6] [-b] [-c] [-d]
                    [-g <min1:pref1:max1[,min2:pref2:max2,...]> / <x-y[:step]>]
                    [-j] [-l {info,warn,fail}] [-L] [-M custom_policy.txt]
                    [-m] [-n] [-P "Built-In Policy Name" / custom_policy.txt]
                    [-p N] [-T targets.txt] [-t N] [-v]
                    [--conn-rate-test N[:max_rate]] [--dheat N[:kex[:e_len]]]
                    [--get-hardening-guide platform] [--list-hardening-guides]
                    [--lookup alg1[,alg2,...]] [--skip-rate-test]
                    [--socks5 host:port] [--threads N]
                    [host]

# ssh-audit.py v3.4.1-dev, https://github.com/jtesta/ssh-audit

positional arguments:
  host                  target hostname or IPv4/IPv6 address
تنزيل الأداة