

Read-only Active Directory & Microsoft Entra ID hygiene auditor in pure PowerShell. Collect once, analyze offline: deterministic findings, attack paths, NIS2/ISO 27001/DORA/GDPR mapping, HTML/CSV/JSONL reports, optional AI analysis
                     .
                    / V\
                  / `  /
                 <<   |                IDWolf
                 /    |                Active Directory / Entra hygiene
               /      |
             /        |
           /    \  \ /
          (      ) | |
  ________|   _/_  | |
<__________\______)\__)

Watch the walkthrough · Open the demo report (no install: it is one HTML file of a synthetic domain) · Site
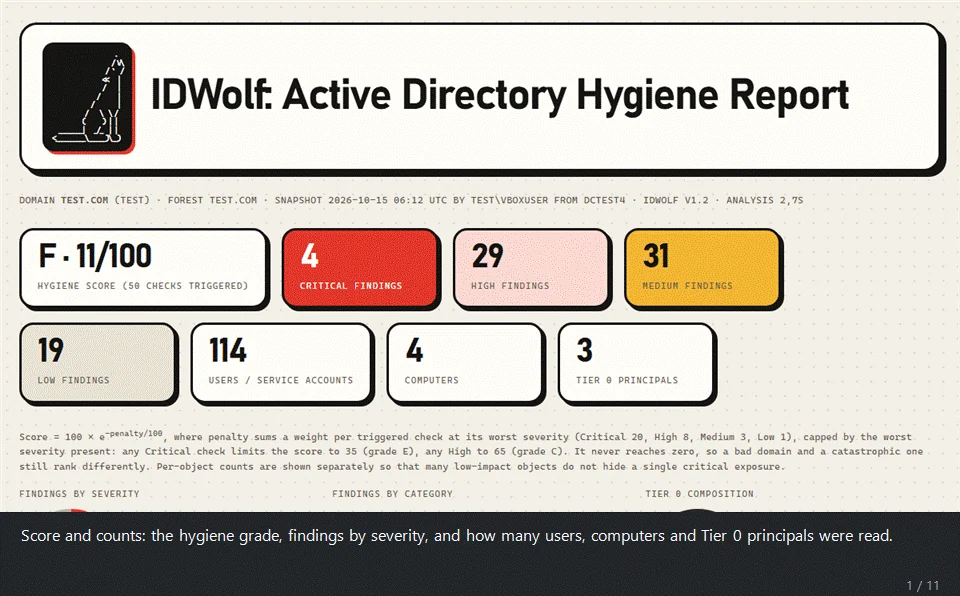
A real report from a throw-away lab domain: the score, the charts, the AI summary with its verdict on chaining the findings into domain compromise, the attack vectors seen in recent attacks, the attack-path map, the Tier 0 members and the findings.
IDWolf is tested on a real Active Directory lab, not only on synthetic data: a
domain populated with Vulnerable-AD
and with the project's own scripts in tests/lab/, which plant ACL chains,
delegation and other misconfigurations.
IDWolf is a hygiene audit for Active Directory and Microsoft Entra ID, written in plain PowerShell. It takes a read-only snapshot of your directory using nothing but the native ActiveDirectory module, then analyzes that snapshot offline and gives you an HTML report, a findings CSV and, if you want, JSON Lines for your SIEM.
On the AD side it runs 186 checks: Kerberos, privileged access, account hygiene, domain configuration, permissions, DNS, AD CS (ESC1-5, 9, 10, 13, 15), operational health (replication, DHCP, backups), host hardening read from the GPOs (SMB and LDAP signing, NTLM, LM hash, user rights) and password quality, all without ever handling a password hash. A separate collector covers Microsoft Entra ID with 92 checks, mapped to the CIS Microsoft 365 benchmark.
If you like, a Gemini step can write an executive summary and a remediation plan. The findings themselves are always computed on your machine, and every directory name is replaced by a token before anything is sent.
The report is one self-contained HTML file, built to be read by the people who have to act on it, not only by the person who ran the audit. A dashboard tab has a score and a grade, an attack-path map and a trust map drawn as SVG, the Tier 0 members, NIS2 / ISO 27001 / DORA / GDPR cards, categories, top risks and charts; a details tab has every finding with its fix. No external libraries, no CDN, nothing loaded from the internet: it opens offline and can be mailed as it is.
GitHub shows HTML files as plain text, so download the samples and open them in a browser:
examples/lab_report.html is the report in the GIF. It comes from the lab
domain (populated with Vulnerable-AD and the tests/lab/ scripts) and
includes the optional Gemini summary.examples/demo_report.html is built on a fictional domain, with
a deep collection, password quality and the optional Gemini summary. Its
findings CSV and JSON Lines sit next to it, together with the exact prompt
that was sent (_ai_prompt.txt) and the reply (_ai_response.json), both
pseudonymized.examples/entra_report.html is the fictional Entra tenant.| Script | Runs on | Needs | Produces |
|---|---|---|---|
Start-IDWolf.ps1 (or Start-IDWolf.cmd) | anywhere | nothing | a menu for everything below |
Collect-ADSnapshot.ps1 | a domain-joined machine | ActiveDirectory module (RSAT), a domain account | AD snapshot JSON |
Collect-EntraSnapshot.ps1 | any machine | Microsoft Graph SDK, Global Reader | Entra snapshot JSON |
Export-PasswordQuality.ps1 | any machine that can reach the PDC (trusted admin host or DC), or an offline NTDS.dit | DSInternals, DCSync rights | password-quality JSON (no hashes) |
IDWolf.ps1 | anywhere | nothing | HTML + CSV + JSONL report |
Export-BloodHound.ps1 | anywhere | nothing | BloodHound CE zip (beta) |
Invoke-IDWolfScheduled.ps1 | a scheduled task | as the collector | collect + analyze with no prompts, a SIEM feed |
You don't have to tell IDWolf.ps1 whether a snapshot is AD or Entra. It
works that out by itself.







