
 dozermx/argus
أداة مسح متعددة المراحل للاستطلاع وسطح الهجوم تقوم بتعيين النطاقات وعناوين IP وأنظمة ASN والأصول السحابية وثغرات CVE في رسم بياني معرفي مع تسجيل درجات CVSS وتعيين الامتثال.





إطار استخبارات أمني
Argus هو إطار استطلاع وتحليل أمني متعدد المراحل، صُمم لاختبار الاختراق الاحترافي وتقييم سطح الهجوم. يعمل بشكل مستقل تمامًا — لا يتطلب مفاتيح API، ولا خدمات خارجية، ولا حسابات. أمر واحد ينتج صورة كاملة عن التعرّض الخارجي للمؤسسة.
argus/
├── sources/          Certificate Transparency, passive DNS, brute force
├── correlators/      DNS resolution, CDN bypass, port scanning
├── intelligence/     43 analysis modules
│   ├── Core          TLS, HTTP, email, content discovery, JS secrets
│   ├── Graph         Attack paths, compliance, CVE, anomaly detection
│   ├── Advanced      SSRF chains, OAuth/GraphQL/WebSocket, BGP, stealth
│   └── Intelligence  Deep CVE, API enumeration, cloud storage, threat intel
├── ontology/         Knowledge graph (NetworkX), entity model, pivot engine
├── output/           HTML report, executive report, CSV, JSON, terminal
└── web/              FastAPI real-time dashboard with WebSocket
يبني المحرك مخطط معرفة لجميع الكيانات المكتشفة — النطاقات وعناوين IP والشهادات والمؤسسات والتقنيات والمنافذ المفتوحة — والعلاقات بينها. كل نتيجة هي شذوذ مرتبط بعقدة في المخطط مع درجة CVSS 3.1 وربط بمسار الهجوم وتخطيط للامتثال.
| النطاق | الفئة | التغطية |
|---|---|---|
| 1–9 | الاستطلاع | جمع سجلات CT، DNS سلبي، AXFR، تخمين قسري للنطاقات الفرعية (أكثر من 2,500 كلمة + توليفات)، تحليل DNS، IPv6، استخبارات ASN، تجاوز أصل CDN |
| 10–17 | تحليل السطح | بصمة TLS، تحليل ترويسات HTTP، اكتشاف المحتوى (أكثر من 100 مسار)، فحص أسرار JavaScript، ثغرات CVE في سلسلة التوريد، تسميم ذاكرة التخزين المؤقت، CORS، فحوصات تهريب HTTP |
| 18–30 | الاستخبارات | أمان البريد الإلكتروني (SPF/DMARC/DKIM)، Wayback Machine، IP عكسي، بصمة JARM لخوادم C2، كشف الشذوذ، تقدير درجات CVSS 3.1، تركيب مسارات الهجوم، تخطيط الامتثال (OWASP/GDPR/ISO 27001/NIST/PCI-DSS)، ربط CVE، تحليلات المخطط، الفرق بين الفحوصات |
| 31–35 | الاختبار النشط | تهريب طلبات HTTP (CL.TE/TE.CL/TE.TE)، الربط بين المؤسسات، توقع النطاقات الفرعية عبر GNN، تحليل المصادقة (النماذج/JWT/المصادقة الأساسية)، تخمين المعاملات (SQLi/XSS/SSRF/IDOR/اجتياز المسار) |
| 36–39 | متقدم | مسار BGP/AS + الربط مع مزودي السحابة، التنقل عبر سلاسل SSRF (البيانات الوصفية السحابية، الخدمات الداخلية، Gopher)، تخمين بروتوكولات OAuth/GraphQL/WebSocket، كشف honeypot |
| 40–43 | استخبارات+ | بصمة CVE العميقة (22 تقنية)، تعداد API/OpenAPI/Swagger، تعداد التخزين السحابي (S3/Azure/GCS/DO)، استخبارات التهديدات (القوائم السوداء في DNS، مخارج Tor، سمعة ASN) |
المتطلبات: Python 3.9+، Linux/macOS/Termux
git clone https://github.com/DozerMx/Argus
cd Argus
pip install -r requirements.txt
واجهة الويب (اختياري):
pip install fastapi uvicorn websockets
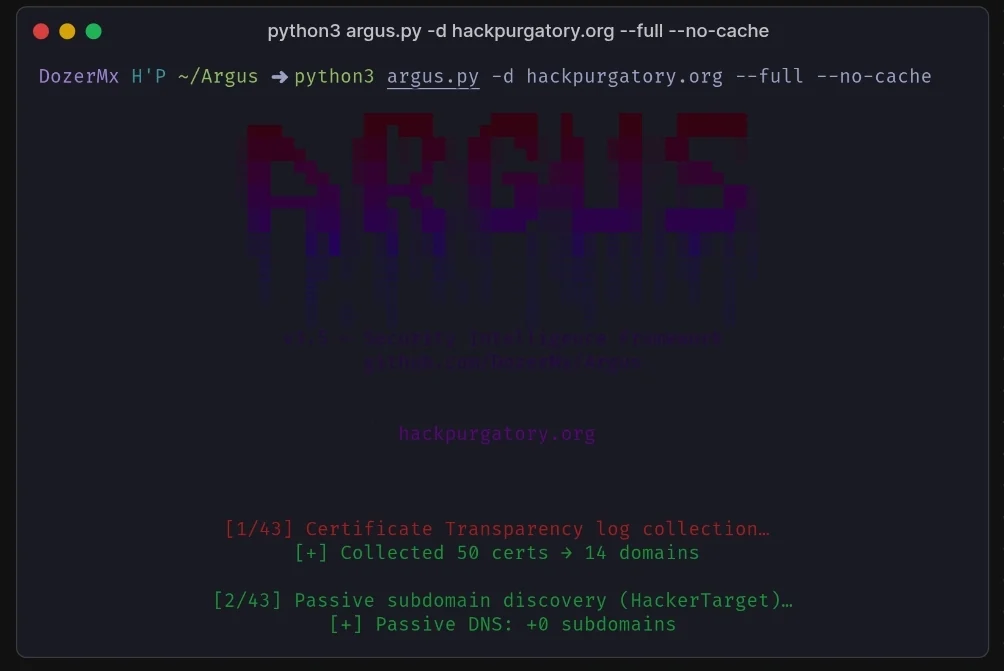
python argus.py -d TARGET [OPTIONS]
# CT log collection + DNS resolution + anomaly detection
python argus.py -d target.com

# Full 43-phase scan
python argus.py -d target.com --full

# Full scan with executive report
python argus.py -d target.com --full --output executive

# Full scan with authentication and fuzzing
python argus.py -d target.com --full --fuzz --auth

# Scan with known credentials
python argus.py -d target.com --full --auth --user admin --password admin123
# Subdomain brute force + AXFR
python argus.py -d target.com --brute --axfr

# Deep infrastructure: ASN + CDN bypass + ports
python argus.py -d target.com --deep --cdn-bypass --ports

# Stealth scan (paranoid jitter profile)
python argus.py -d target.com --full --stealth-profile paranoid

# Through Tor
python argus.py -d target.com --full --proxy socks5://127.0.0.1:9050
# Bulk scan from file
python argus.py -f targets.txt --full --output json

# Continuous monitoring with Slack alerts
python argus.py -d target.com --daemon --webhook https://hooks.slack.com/...

# Web UI dashboard
python argus.py --serve --ui-port 8080
Target:
  -d DOMAIN             Single target domain
  -f FILE               File with one domain per line

Scan Modules:
  --full                Enable all modules
  --deep                ASN, cloud detection, Wayback, reverse IP
  --brute               Subdomain brute force + permutations
  --axfr                DNS zone transfer
  --cdn-bypass          CDN/WAF origin IP discovery
  --ports               TCP port scan + banner grab (178 ports)
  --jarm                JARM TLS fingerprinting
  --fuzz                Parameter fuzzing (SQLi, XSS, SSRF, IDOR, traversal)
  --auth                Authentication analysis
  --user USER           Username for authenticated scanning
  --password PASS       Password for authenticated scanning

Output:
  --output FORMAT       terminal | html | executive | json | csv
  --outfile PATH        Output file path
  -v                    Verbose logging
  -q                    Quiet mode

Performance:
  --threads N           Concurrent threads (default: 30)
  --timeout N           Request timeout in seconds (default: 10)
  --proxy URL           Proxy (socks5://host:port or http://host:port)
  --no-cache            Disable disk cache
  --stealth-profile     paranoid | careful | normal | aggressive

Web UI:
  --serve               Launch real-time web dashboard
  --ui-port N           Web UI port (default: 8080)

Daemon:
  --daemon              Continuous monitoring mode
  --webhook URL         Webhook URL for alerts (Slack/Telegram)
  --interval N          Scan interval in hours (default: 6)
تصور تفاعلي للمخطط الكامل للبنية التحتية مع النتائج وتقييم المخاطر ورسم العلاقات. ملف واحد مكتفٍ ذاتيًا.
ملخص بلغة الأعمال يتضمن سردًا لمسارات الهجوم، وانتهاكات الامتثال حسب الإطار، وخارطة طريق للمعالجة مرتّبة حسب الأولوية، ومصفوفة مخاطر.
مخرجات كاملة قابلة للقراءة آليًا تشمل مخطط المعرفة الكامل، وجميع الشذوذات مع درجات CVSS، ومسارات الهجوم، وبيانات الفحص الوصفية. مناسبة للتكامل مع SIEM أو أنظمة التذاكر أو الأدوات المخصصة.

