
Skip to content
KitploitKITPLOIT
أدواتعمليات الاستغلالالمدونة
Log in
إرسال
أدواتعمليات الاستغلالالمدونة
إرسال

أدوات الاختراق واختبار الاختراق والأمن السيبراني لترسانتك الأمنية!

Kitploit هو دليل لأدوات الاختراق والأمن السيبراني واختبار الاختراق. اكتشف آخر تحديثات المشاريع للعثور على الثغرات وتحليل الأنظمة وأتمتة الاختبارات وتعزيز أمنك.

الخلاصاتاتصالالخصوصية© 2026 Kitploit

دليل الأدوات

الفئات

عرض جميع الفئات
Loading categories
cartography — Pulls infrastructure assets and their relationships from 30+ cloud, identity, and SaaS platforms into a Neo4j graph for security queries and rule-based analysis. | Kitploit
أدوات/GitHubGitHub/cartography-cncf/cartography
Cloud Infrastructure SecurityContainer SecurityNetwork MappingVulnerability AnalysisConfiguration AuditingInformation GatheringCloud SecurityDevSecOpsThreat IntelligenceIdentity & Access Management (IAM)Supply Chain Security
4.2k611140منذ 8س 39دتمت المراجعة من قبل Kitploit
GitHubcartography-cncf/cartography

cartography

Pulls infrastructure assets and their relationships from 30+ cloud, identity, and SaaS platforms into a Neo4j graph for security queries and rule-based analysis.
عرض المستودعالموقع الإلكتروني
مشاركة
المحتوى غير متوفر باللغة المطلوبة. عرض النسخة الإنجليزية.
Cartography

OpenSSF Scorecard OpenSSF Best Practices build

Documentation

Cartography is a Python tool that pulls infrastructure assets and their relationships into a Neo4j graph database.

What it connects: AWS, GCP, Azure, Kubernetes, GitHub, Okta, Entra ID, CrowdStrike, and 30+ more platforms.

Questions it answers:
  • Which identities have access to which datastores? How about across multiple tenants, or providers?
  • Am I affected by any critical vulnerabilities or compromised software packages?
  • What are the network paths in and out of my environment?
  • Which compute instances are exposed to the internet?
  • What AI agents are running in production, and what permissions do they have?

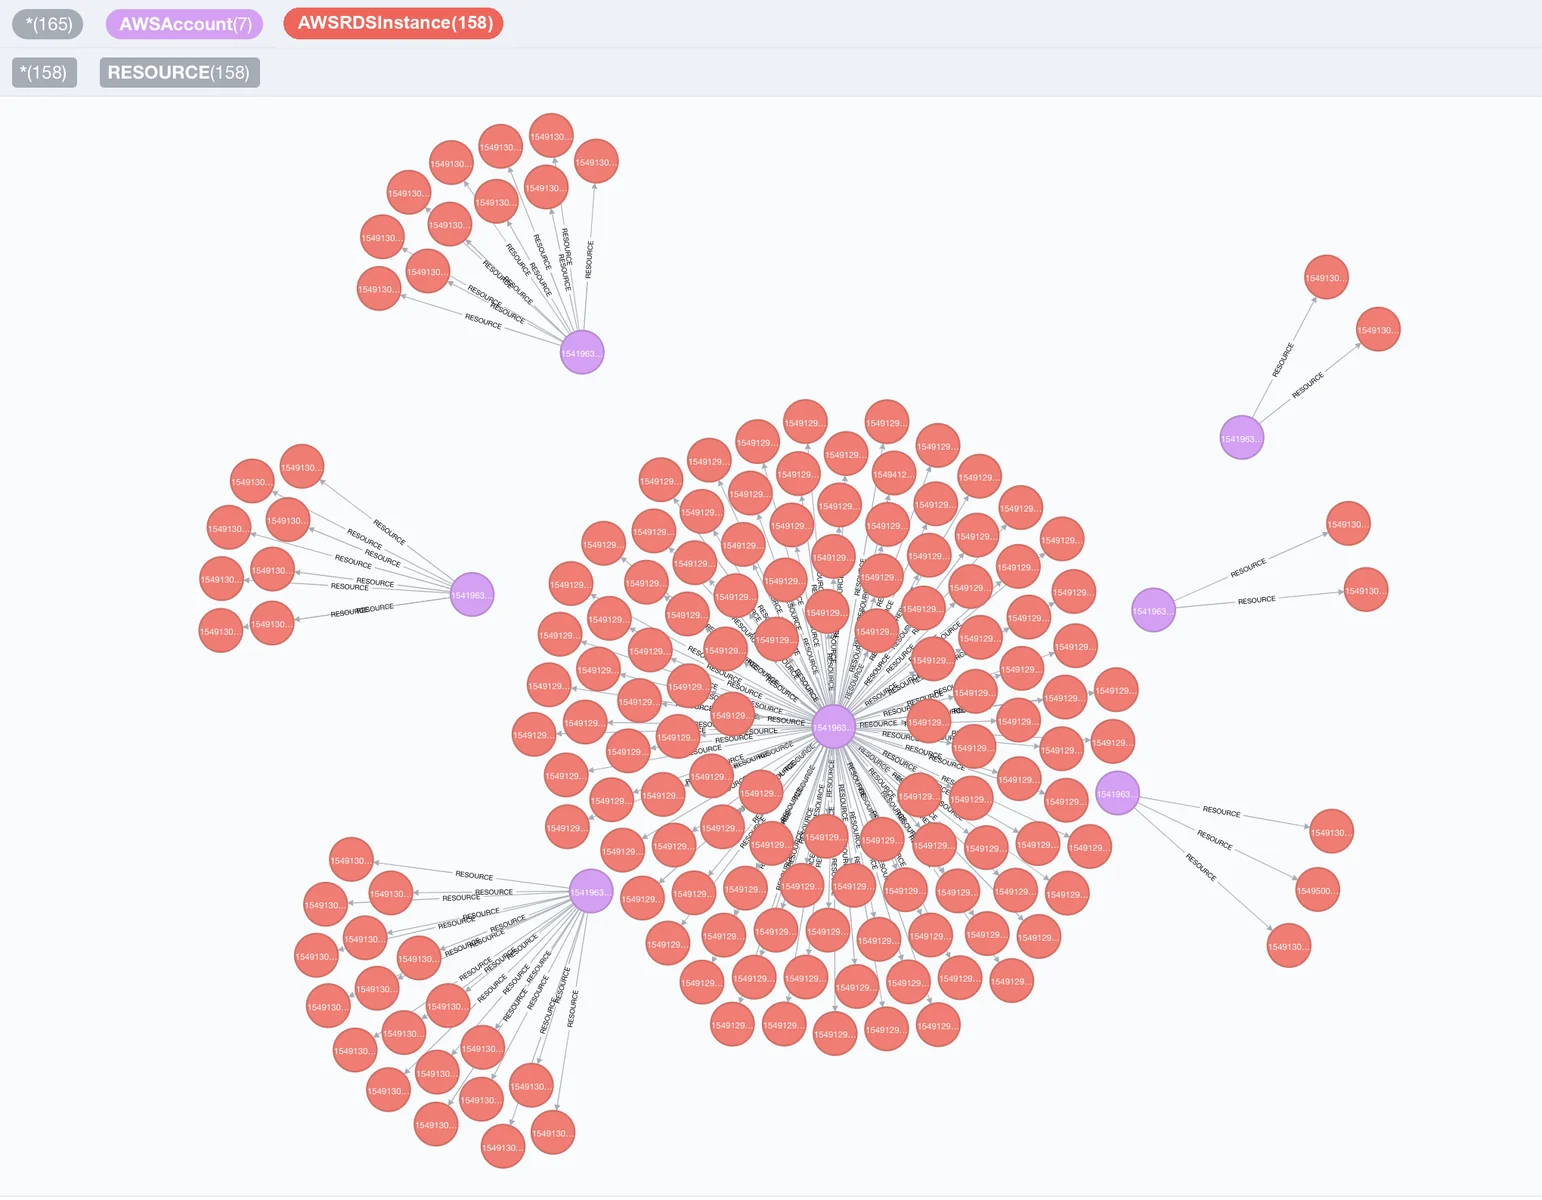
Visualization of RDS nodes and AWS nodes

Quick Start

Install Cartography

pip install cartography

Install cartography[neo4j-rust] instead to swap in Neo4j's Rust Bolt codec, which cuts sync time by roughly 20-30%. See Faster Neo4j driver.

Start Neo4j database

docker run -d --publish=7474:7474 --publish=7687:7687 -v data:/data --env=NEO4J_AUTH=none neo4j:5-community

Confirm that http://localhost:7474 is up.

Sync your first data source (AWS example)

Ensure your AWS credentials and default region are configured (e.g. via AWS_PROFILE, AWS_DEFAULT_REGION, or ~/.aws/config). See AWS credentials docs for reference.

Run Cartography:

cartography --neo4j-uri bolt://localhost:7687 --selected-modules aws

See the full install guide for other platforms.

Query the graph

Open http://localhost:7474 and try:

// Find unencrypted RDS instances by account
MATCH (a:AWSAccount)-[:RESOURCE]->(rds:AWSRDSInstance{storage_encrypted:false})
RETURN a.name, rds.id
// Find EC2 instances exposed to the internet
MATCH (instance:AWSEC2Instance{exposed_internet: true})
RETURN instance.instanceid, instance.publicdnsname

See the querying tutorial and data schema for more use-cases.

Run security rules

Once Cartography has populated the reachable Neo4j graph, list, inspect, and run security rules. This quickstart uses the no-auth Neo4j container started above, so no password is required:

cartography-rules list
cartography-rules list object_storage_public
cartography-rules run object_storage_public

For authenticated Neo4j, set NEO4J_PASSWORD or use one of the other secure password options in the rules docs.

Supported platforms

Click to expand full list of 30+ supported platforms
تنزيل الأداة

الأكثر شعبية

عرض الكل →

اكتشف الأدوات الأكثر استخدامًا من قبل مجتمعنا.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 مجموعة أدوات OSINT المثالية: رسم بياني للتحقيق، وتقييم الثقة، وعائلات الأسماء المستعارة، وخريطة، وخط زمني، وتقارير. 49 وحدة، وأكثر من 400 موقع، دون الحاجة إلى مفاتيح API.

    871
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    # تطبيق GhostLock للتنفيذ بنقرة واحدة (CVE-2026-43499)

    548
  • 3

    ARTEX

    baarai/artex

    منصة اختبار اختراق مستقلة متعددة الوكلاء تعتمد على LLM، مع وكلاء تخطيط وتنفيذ، ومخططات للأصول والاستكشاف، وتسجيل حركة مرور MITM، وإعادة اختبار الثغرات.

    383
  • 4

    redforge

    cybersecurity91/redforge

    مجموعة أدوات الفريق الأحمر في المتصفح مع 102 أداة دون اتصال للاستطلاع، وتوليد الحمولات، وهجمات بيانات الاعتماد، والتشفير، والترميز، وإعداد تقارير المهام.

    361
  • 5

    looking-glass

    anonghosty/looking-glass

    منصة CSIRT تستقبل تقارير Shadowserver في MongoDB وتعيد عرضها كخرائط تفاعلية وتحليلات ونتائج وإرشادات ولوحات معلومات تنفيذية.

    305
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    نظام العمل للأمن السيبراني الأصلي بالذكاء الاصطناعي — حيث تتحول النية إلى تنفيذ محكوم، وتصبح الأدلة ذاكرة تشغيلية، وكل عملية تحسن التي تليها.

    280

استكشف جميع الأدوات

تصفح مجموعتنا من الأدوات

عرض جميع الأدوات →







