
 ashrafzaryouh/cve-2026-21962
استشارة بشأن CVE-2026-21962، وهو تجاوز حرج للمصادقة دون مصادقة في Oracle HTTP Server وإضافات وكيل WebLogic، مع الإصدارات المتأثرة ومؤشرات الكشف وإرشادات التخفيف.



🔥 ثغرة بأقصى درجة خطورة (10.0) تتيح وصولاً عن بُعد دون مصادقة إلى أنظمة Oracle الوسيطة.
CVE ID        : CVE-2026-21962
Severity      : CRITICAL
Published     : 2026-01-20
Category      : Authentication Bypass
CWE           : CWE-284 (Improper Access Control)
- Authentication boundary is improperly enforced
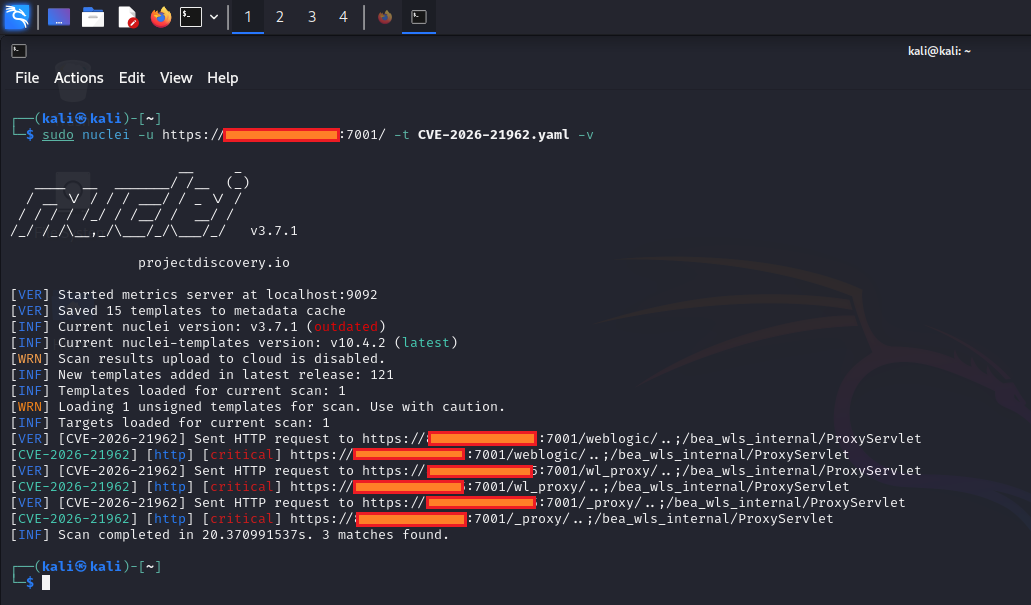
- Crafted HTTP requests bypass access control
+ Direct access to protected backend resources
⚡ لا حاجة لتسجيل الدخول — يتفاعل المهاجم مباشرةً مع الخدمات المكشوفة.
+ Full unauthorized access to application data
+ Data tampering or deletion
+ Backend system exposure through proxy chain
+ Potential lateral movement across services
| السمة | القيمة |
|---|---|
| 🌍 المتجه | الشبكة |
| ⚙️ التعقيد | منخفض |
| ❌ الامتيازات المطلوبة | لا شيء |
| 👤 تفاعل المستخدم | لا شيء |
| 🔄 النطاق | متغيّر |
Apache
IIS
+ Apply latest Oracle Critical Patch Update (Jan 2026)
# Reduce exposure
- Restrict proxy endpoints
- Limit external access
- Enforce network segmentation

# Detection & monitoring
- Enable HTTP request inspection
- Log and analyze anomalies
- Deploy WAF protections
+ Unexpected HTTP requests to proxy endpoints
+ Access without authentication tokens
+ Irregular request patterns or headers
+ Sudden spikes in backend responses
| العامل | التقييم |
|---|---|
| 🔥 الخطورة | حرجة |
| ⚡ قابلية الاستغلال | عالية |
| 💥 التأثير | أقصى |
Entry Point   : HTTP Request
Attack Type   : Remote
Auth Needed   : No
Skill Level   : Low
🚨 الأنظمة المكشوفة على الإنترنت معرّضة لخطر فوري. 🔓 يمكن تجاوز المصادقة بالكامل. 🛠️ قم بالتحديث فوراً أو اعزل الخدمات المتأثرة.
[ Attacker ]
      │
      ▼
[ Crafted HTTP Request ]
      │
      ▼
[ Proxy Bypass ]
      │
      ▼
[ Backend Access ]
      │
      ▼
[ Data Compromise ]
- This vulnerability requires immediate attention
- Delayed patching significantly increases risk
+ Treat as actively exploitable in real-world scenarios







