Skip to content
KitploitKITPLOIT
أدواتعمليات الاستغلالالمدونة
Log in
إرسال
أدواتعمليات الاستغلالالمدونة
إرسال

أدوات الاختراق واختبار الاختراق والأمن السيبراني لترسانتك الأمنية!

Kitploit هو دليل لأدوات الاختراق والأمن السيبراني واختبار الاختراق. اكتشف آخر تحديثات المشاريع للعثور على الثغرات وتحليل الأنظمة وأتمتة الاختبارات وتعزيز أمنك.

الخلاصاتاتصالالخصوصية© 2026 Kitploit

دليل الأدوات

الفئات

عرض جميع الفئات
Loading categories
Hx0-HawkEye — 一个轻量级浏览器抓包与安全分析扩展,在浏览器侧边栏中即可完成抓包、拦截、修改、重放、规则检测与AI辅助分析的完整工作流。(إضافة متصفح خفيفة لالتقاط حركة المرور وتحليل الأمان، تتيح الالتقاط والاعتراض والتعديل وإعادة الإرسال والكشف القائم على القواعد والتحليل المدعوم بالذكاء الاصطناعي - كل ذلك من الشريط الجانبي للمتصفح.) | Kitploit
أدوات/GitHubGitHub/asaotomo/hx0-hawkeye
التقاط وتحليل الحزمماسحات الثغرات الأمنيةبروكسيات الويب والاعتراضاختبار أمان APIأمن الويبالاختبار العشوائيCTFاختبار الاختراقالتعلم والتعليمأمن الذكاء الاصطناعي
GitHubasaotomo/hx0-hawkeye
60679منذ 6 أيامتمت المراجعة من قبل Kitploit

Hx0-HawkEye

一个轻量级浏览器抓包与安全分析扩展,在浏览器侧边栏中即可完成抓包、拦截、修改、重放、规则检测与AI辅助分析的完整工作流。(إضافة متصفح خفيفة لالتقاط حركة المرور وتحليل الأمان، تتيح الالتقاط والاعتراض والتعديل وإعادة الإرسال والكشف القائم على القواعد والتحليل المدعوم بالذكاء الاصطناعي - كل ذلك من الشريط الجانبي للمتصفح.)

عرض المستودعالموقع الإلكتروني

الأكثر شعبية

عرض الكل →

اكتشف الأدوات الأكثر استخدامًا من قبل مجتمعنا.

استكشف جميع الأدوات

تصفح مجموعتنا من الأدوات

عرض جميع الأدوات →
مشاركة
المحتوى غير متوفر باللغة المطلوبة. عرض النسخة الإنجليزية.

🦅 Hx0 HawkEye: Full-stack lightweight capture & AI security auditing extension

【中文 / English】

1. What it is

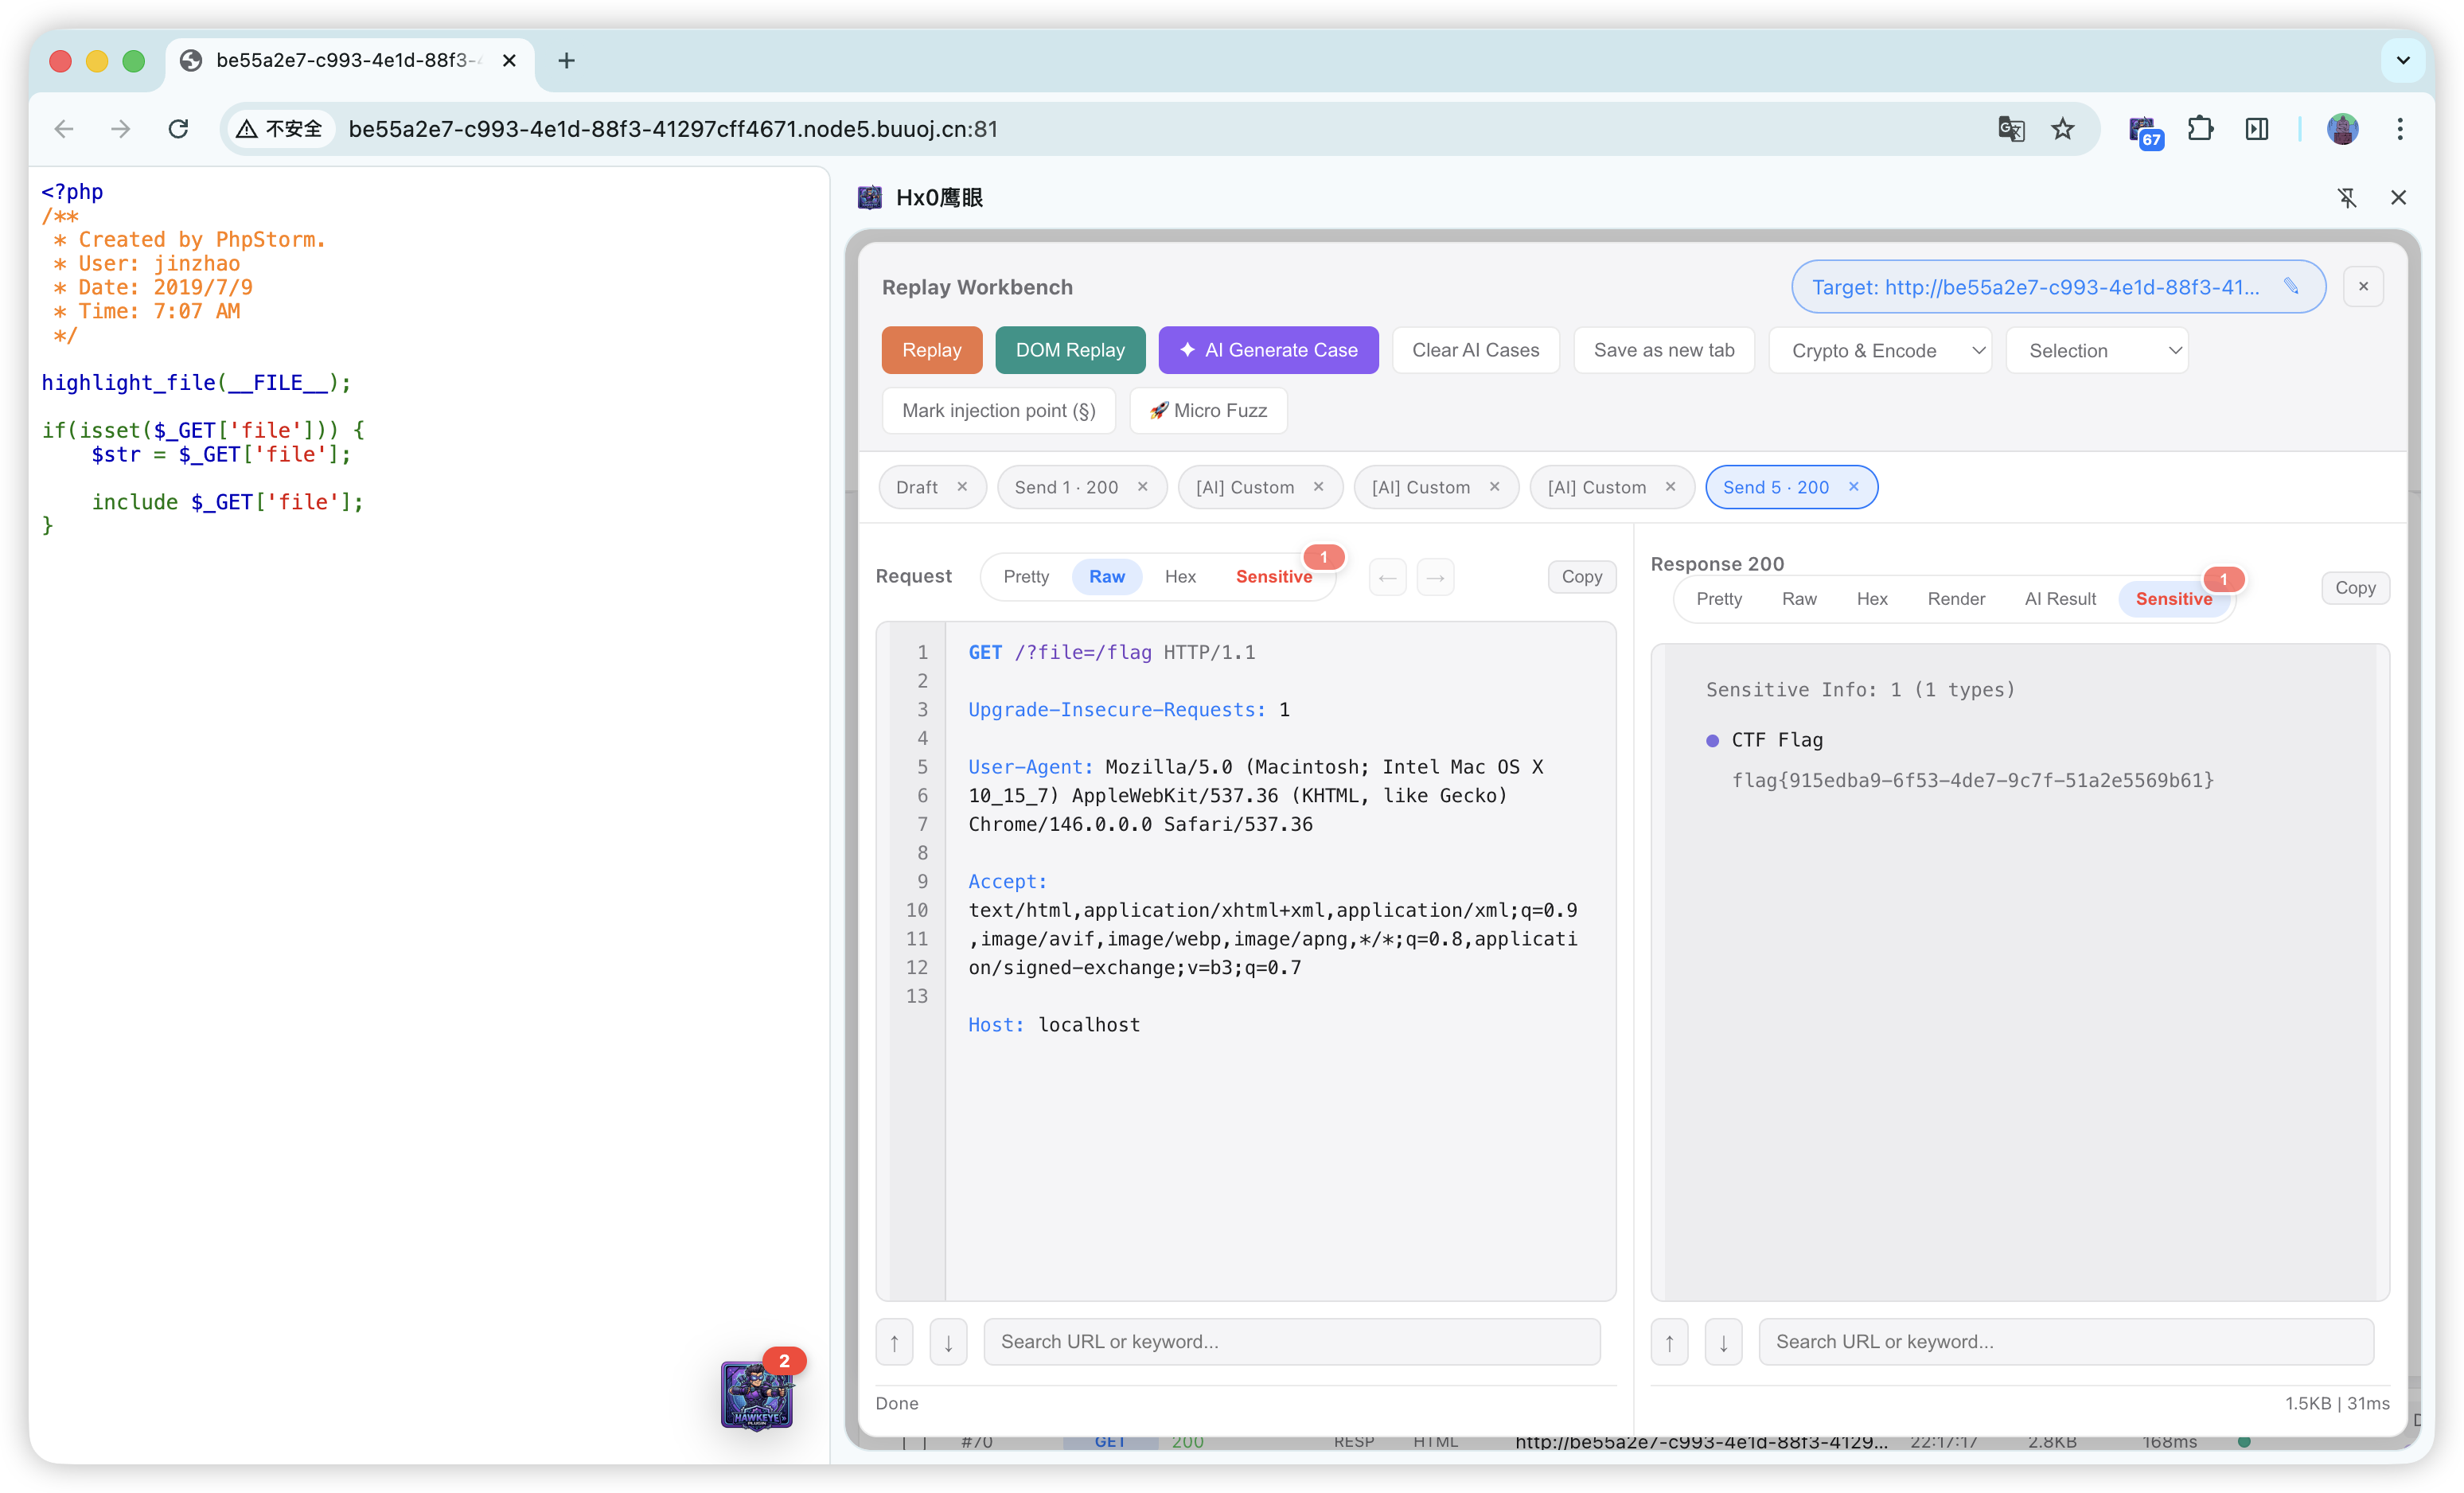
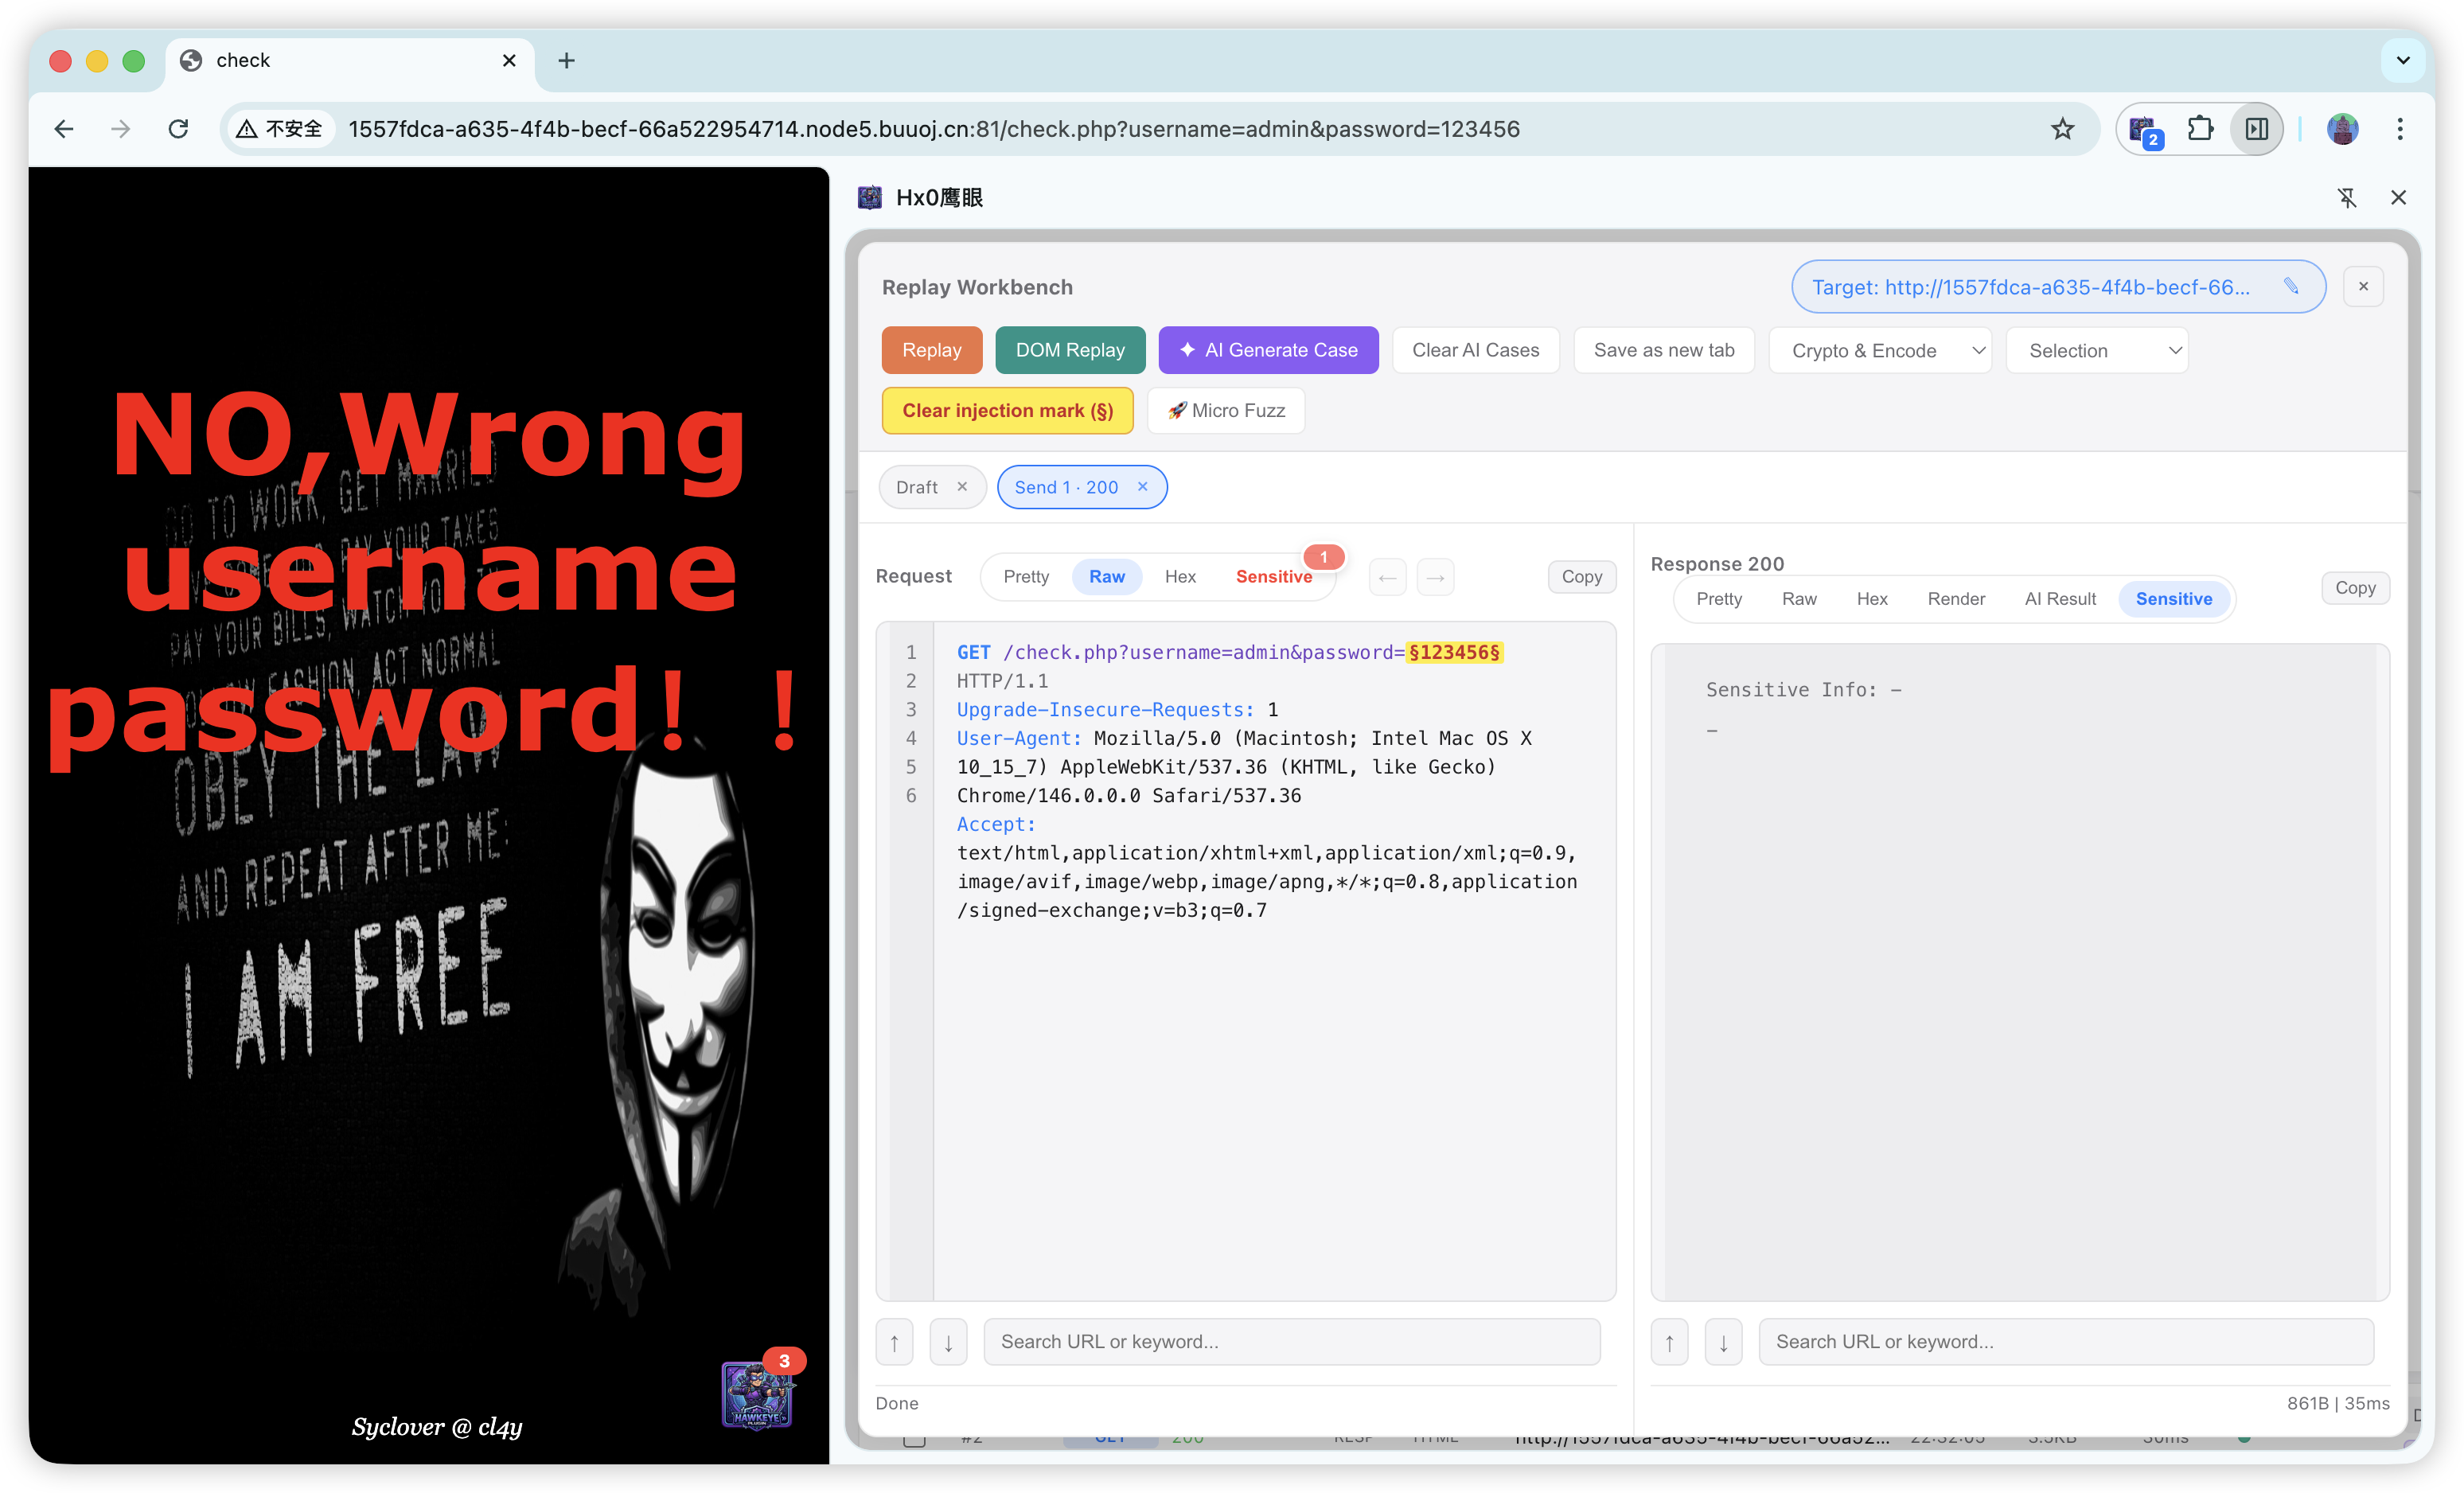
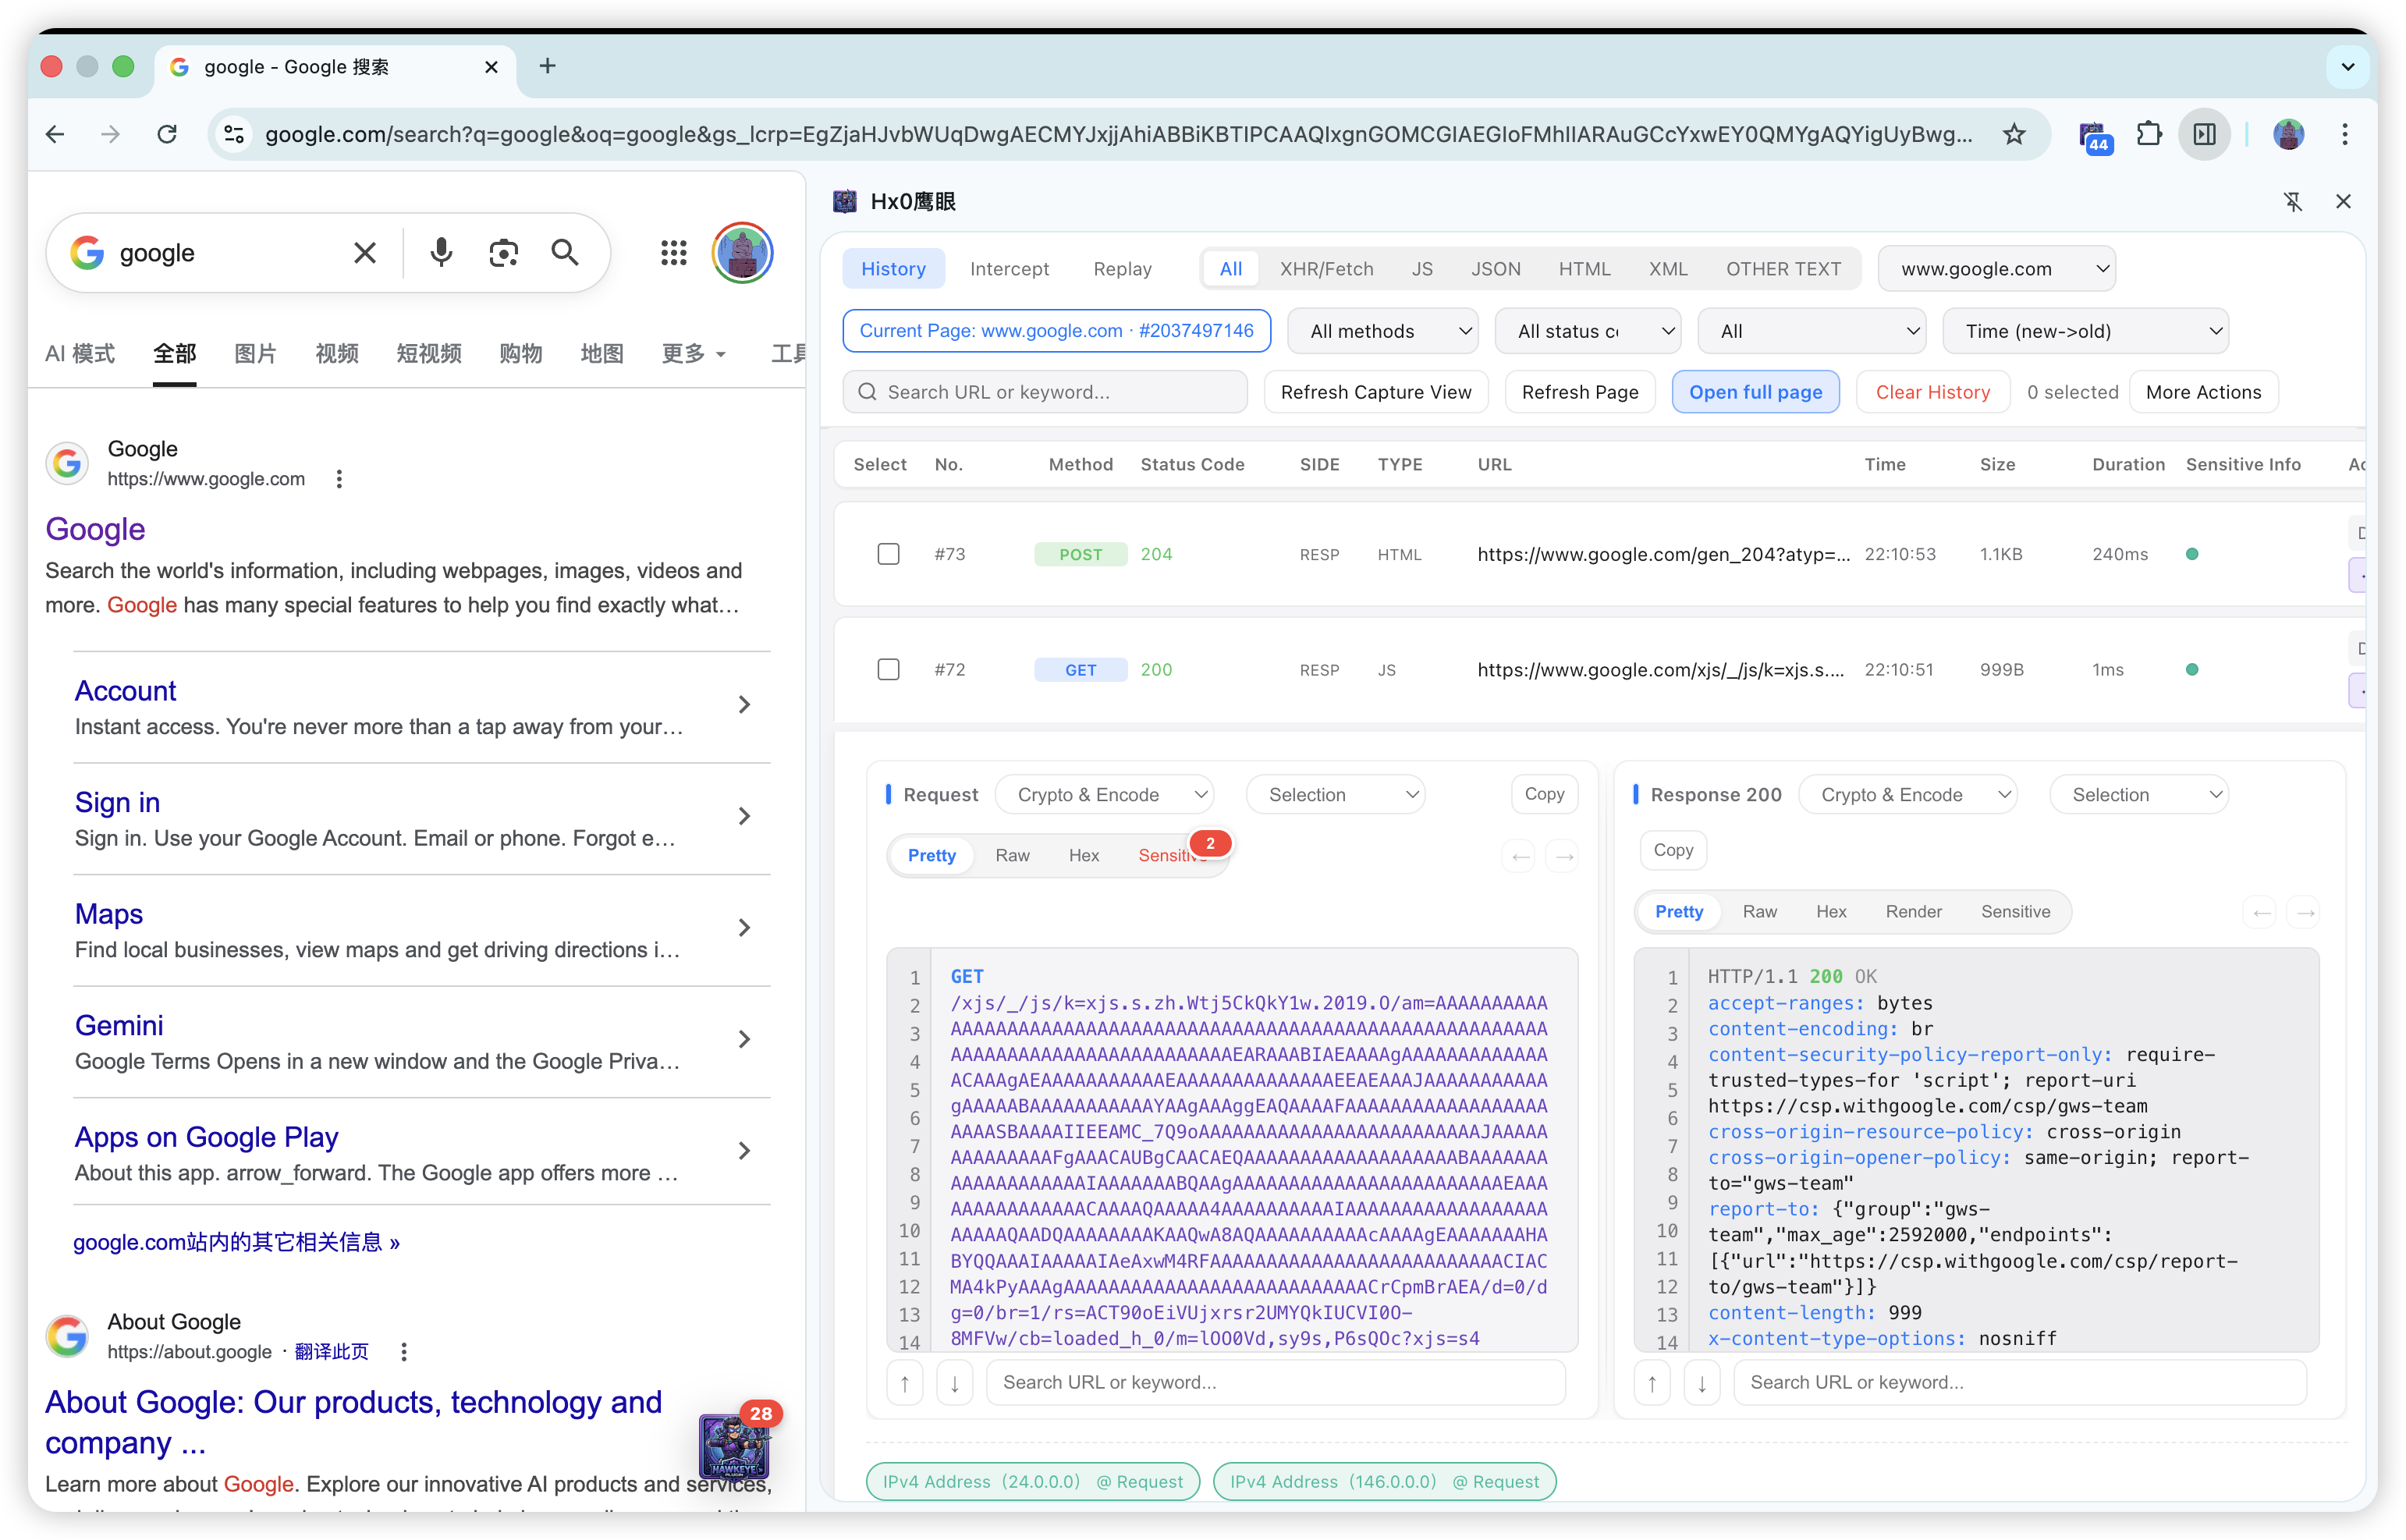
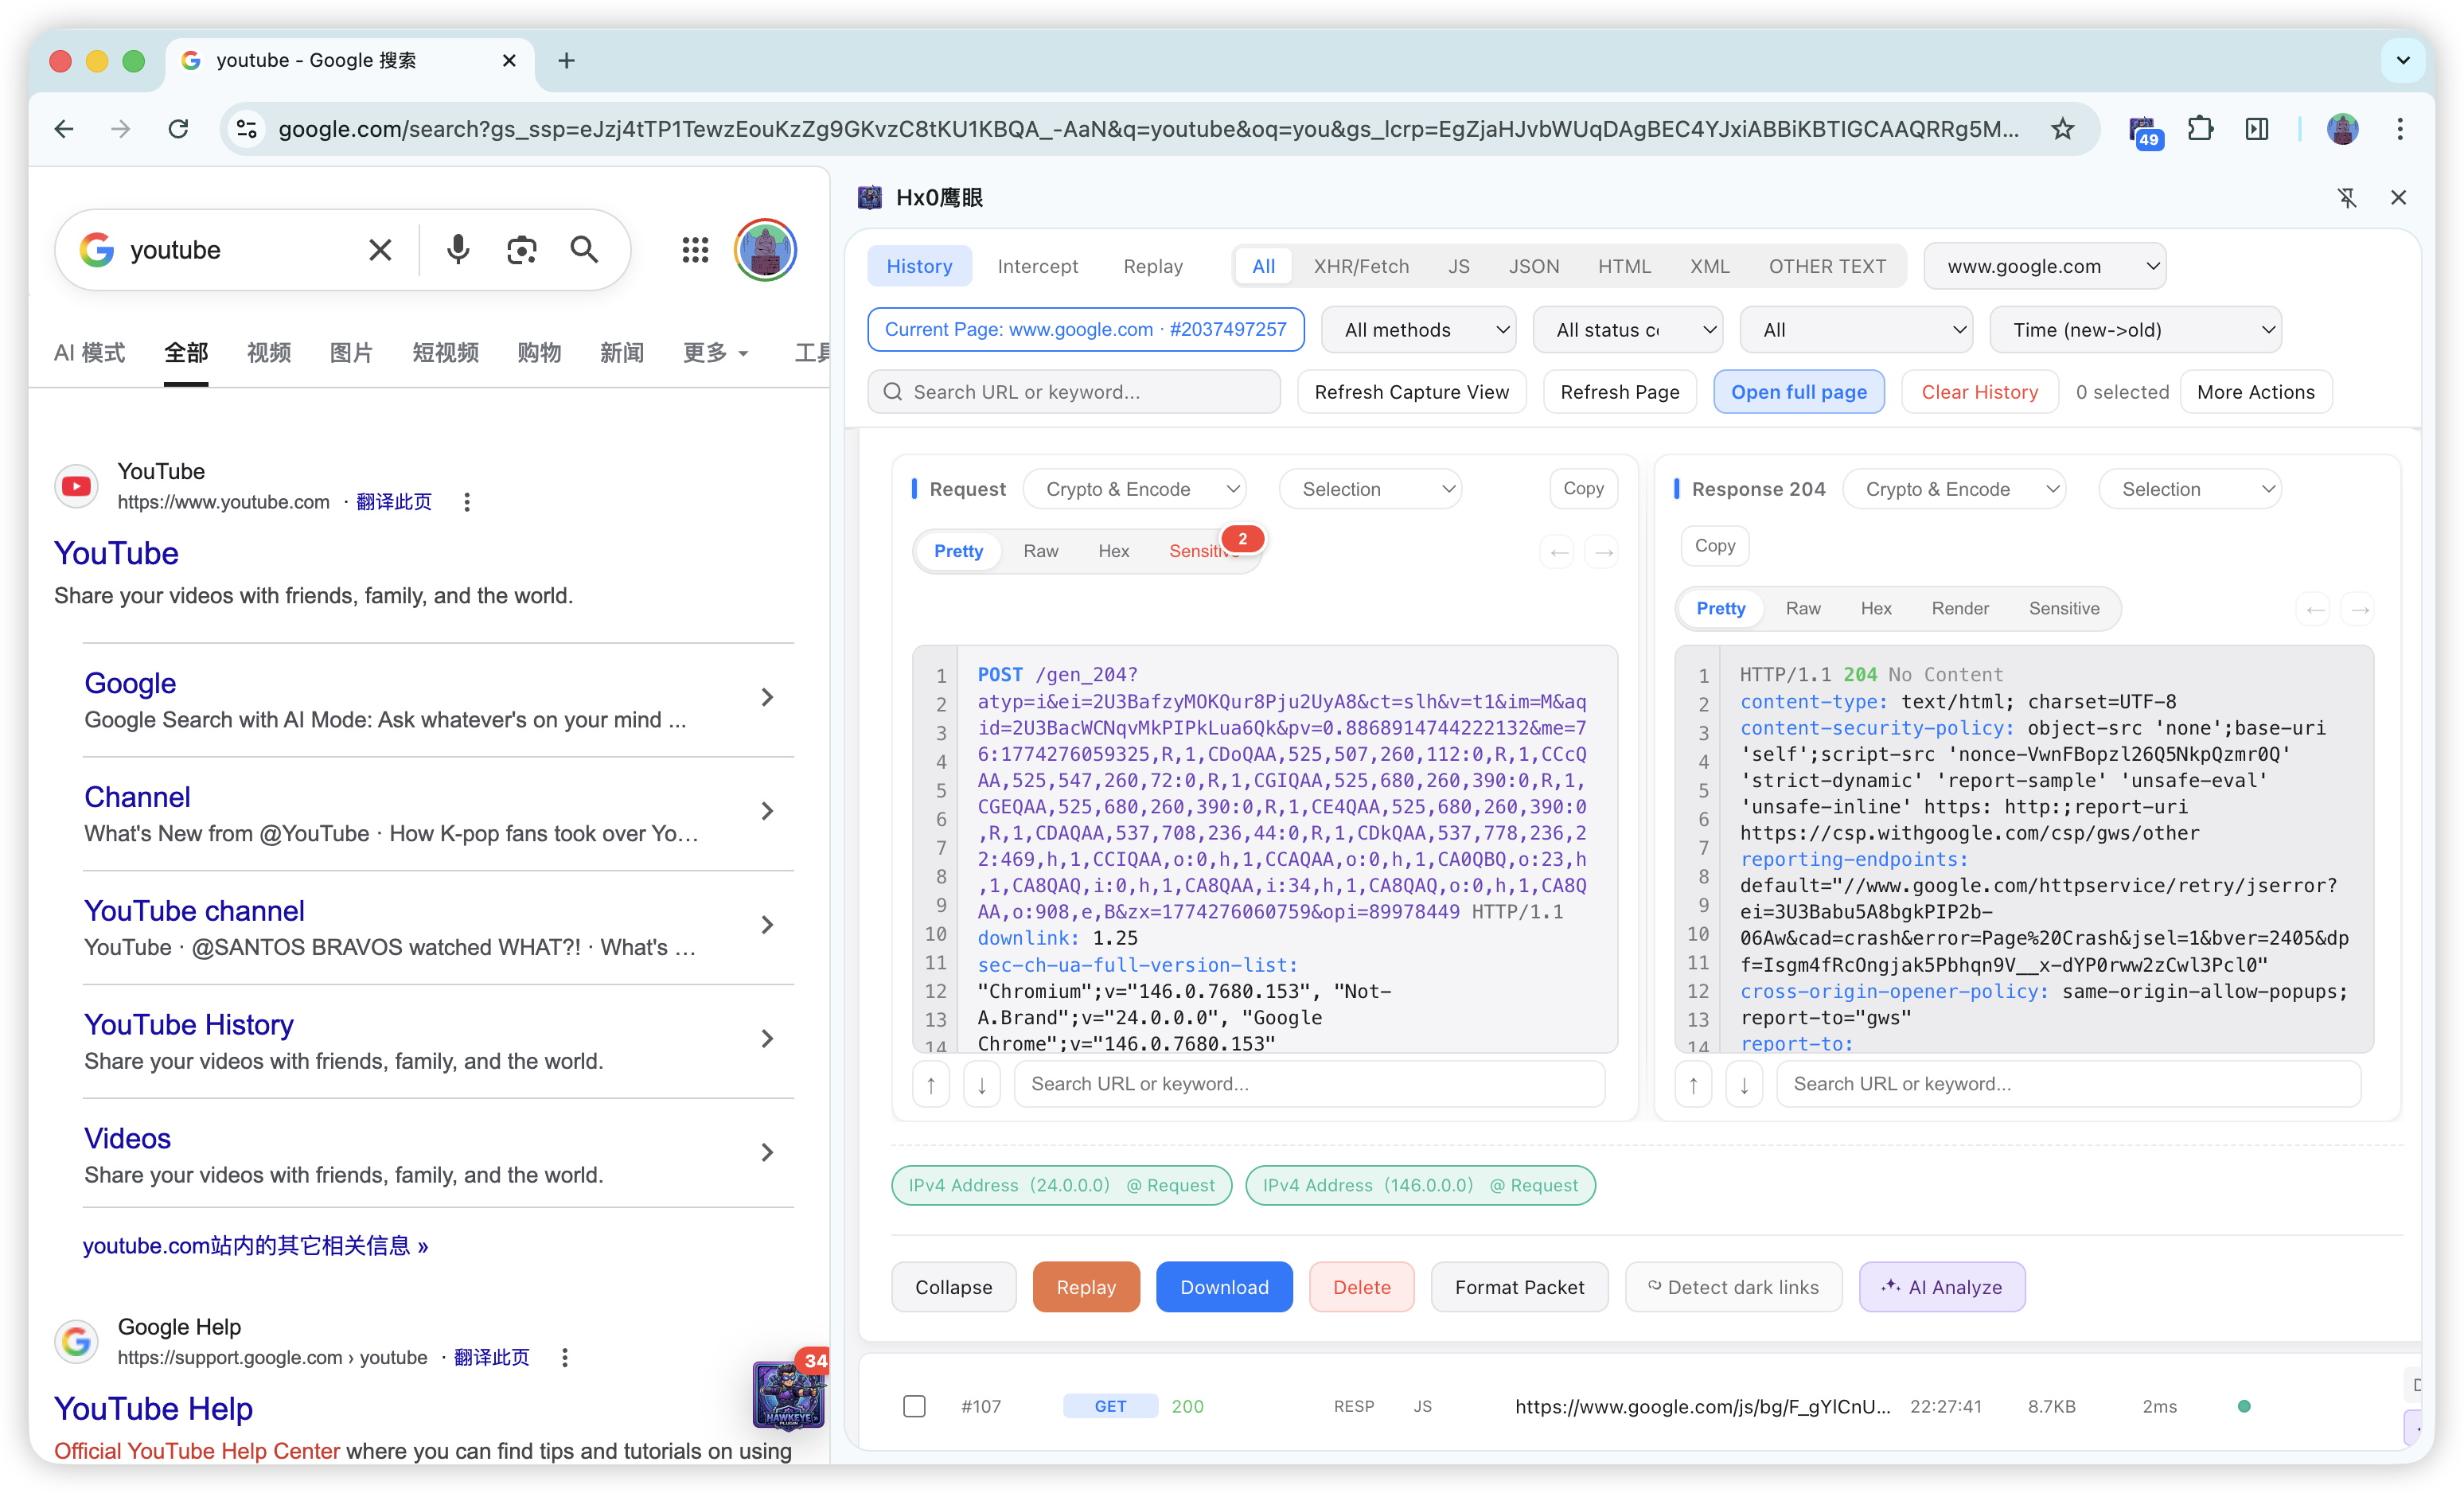
Skip the proxy hassle—truly ready out of the box. Hx0 HawkEye is a native browser extension (Chrome / Firefox and mainstream Chromium) that gives you a full capture, intercept (HTTP + WebSocket frames), replay, micro-Fuzz, and AI-assisted auditing loop directly in the sidebar.
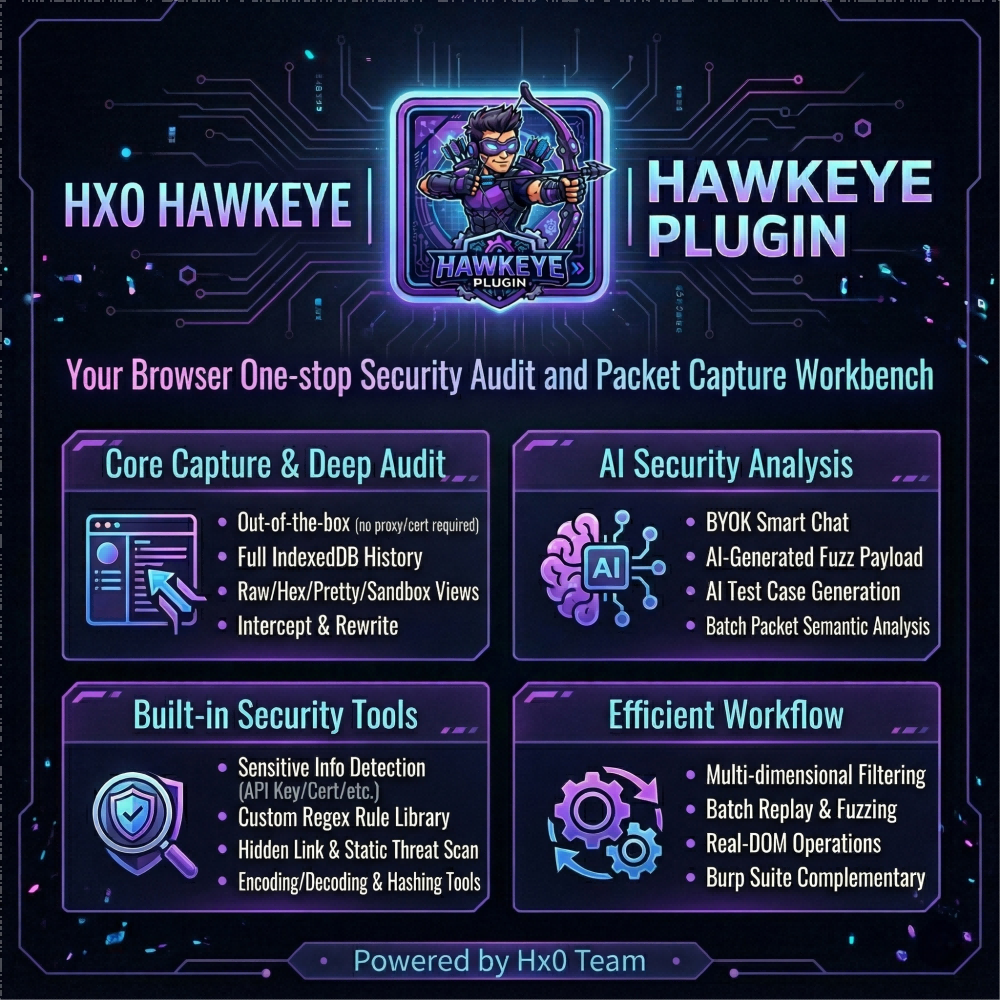
⚡ Core advantage: why not a classic proxy?

  • Zero environment overhead: no Burp Suite required, no system proxy, no root trust or Java setup.
  • Session fidelity: sees real page XHR / Fetch / WebSocket traffic with the same origin login state as the active tab—no more “proxy ate my cookies” or constant re-auth pain.
  • Works immediately after install: ideal for day-to-day dev/debug, API triage, and authorized first-pass security review.

🤖 Differentiator: end-to-end AI (BYOK)

Bring your own model API (BYOK) and embed AI into the sidebar workflow:
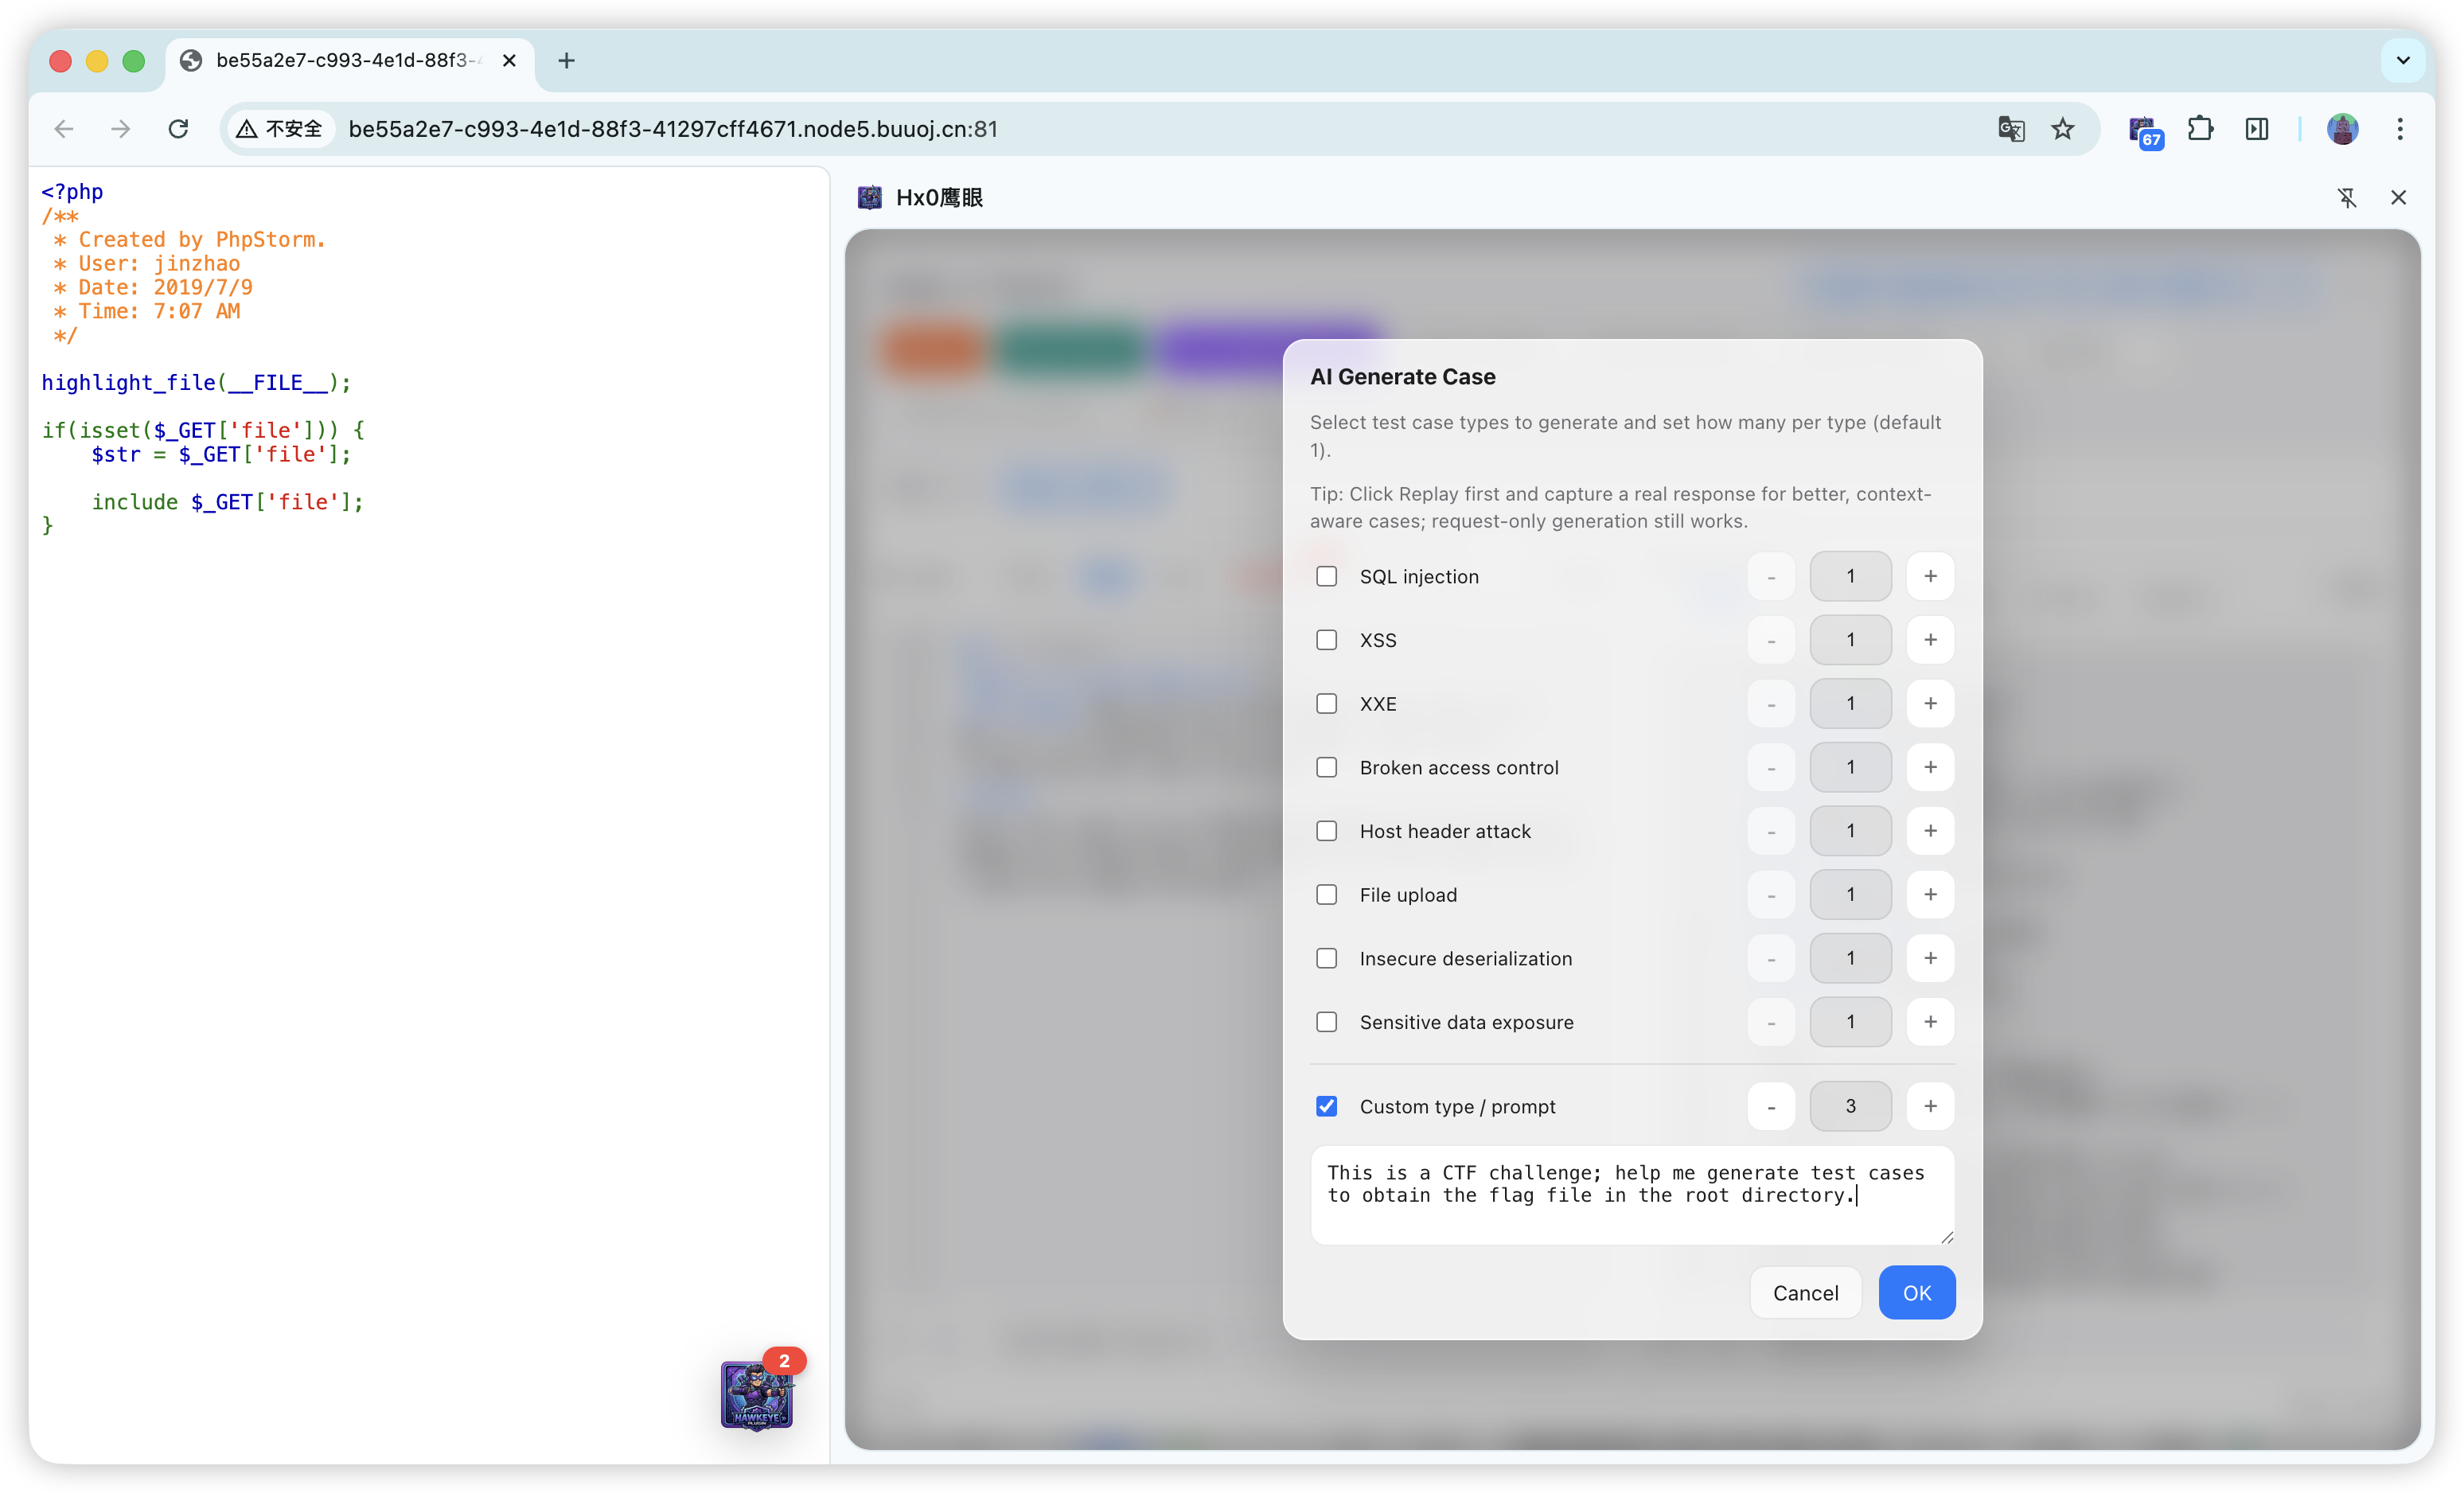
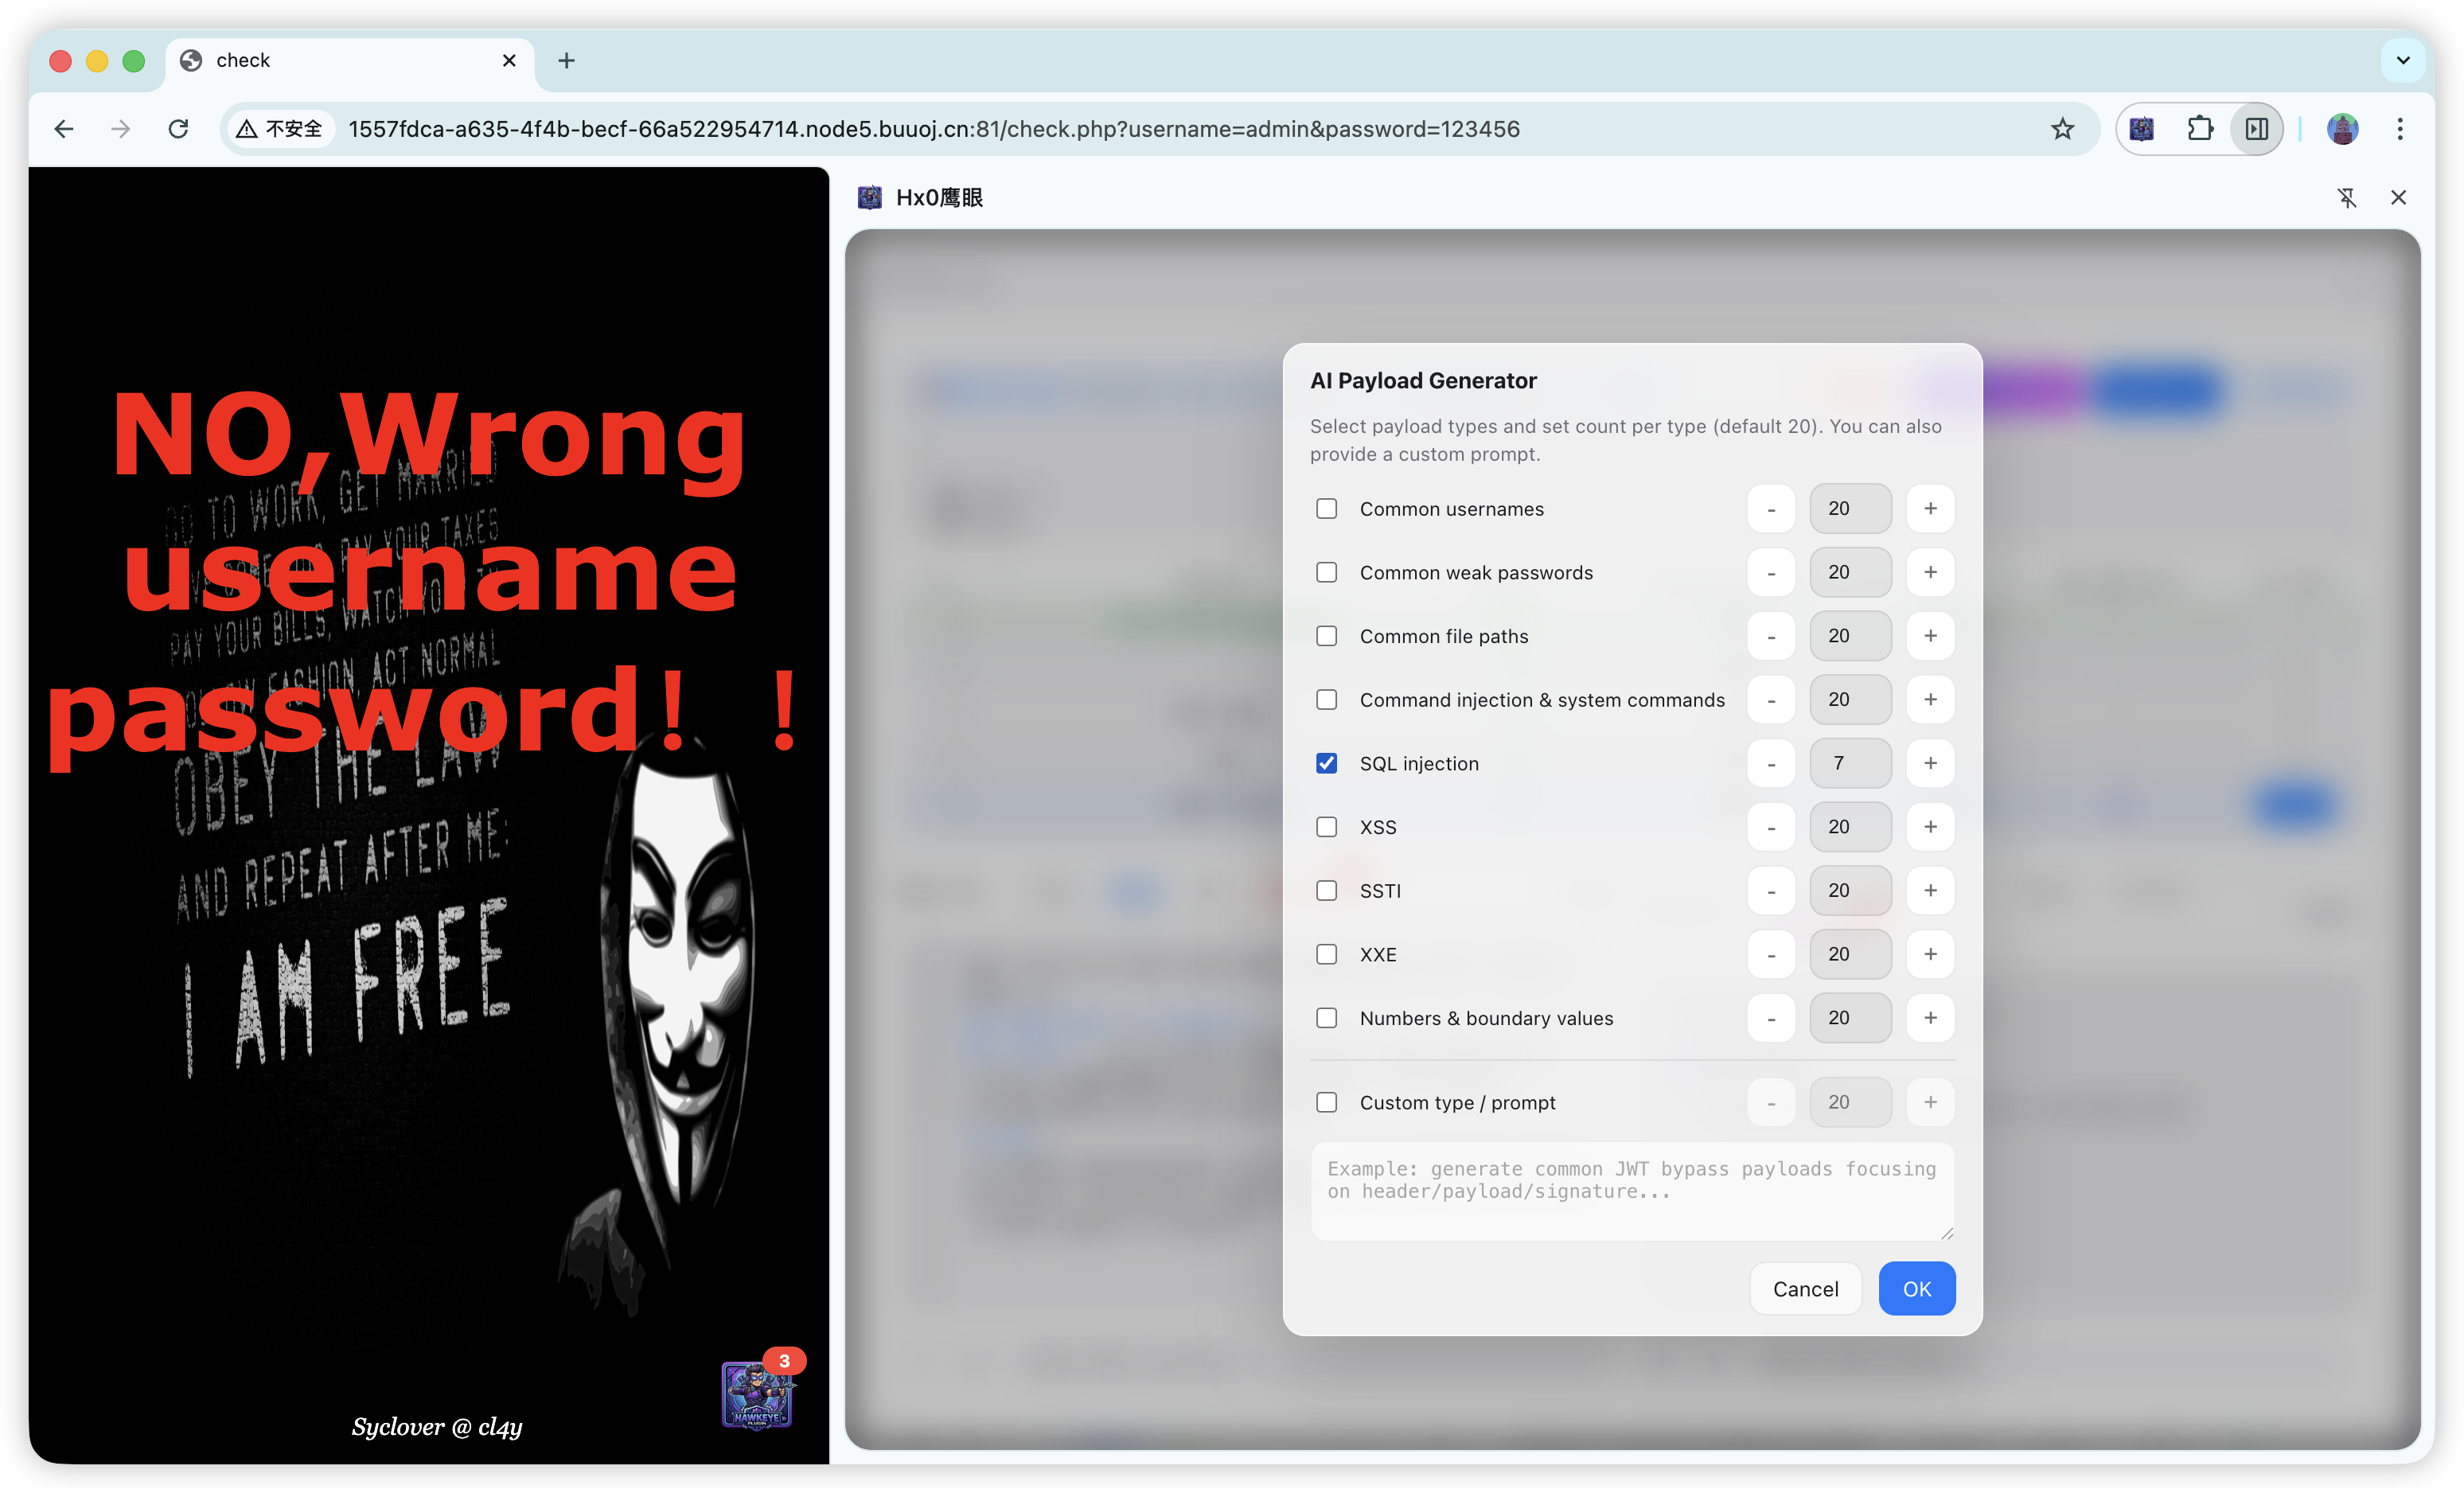
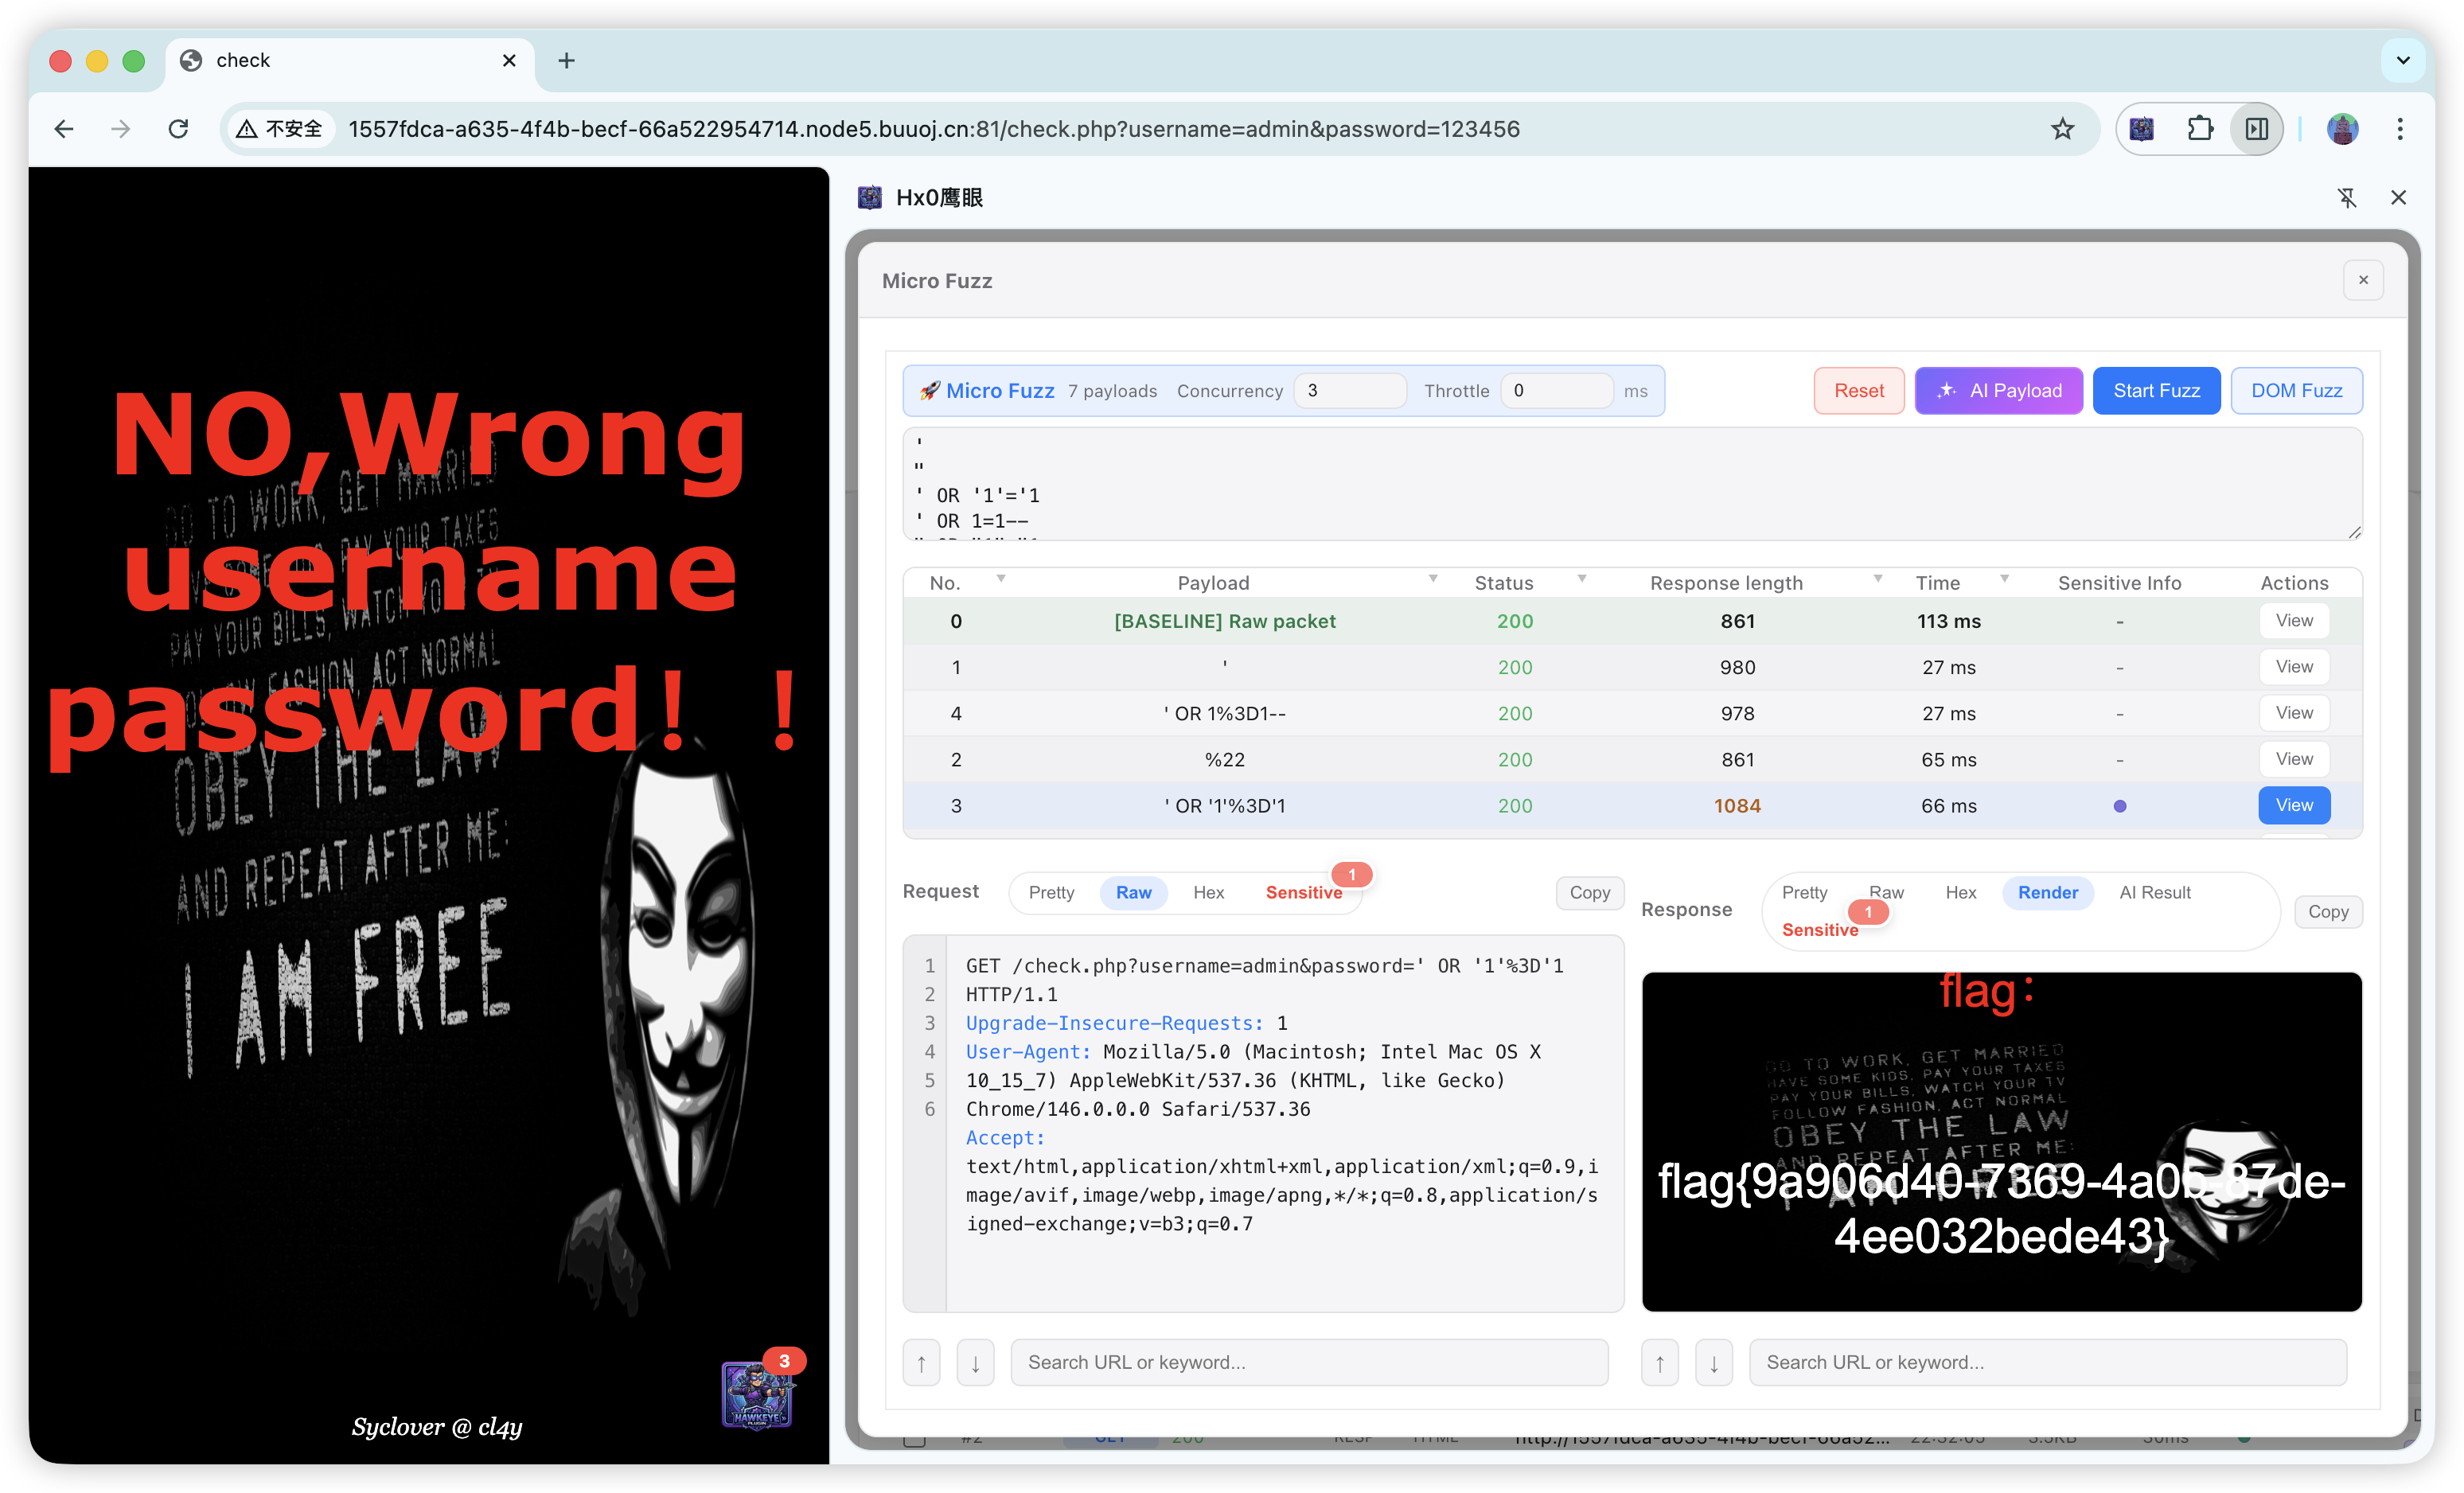
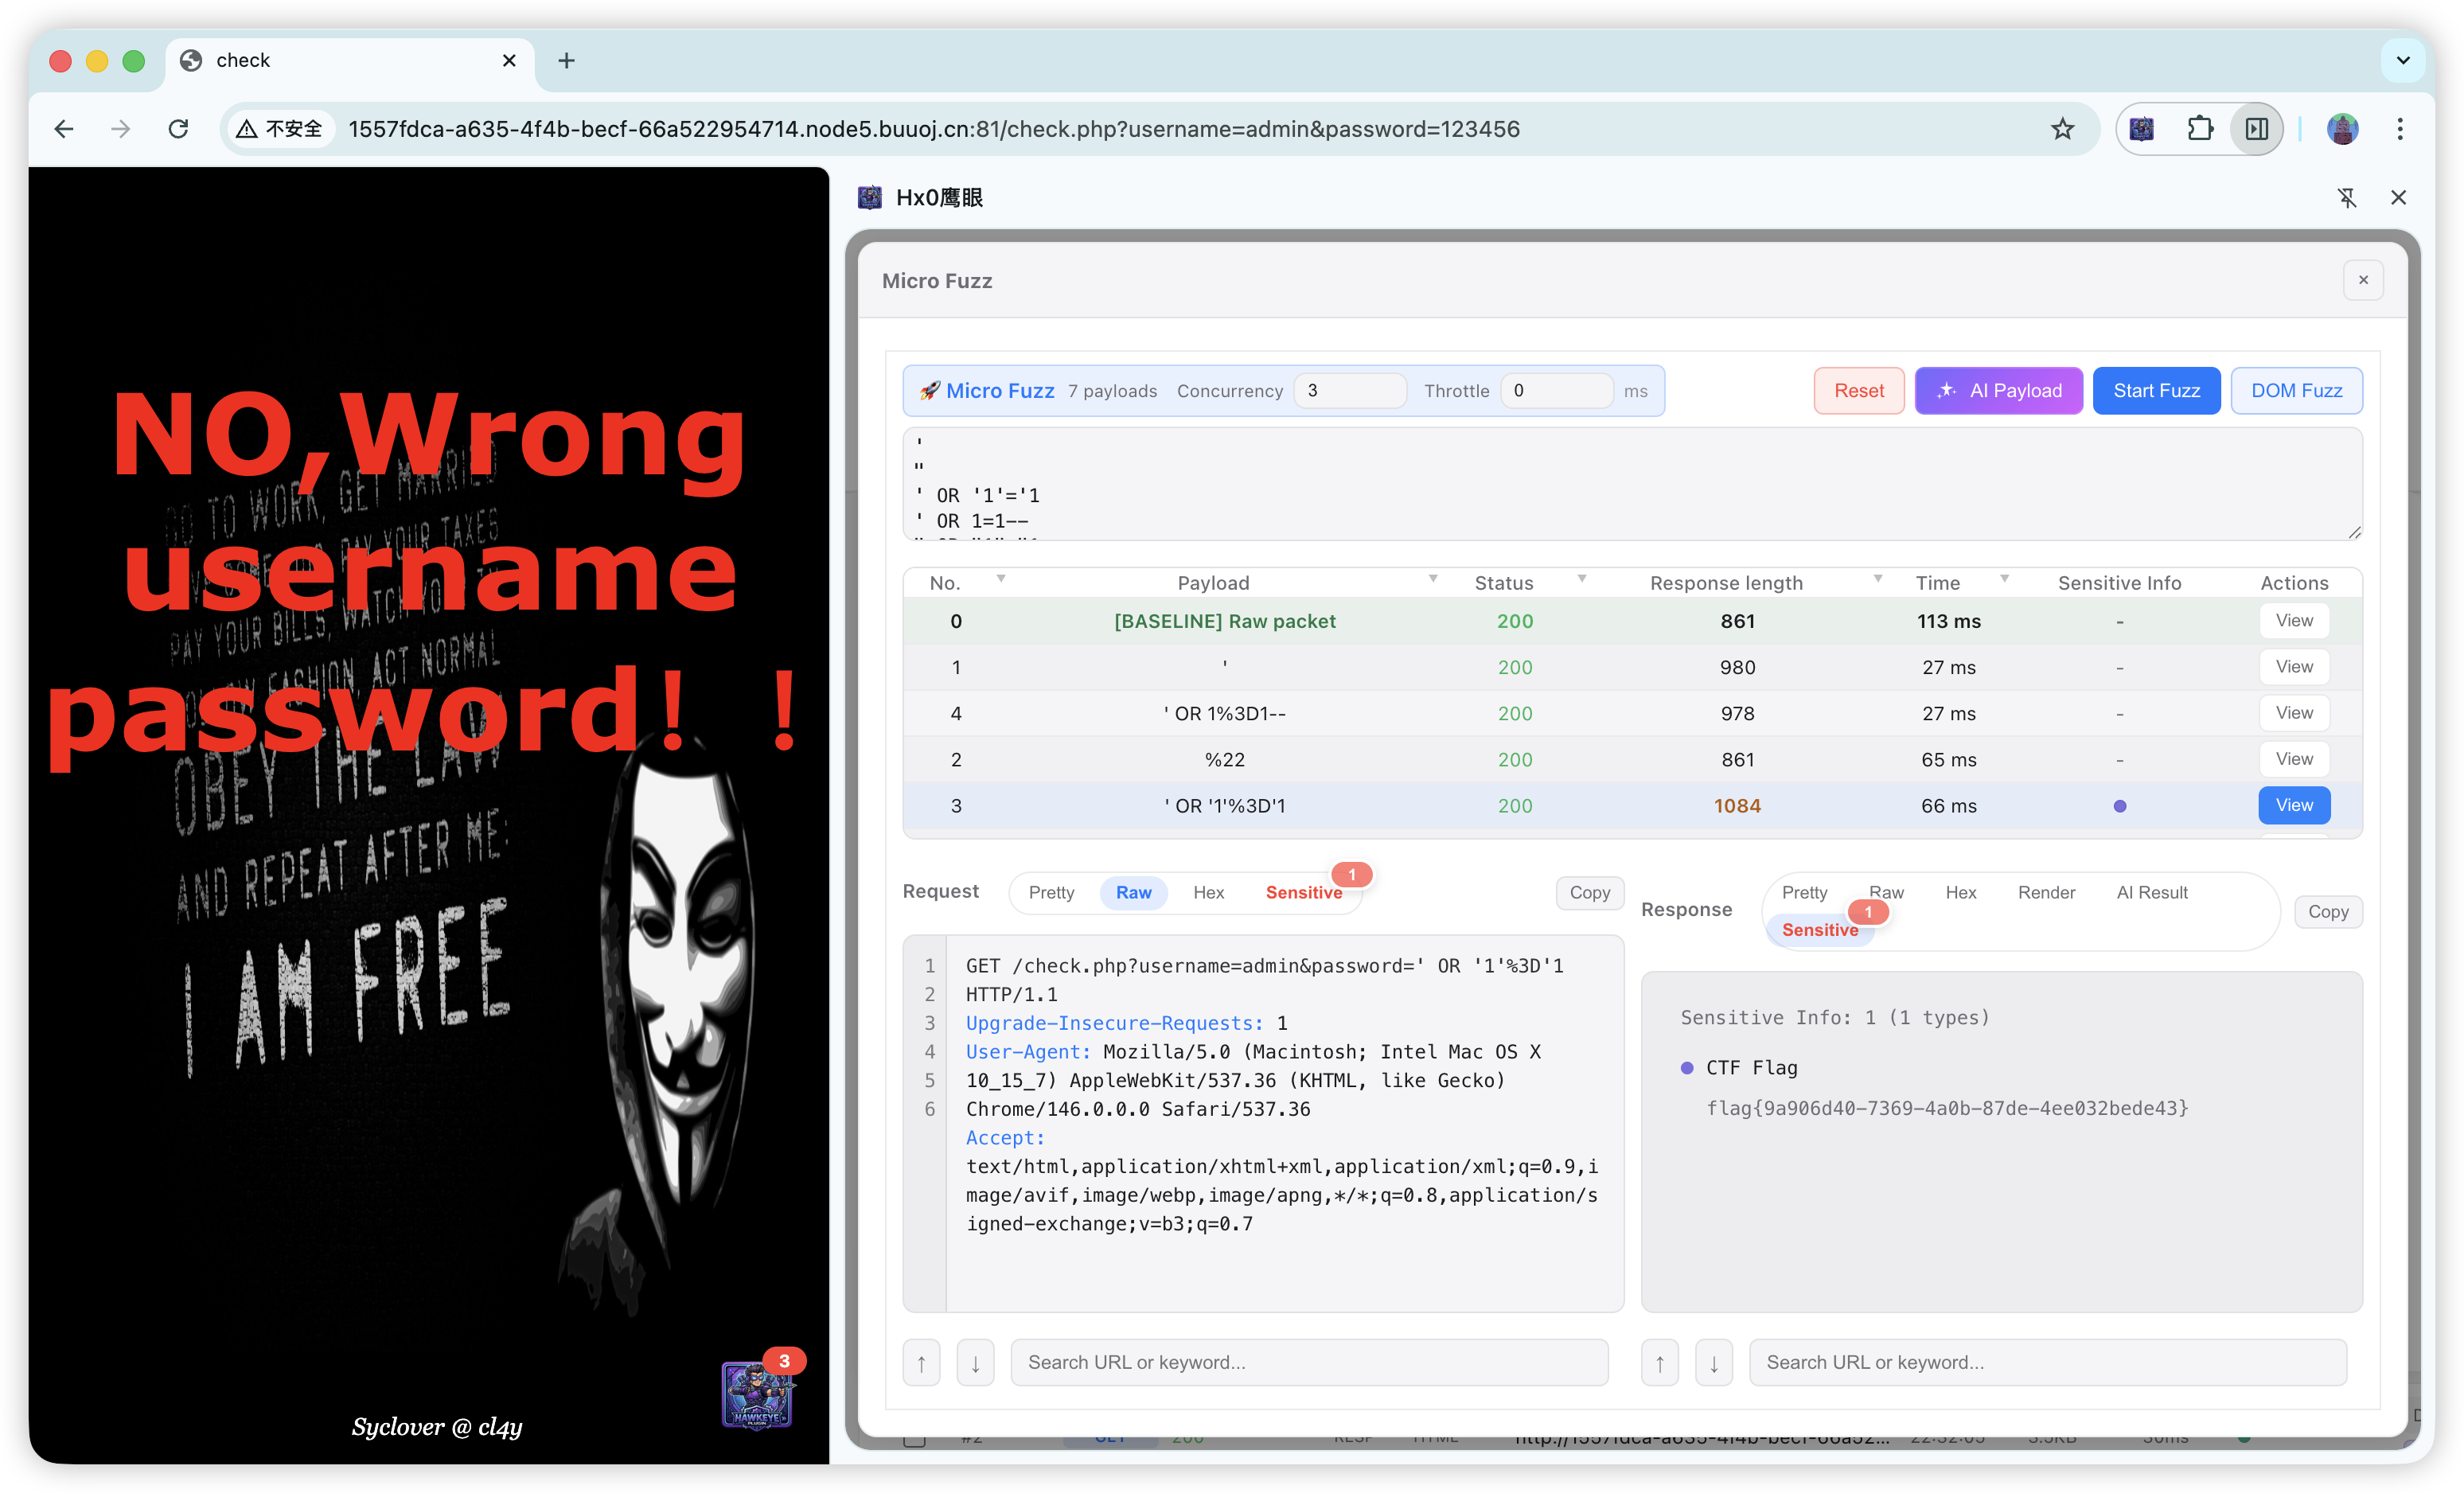
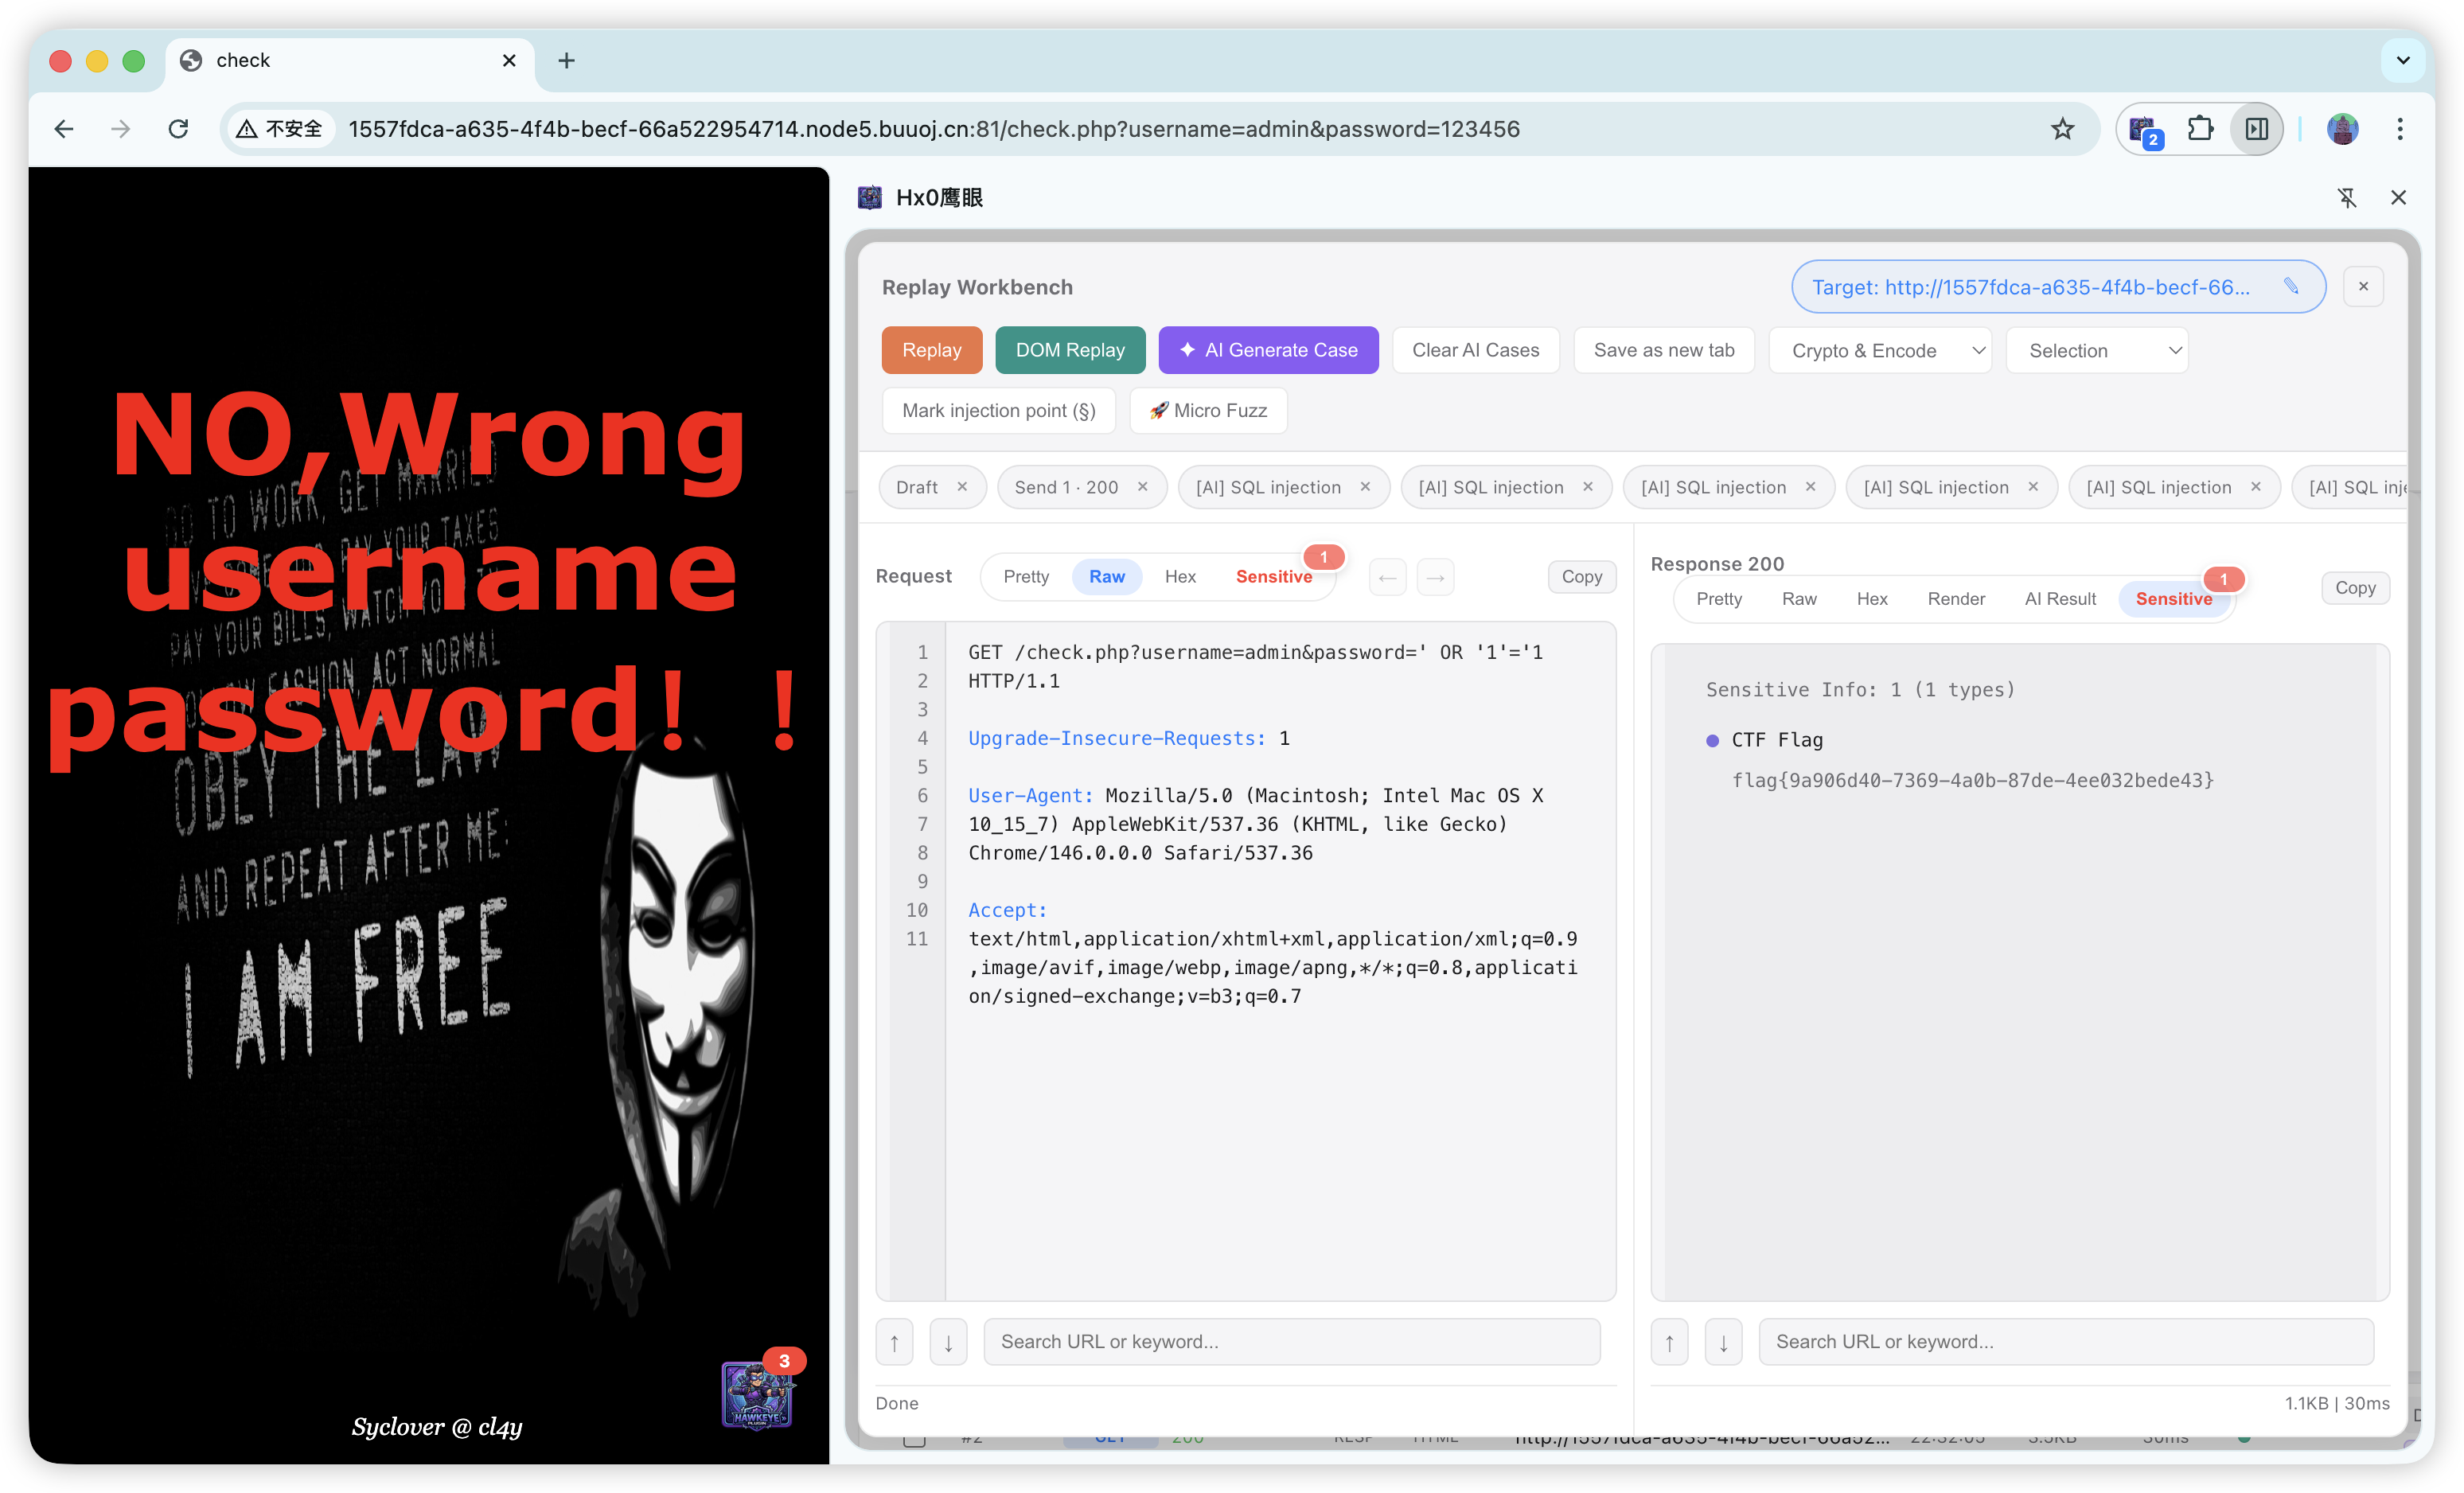
  • Smart cases & payload generation: structured test ideas in the replay workbench; context-aware mutated payloads in micro Fuzz—without bloated static wordlists.

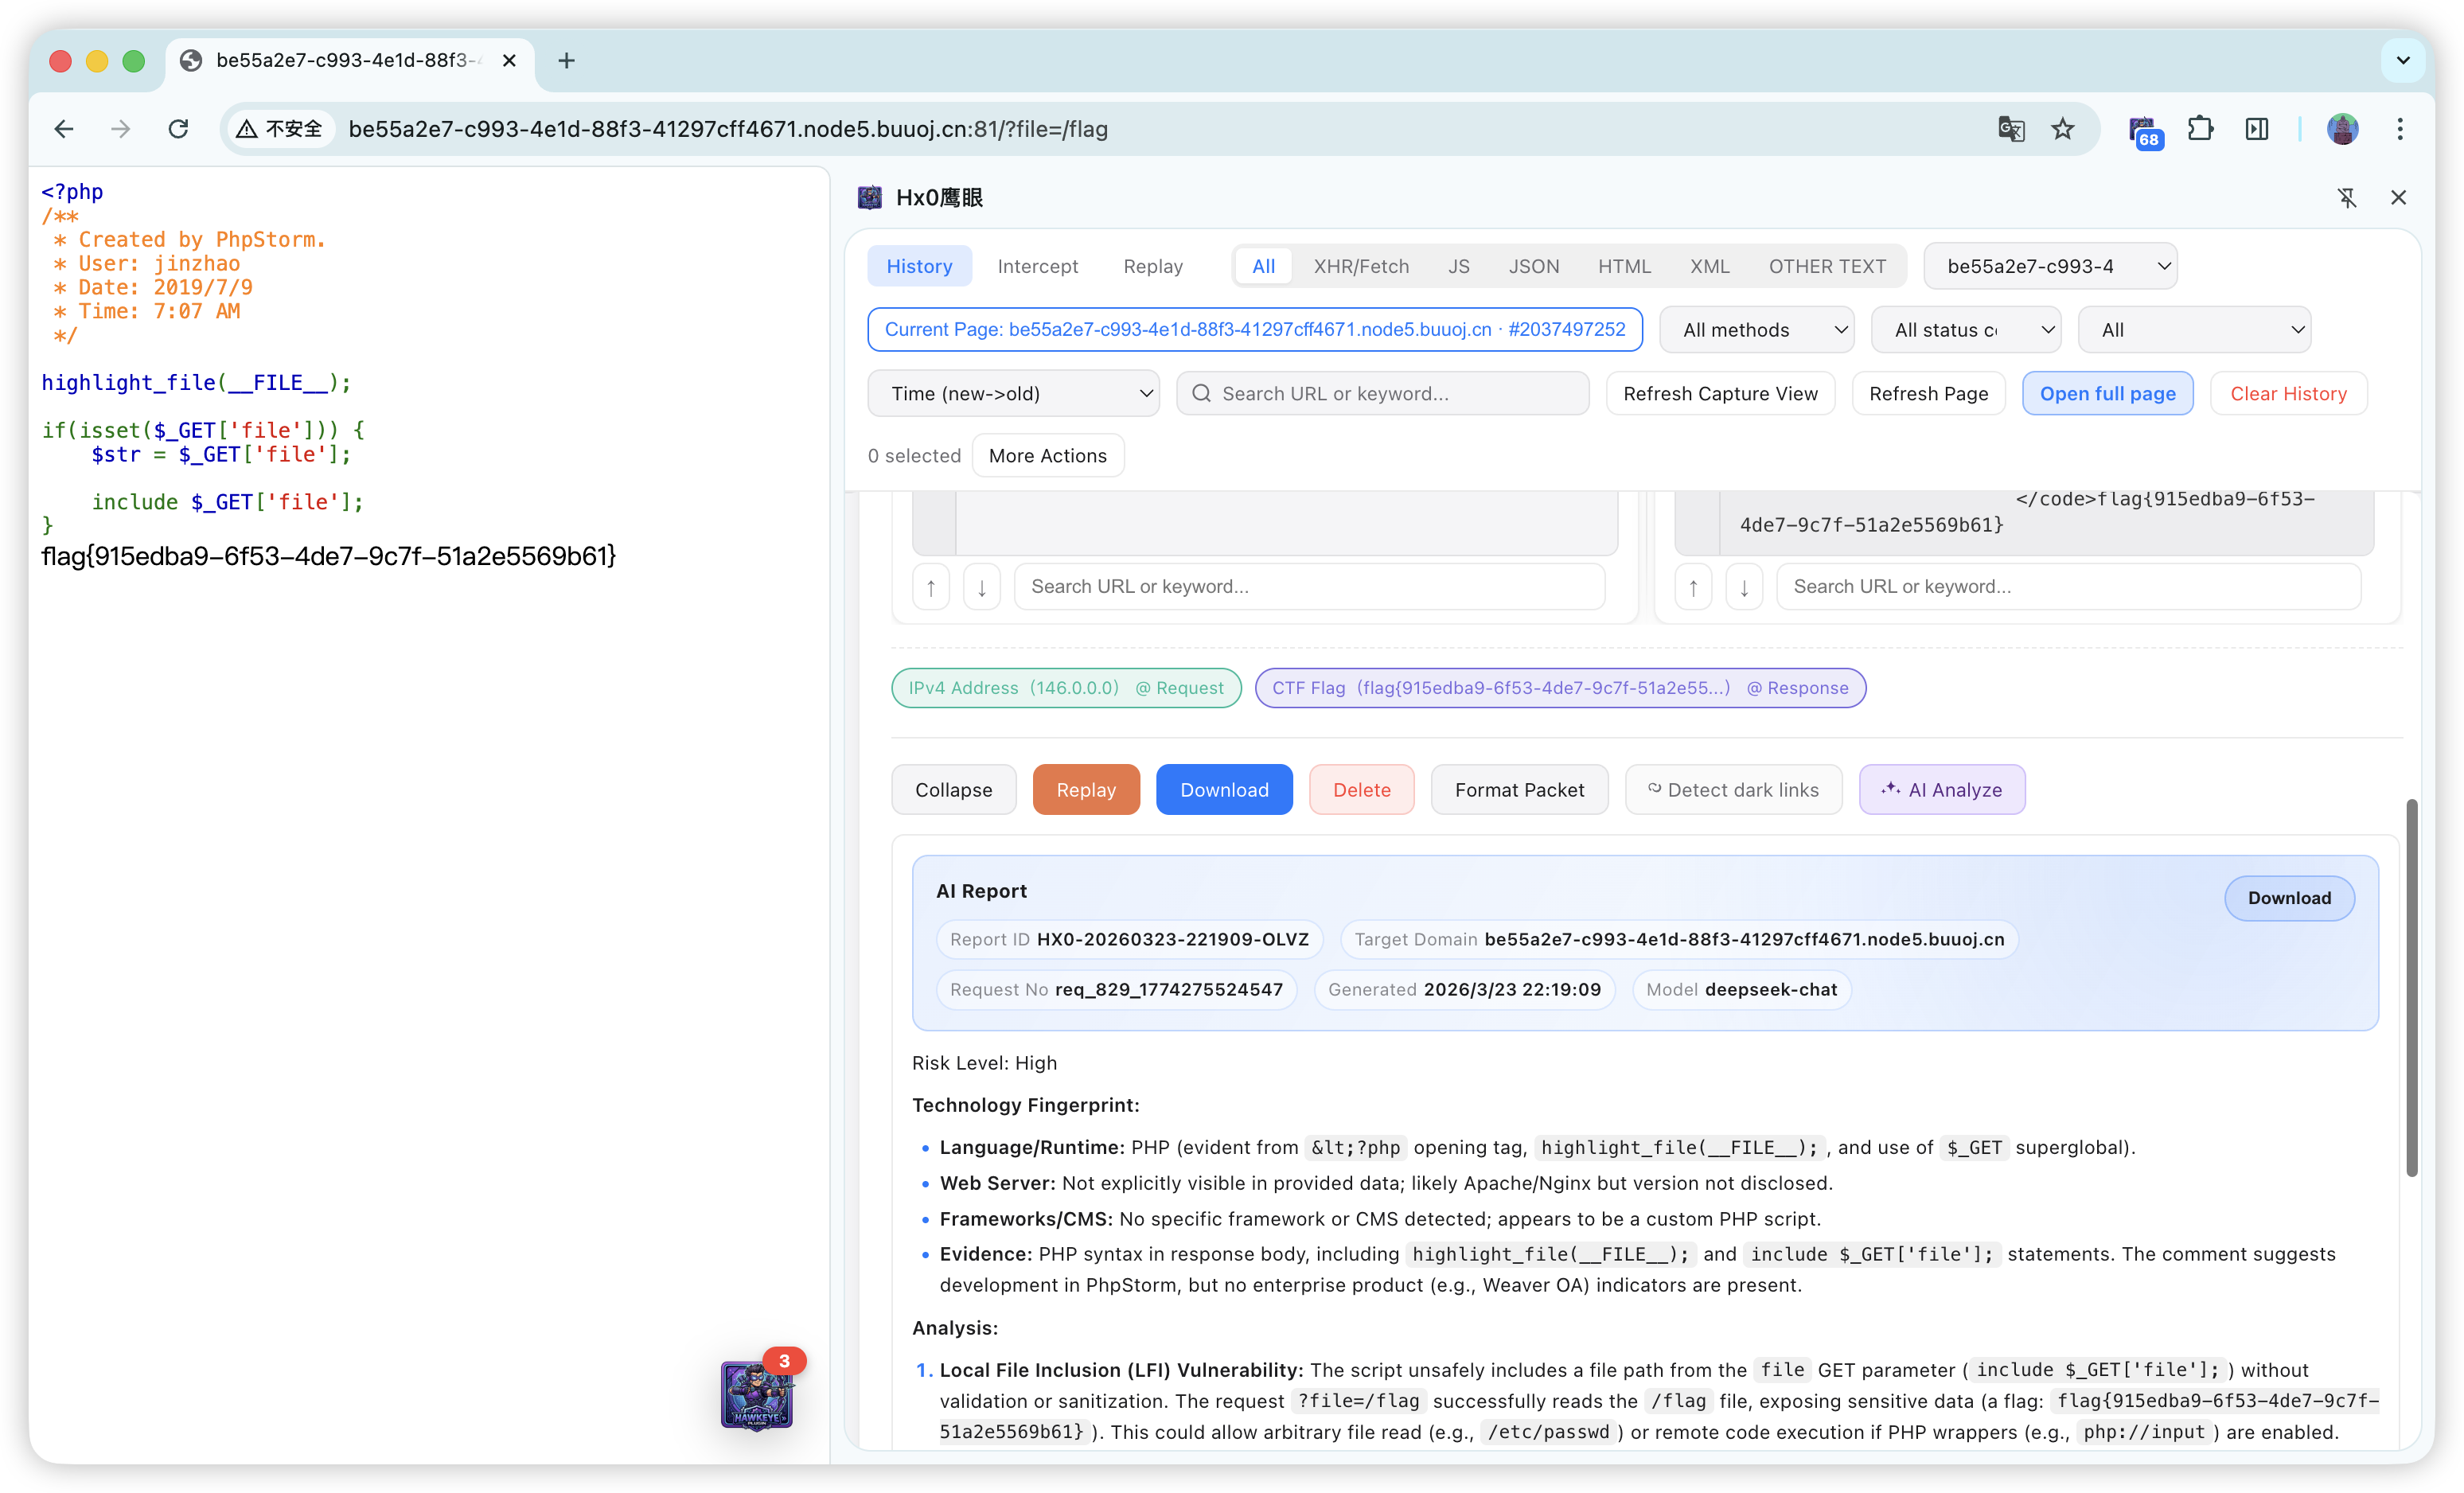
  • Deep single-request analysis: semantic AI read-through of full Request / Response for risk triage.

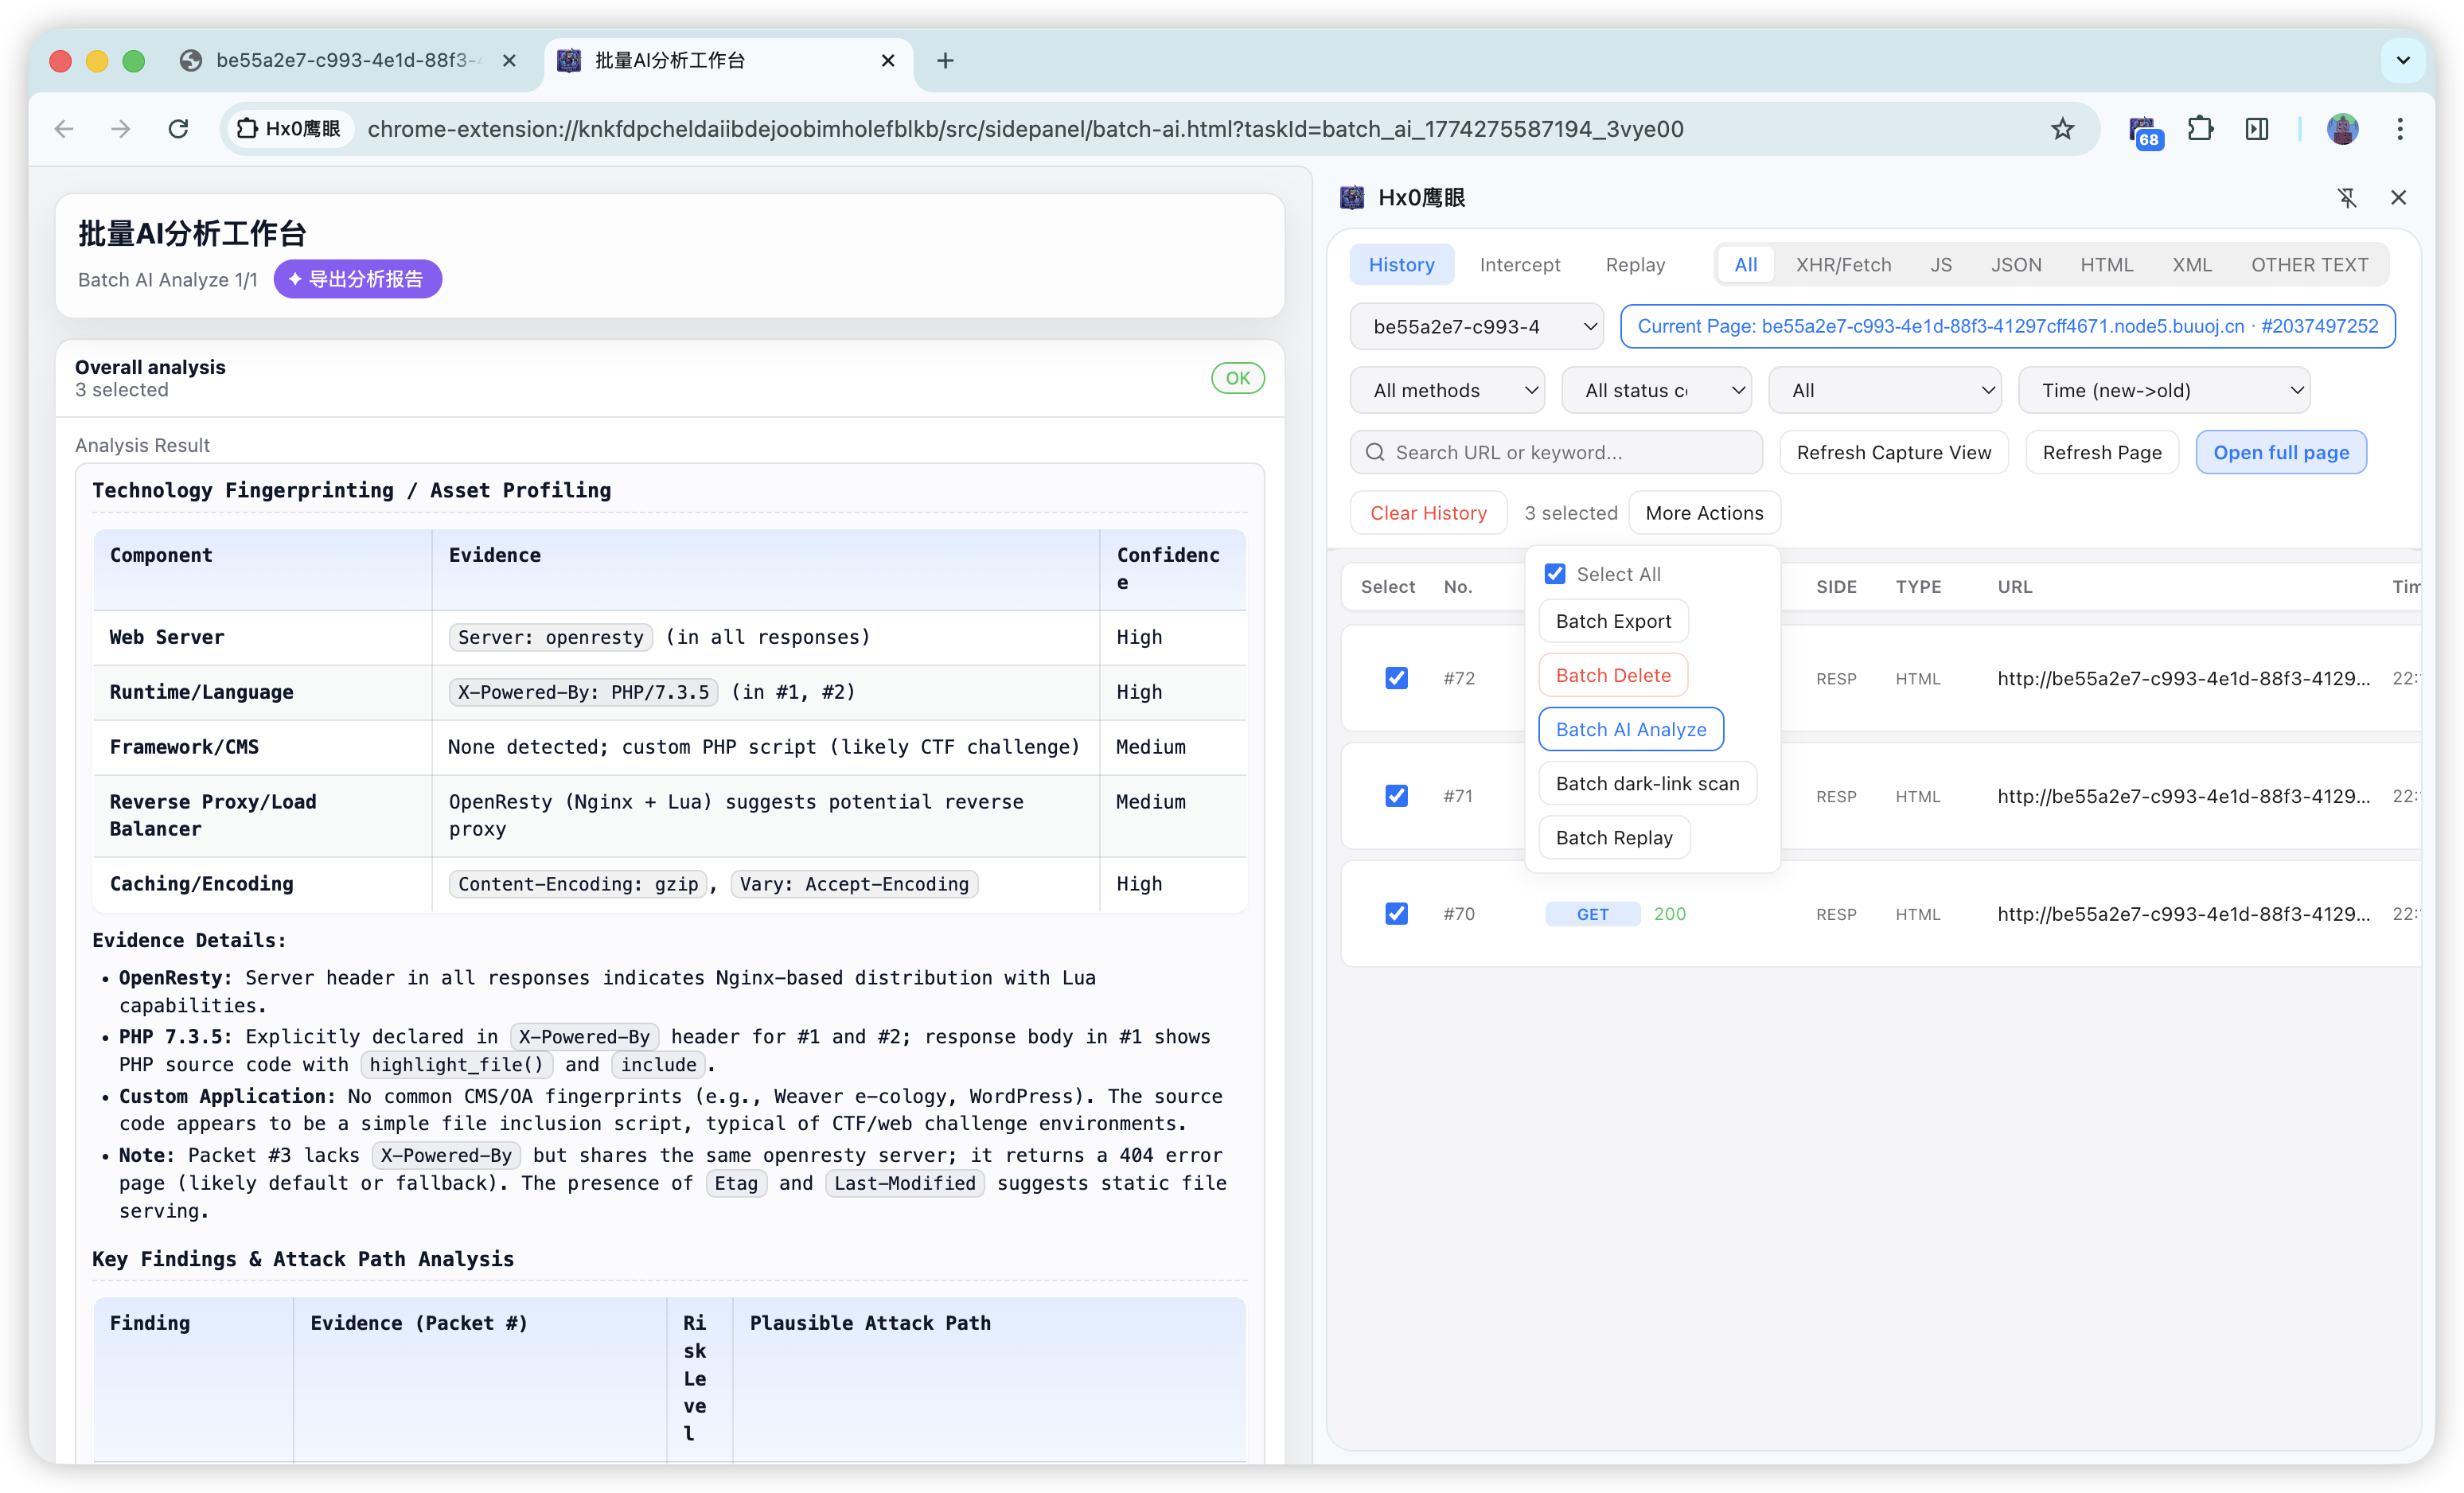
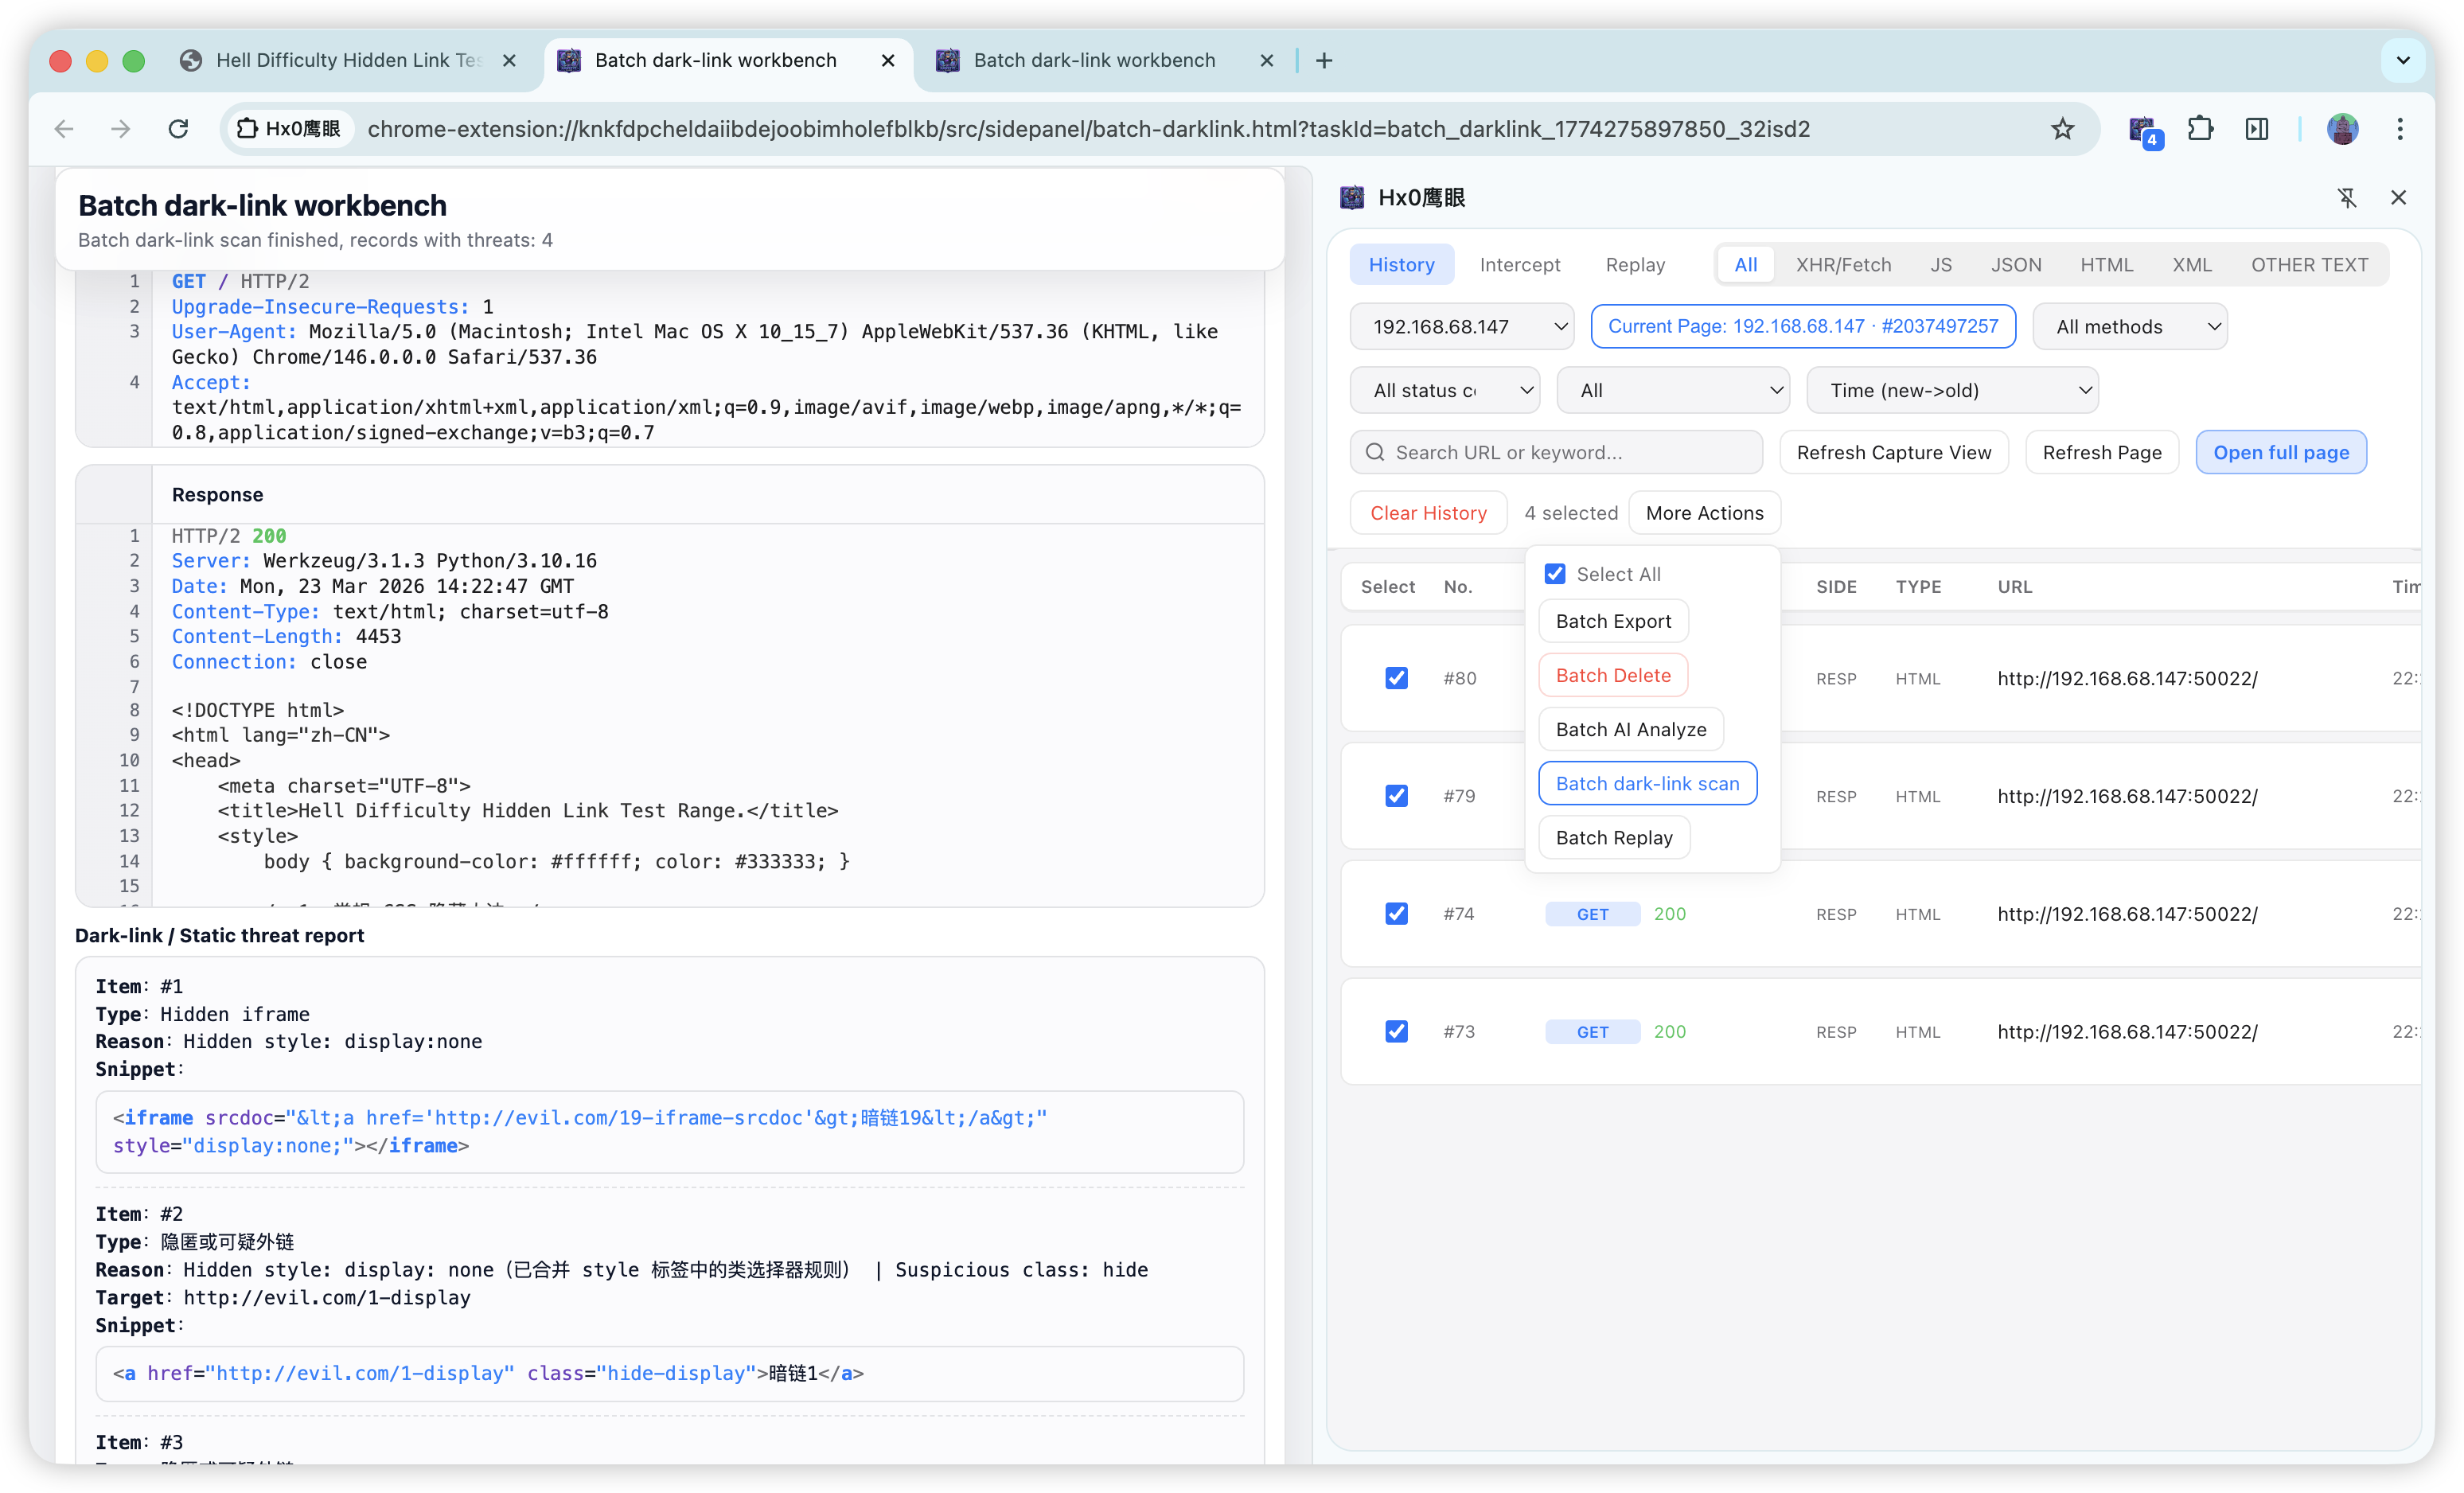
  • Batch synthesis: select multiple packets in a dedicated workbench; AI extracts patterns across APIs and third-party calls to support supply-chain / dependency-surface first-pass review.

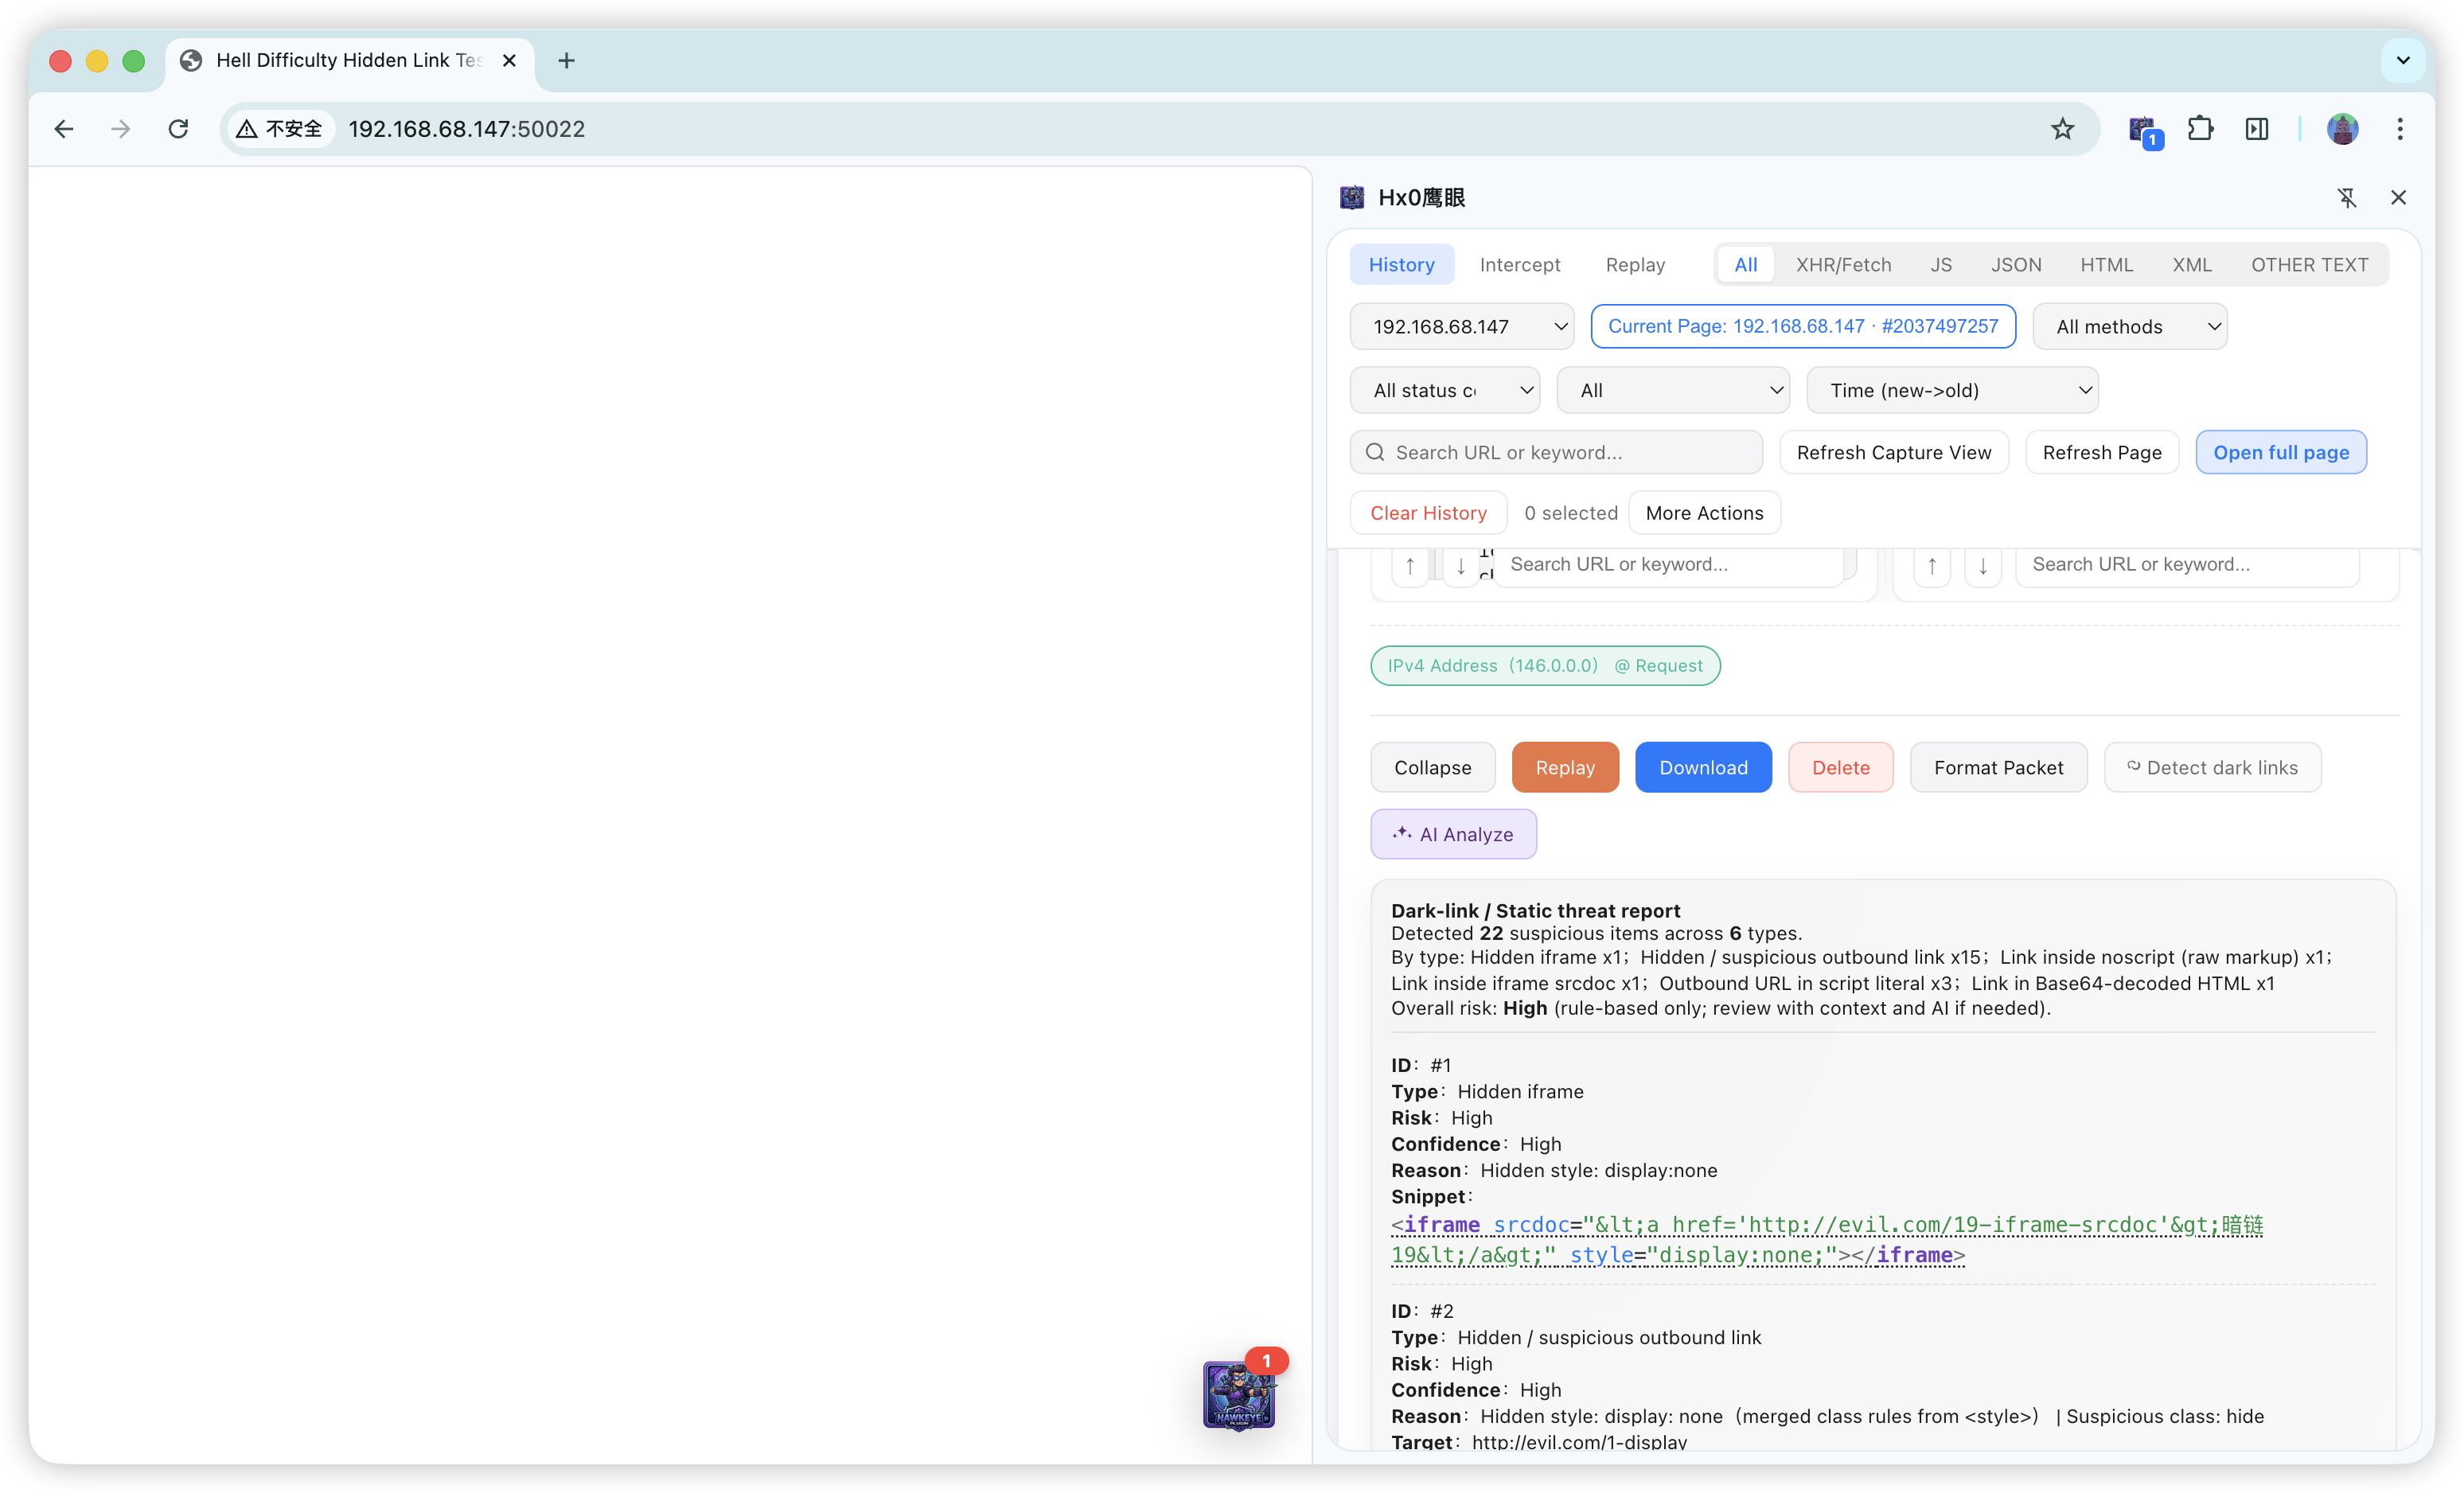
  • Dual-engine static hunting: built-in dark-link rules + AI contextual interpretation for batch replay across pages and broad static coverage.


2. Why we built it

With SPAs, heavy XHR/Fetch, and WebSocket, engineers constantly switch between “real browser session” and “capture / tamper / replay.” Classic proxies (e.g. Burp) are powerful but need system proxy and trust, and cookies / login state can diverge from the tab; lightweight toolbar extensions often lack durable history, structured detail, and a closed-loop workbench.

Hx0 HawkEye aims to keep no mandatory system proxy while folding capture (HTTP / WebSocket) → filter → detail audit → intercept → replay → micro Fuzz → sensitive & dark-link checks → optional AI into one sidebar hub, cutting context-switch cost for dev triage and authorized API review.


3. Features

Core flow: Capture (optional WebSocket) → Filter → Detail → Replay (HTTP / WebSocket frames; optional AI test cases) → Micro Fuzz (HTTP / WS; optional AI payloads) → Dark-link / AI packet analysis (including batch AI / dark-link workbenches after multi-select) → AI Task Console (Pro, multi-stage automation).
تنزيل الأداة