

njsscan v1.0.1
ماسح SAST واعي دلالياً لتطبيقات Node.js يكتشف أنماط الشيفرة غير الآمنة باستخدام مطابقة أنماط libsast وتحليل semgrep الواعي بالصياغة.
njsscan
njsscan هي أداة اختبار تطبيقات ثابتة (SAST) يمكنها اكتشاف أنماط التعليمات البرمجية غير الآمنة في تطبيقات node.js الخاصة بك باستخدام مطابق الأنماط البسيط من libsast وأداة البحث الدلالي الواعي بالصياغة لأنماط التعليمات البرمجية semgrep.
صُنعت بـ  في الهند


دعم njsscan
- التبرع عبر Paypal:

- رعاية المشروع:

دورات التعلم الإلكتروني والشهادات
 OpSecX Node.js Security: Pentesting and Exploitation - NJS
التثبيت
pip install njsscan
يتطلب Python 3.10+ ويدعم Mac و Linux فقط
خيارات سطر الأوامر
$ njsscan
usage: njsscan [-h] [--json] [--sarif] [--sonarqube] [--defectdojo] [--gitlab-sast] [--html] [-o OUTPUT] [-c CONFIG] [--missing-controls] [-w] [-v] [path ...]

positional arguments:
  path                  Path can be file(s) or directories with source code

optional arguments:
  -h, --help            show this help message and exit
  --json                set output format as JSON
  --sarif               set output format as SARIF 2.1.0
  --sonarqube           set output format compatible with SonarQube
  --defectdojo          set output format compatible with DefectDojo Generic Findings Import
  --gitlab-sast         set output format as GitLab SAST report
  --html                set output format as HTML
  -o OUTPUT, --output OUTPUT
                        output filename to save the result
  -c CONFIG, --config CONFIG
                        Location to .njsscan config file
  --missing-controls    enable missing security controls check
  -w, --exit-warning    non zero exit code on warning
  -v, --version         show njsscan version
مثال على الاستخدام
$ njsscan test.js
- Pattern Match ████████████████████████████████████████████████████████████ 1
- Semantic Grep ███████████████████████████ 160

njsscan: v0.1.9 | Ajin Abraham | opensecurity.in
╒═════════════╤═══════════════════════════════════════════════════════════════════════════════════════════════╕
│ RULE ID     │ express_xss                                                                                   │
├─────────────┼───────────────────────────────────────────────────────────────────────────────────────────────┤
│ OWASP       │ A1: Injection                                                                                 │
├─────────────┼───────────────────────────────────────────────────────────────────────────────────────────────┤
│ CWE         │ CWE-79: Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting')  │
├─────────────┼───────────────────────────────────────────────────────────────────────────────────────────────┤
│ DESCRIPTION │ Untrusted User Input in Response will result in Reflected Cross Site Scripting Vulnerability. │
├─────────────┼───────────────────────────────────────────────────────────────────────────────────────────────┤
│ SEVERITY    │ ERROR                                                                                         │
├─────────────┼───────────────────────────────────────────────────────────────────────────────────────────────┤
│ FILES       │ ╒════════════════╤═══════════════════════════════════════════════╕                            │
│             │ │ File           │ test.js                                       │                            │
│             │ ├────────────────┼───────────────────────────────────────────────┤                            │
│             │ │ Match Position │ 5 - 46                                        │                            │
│             │ ├────────────────┼───────────────────────────────────────────────┤                            │
│             │ │ Line Number(s) │ 7: 8                                          │                            │
│             │ ├────────────────┼───────────────────────────────────────────────┤                            │
│             │ │ Match String   │ const { name } = req.query;                   │                            │
│             │ │                │     res.send('<h1> Hello :' + name + "</h1>") │                            │
│             │ ╘════════════════╧═══════════════════════════════════════════════╛                            │
╘═════════════╧═══════════════════════════════════════════════════════════════════════════════════════════════╛
nodejsscan SAST
nodejsscan، المبنية على njsscan، توفر واجهة مستخدم كاملة لإدارة الثغرات الأمنية إلى جانب تكاملات أخرى أنيقة.
انظر nodejsscan
Python API
>>> from njsscan.njsscan import NJSScan
>>> node_source = '/node_source/true_positives/sqli_node.js'
>>> scanner = NJSScan([node_source], json=True, check_controls=False)
>>> scanner.scan()
{
    'templates': {},
    'nodejs': {
        'node_sqli_injection': {
            'files': [{
                'file_path': '/node_source/true_positives/sqli_node.js',
                'match_position': (1, 24),
                'match_lines': (4, 11),
                'match_string': 'var employeeId = req.foo;\n\nvar sql = "SELECT * FROM trn_employee WHERE employee_id = " + employeeId;\n\n\n\nconnection.query(sql, function (error, results, fields) {\n\n    if (error) {\n\n        throw error;\n\n    }\n\n    console.log(results);'
            }],
            'metadata': {
                'owasp': 'A1: Injection',
                'cwe': "CWE-89: Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection')",
                'description': 'Untrusted input concatinated with raw SQL query can result in SQL Injection.',
                'severity': 'ERROR'
            }
        }
    },
    'errors': []
}
تكوين njsscan
ملف .njsscan في جذر دليل التعليمات البرمجية المصدرية يسمح لك بتكوين njsscan. يمكنك أيضًا استخدام ملف .njsscan مخصص باستخدام وسيطة --config.
---
- nodejs-extensions:
  - .js

  template-extensions:
  - .new
  - .hbs
  - ''

  ignore-filenames:
  - skip.js

  ignore-paths:
  - __MACOSX
  - skip_dir
  - node_modules

  ignore-extensions:
  - .jsx

  ignore-rules:
  - regex_injection_dos
  - pug_jade_template

  severity-filter:
  - WARNING
  - ERROR

  severity-overrides:
    express_xss: WARNING
    node_secret: ERROR
كتم النتائج
يمكنك كتم النتائج من ملفات مصدر javascript عن طريق إضافة التعليق // njsscan-ignore: rule_id1, rule_id2 إلى السطر الذي يُفعّل النتائج.
مثال:
app.get('/some/redirect', function (req, res) {
    var target = req.param("target");
    res.redirect(target); // njsscan-ignore: express_open_redirect
});
تكاملات CI/CD
يمكنك تمكين njsscan في خطوط أنابيب CI/CD أو DevSecOps الخاصة بك.
Github Action
أضف ما يلي إلى الملف .github/workflows/njsscan.yml.
name: njsscan
on:
  push:
    branches: [ master, main ]
  pull_request:
    branches: [ master, main ]
jobs:
  njsscan:
    runs-on: ubuntu-latest
    name: njsscan check
    steps:
    - name: Checkout the code
      uses: actions/checkout@3d3c42e5aac5ba805825da76410c181273ba90b1 # v7.0.1
    - uses: actions/setup-python@5fda3b95a4ea91299a34e894583c3862153e4b97 # v7.0.0
      with:
        python-version: '3.12'
    - name: nodejsscan scan
      id: njsscan
      uses: ajinabraham/njsscan-action@231750a435d85095d33be7d192d52ec650625146 # v9
      with:
        args: '.'
مثال: dvna with njsscan github action
تكامل Github Code Scanning
أضف ما يلي إلى الملف .github/workflows/njsscan_sarif.yml.
name: njsscan sarif
on:
  push:
    branches: [ master, main ]
  pull_request:
    branches: [ master, main ]
jobs:
  njsscan:
    runs-on: ubuntu-latest
    name: njsscan code scanning
    steps:
    - name: Checkout the code
      uses: actions/checkout@3d3c42e5aac5ba805825da76410c181273ba90b1 # v7.0.1
    - uses: actions/setup-python@5fda3b95a4ea91299a34e894583c3862153e4b97 # v7.0.0
      with:
        python-version: '3.12'
    - name: nodejsscan scan
      id: njsscan
      uses: ajinabraham/njsscan-action@231750a435d85095d33be7d192d52ec650625146 # v9
      with:
        args: '. --sarif --output results.sarif || true'
    - name: Upload njsscan report
      uses: github/codeql-action/upload-sarif@1c5b675653bb5c22dbe9b12b556ec555138e09fd # v4.38.1
      with:
        sarif_file: results.sarif
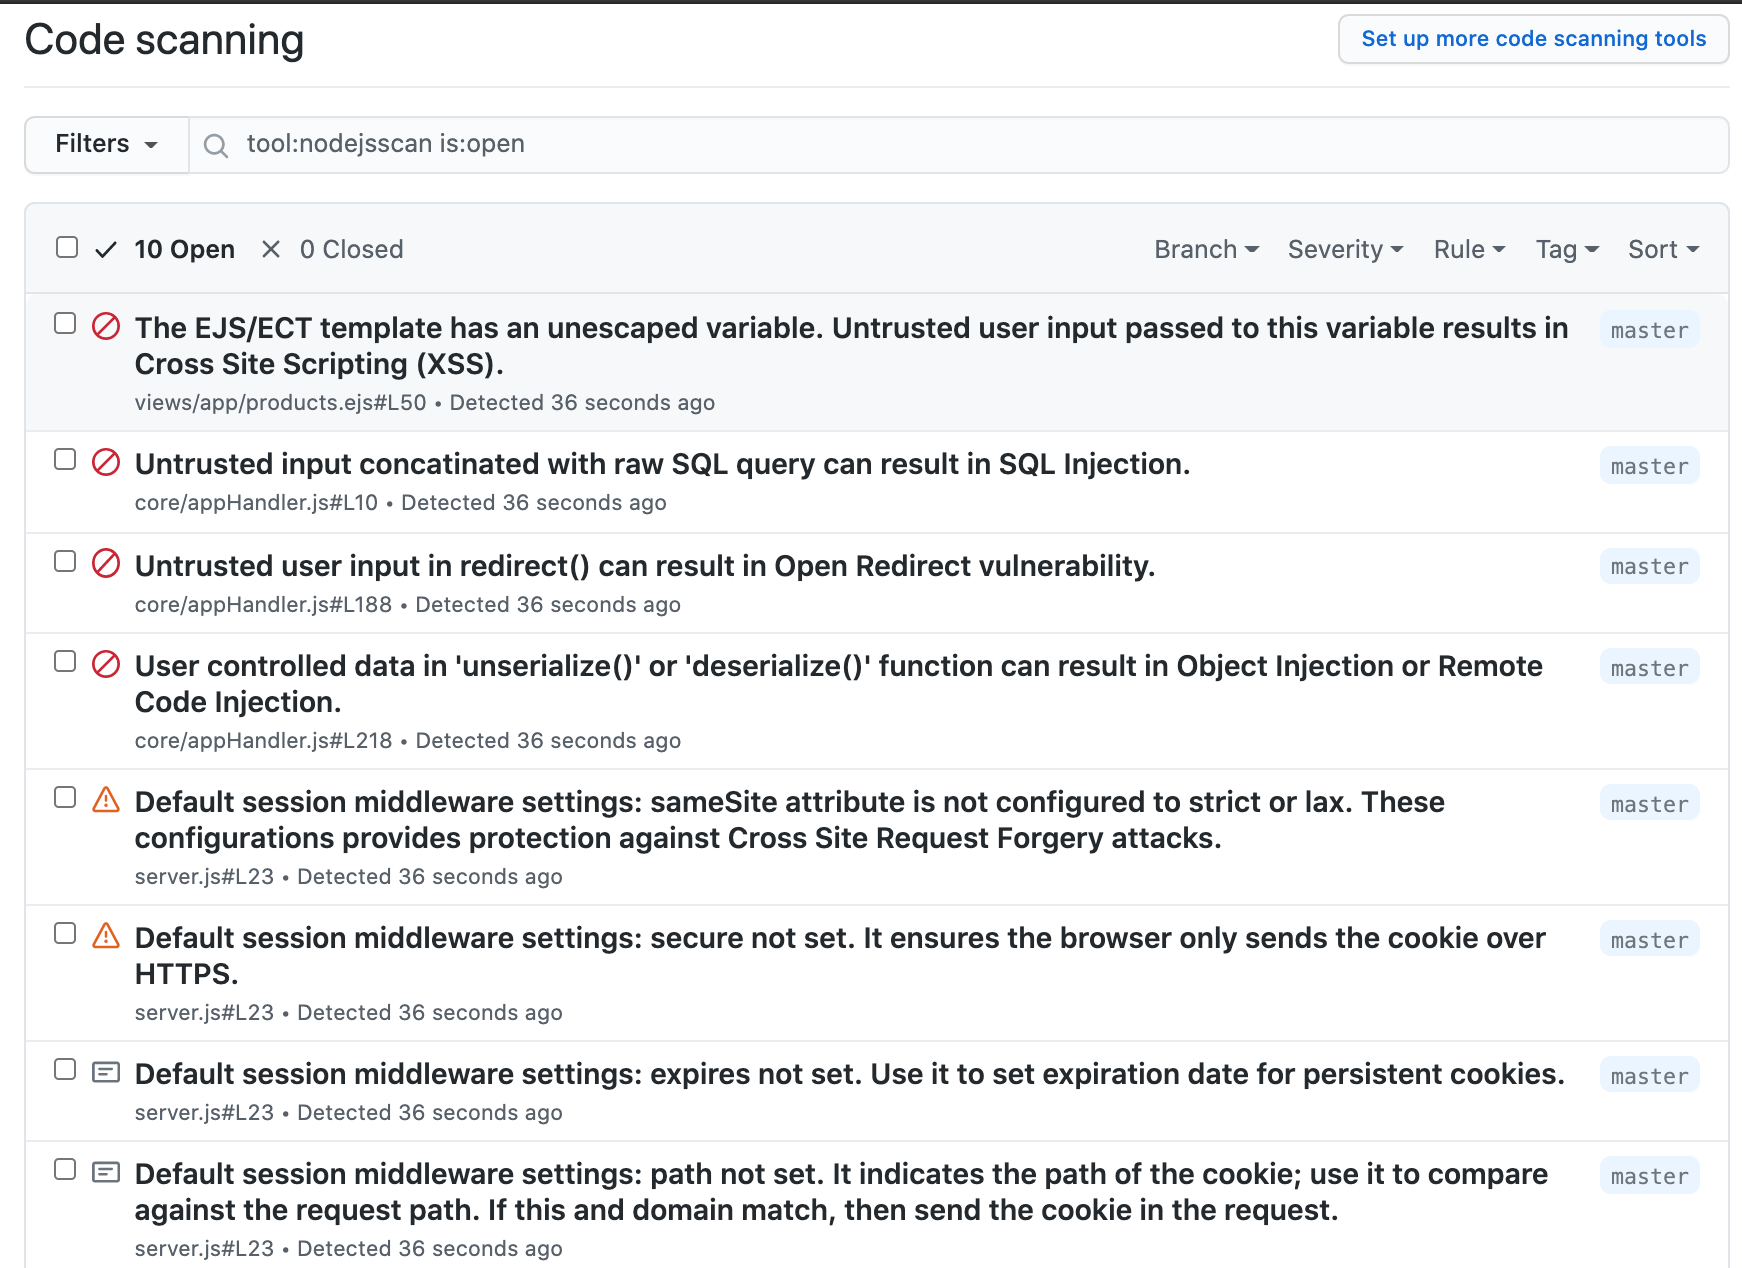
Gitlab CI/CD
أضف ما يلي إلى الملف .gitlab-ci.yml.
stages:
  - test

njsscan:
  image: python:3.12
  stage: test
  before_script:
    - pip3 install --upgrade njsscan
  script:
    - njsscan . --gitlab-sast -o gl-sast-report.json
  artifacts:
    when: always
    reports:
      sast: gl-sast-report.json
مثال على الأمر (محليًا):
njsscan . --gitlab-sast -o gl-sast-report.json
يكتب هذا تقرير GitLab SAST أصلي بحيث تظهر النتائج في تقرير الثغرات / أداة أمان MR دون الحاجة إلى محول SARIF.
مثال: dvna with njsscan gitlab
Travis CI
أضف ما يلي إلى الملف .travis.yml.
language: python
install:
    - pip3 install --upgrade njsscan
script:
    - njsscan .
Circle CI
أضف ما يلي إلى الملف .circleci/config.yaml
version: 2.1
jobs:
  njsscan:
    docker:
      - image: cimg/python:3.9.6
    steps:
      - checkout
      - run:
          name: Install njsscan
          command: pip install --upgrade njsscan
      - run:
           name: njsscan check
           command: njsscan .
Docker
صورة جاهزة من DockerHub
docker pull opensecurity/njsscan
docker run -v /path-to-source-dir:/src opensecurity/njsscan /src
البناء محليًا
docker build -t njsscan .
docker run -v /path-to-source-dir:/src njsscan /src