
 wgpsec/aboutsecurity
Everything for pentest. | 渗透测试知识库,以 AI Agent 可执行的格式沉淀安全方法论。
中文文档 | English
Penetration testing knowledge base with security methodologies in AI Agent-executable format.
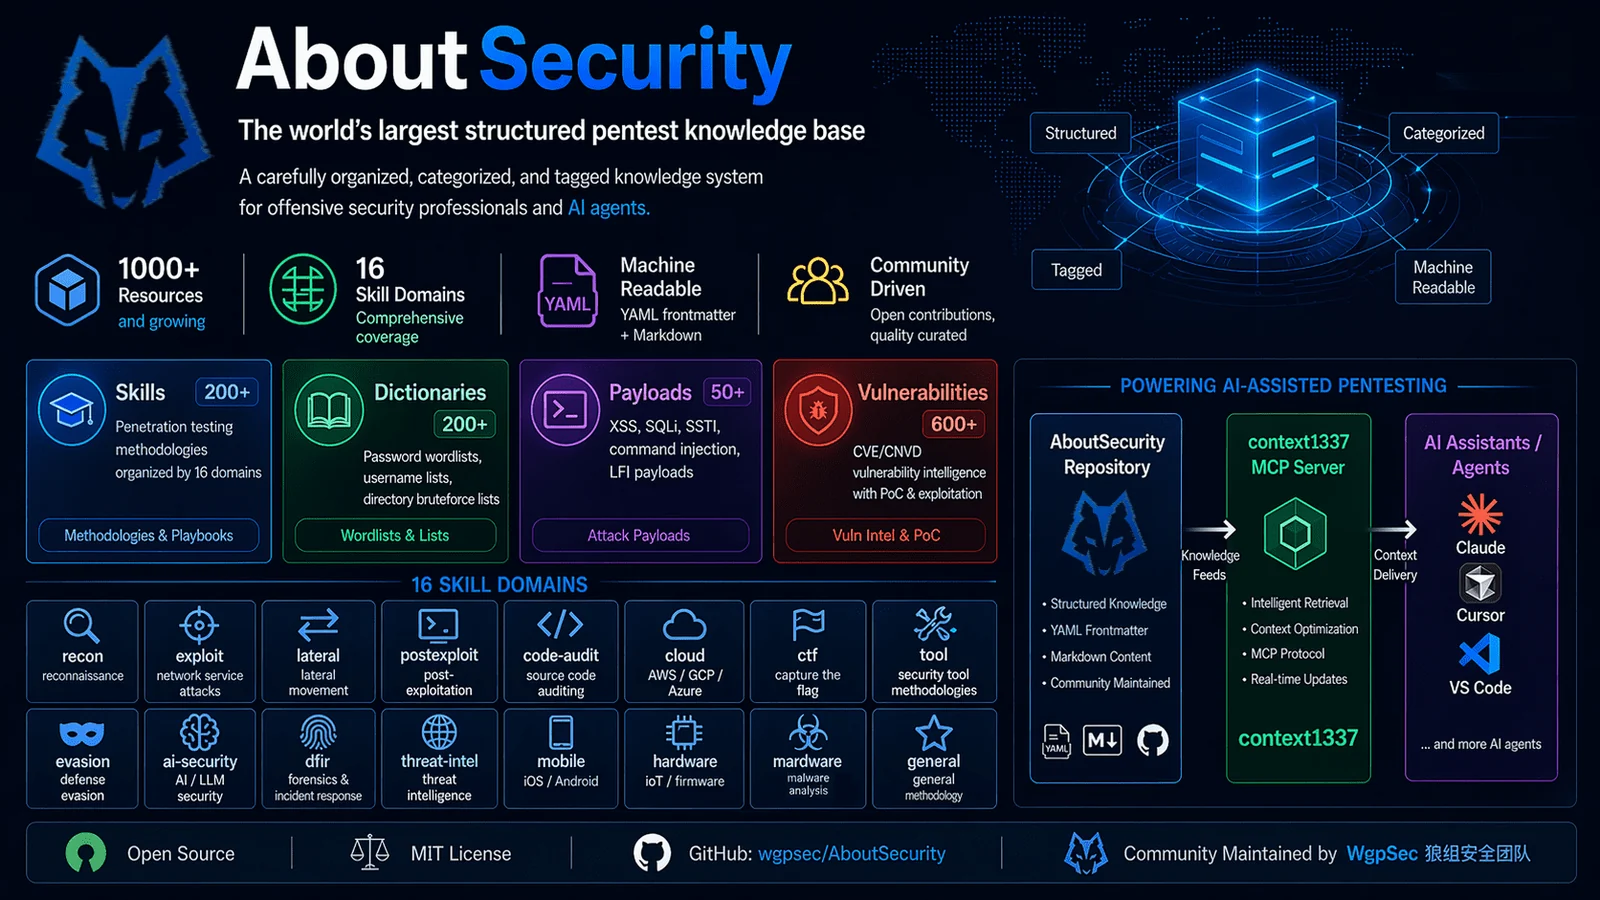
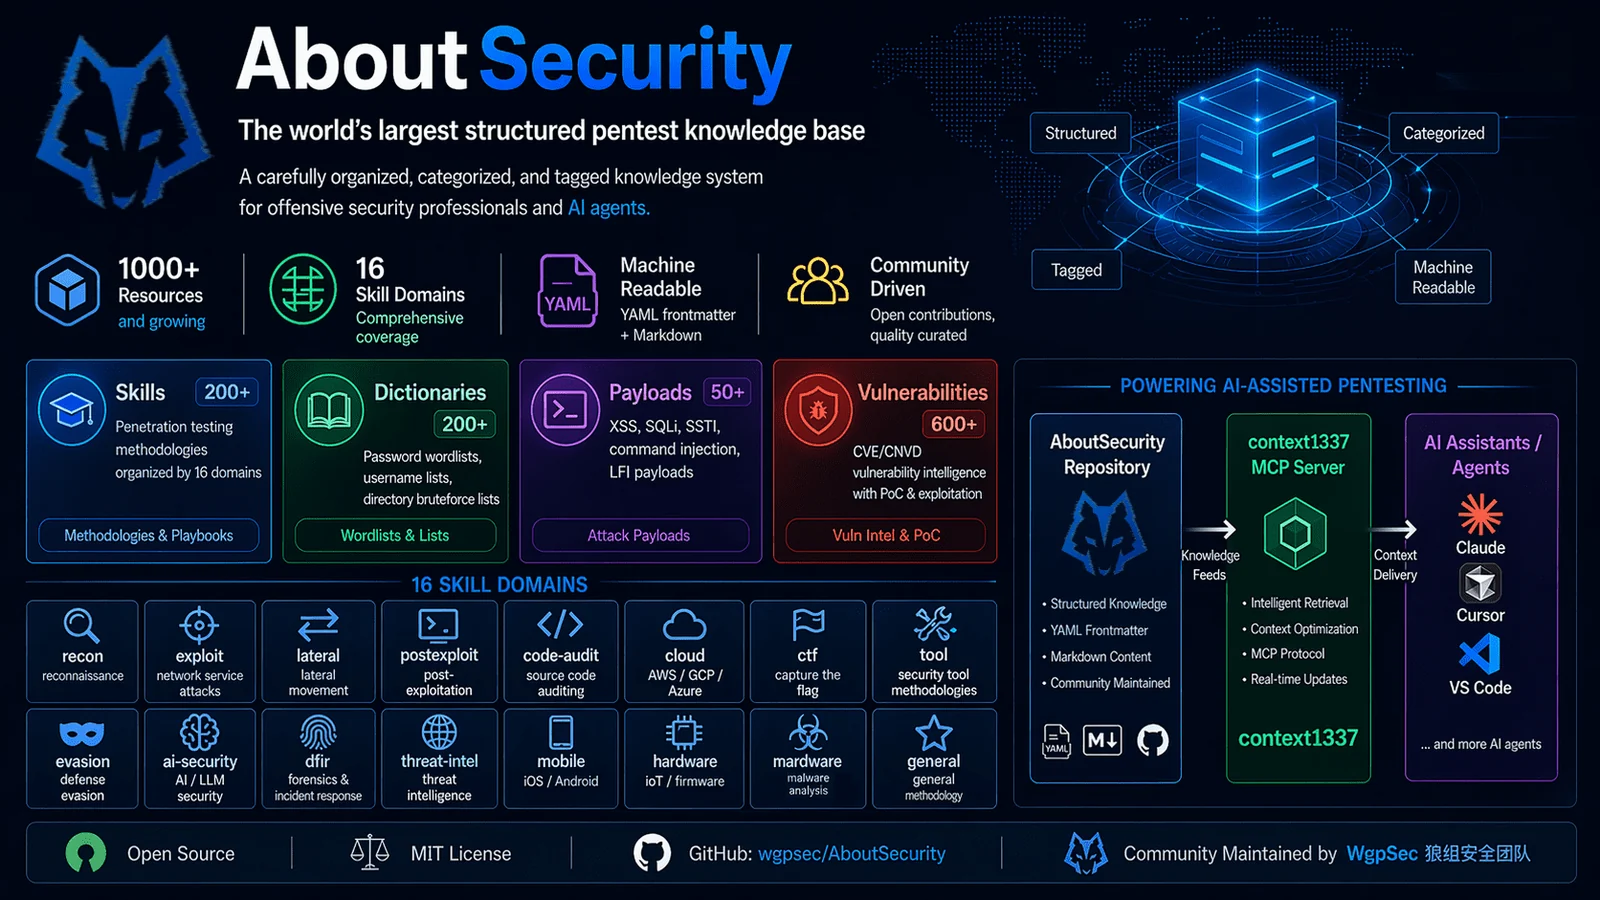
Skills/ — 200+ skill methodologies covering the full chain from recon to post-exploitation
ai-security/ — AI security (prompt injection, model jailbreaking, prompt leaking, agent attack chains)cloud/ — Cloud environments (Docker escape, K8s attack chains, AWS IAM, Alibaba Cloud, Tencent Cloud, Serverless)code-audit/ — Code auditing (PHP 8-skill system, Java 8-skill system covering injection/file/serialization/auth/framework/exploit chains)ctf/ — CTF competitions (Web challenges, reversing, PWN, cryptography, forensics, AI/ML)dfir/ — Digital forensics & incident response (memory forensics & anti-forensics, disk forensics, log evasion)evasion/ — Evasion techniques (C2 frameworks, shellcode generation, security research)exploit/ — Exploitation (organized by subcategory)
advanced/ — Advanced exploitation (HTTP smuggling, race conditions, supply chain attacks, OT/ICS, crypto attacks)auth/ — Authentication & authorization (JWT, OAuth/SSO, IDOR, CORS, CSRF, cookie analysis)binary/ — Binary exploitation methodology and toolsnetwork-service/ — Network service pentesting by port/protocol (SMB, FTP, SMTP, DNS, LDAP, etc.)web-method/ — Web methodology (injection, XSS, SSRF, SSTI, file upload, deserialization, WAF bypass...)general/ — General (report generation, supply chain auditing, mobile backend API)hardware/ — Hardware/physical access pentestinglateral/ — Lateral movement (AD domain attacks, NTLM relay, database pivoting, Kerberoasting, ACL abuse)malware/ — Malware (sample analysis methodology, C2 beacon config extraction, sandbox evasion)mobile/ — Mobile app pentesting (Android, iOS)postexploit/ — Post-exploitation
post-exploit-linux/ / post-exploit-windows/ — OS-level privilege escalation, credential theftpersist-maintain/ — Persistence techniques (cron, services, webshell)tool-delivery/ — Tool delivery to compromised hosts (fscan, frp, chisel, linpeas, mimikatz, etc.; Linux/Windows transfer methods: wget/curl/certutil/bitsadmin/PowerShell/python/nc/base64/SMB; no-egress scenarios, AV bypass, post-exec cleanup)product/ — Product-specific post-exploitation tactics (ArgoCD, Harbor, databases, middleware, Portainer, RabbitMQ)recon/ — Reconnaissance (subdomain enumeration, passive information gathering, JS API extraction)threat-intel/ — Threat intelligence (IOC evasion, APT simulation, threat hunting evasion)tool/ — Tool usage (fscan, nuclei, sqlmap, msfconsole, ffuf, hashcat)Dic/ — Dictionary library (lowercase hyphen-separated naming, each directory has _meta.yaml metadata)
auth/ — Usernames/passwords (complexity-rule passwords, WPA, pinyin names), plus default credentials of government/enterprise security appliances & OA systems (device-default/)network/ — DNS servers, excluded IP rangesport/ — Service-specific brute-force dictionaries (mysql, redis, ssh, etc. — 19 types)regular/ — General-purpose dictionaries (numbers, letters, addresses, keywords)web/ — Web directories, API parameters, middleware, upload bypass, webshells, HTTP headersPayload/ — Attack payloads (lowercase hyphen-separated naming, each directory has _meta.yaml metadata)
sqli/, xss/, ssrf/, xxe/, lfi/, rce/, upload/, cors/, hpp/, format/, ssi/, email/, access-bypass/, prompt-injection/, reverse-shell/Vuln/ — 600+ vulnerability entries, structured vulnerability data organized by product
ai/ — AI-related (ComfyUI, Dify, LangFlow, AnythingLLM, etc.)cloud/ — Cloud platforms (AWS API Gateway, etc.)middleware/ — Middleware (ActiveMQ, Nacos, Grafana, Jenkins, RocketMQ, etc. — 437 entries)network/ — Network devices (routers, switches, etc.)web/ — Web applications (1Panel, WordPress, OFBiz, etc.)postexploit/ vs Vuln/: Skills under
postexploit/are the post-exploitation layer — what to do after gaining access (privilege escalation, persistence, credential extraction, lateral movement, product-specific tactics). Entries underVuln/are the vulnerability data layer — affected versions, PoC code, specific exploitation steps per CVE. In short: Skills tell you "what to do after you're in", Vuln tells you "how to get in".
git clone https://github.com/wgpsec/AboutSecurity.git
# Sync all security skills to your working project
cd AboutSecurity
./scripts/sync-claude-skills.sh --target /path/to/your-project

# Result: creates .claude/skills/<skill-name>/ symlinks in the target project
# Claude Code will automatically discover and invoke these skills
Omit
--targetto sync to the AboutSecurity repo itself (for using Agent directly in this repo). Re-run after adding or removing skills.
Dictionaries and payloads don't need syncing — just reference the paths in your Agent conversation:
"Use the dictionaries under /path/to/AboutSecurity/Dic/auth/ to brute-force SSH"
"Load the payload list from /path/to/AboutSecurity/Payload/xss/ for fuzz testing"
The Agent reads these files directly via Read / Glob tools — just provide the correct repo path.
SKILL.md) that tells an AI Agent "what to do when encountering scenario X".claude/skills/<name>/SKILL.mdskills/exploit/web-method/sql-injection/SKILL.md), the sync script creates symlinks for the nested → flat mappingIf you want to search and invoke all resources in this repo via natural language through AI assistants (Claude Code, Cursor, Claude Desktop, etc.), deploy context1337 — a standalone MCP resource service that turns AboutSecurity from a file repo into a consumable API (like context7, but for security).
git clone https://github.com/wgpsec/context1337.git
cd context1337
make run   # One command: clone data + build index + start server
Then add the MCP service to your AI tool:
# Claude Code
claude mcp add aboutsecurity --transport http http://localhost:1337/mcp
After that, query with natural language: "Search for SQL injection resources", "List all XSS payloads", "Find critical Apache vulnerabilities", etc. See context1337 README for details.
skills/README.md covers the skills classification architecture, format specification, and benchmark testing process.
file-backup/, api-param/, prompt-injection/Fuzz_ prefix (legacy naming has been cleaned up)password-top100.txt, xss-tag-event-full.txt, complex-8char-upper-lower-digit.txt_meta.yaml Metadata