 nshalabi/attack-tools
SQLite relational data model for MITRE ATT&CK plus an adversary emulation planning tool, enriched with Red Canary ATOMIC tests and APT3 emulation plans.


Utilities for working with the MITRE™ ATT&CK™ framework, including a relational data model and an adversary emulation planning tool.
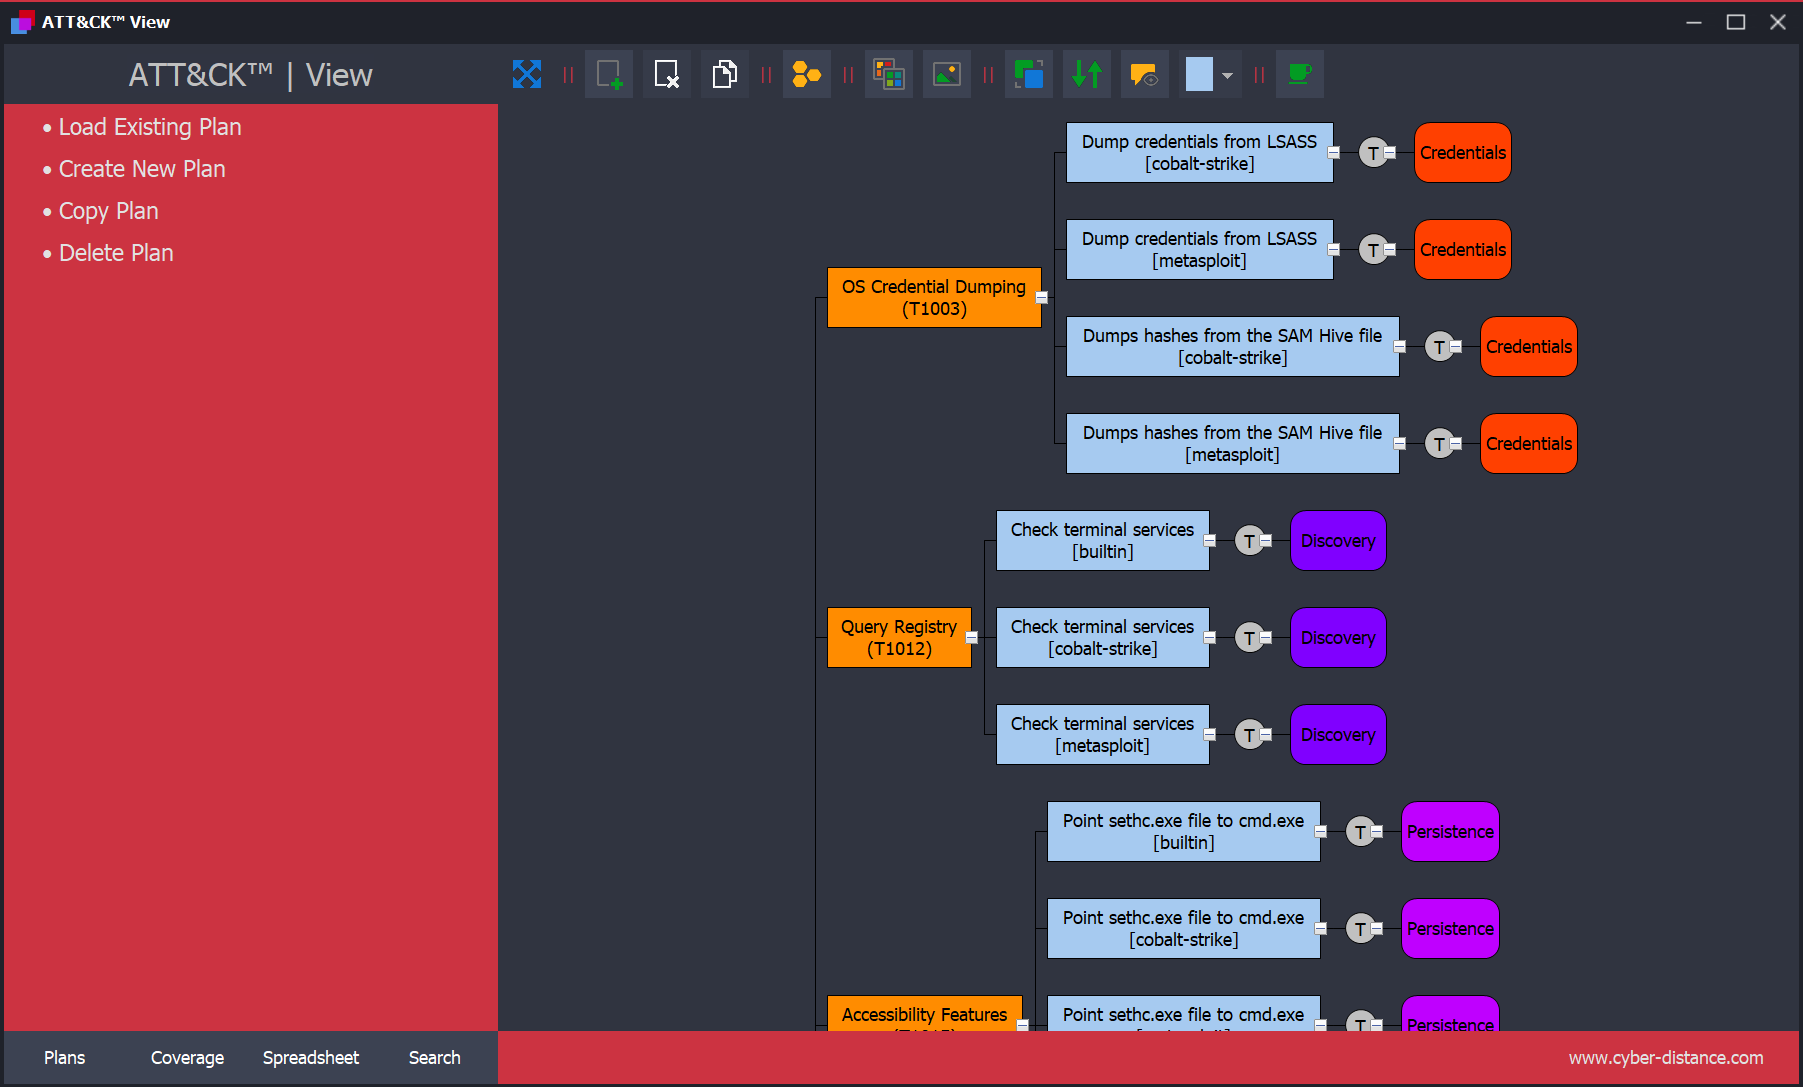
ATT&CK™ View is a planning tool to help defenders design adversary emulation plans using the MITRE™ ATT&CK™ framework.
It provides a structured approach and comes bundled with a full adversary emulation plan for APT3 (developed by MITRE™). It also serves as an example usage of teh relational data model and how to enrich teh model (extend) with additonal data such as Red Canary ATOMIC™ tests.
(Source: MITRE Adversary Emulation Plans)
The ATT&CK™ framework is widely used, but many use cases require ATT&CK-enabled tools.
This repository provides a relational database (SQLite) to simplify integration and enable building custom tools or fusing ATT&CK with other frameworks.
Think in terms of a data model instead of the underlying database technology — the schema can be adapted to any DBMS.
Example conceptual model (can be implemented in any RDBMS):

Below are sample SQL queries for exploring the ATT&CK™ database.
To run them, use any SQLite management tool (see SQLite Management Tools).
SELECT name
FROM sdos_object
WHERE type IS "attack-pattern";
OUTPUT
| name |
|---|
| .bash_profile and .bashrc |
| Access Token Manipulation |
| Accessibility Features |
| Account Discovery |
| Account Manipulation |
| ... |
SELECT id, name
FROM sdos_object
WHERE type IS "attack-pattern";
OUTPUT
| id | name |
|---|---|
| attack-pattern--01df3350-ce05-4bdf-bdf8-0a919a66d4a8 | .bash_profile and .bashrc |
| attack-pattern--dcaa092b-7de9-4a21-977f-7fcb77e89c48 | Access Token Manipulation |
| attack-pattern--9b99b83a-1aac-4e29-b975-b374950551a3 | Accessibility Features |
| attack-pattern--72b74d71-8169-42aa-92e0-e7b04b9f5a08 | Account Discovery |
| attack-pattern--a10641f4-87b4-45a3-a906-92a149cb2c27 | Account Manipulation |
| ... | |
The id field is a unique key that will be used frequently in many SQL queries
The external references are stored in external_references table, since one ATT&CK™ technique can have one or more references, the link between the two tables is the technique identifier (check previous query), I will list multiple ways to access the external references
SELECT name, external_id
FROM sdos_object INNER JOIN external_references
  ON sdos_object.id = external_references.fk_object_id
WHERE sdos_object.type IS "attack-pattern"
  AND external_references.source_name IS "mitre-attack";
OUTPUT
| name | external_id |
|---|---|
| .bash_profile and .bashrc | T1156 |
| Access Token Manipulation | T1134 |
| Accessibility Features | T1015 |
| Account Discovery | T1087 |
| Account Manipulation | T1098 |
| ... | |
SELECT name, external_id
FROM sdos_object INNER JOIN external_references
  ON sdos_object.id = external_references.fk_object_id
WHERE sdos_object.type IS "attack-pattern"
  AND x_mitre_platforms_windows IS "true"
  AND external_references.source_name IS "mitre-attack";
OUTPUT
| name | external_id |
|---|---|
| Access Token Manipulation | T1134 |
| Accessibility Features | T1015 |
| Account Discovery | T1087 |
| Account Manipulation | T1098 |
| AppCert DLLs | T1182 |
| ... | |
SELECT name, description
FROM sdos_object
WHERE type IS "malware";
OUTPUT
| name | description |
|---|---|
| 3PARA RAT | 3PARA RAT is a remote access tool (RAT) programmed in C++ that has been used by Putter Panda. (Citation: CrowdStrike Putter Panda) Aliases: 3PARA RAT |
| 4H RAT | 4H RAT is malware that has been used by Putter Panda since at least 2007. (Citation: CrowdStrike Putter Panda) Aliases: 4H RAT |
| ADVSTORESHELL | ADVSTORESHELL is a spying backdoor that has been used by APT28 from at least 2012 to 2016. It is generally used for long-term espionage and is deployed on targets deemed interesting after a reconnaissance phase. (Citation: Kaspersky Sofacy) (Citation: ESET Sednit Part 2) Aliases: ADVSTORESHELL, NETUI, EVILTOSS, AZZY, Sedreco |
| ASPXSpy | ASPXSpy is a Web shell. It has been modified by Threat Group-3390 actors to create the ASPXTool version. (Citation: Dell TG-3390) Aliases: ASPXSpy, ASPXTool |
| Agent.btz | Agent.btz is a worm that primarily spreads itself via removable devices such as USB drives. It reportedly infected U.S. military networks in 2008. (Citation: Securelist Agent.btz) Aliases: Agent.btz |
| ... | |
SELECT name, description
FROM sdos_object
WHERE type IS "intrusion-set";
OUTPUT

