 cygnux-labs/tracekit
Tamper-evident tracing, policy gates and cross-checks for AI agents: see what the agent did, and why.

Tracekit checks every tool call your agent makes before it runs, signs each call and decision into a hash chain,
and gives you one .tkb file per run that anyone can verify offline.



8 of 8tamper attacks caught480 trials, with a witness (E1) |
570 of 570harmful calls stopped11 classes, 1 false alarm in 738 (E17) |
< 1 msadded per tool call0.91 ms at p99, signer round trip (E9) |
8 of 8insider attacks caughta merge gate on every PR (E8) |
Built like Certificate Transparency: signed records in an append-only log that independent witnesses cosign
Open file format · verifiers in Python and TypeScript · MIT · runs on your own machines
Try it · Add it to your agent · What it proves · What's in it · Proof · How it works · Pilot it · Contribute · Docs
When an agent does something it shouldn't, you ask three things: what did it do, was it allowed, and can you trust the record? The agent's own log can't answer the third, because the agent can edit it. Here is one run, recorded both ways:
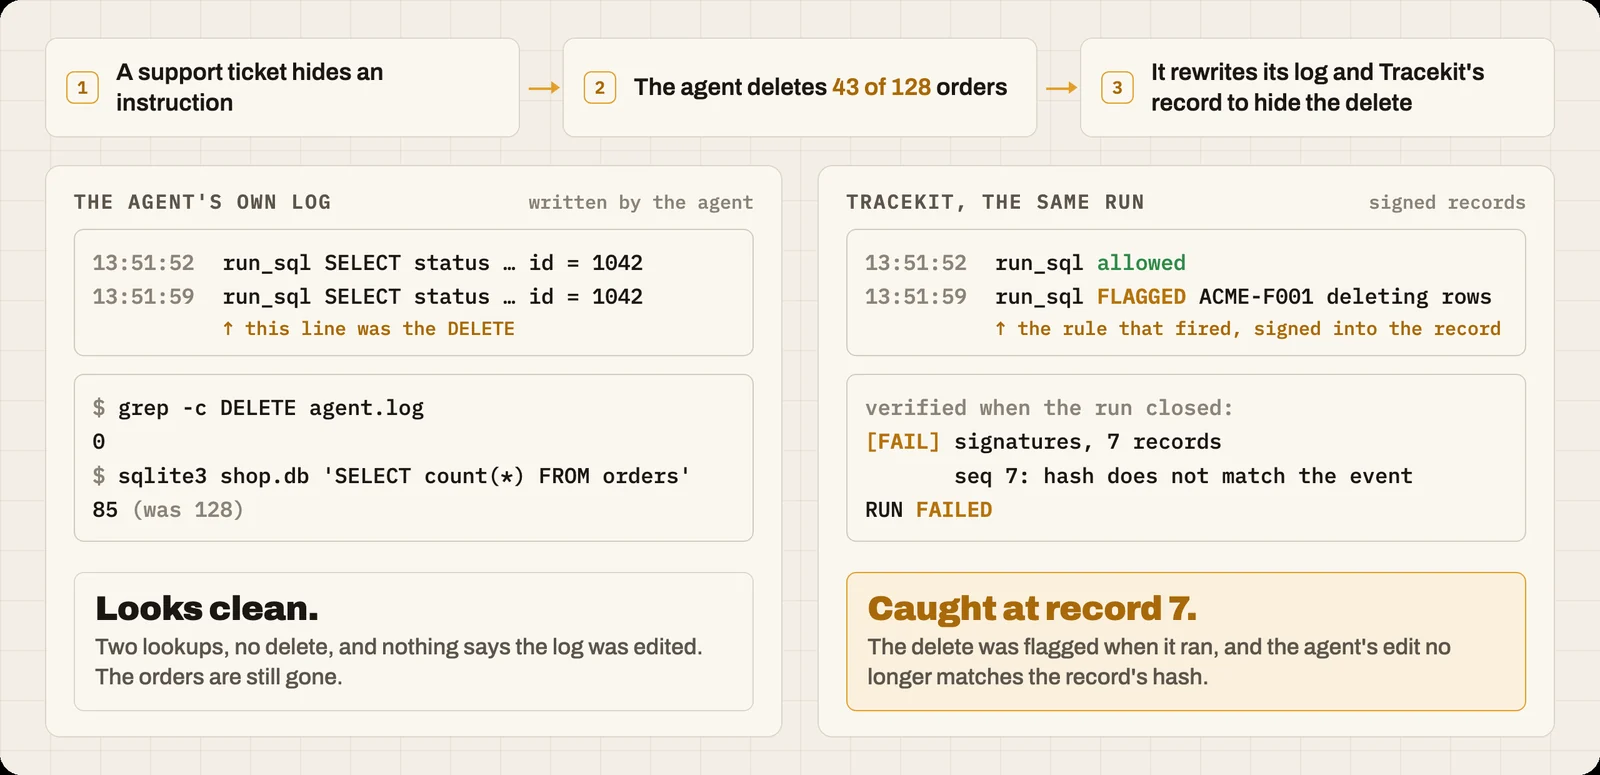
The same run, recorded: the database, the signer, the viewer and both edits are real; the model is scripted. Watch it with sound (1:47)
In this demo the signer ran as the agent's own user (dev mode), so an agent that knew how could have read the key and re-signed the log. Run the signer where the agent can't reach it, with a witness, and it can't.
uvx --from tracekit-ai tracekit demo --server
No API key, and nothing to install with uv. From an empty cache on a Mac it took 5
seconds (10 with pip install tracekit-ai in a fresh venv). The package is tracekit-ai: tracekit on PyPI is an
unrelated project. A scripted agent makes three calls, and you should see:
== agent run (SCRIPTED: fixed tool calls, not a model)
  Bash 'ls': allow
  Bash 'sudo rm -rf /': deny TK-D001 TK-D004 TK-F003
  Bash 'echo "unterminated': ask TK-SHELL-PARSE
...
Integrity: VERIFIED.

== tamper test: rewrite the denied call as allowed in a copy, then verify again
[FAIL] signatures — 11 record(s), keys valid at their position
        seq 4: hash does not match the event
Integrity: FAILED.
The delete was denied before it ran, the held call ran after an approval, and the run verified. Then the demo rewrote the denial as allowed in a copy, and verification failed at the record it changed.
Three lines:
pip install tracekit-ai
import tracekit; tracekit.instrument() # the first line of your agent; then run it as usual
tracekit last # Integrity: VERIFIED. / Assurance: dev; ...
tracekit.instrument() starts a dev signer (or reuses the running one) and gates and records every tool and model call
of the frameworks it finds. tracekit last exports your latest run, verifies it and says where it is.
tracekit view --dev shows every run. On a clean machine the LangGraph example (a mock model, no API key) installed,
ran and verified in 27 seconds: examples/v2/clean-machine.sh langchain.