 tylous/sourcepoint
Полиморфный генератор профилей C2 для Cobalt Strike, который автоматизирует создание уклончивых конфигураций beacon со случайными параметрами для HTTP, DNS и внедрения процессов для снижения обнаружения.

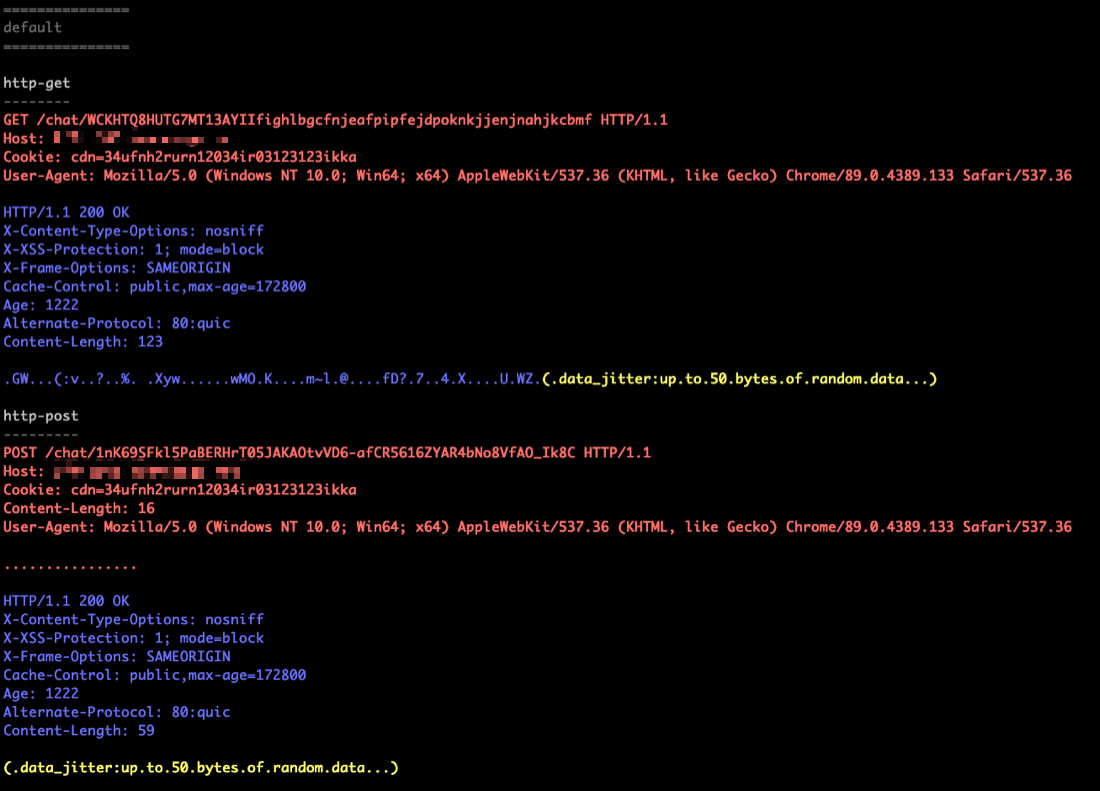
SourcePoint — это полиморфный генератор профилей C2 для Cobalt Strike C2, написанный на Go. SourcePoint позволяет создавать уникальные профили C2 на лету, что помогает уменьшить наши индикаторы компрометации («IoCs») и позволяет оператору создавать сложные профили с минимальными усилиями. Это было достигнуто путём тщательного изучения статей, а также примечаний к выпускам для выявления ключевых функций и модифицируемых возможностей. SourcePoint был разработан с намерением решить проблему того, как сделать нашу C2-активность сложнее для обнаружения, сосредоточившись на переходе от вредоносных IoCs к подозрительным. Цель здесь в том, что нашу C2 сложнее обнаружить, если наши IoCs не являются вредоносными по своей природе и требуют дополнительного исследования для выявления подозрительного характера. SourcePoint содержит множество различных настраиваемых параметров на выбор для изменения вашего профиля (в большинстве случаев, если оставить поле пустым, SourcePoint выберет их случайным образом за вас). Сгенерированные профили изменяют все аспекты вашей C2. Цель этого проекта — не только помочь в обходе средств защиты на основе обнаружения, но и помочь замаскировать C2-трафик и активность в среде, делая эту активность труднообнаружимой.
go install github.com/Tylous/SourcePoint
$go get gopkg.in/yaml.v2

$go build SourcePoint.go
#./SourcePoint -h

	   _____                            ____        _       __
	  / ___/____  __  _______________  / __ \____  (_)___  / /_
	  \__ \/ __ \/ / / / ___/ ___/ _ \/ /_/ / __ \/ / __ \/ __/
	 ___/ / /_/ / /_/ / /  / /__/  __/ ____/ /_/ / / / / / /_
	/____/\____/\__,_/_/   \___/\___/_/    \____/_/_/ /_/\__/
  							(@Tyl0us)


Usage of ./SourcePoint:
  -Allocation string
        Minimum amount of memory to request for injected content (must be higher than 4096)
  -BeaconGate string
        Specify beacon gate options (All, Comms, Core, Cleanup) or specific APIs
  -CDN string
        CDN cookie name (typically used for AzureEdge profiles)
  -CDN-Value string
        CDN cookie value (typically used for AzureEdge profiles)
  -Customuri string
        The base URI for custom HTTP GET/POST profile - Cannot be used with CustomuriGET or CustomuriPOST
  -CustomuriGET string
        The base URI for custom HTTP GET profile - Must be used with CustomuriPOST
  -CustomuriPOST string
        The base URI for custom HTTP POST profile - Must be used with CustomuriGET
  -Datajitter string
        Appends a value to HTTP-Get and HTTP-Post server output (default "50")
  -Forwarder
        Enabled the X-forwarded-For header (Good for when your C2 is behind a redirector)
  -Host string
        Team server domain name
  -Httplib string
        Select the default HTTP Beacon library:
        [*] wininet
        [*] winhttp' (default "winhttp")
  -Injector string
        Select the preferred method to allocate memory in the remote process:
        [*] VirtualAllocEx (Great for cross architecture i.e x86 -> x64 and x64->x86)
        [*] NtMapViewOfSection (A more stealthly option, however fails over to VirtualAllocEx, generating more events when it does)
  -Jitter string
        Jitter percentage for beacon call home
  -Keylogger string
        Select the preferred method the beacon will use to log keystrokes:
        [*] GetAsyncKeyState (Uses GetAsyncKeyState API (Separate DLL for x86/x64 process))
        [*] SetWindowsHookEx (Uses SetWindowsHookEx API)
  -Keystore string
        SSL keystore name
  -Metadata string
        Specifies how to transform and embed metadata into the HTTP request:
        [*] base64
        [*] base64url
        [*] netbios
        [*] netbiosu (default "base64url")
  -Outfile string
        Name of output file
  -PE_Clone string
        PE file beacon will mimic (Use the number):
        [1] ActivationManager.dll
        [2] audioeng.dll
        [3] AzureSettingSyncProvider.dll
        [4] BingMaps.dll
        [5] DIAGCPL.dll
        [6] EDGEHTML.dll
        [7] FILEMGMT.dll
        [8] FIREWALLCONTROLPANEL.dll
        [9] GPSVC.dll
        [10] gpupvdev.dll
        [11] libcrypto.dll
        [12] srvcli.dll
        [13] srvsvc.dll
        [14] Windows.Storage.Search.dll
        [15] Windows.System.Diagnostics.dll
        [16] Windows.System.Launcher.dll
        [17] Windows.System.SystemManagement.dll
        [18] Windows.UI.BioFeedback.dll
        [19] Windows.UI.BlockedShutdown.dll
        [20] Windows.UI.Core.TextInput.DLL
        [21] winsqlite3.dll
        [22] WMNetMgr.DLL
        [23] wwanapi.dll
        [24] WWANSVC.DLL
        [25] wow64win.dll
        [26] wow64.dll
        [27] ctiuser.dll (Carbon Black's DLL)
        [28] InProcessClient.dll (SentinelOne's DLL)
        [29] umppc.dll (CrowdStrike's DLL)
        [30] CyMemDef64.dll (Cylance's DLL)
  -Password string
        SSL certificate password
  -PostEX_Name string
        File Post-Ex activities will spawn and inject into (Use the number):
        [1] WerFault.exe
        [2] WWAHost.exe
        [3] choice.exe
        [4] bootcfg.exe
        [5] w32tm.exe
        [6] expand.exe
        [7] fsutil.exe
        [8] gpupdate.exe
        [9] gpresult.exe
        [10] logman.exe
        [11] mcbuilder.exe
        [12] mtstocom.exe
        [13] pcaui.exe
        [14] powercfg.exe
        [15] svchost.exe
  -Profile string
        HTTP GET/POST profile (Use the number):
        [1] Windowsupdate
        [2] Slack
        [3] Gotomeeting
        [4] Outlook.Live
        [5] Safebrowsing [Cloudfront Compatible]
        [6] AzureEdge [AzureEdge Compatible]
        [7] Field-Keyword [Cloudfront Compatible]
        [8] Custom (Used with ProfilePath)
  -ProfilePath string
        Path of custom HTTP GET/POST profile...
  -Sleep string
        Initial beacon sleep time
  -Stage string
        Disable host staging (Default: False) (default "false")
  -Syscall string
        Defines the ability to use direct/indirect system calls instead of the standard Windows API functions calls:
        [*] None
        [*] Direct
        [*] Indirect (default "None")
  -TasksDnsProxyMaxSize string
        The maximum size (in bytes) of proxy data to transfer via the DNS communication channel at a check in
  -TasksMaxSize string
        The maximum size (in bytes) of task(s) and proxy data that can be transferred through a communication channel at a check in
  -TasksProxyMaxSize string
        The maximum size (in bytes) of proxy data to transfer via the communication channel at a check in
  -ThreadSpoof
        Sets post-ex DLLs to spawn threads with a spoofed start address. These are generated randomly (default true)
  -RdllUseDriploading
        Enable driploading for RDLL stage (gradually loads beacon in smaller chunks to evade memory scanners) (default true)
  -RdllDriploadDelay string
        Delay in milliseconds between loading chunks for RDLL driploading (default: random 100-200ms)
  -UseDriploading
        Enable driploading for process injection (gradually writes payload in smaller chunks to evade EDR) (default true)
  -DriploadDelay string
        Delay in milliseconds between writing chunks for process injection driploading (default: random 100-200ms)
  -CopyPEHeader
        Copy PE Header to match cloned DLL characteristics (default false)
  -EafBypass
        Enable Export Address Filtering (EAF) bypass (default false)
  -RdllLoader string
        Rdll Loader Options:
        [*] PrependLoader (default)
        [*] StompLoader (Older method)
  -RdllUseSyscalls
        Use Syscalls for Rdll operations (default false)
  -SmartInject
