 sh1yo/x8
Набор инструментов для обнаружения скрытых параметров


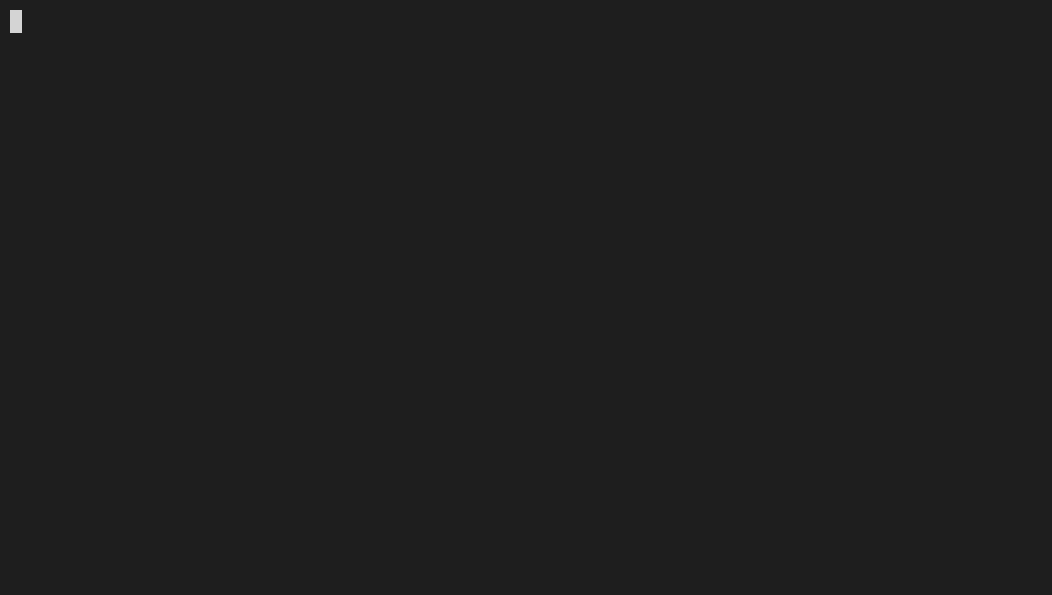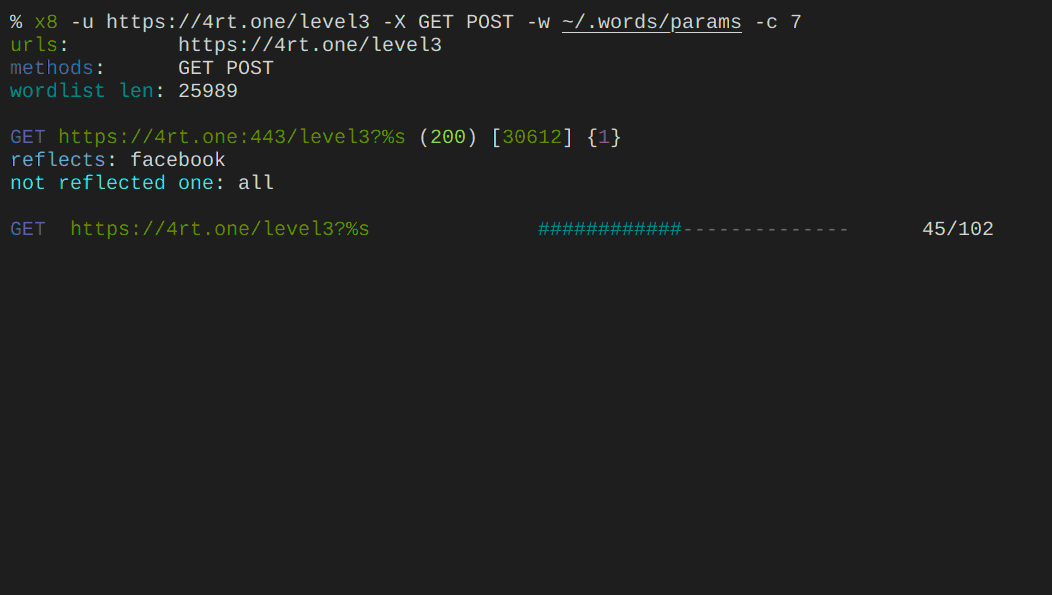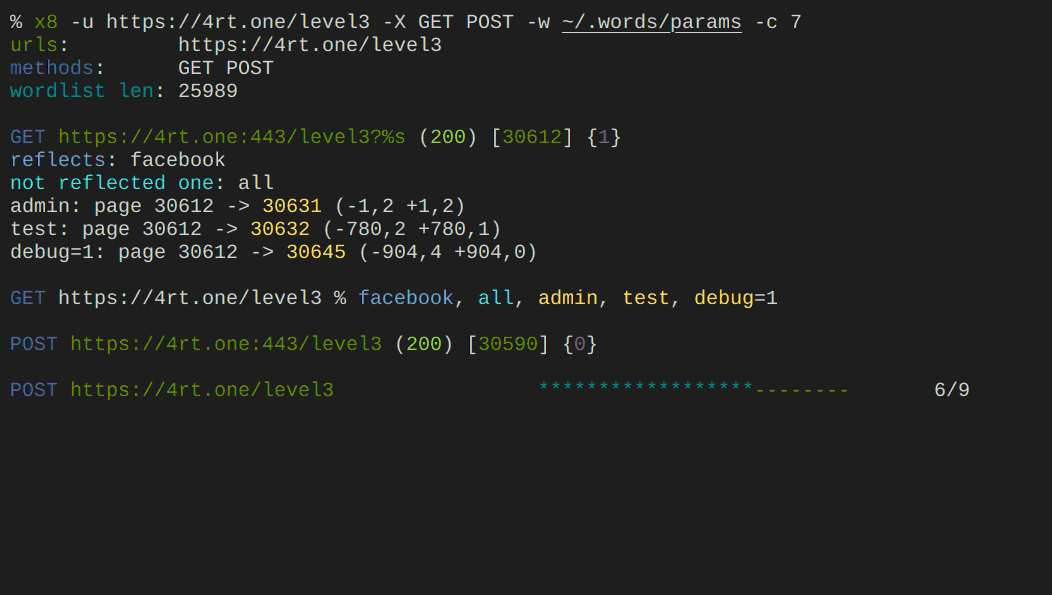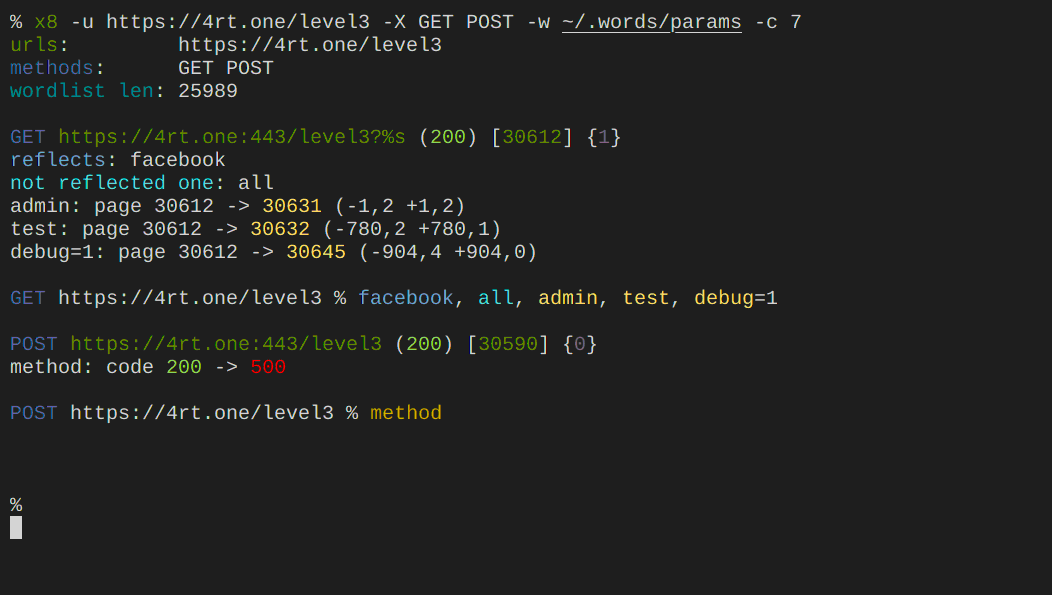
Инструмент помогает выявлять скрытые параметры, которые могут быть уязвимы или раскрывать интересный функционал, упущенный другими тестировщиками. Высокая точность достигается за счет построчного сравнения страниц, сравнения кодов ответов и отражений.
Документация с объяснением всех функций доступна по адресу https://sh1yo.art/x8docs/. Исходный код документации находится в /docs.md.
admin=true.x8 -u "https://example.com/" -w <wordlist>
С параметрами по умолчанию:
x8 -u "https://example.com/?something=1" -w <wordlist>
/?something=1 эквивалентно /?something=1&%s
x8 -u "https://example.com/" -X POST -w <wordlist>
Или с произвольным телом:
x8 -u "https://example.com/" -X POST -b '{"x":{%s}}' -w <wordlist>
%s будет заменён на различные параметры, например {"x":{"a":"b3a1a", "b":"ce03a", ...}}
x8 -u "https://example.com/" "https://4rt.one/" -W0
x8 -u "https://example.com/" --param-template "user[%k]=%v" -w <wordlist>
Теперь каждый запрос будет выглядеть как /?user[a]=hg2s4&user[b]=a34fa&...
Иногда параметры необходимо кодировать. Это тоже возможно:
x8 -u "https://example.com/?path=..%2faction.php%3f%s%23" --encode -w <wordlist>
GET /?path=..%2faction.php%3fWTDa8%3Da7UOS%26rTIDA%3DexMFp...%23 HTTP/1.1
Host: example.com
x8 -u "https://example.com" --headers -w <wordlist>
Также можно нацелиться на отдельные заголовки:
x8 -u "https://example.com" --headers -H "Cookie: %s" -w <wordlist>
Вы можете проверить инструмент и сравнить его с другими по следующим URL:
https://4rt.one/level1 (GET)
https://4rt.one/level3 (GET)
USAGE:
    x8 [FLAGS] [OPTIONS]

FLAGS:
        --append                       Append to the output file instead of overwriting it.
    -B                                 Equal to -x http://localhost:8080
        --check-binary                 Check the body of responses with binary content types
        --disable-additional-checks    Private
        --disable-colors
        --disable-custom-parameters    Do not automatically check parameters like admin=true
        --disable-progress-bar
        --disable-trustdns             Can solve some dns related problems
        --encode                       Encodes query or body before making a request, i.e & -> %26, = -> %3D
                                       List of chars to encode: ", `, , <, >, &, #, ;, /, =, %
    -L, --follow-redirects             Follow redirections
        --force                        Force searching for parameters on pages > 25MB. Remove an error in case there's 1
                                       worker with --one-worker-per-host option.
    -h, --help                         Prints help information
        --headers                      Switch to header discovery mode.
                                       NOTE Content-Length and Host headers are automatically removed from the list
        --invert                       By default, parameters are sent within the body only in case PUT or POST methods
                                       are used.
                                       It's possible to overwrite this behavior by specifying the option
        --mimic-browser                Add default headers that browsers usually set.
        --one-worker-per-host          Multiple urls with the same host will be checked one after another,
                                       while urls with different hosts - are in parallel.
                                       Doesn't increase the number of workers
        --reflected-only               Disable page comparison and search for reflected parameters only.
        --remove-empty                 Skip writing to file outputs of url:method pairs without found parameters
        --replay-once                  If a replay proxy is specified, send all found parameters within one request.
        --strict                       Only report parameters that have changed the different parts of a page
        --test                         Prints request and response
    -V, --version                      Prints version information
        --verify                       Verify found parameters.

OPTIONS:
    -b, --body <body>                                       Example: --body '{"x":{%s}}'
                                                            Available variables: {{random}}
    -c <concurrency>                                        The number of concurrent requests per url [default: 1]
        --custom-parameters <custom-parameters>
            Check these parameters with non-random values like true/false yes/no
            (default is "admin bot captcha debug disable encryption env show sso test waf")
        --custom-values <custom-values>
            Values for custom parameters (default is "1 0 false off null true yes no")


