
 ncsa/ssh-auditor
Лучший способ сканировать слабые пароли SSH в вашей сети


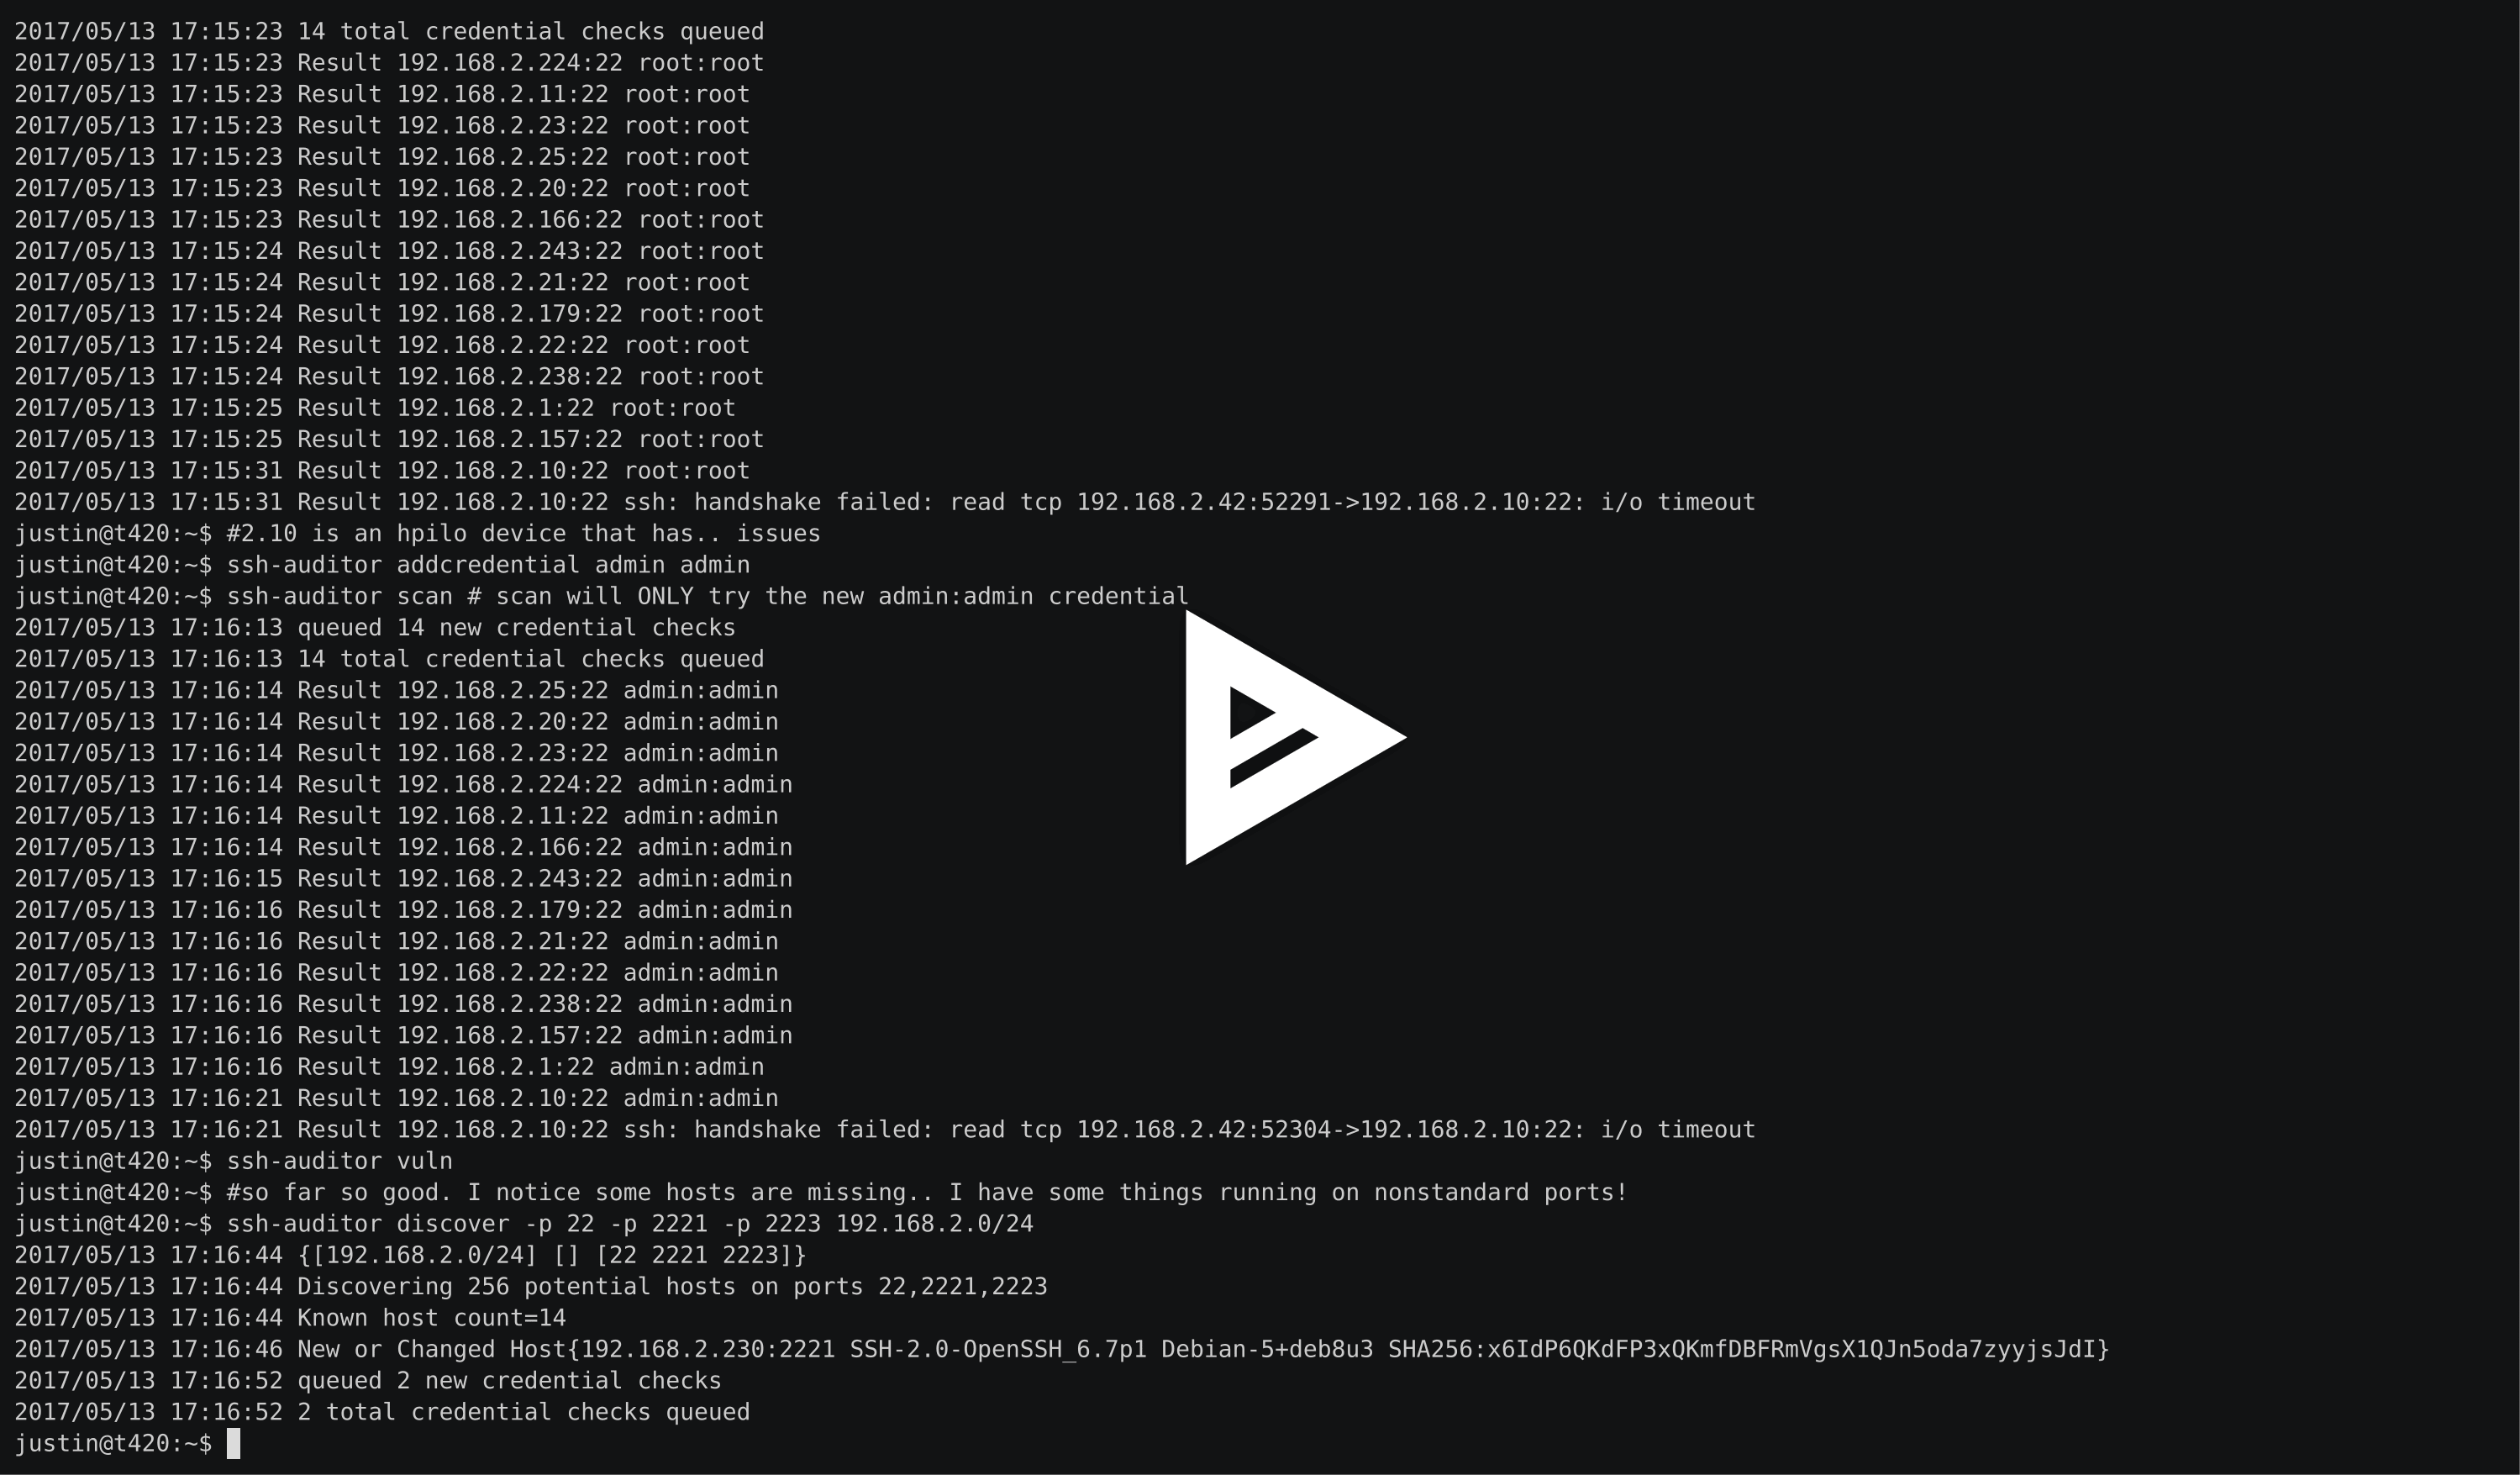
ssh-auditor будет автоматически:
scan_interval для каждой учетной записи — по умолчанию 14 дней.Он спроектирован так, что вы можете запускать ssh-auditor discover + ssh-auditor scan из cron каждый час для проведения постоянного аудита.
$ brew install go # or however you want to install the go compiler
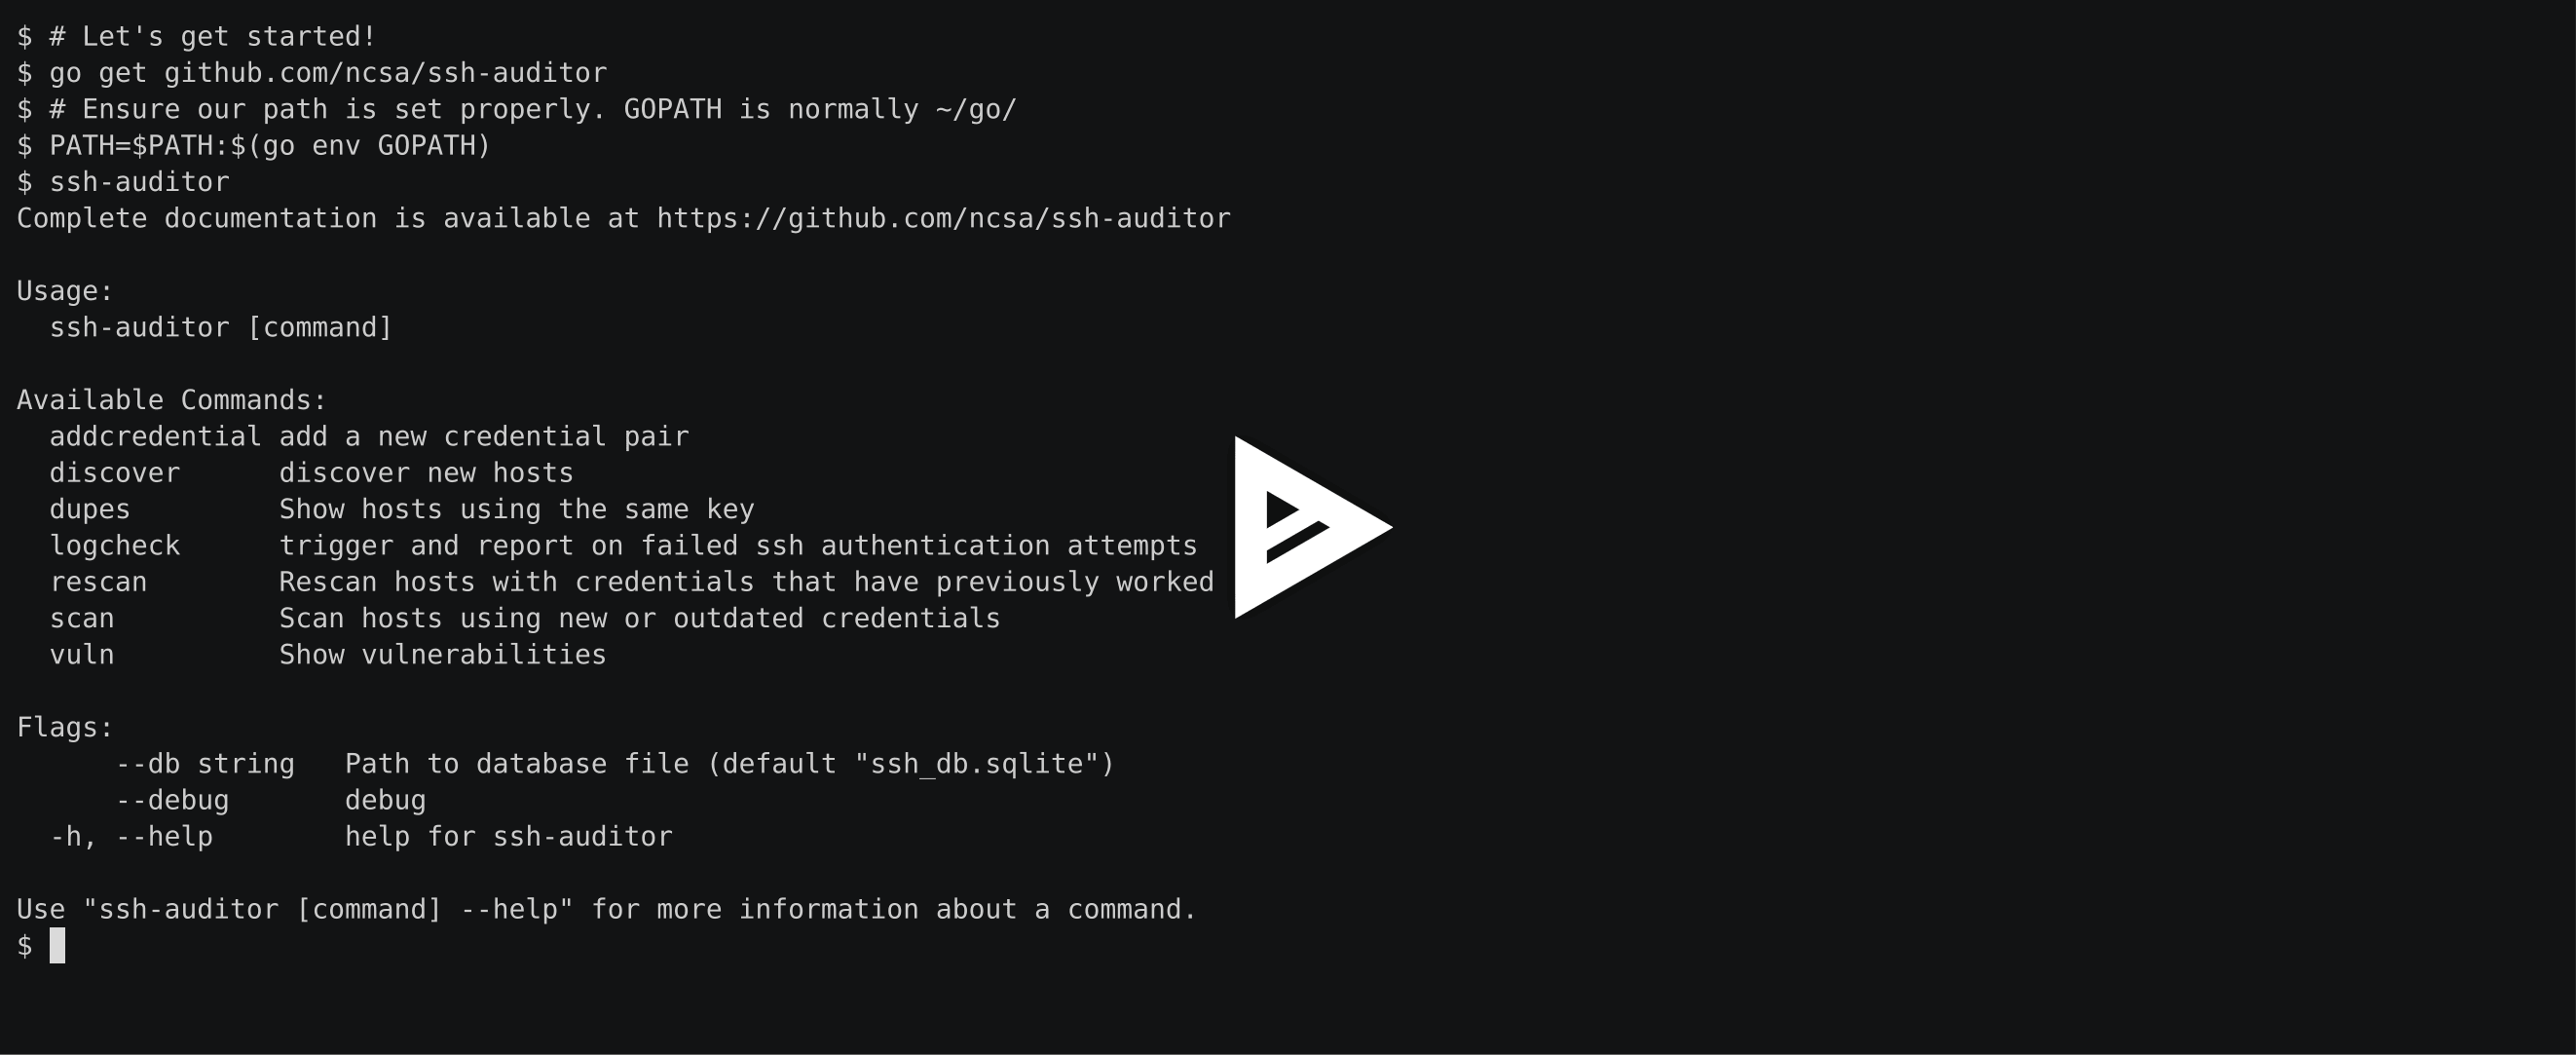
$ go get github.com/ncsa/ssh-auditor
$ go build
$ make static
$ ulimit -n 4096
$ ./ssh-auditor discover -p 22 -p 2222 192.168.1.0/24 10.0.0.1/24
$ ./ssh-auditor addcredential root root
$ ./ssh-auditor addcredential admin admin
$ ./ssh-auditor addcredential guest guest --scan-interval 1 #check this once per day
$ ./ssh-auditor scan
$ ./ssh-auditor vuln
$ ./ssh-auditor rescan
$ ./ssh-auditor dupes
scan_interval в дняхЭто запрос, который выполняется ssh-auditor vuln:
select
        hc.hostport, hc.user, hc.password, hc.result, hc.last_tested, h.version
 from
        host_creds hc, hosts h
 where
        h.hostport = hc.hostport
 and    result!='' order by last_tested asc
