 ultrasecurity/storm-breaker
Full-featured Social Engineering Framework with Page Cloning, MITM Proxy, Credential Capture, Session Extraction, and Real-time Monitoring.

Phishing & social-engineering framework — clone any page, inject capture payloads, harvest credentials and sessions from one live panel.


For authorized security testing and research only. Use within legal boundaries.
flowchart LR
    A[🎯 Clone / proxy<br/>the target page] --> B[🔗 Victim opens<br/>your link]
    B --> C[⚡ Payloads fire<br/>in their browser]
    C --> D[📊 Data streams<br/>to your panel]
    style A fill:#0b3d5c,stroke:#00c8ff,color:#fff
    style B fill:#0b3d5c,stroke:#00c8ff,color:#fff
    style C fill:#0b3d5c,stroke:#00c8ff,color:#fff
    style D fill:#0b3d5c,stroke:#00c8ff,color:#fff
Storm Breaker renders a copy of the target page, swaps in capture modules that run client-side, and relays everything the visitor's browser gives up back to a real-time operator dashboard.
| 🧬 Page Cloning | Headless Chrome render with cURL fallback | 🔀 MITM Proxy | Transparent reverse proxy, full URL & fetch/XHR rewrite |
| 🔑 Credential Sniffing | Extracts from form, JSON, GraphQL, Livewire, Inertia | ✅ Login Verification | Auto-detects success from status, redirect & body |
| 🍪 Session Hijacking | Exports Cookie-Editor JSON for instant replay | 📷 Camera Capture | Periodic webcam snapshots with clean revoke handling |
| 🎙️ Mic Recording | Grabs audio clips from the visitor's microphone | 📍 Geolocation | GPS pings with coordinates and accuracy |
| 🖥️ Device Fingerprint | Browser, OS, screen & hardware (always on) | 🧩 Custom JS | Inject your own scripts over the runtime API |
| 🌐 Homograph Generator | 9 confusion sets + RDAP availability check | 📡 Live SSE Stream | Server-Sent push for credential & session alerts |
| Targets | Credentials | Dashboard |
|---|---|---|
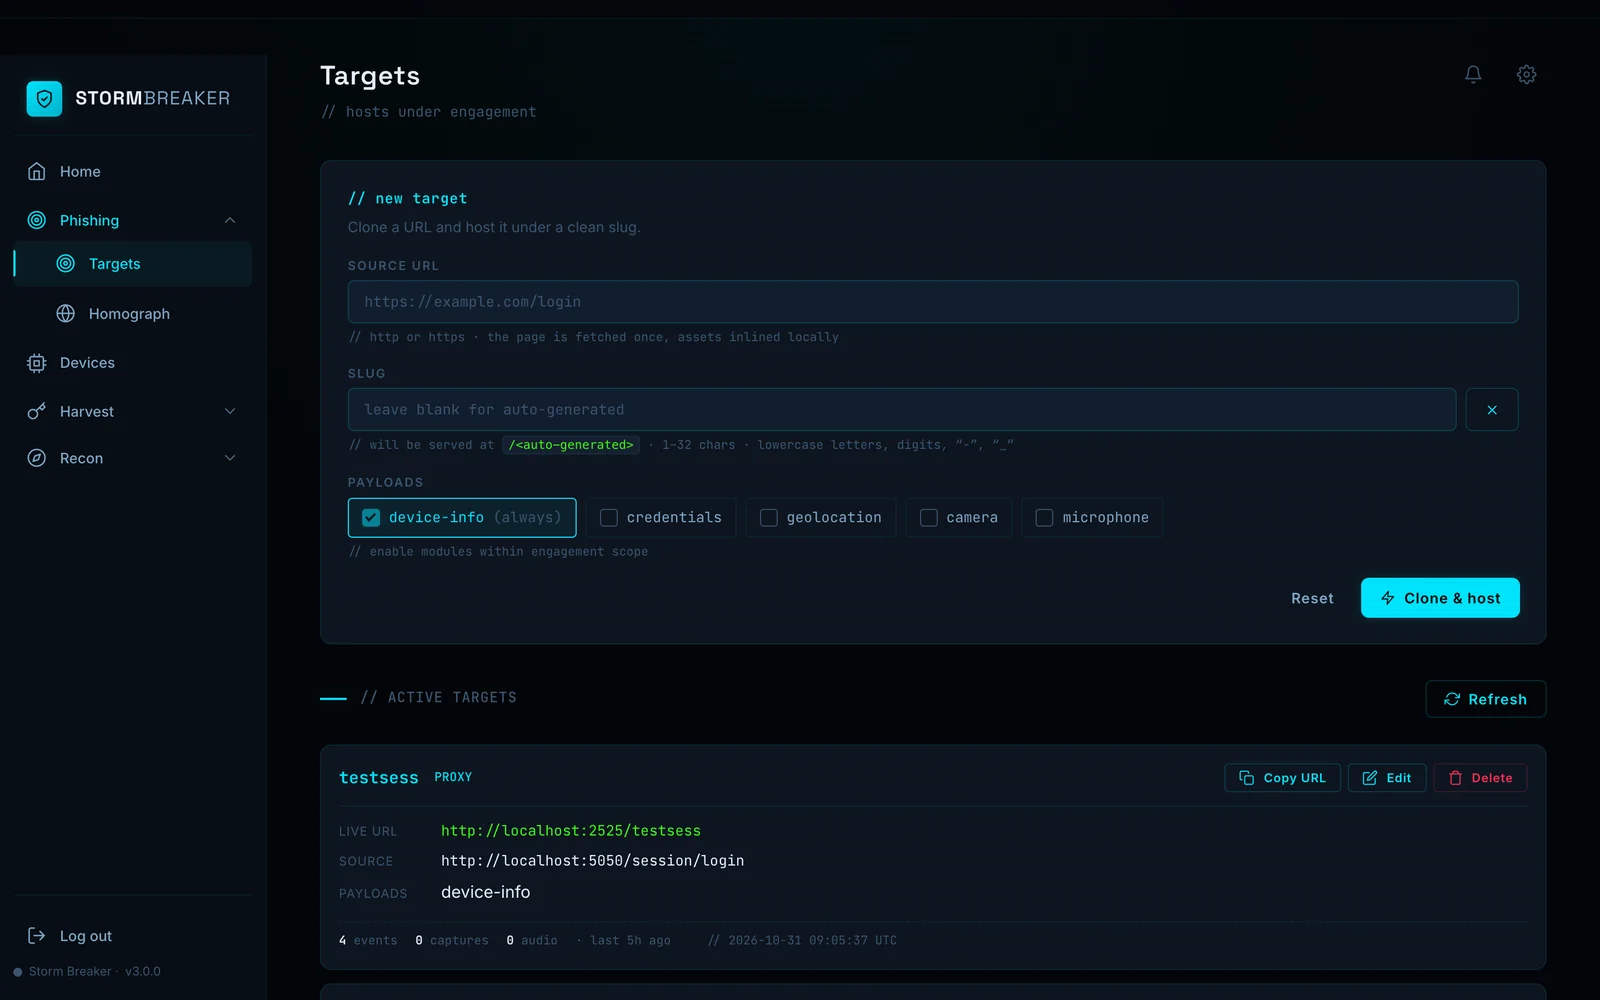 | 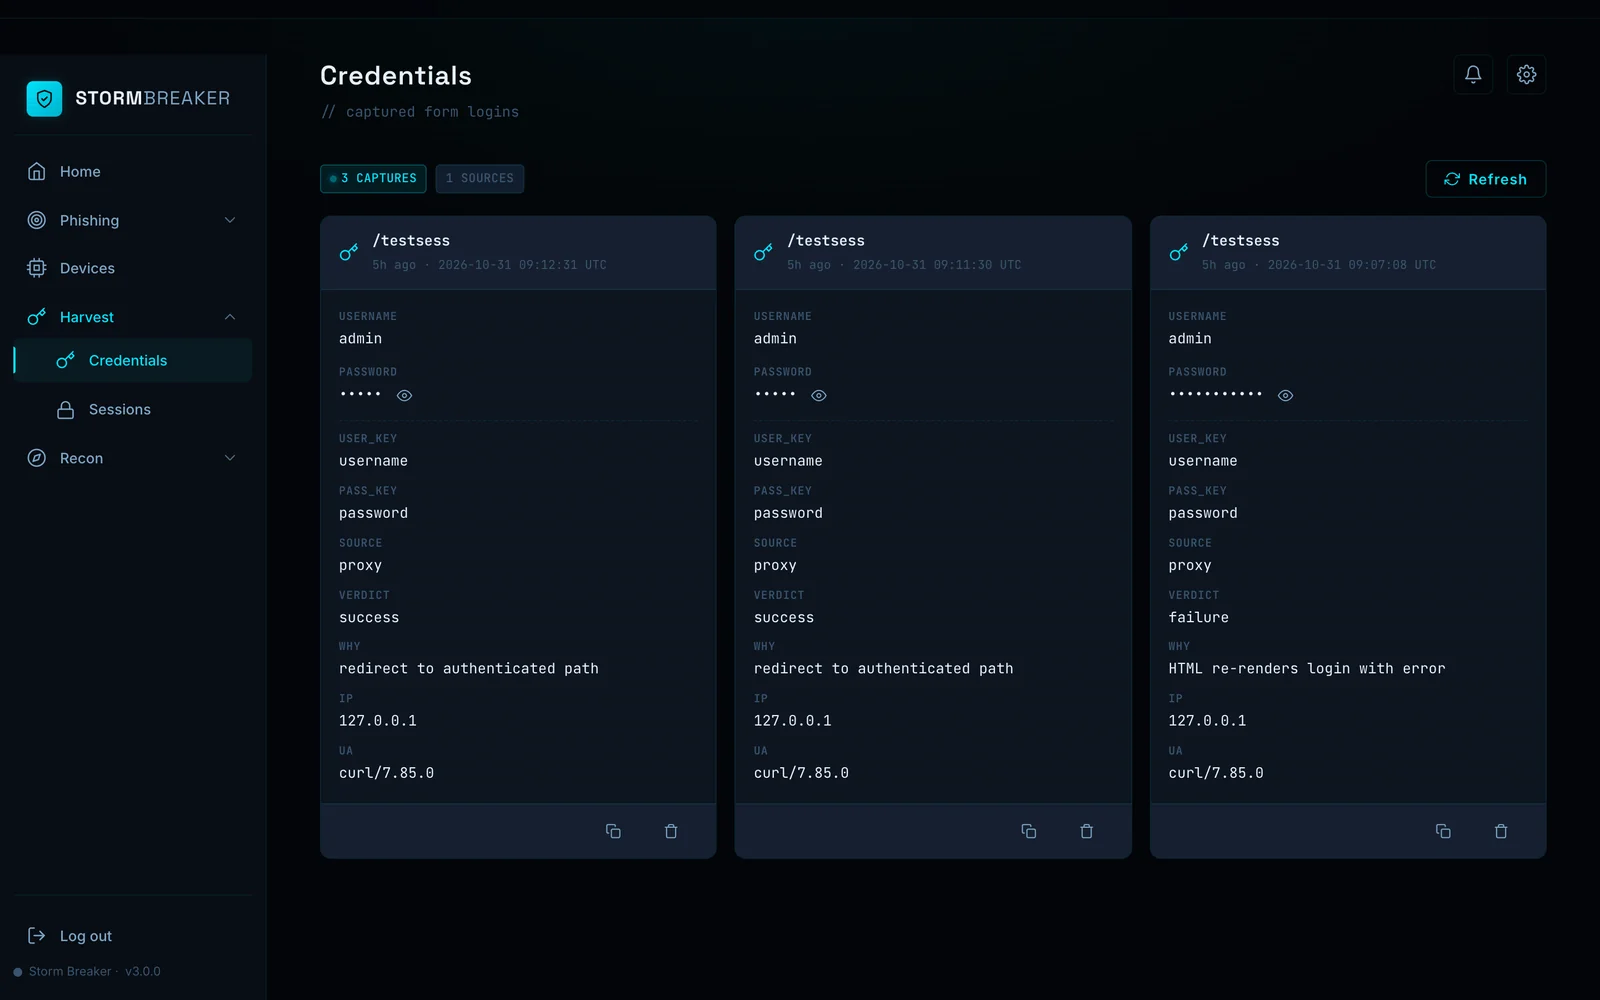 | Dashboard |
| Clone & host a page | Captured logins | Live operator panel |
git clone https://github.com/ultrasecurity/Storm-Breaker.git
cd Storm-Breaker
bash deploy.sh --local    # installs PHP + extensions (macOS & Linux)
php run-local.php          # → http://localhost:2525  (admin / admin)
--local installs only what's needed to run on your own machine — no nginx, systemd, or TLS.
| Platform | Package Manager | Root |
|---|---|---|
| macOS | Homebrew | No |
| Debian / Ubuntu | apt | Yes |
| RHEL / Fedora | dnf | Yes |
Requirements: PHP 7.4+ with ext-sqlite3, ext-curl, ext-json, ext-session, ext-mbstring. Headless Chrome is optional and unlocks full SPA cloning. Local mode is for testing — camera, mic, and geo need HTTPS, so use a server deployment for live work.
sudo bash deploy.sh
The wizard walks through server IP, admin credentials, and a free Let's Encrypt certificate (have your domain and email ready). HTTPS is required — camera, mic, and geolocation only work in a secure context.
# skip the wizard with flags
sudo bash deploy.sh --ip 1.2.3.4 --domain panel.example.com --email [email protected]
| Flag | Description |
|---|---|
--ip | Server IP (auto-detected) |
--domain | Domain for Let's Encrypt TLS |
--email | Email for Let's Encrypt |
--php-port | Internal PHP port (default 9874) |
--user | Service user (default stormbreaker) |
--uninstall | Remove service + nginx config |
1. Open Targets, enter a URL, pick payloads, and hit Clone & host. → 2. Send the generated link to your target. → 3. Watch captures land under Devices, Credentials, Captures, Audio, and Geo Data.
capture.php is intentionally public, guarded by slug validation, path-traversal checks, and size/rate caps.data/ is protected by router.php (with .htaccess as backup).NoNewPrivileges, PrivateTmp, ProtectSystem=full, UMask=0077.Migrating a v2 install:
php storm-web/tools/migrate-to-sqlite.php # imports result.txt, meta.json, captures/, audio/ — safe to re-run
Released under the MIT License.
Descubra as ferramentas mais usadas pela nossa comunidade.
Sem dados de popularidade ainda.
