
Skip to content
KitploitKITPLOIT
FerramentasExploitsBlog
Log in
Enviar
FerramentasExploitsBlog
Enviar

Ferramentas de Hacking, PenTest e Cibersegurança para o seu Arsenal de Segurança!

Kitploit é um diretório de ferramentas de hacking, cibersegurança e pentesting. Descubra as últimas atualizações de projetos para encontrar vulnerabilidades, analisar sistemas, automatizar testes e fortalecer sua segurança.

FeedsContatoPrivacidade© 2026 Kitploit

Diretório de Ferramentas

Categorias

Ver todas as categorias
Loading categories
Ferramentas/GitHubGitHub/topscoder/nuclei-wordfence-cve
Vulnerability ScannersVulnerability AnalysisExploitationInformation GatheringWeb SecurityCrawler
GitHubtopscoder/nuclei-wordfence-cve

nuclei-wordfence-cve

80k+ WordPress Nuclei templates, updated daily from Wordfence intel—filter by severity/tags/CVE and scan in one line. 🚀🔒

Ver Repositório
1.3k15451há 1 diaRevisado pelo Kitploit
Compartilhar
Conteúdo não disponível no idioma solicitado. Mostrando versão em inglês.

Nuclei + Wordfence = ♥

90,951 Nuclei Templates for WordPress Security Scanning 🥳

GitHub Workflow Status pre-commit Templates added
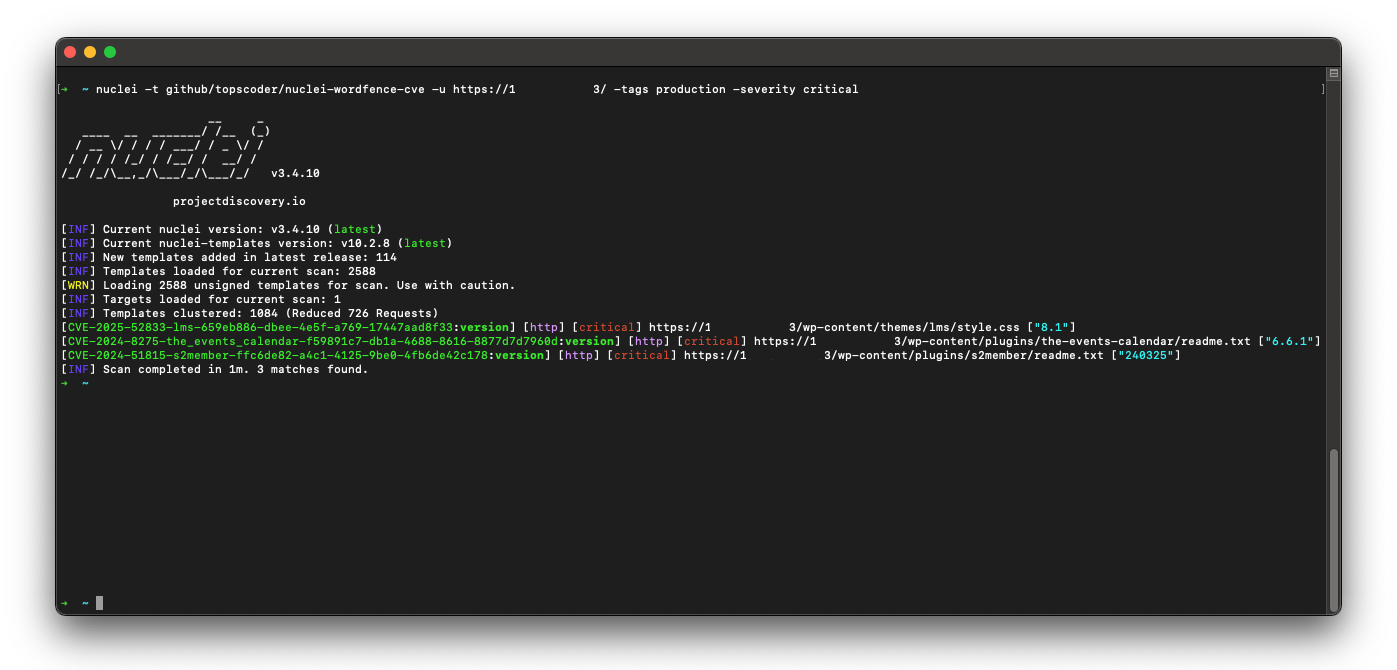
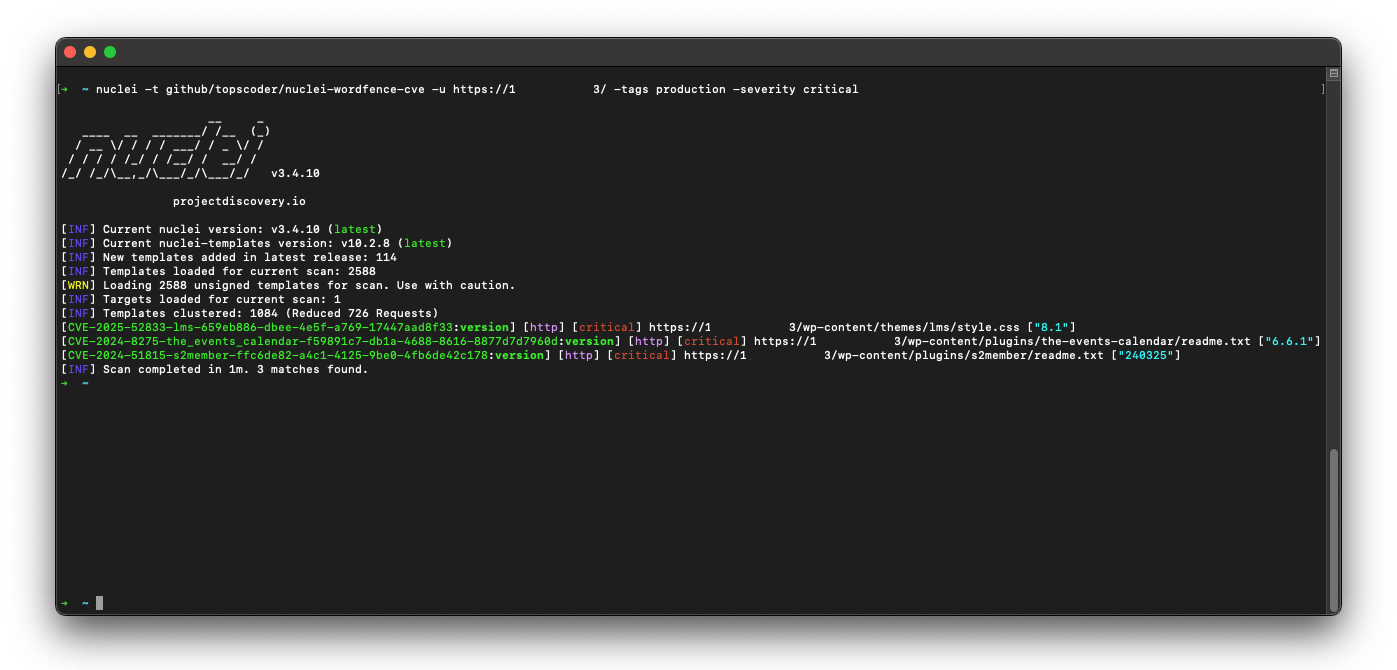
Project Demo

Level up your WordPress security game! This project's got a treasure trove of fresh Nuclei templates for WordPress. Scan for weaknesses in Core, plugins, and themes – all based on the latest intel from Wordfence.com.

Here's why this is your new best friend:

  • Massive collection: No more hunting for individual templates, you've got a whole arsenal at your fingertips.
  • Always on point: These templates stay updated with the freshest threats, so you're never behind the curve.
  • Open source magic: Need to tweak a template for a specific situation? No problem, you've got full control.

If you're guarding a WordPress site, this project is your secret weapon to identify vulnerabilities before the bad guys do. Stop wasting time and secure your sites like a pro!


[!TIP] If you found this project helpful, please consider buying me a coffee.

Buy Me A Coffee

✨ What's in it?!

categorytotal
wp-plugins83,883
wp-themes6,286
wp-core788
other0
severitytotal
critical8,859
high16,247
medium23,786
low42,059
info0

🚀 Quick Start

To install this nuclei-wordfence-cve repository for use with Nuclei, you can use the following commands:

export GITHUB_TEMPLATE_REPO=topscoder/nuclei-wordfence-cve
nuclei -update-templates

Once you have installed this template repo using the commands above, you can run the following command to scan for vulnerabilities using Nuclei:

nuclei -t github/topscoder/nuclei-wordfence-cve -u https://target.com

Wordfence provides two separate feeds for vulnerabilities. The first feed includes only production vulnerabilities, each with an assigned CVE. The second feed contains candidate vulnerabilities, which do not yet have a CVE assigned and may or may not be promoted to the production feed. To differentiate templates generated from these feeds, a tag is assigned to each template—either production or candidate—allowing you to target them using a tag filter.

Include only production templates:

nuclei -t github/topscoder/nuclei-wordfence-cve -tags production -u https://target.com

Include only candidate templates:

nuclei -t github/topscoder/nuclei-wordfence-cve -tags candidate -u https://target.com

💻 Examples

Here are some examples how to use the templates:

  • To scan for all known vulnerabilities in WordPress, you can run the following command:
nuclei -t github/topscoder/nuclei-wordfence-cve -u https://target.com
  • To scan for a CVE specific vulnerability, you can run the following command:
nuclei -t github/topscoder/nuclei-wordfence-cve -template-id cve-2023-32961 -u https://target.com
  • To scan only for critical vulnerabilities, you can run the following command:
nuclei -t github/topscoder/nuclei-wordfence-cve -severity critical -u https://target.com
  • To scan only for WordPress core vulnerabilities, you can run the following command:
nuclei -t github/topscoder/nuclei-wordfence-cve -tags wp-core -u https://target.com
  • To scan only for WordPress plugin vulnerabilities, you can run the following command:
nuclei -t github/topscoder/nuclei-wordfence-cve -tags wp-plugin -u https://target.com
  • To scan only for WordPress theme vulnerabilities, you can run the following command:
nuclei -t github/topscoder/nuclei-wordfence-cve -tags wp-theme -u https://target.com
  • To go wild, you can combine and combine and combine:
nuclei -t github/topscoder/nuclei-wordfence-cve -tags wp-plugin,wp-theme -severity critical,high
  • To go even wilder, you can use the template condition flag (-tc) that allows complex expressions like the following ones:
nuclei -t github/topscoder/nuclei-wordfence-cve -template-condition "contains(to_lower(name),'cross-site scripting') || contains(to_upper(name),'XSS')" -u https://target.com

nuclei -t github/topscoder/nuclei-wordfence-cve -template-condition "contains(to_lower(name),'sql injection') || contains(to_lower(description),'sql injection')" -u https://target.com

nuclei -t github/topscoder/nuclei-wordfence-cve -template-condition "contains(to_lower(name),'file inclusion') || contains(to_lower(description),'file inclusion')" -u https://target.com

Baixar ferramenta

Mais Populares

Ver todos →

Descubra as ferramentas mais usadas pela nossa comunidade.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 O kit definitivo de OSINT: grafo de investigação, pontuação de confiança, famílias de alias, mapa, linha do tempo e relatórios. 49 módulos, mais de 400 sites, sem necessidade de chaves de API.

    654
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    # Aplicativo de Execução em Um Toque GhostLock (CVE-2026-43499)

    490
  • 3

    ARTEX

    baarai/artex

    Plataforma autônoma de testes de penetração multiagente com LLM, com agentes planejador/executor, grafos de ativos e de exploração, registro de tráfego MITM e reteste de vulnerabilidades.

    395
  • 4

    redforge

    cybersecurity91/redforge

    Kit de ferramentas de red team do lado do navegador com 102 ferramentas offline para reconhecimento, geração de payloads, ataques a credenciais, criptografia, codificação e relatórios de engajamento.

    336
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    O sistema de ação para cibersegurança nativa em IA—onde a intenção se torna execução governada, a evidência se torna memória operacional, e cada operação melhora a próxima.

    258
  • 6

    antifox

    antifox-ai/antifox

    Plataforma de testes de penetração autónoma com multiagentes de IA que executa reconhecimento, descoberta de superfície de ataque, validação de exploração e entrega de relatórios com evidências.

    252

Explore todas as ferramentas

Navegue pela nossa coleção de ferramentas

Ver todas as ferramentas →