secrary/makin
makin - revela truques anti-debugging e anti-VM [Este projeto não é mais mantido]

Criei o makin para tornar a avaliação inicial de malware um pouco mais fácil para mim, acho que é útil para outros também. Ele ajuda a revelar técnicas de detecção de depurador usadas por uma amostra.
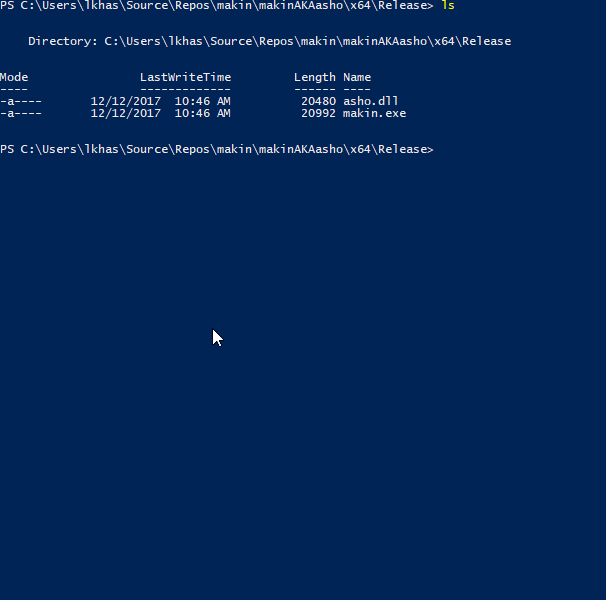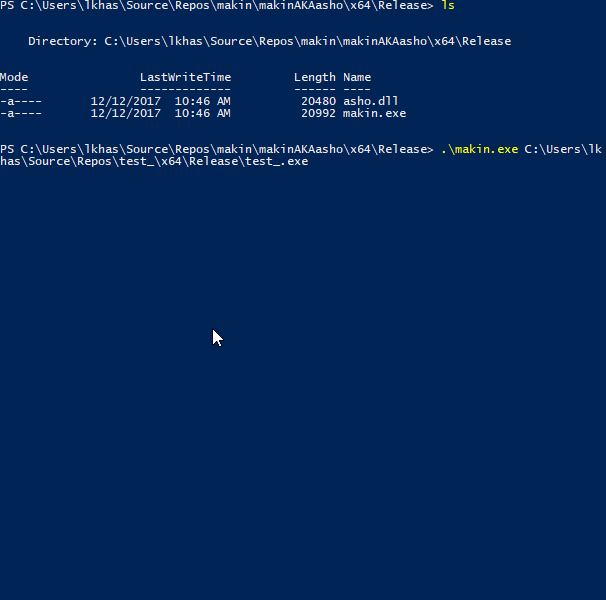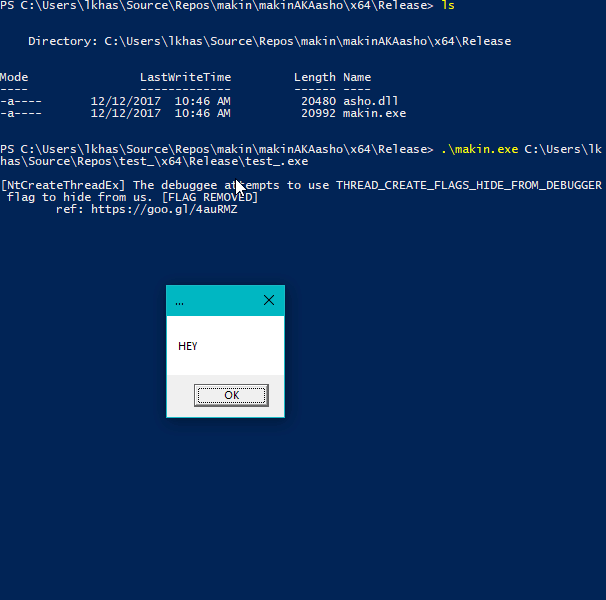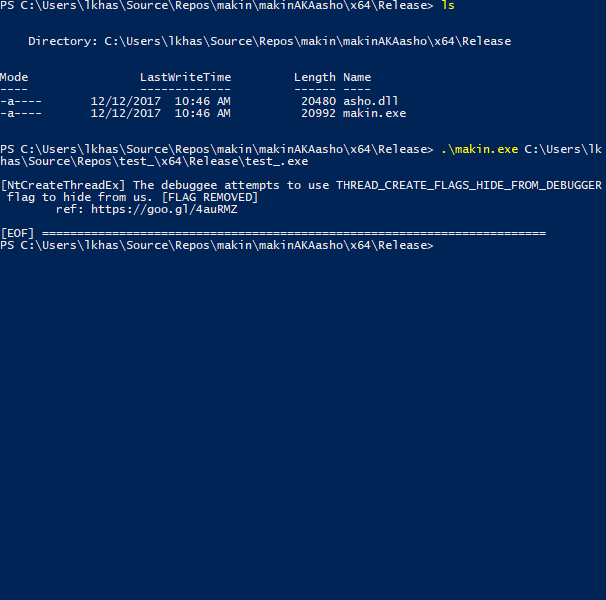
makin abre uma amostra como debuggee e injeta asho.dll (o módulo principal renomeia todas as dlls antes da injeção). asho.dll intercepta várias funções nas bibliotecas ntdll.dll e kernelbase.dll e, após verificações de parâmetros, envia a mensagem correspondente para o depurador (makin.exe).
makin também gera um script para o IDA Pro definir pontos de interrupção nas APIs detectadas.
Neste momento, makin pode revelar as seguintes técnicas:
ntdll.dll:
NtClose - ref: The "Ultimate" Anti-Debugging Reference: 7.B.iiNtOpenProcess - ref: The "Ultimate" Anti-Debugging Reference: 7.B.iNtCreateFile - ref: The "Ultimate" Anti-Debugging Reference: 7.B.iii (Open itself)NtCreateFile - ref: The "Ultimate" Anti-Debugging Reference: 7.B.iii (Open a driver)LdrLoadDll - ref: The "Ultimate" Anti-Debugging Reference: 7.B.ivNtSetDebugFilterState - ref: The "Ultimate" Anti-Debugging Reference: 7.D.viNtQueryInformationProcess - ref: The "Ultimate" Anti-Debugging Reference: 7.D.viii.a, 7.D.viii.b, 7.D.viii.cNtQuerySystemInformation - ref: The "Ultimate" Anti-Debugging Reference: 7.E.iiiNtSetInformationThread - ref: The "Ultimate" Anti-Debugging Reference 7.F.iiiNtCreateUserProcess - ref: The "Ultimate" Anti-Debugging Reference 7.G.iNtCreateThreadEx - ref: ntuery blog postNtSystemDebugControl - ref: @waleedassar - pastebinNtYieldExecution - ref: The "Ultimate" Anti-Debugging Reference 7.D.xiiiNtSetLdtEntries - ref: ANTI-UNPACKER TRICKS: PART ONE - 2.1.2NtQueryInformationThread - ref: ntquery - NtQueryInformationThreadNtCreateDebugObject and NtQueryObject - ref: Anti-Debug NtQueryObjectRtlAdjustPrivilege - ref: Using RtlAdjustPrivilege to detect debugger by insid3codeteamPEB->BeingDebugged - Em vez de chamar IsDebuggerPresent(), alguns programas verificam manualmente o PEB (Process Environment Block) pela flag BeingDebugged.PEB->NtGlobalFlag - ref: al-khaserUserSharedData->KdDebuggerEnabled - ref: al-khaser - SharedUserData_KernelDebuggerPROCTECTED handle trick - ref: al-khaser - HANDLE_FLAG_PROTECT_FROM_CLOSEkernelbase.dll:
IsDebuggerPresent - ref: MSDNCheckRemoteDebuggerPresent - ref: MSDNSetUnhandledExceptionFilter - ref: The "Ultimate" Anti-Debugging Reference: D.xvRegOpenKeyExInternalW - verifica chaves de registroRegQueryValueExW - verifica valores de chaves de registroVocê pode adicionar mais verificações de VM editando o arquivo checks.json, sem modificar o executável.
Isso é tudo por enquanto, você pode adicionar quanto quiser :)