

 dolevf/graphw00f
Ferramenta de identificação de engine de servidor GraphQL que envia consultas benignas e malformadas para identificar a tecnologia do backend e avaliar as defesas de segurança através da GraphQL Threat Matrix.
graphw00f (inspirado por wafw00f) é a ferramenta de identificação de GraphQL para endpoints GQL. Ela envia uma mistura de consultas benignas e malformadas para determinar qual engine GraphQL está sendo executado nos bastidores. graphw00f utilizará o projeto GraphQL Threat Matrix para fornecer informações sobre quais defesas de segurança cada tecnologia oferece prontas para uso, e se estão ativadas ou desativadas por padrão.
Consultas especialmente elaboradas fazem com que diferentes implementações de servidor GraphQL respondam de forma única a consultas, mutações e inscrições, o que torna trivial identificar o engine backend e distinguir entre as várias implementações GraphQL. (CWE: CWE-200)
graphw00f suporta a detecção e identificação de servidores GraphQL que utilizam consultas baseadas em GET ou POST.
Atualmente, graphw00f tenta descobrir os seguintes engines GraphQL:
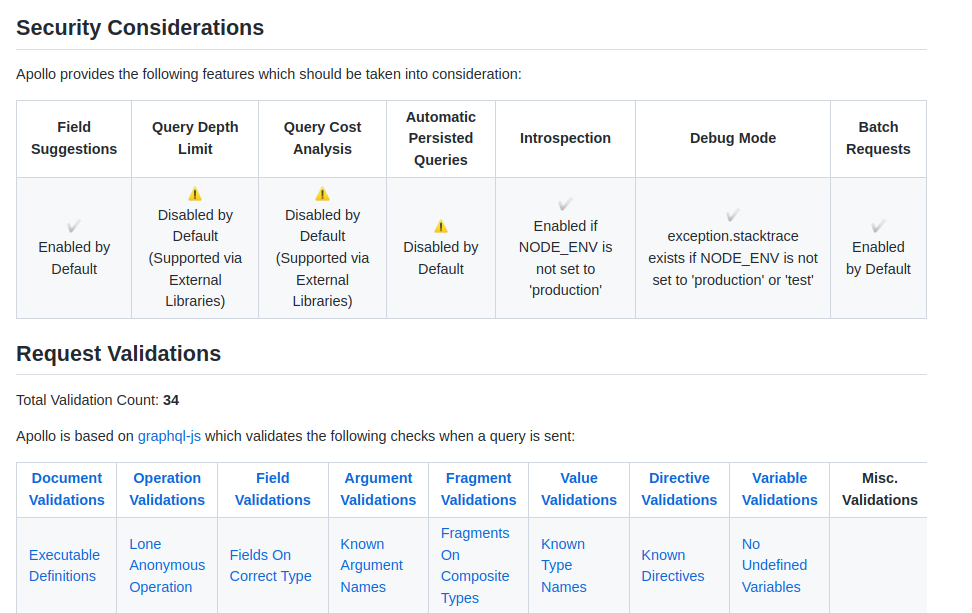
O projeto graphw00f utiliza o GraphQL Threat Matrix Project como seu banco de dados de matriz de segurança tecnológica. Quando graphw00f identifica com sucesso um endpoint GraphQL, ele imprime o documento da matriz de ameaças. Este documento ajuda engenheiros de segurança a identificar o quão madura é a tecnologia, quais recursos de segurança ela oferece e se contém algum CVE.
git clone https://github.com/dolevf/graphw00f.git
Usage: main.py -d -f -t http://example.com

Options:
  -h, --help            show this help message and exit
  -r, --noredirect      Do not follow redirections given by 3xx responses
  -t URL, --target=URL  target url with the path
  -f, --fingerprint     fingerprint mode
  -d, --detect          detect mode
  -p PROXY, --proxy=PROXY
                        HTTP(S) proxy URL in the form
                        http://user:pass@host:port
  -T TIMEOUT, --timeout=TIMEOUT
                        Request timeout in seconds
  -o OUTPUT_FILE, --output-file=OUTPUT_FILE
                        Output results to a file (CSV)
  -l, --list            List all GraphQL technologies graphw00f is able to
                        detect
  -u USERAGENT, --user-agent=USERAGENT
                        Custom user-agent to use (overrides the one from
                        headers configuration)
  -H HEADER, --header=HEADER
                        Custom headers to send (e.g. "Authorization: Bearer
                        ey...").
  -w WORDLIST, --wordlist=WORDLIST
                        Path to a list of custom GraphQL endpoints
  -v, --version         Print out the current version and exit.
Não há muitas configurações necessárias para graphw00f. Mas, se você precisar de cabeçalhos de Autorização ou Cookies para um endpoint específico, use o arquivo conf.py.
# Custom Headers
HEADERS = {'User-Agent':'graphw00f'}

# Custom Cookies
COOKIES = {"PHPSESS":"DEADBEEF"}
Usar --user-agent adiciona a chave User-Agent independentemente de o arquivo conf.py a ter; se o arquivo já tiver uma, o parâmetro de linha de comando a substitui.
Este é um exemplo de como identificar (-f) um endpoint onde a localização do GraphQL é conhecida antecipadamente (/graphql)
python3 main.py -f -t https://demo.hypergraphql.org:8484/graphql

                +-------------------+
                |     graphw00f     |
                +-------------------+
                  ***            ***
                **                  ***
              **                       **
    +--------------+              +--------------+
    |    Node X    |              |    Node Y    |
    +--------------+              +--------------+
                  ***            ***
                     **        **
                       **    **
                    +------------+
                    |   Node Z   |
                    +------------+

                graphw00f - v1.0.7
          The fingerprinting tool for GraphQL
           Dolev Farhi <[email protected]>

[*] Checking if GraphQL is available at https://demo.hypergraphql.org:8484/graphql...
[*] Found GraphQL...
[*] Attempting to fingerprint...
[*] Discovered GraphQL Engine: (HyperGraphQL)
[!] Attack Surface Matrix: https://github.com/dolevf/graphw00f/blob/main/docs/hypergraphql.md
[!] Technologies: Java
[!] Homepage: https://www.hypergraphql.org
[*] Completed.
Este é um exemplo de como graphw00f pode detectar (-d) onde o GraphQL está e então executar o processo de identificação (-f).
python3 main.py -f -d -t http://localhost:5000

                +-------------------+
                |     graphw00f     |
                +-------------------+
                  ***            ***
                **                  ***
              **                       **
    +--------------+              +--------------+
    |    Node X    |              |    Node Y    |
    +--------------+              +--------------+
                  ***            ***
                     **        **
                       **    **
                    +------------+
                    |   Node Z   |
                    +------------+

                graphw00f - v1.1.2
          The fingerprinting tool for GraphQL
           Dolev Farhi <[email protected]>

[*] Checking http://dvga.example.local:5000/graphql
[!] Found GraphQL at http://dvga.example.local:5000/graphql
[*] Attempting to fingerprint...
[*] Discovered GraphQL Engine: (Graphene)
[!] Attack Surface Matrix: https://github.com/nicholasaleks/graphql-threat-matrix/blob/master/implementations/graphene.md
[!] Technologies: Python
[!] Homepage: https://graphene-python.org
[*] Completed.
Qualquer problema com graphw00f, como falsos positivos, detecções imprecisas, bugs, etc., por favor crie uma issue no GitHub com detalhes do ambiente.
