
Skip to content
KitploitKITPLOIT
FerramentasBlog
Log in
Enviar
FerramentasBlog
Enviar

Ferramentas de Hacking, PenTest e Cibersegurança para o seu Arsenal de Segurança!

Kitploit é um diretório de ferramentas de hacking, cibersegurança e pentesting. Descubra as últimas atualizações de projetos para encontrar vulnerabilidades, analisar sistemas, automatizar testes e fortalecer sua segurança.

··Feeds·Contato·Privacidade·© 2026 Kitploit

Diretório de Ferramentas

Categorias

Ver todas as categorias
Loading categories
al-khaser — Técnicas de malware públicas utilizadas na natureza: Máquina Virtual, Emulação, Depuradores, Detecção de Sandbox. | Kitploit
Ferramentas/GitHubGitHub/ayoubfaouzi/al-khaser
Evasão de IDS/IPSAnálise de MalwareTestes de PenetraçãoAprendizado e EducaçãoRed TeamingLabs e Prática
GitHubayoubfaouzi/al-khaser

al-khaser

Técnicas de malware públicas utilizadas na natureza: Máquina Virtual, Emulação, Depuradores, Detecção de Sandbox.

Ver Repositório
7.1k1.3k26há 3 mesesRevisado pelo Kitploit

Mais Populares

Ver todos →

Descubra as ferramentas mais usadas pela nossa comunidade.

Explore todas as ferramentas

Navegue pela nossa coleção de ferramentas

Ver todas as ferramentas →
Compartilhar

Al-Khaser v0.81

Logo

Conteúdo

  • Introdução
  • Possíveis usos
  • Funcionalidades
  • Ataques anti-debugging
  • Anti-Dumping
  • Ataques de temporização
  • Interação Humana
  • Anti-VM
  • Anti-Desmontagem
  • Requisitos
  • Licença

Introdução

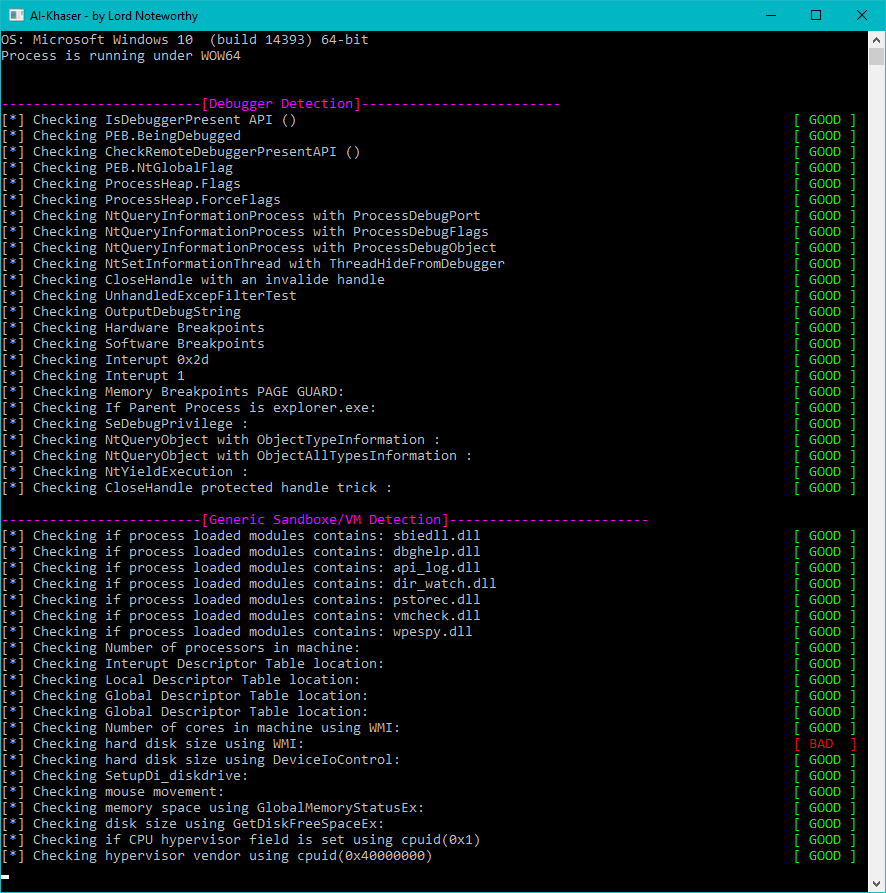
al-khaser é uma aplicação "malware" PoC com boas intenções que visa estressar seu sistema anti-malware. Ela executa uma série de truques comuns de malware com o objetivo de ver se você passa despercebido.
Logo

Uso

$ ./al-khaser.exe -h
Usage: al-khaser.exe [OPTIONS]
Options:
  --check <type>      Enable specific check(s). Can be used multiple times. Valid types are:
                        TLS              (Thread Local Storage callback checks)
                        DEBUG            (Anti-debugging checks)
                        INJECTION        (Code injection checks)
                        GEN_SANDBOX      (Generic sandbox checks)
                        VBOX             (VirtualBox detection)
                        VMWARE           (VMware detection)
                        VPC              (Virtual PC detection)
                        QEMU             (QEMU detection)
                        KVM              (KVM detection)
                        XEN              (Xen detection)
                        WINE             (Wine detection)
                        PARALLELS        (Parallels detection)
                        HYPERV           (Hyper-V detection)
                        CODE_INJECTIONS  (Additional code injection techniques)
                        TIMING_ATTACKS   (Timing/sleep-based sandbox evasion)
                        DUMPING_CHECK    (Dumping memory/process checks)
                        ANALYSIS_TOOLS   (Analysis tools detection)
                        ANTI_DISASSM     (Anti-disassembly checks)
  --sleep <seconds>   Set sleep/delay duration in seconds (default: 600).
  --delay <seconds>   Alias for --sleep.
  -h, --help          Show this help message and exit.

Examples:
  al-khaser.exe --check DEBUG --check TIMING_ATTACKS --sleep 30
  al-khaser.exe --check VMWARE --check QEMU
  al-khaser.exe --sleep 30

Download

Você pode baixar os binários compilados (x86, x64) na página de releases deste projeto. A senha dos arquivos 7z pode ser encontrada aqui.

Possíveis usos

  • Você está criando um plugin anti-debug e deseja verificar sua eficácia.
  • Você quer garantir que sua solução de sandbox esteja suficientemente oculta.
  • Ou você quer garantir que seu ambiente de análise de malware esteja bem oculto.

Por favor, se você encontrar algum dos truques anti-análise que já viu em um malware, não hesite em contribuir.

Funcionalidades

Ataques anti-debugging

  • IsDebuggerPresent
  • CheckRemoteDebuggerPresent
  • Process Environment Block (BeingDebugged)
  • Process Environment Block (NtGlobalFlag)
  • ProcessHeap (Flags)
  • ProcessHeap (ForceFlags)
  • Low Fragmentation Heap (LFH)
  • NtQueryInformationProcess (ProcessDebugPort)
  • NtQueryInformationProcess (ProcessDebugFlags)
  • NtQueryInformationProcess (ProcessDebugObject)
  • WudfIsAnyDebuggerPresent
  • WudfIsKernelDebuggerPresent
  • WudfIsUserDebuggerPresent
  • NtSetInformationThread (HideThreadFromDebugger)
  • NtQueryObject (ObjectTypeInformation)
  • NtQueryObject (ObjectAllTypesInformation)
  • CloseHanlde (NtClose) Invalide Handle
  • SetHandleInformation (Protected Handle)
  • UnhandledExceptionFilter
  • OutputDebugString (GetLastError())
  • Hardware Breakpoints (SEH / GetThreadContext)
  • Software Breakpoints (INT3 / 0xCC)
  • Memory Breakpoints (PAGE_GUARD)
  • Interrupt 0x2d
  • Interrupt 1
  • Trap Flag
  • Parent Process (Explorer.exe)
  • SeDebugPrivilege (Csrss.exe)
  • NtYieldExecution / SwitchToThread
  • TLS callbacks
  • Process jobs
  • Memory write watching
  • Page exception breakpoint detection
  • API hook detection (module bounds based)

Anti-injeção

  • Enumerate modules with EnumProcessModulesEx (32-bit, 64-bit, and all options)
  • Enumerate modules with ToolHelp32
  • Enumerate the process LDR structures with LdrEnumerateLoadedModules
  • Enumerate the process LDR structures directly
  • Walk memory with GetModuleInformation
  • Walk memory for hidden modules

Anti-Dumping

  • Erase PE header from memory
  • SizeOfImage

Ataques de temporização [Anti-Sandbox]

  • RDTSC (with CPUID to force a VM Exit)
  • RDTSC (Locky version with GetProcessHeap & CloseHandle)
  • Sleep -> SleepEx -> NtDelayExecution
  • Sleep (in a loop a small delay)
  • Sleep and check if time was accelerated (GetTickCount)
  • SetTimer (Standard Windows Timers)
  • timeSetEvent (Multimedia Timers)
  • WaitForSingleObject -> WaitForSingleObjectEx -> NtWaitForSingleObject
  • WaitForMultipleObjects -> WaitForMultipleObjectsEx -> NtWaitForMultipleObjects
  • IcmpSendEcho (CCleaner Malware)
  • CreateWaitableTimer
  • CreateTimerQueueTimer
  • Big crypto loops (todo)

Interação Humana / Genérico [Anti-Sandbox]

  • Mouse movement
  • File names like sample.exe or sandbox.exe.
  • Total Physical memory (GlobalMemoryStatusEx)
  • Disk size using DeviceIoControl (IOCTL_DISK_GET_LENGTH_INFO)
  • Disk size using GetDiskFreeSpaceEx (TotalNumberOfBytes)
  • Mouse (Single click / Double click) (todo)
  • DialogBox (todo)
  • Scrolling (todo)
  • Execution after reboot (todo)
  • Count of processors (Win32/Tinba - Win32/Dyre)
  • Sandbox known product IDs (todo)
  • Color of background pixel (todo)
  • Keyboard layout (Win32/Banload) (todo)
  • Genuine Windows installation.
  • Known Sandbox hostnames and usernames
Baixar ferramenta