 0xdsm/juumla
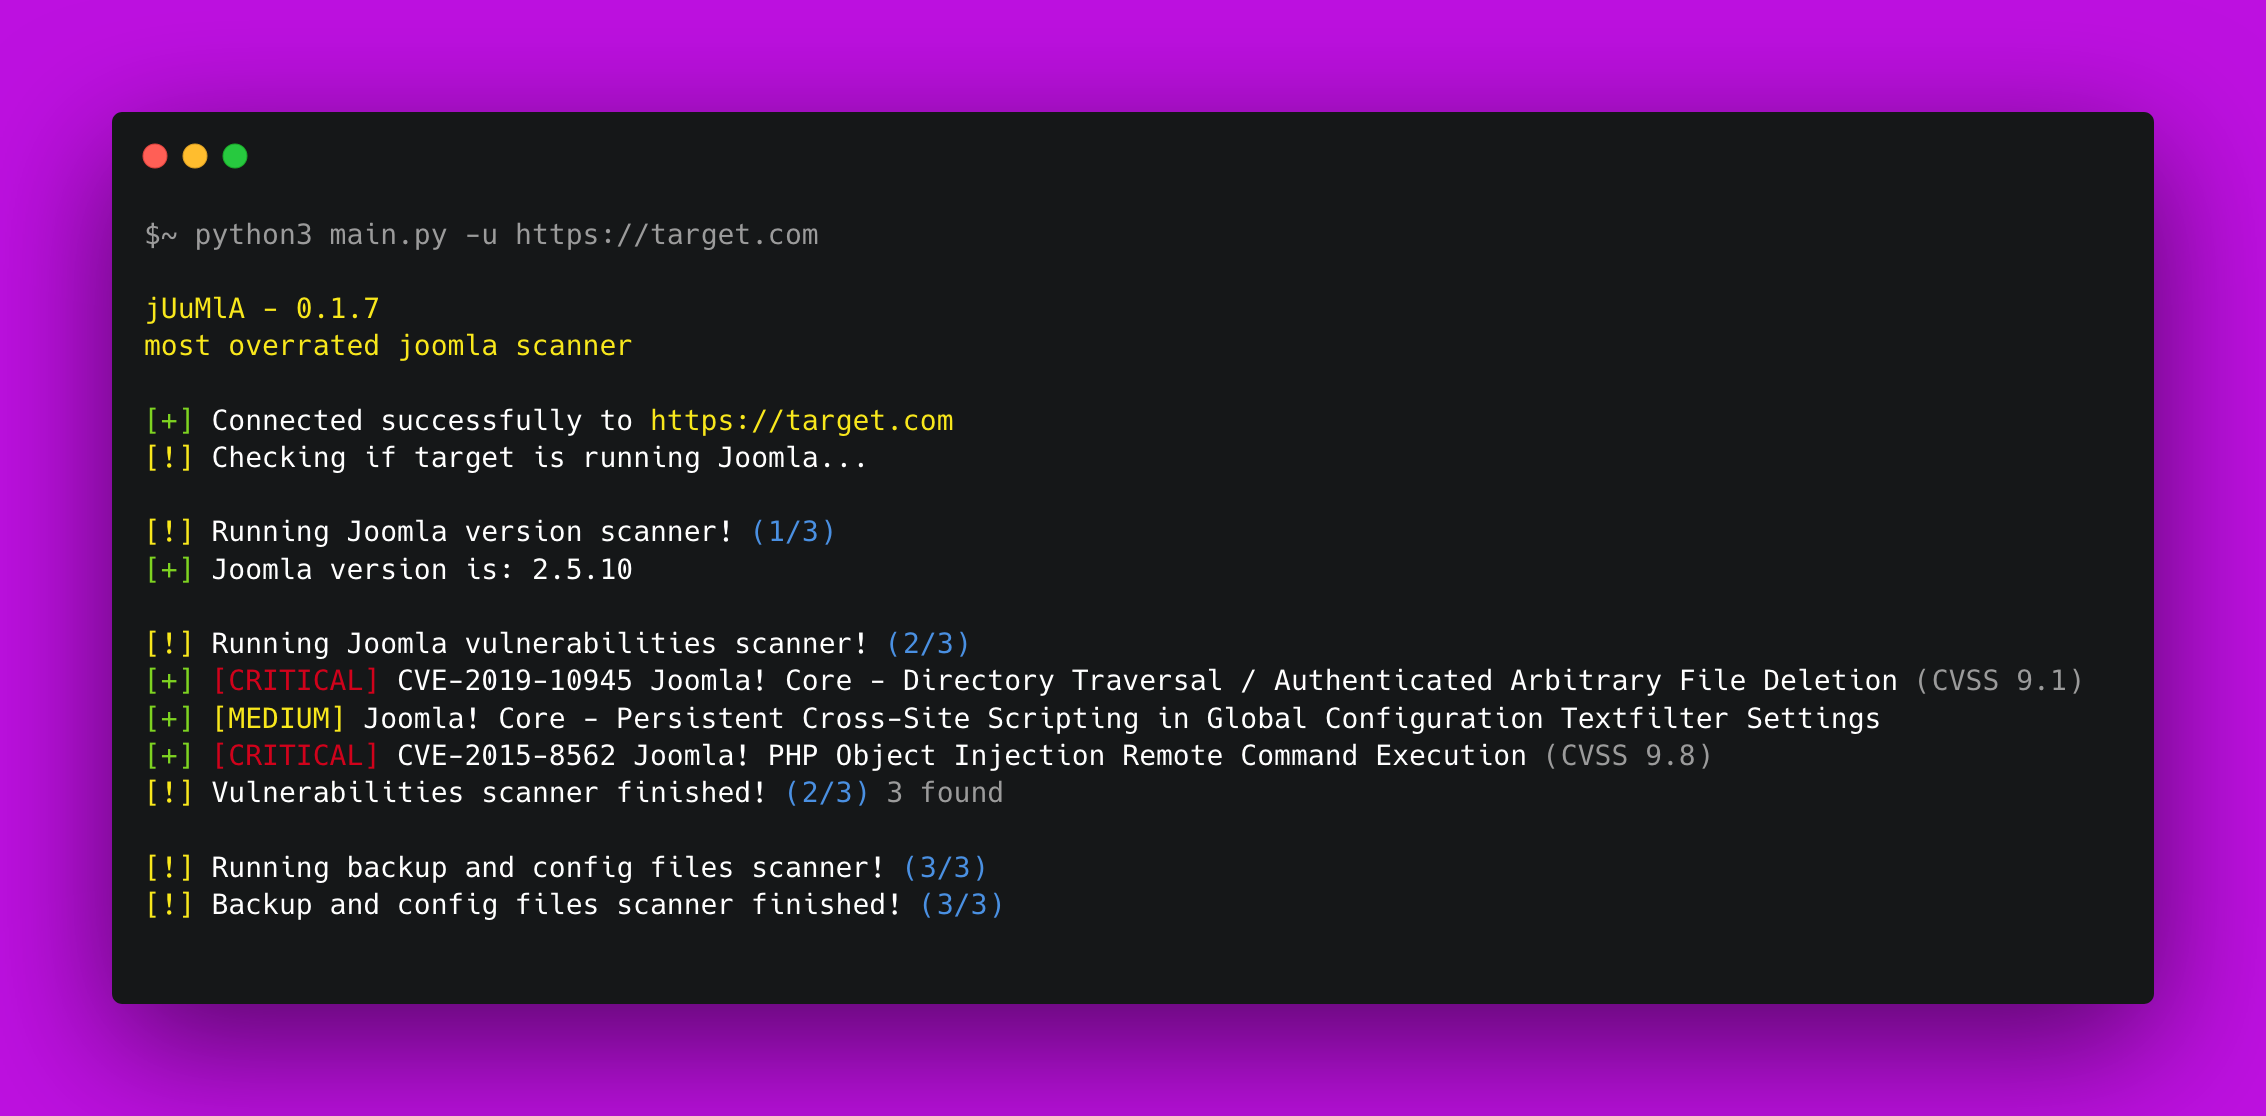
🦁 Projeto em Python para identificar e verificar vulnerabilidades relacionadas ao projeto Joomla CMS. Ele verifica configurações incorretas comuns e vulnerabilidades públicas.

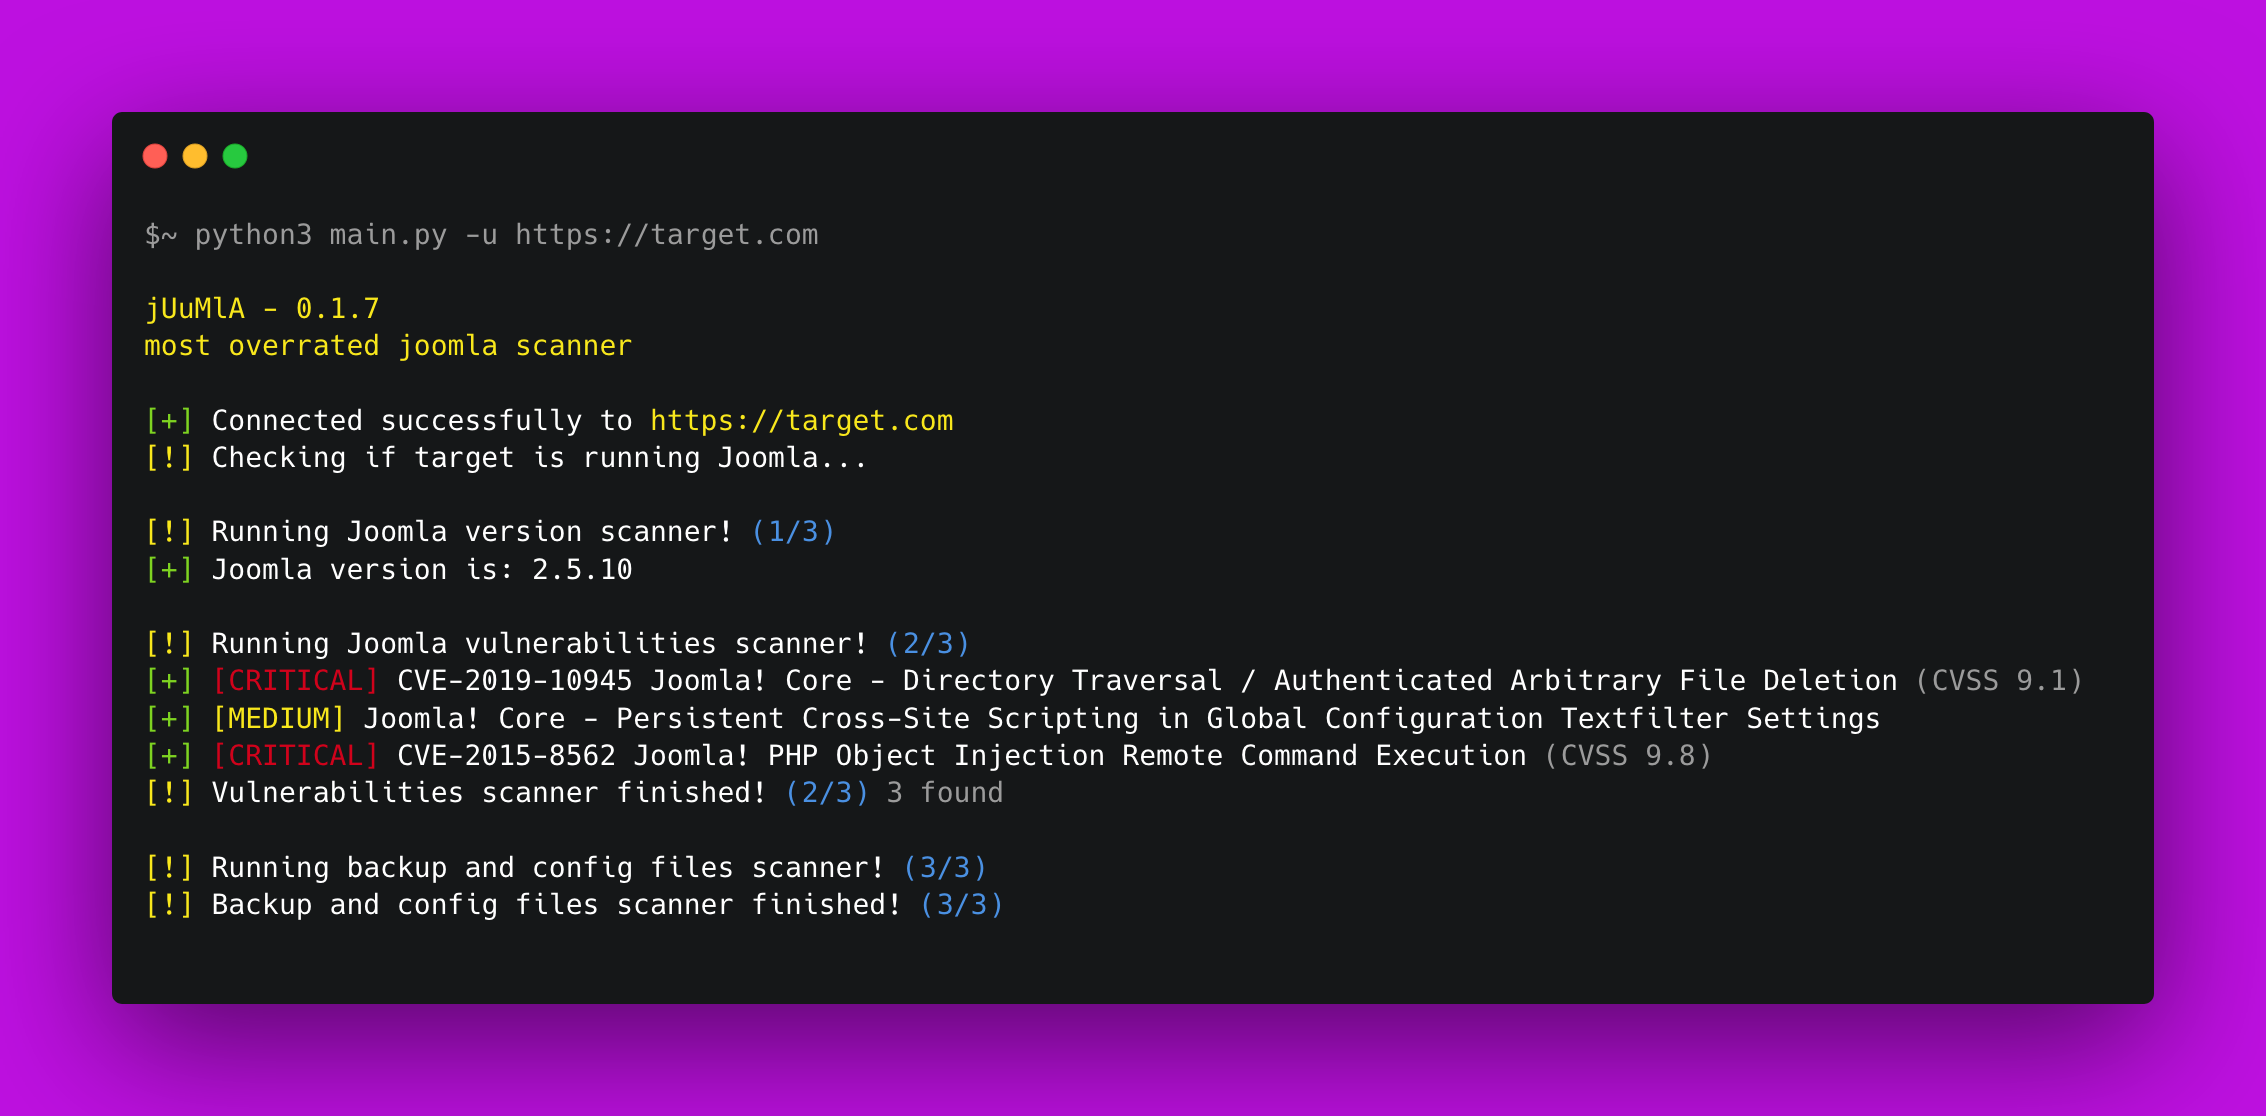


🦁 Juumla Juumla é uma ferramenta Python criada para identificar a versão do Joomla, escanear vulnerabilidades e arquivos sensíveis.
Um guia rápido sobre como instalar e usar o Juumla.
1. Clone the repository - git clone https://github.com/oppsec/juumla.git
2. Install the libraries - pip3 install -r requirements.txt
3. Run Juumla - python3 main.py -u https://example.com
Se você quiser executar o Juumla em um contêiner Docker, siga estes comandos:
1. Clone the repository - git clone https://github.com/oppsec/juumla.git
2. Build the image - sudo docker build -t juumla:latest .
3. Run container - sudo docker run juumla:latest
Se você quiser criar um ambiente Joomla em um contêiner Docker, siga estes comandos:
1. Clone the repository - git clone https://github.com/oppsec/juumla.git (or download the docker-compose.yml file)
2. Install docker-compose (e.g: sudo apt install docker-compose)
3. sudo docker-compose up
4. Access http://localhost:8080/

The default root password is: example
The default database name is: joomladb
The default DBMS is: MySQL 5.6
pip3 install -r requirements.txtUm guia rápido sobre como contribuir para o projeto.
1. Create a fork from Juumla repository
2. Download the project with git clone https://github.com/your/juumla.git
3. Make your changes
4. Commit and makes a git push
5. Open a pull request

