 x90skysn3k/brutespray
Fast, multi-protocol credential brute-forcer. Parses Nmap, Nessus, and Nexpose output to automatically test default and custom credentials across 30+ protocols.



Created by: Shane Young/@x90sky && Jacob Robles/@shellfail
Inspired by: Leon Johnson/@sho-luv
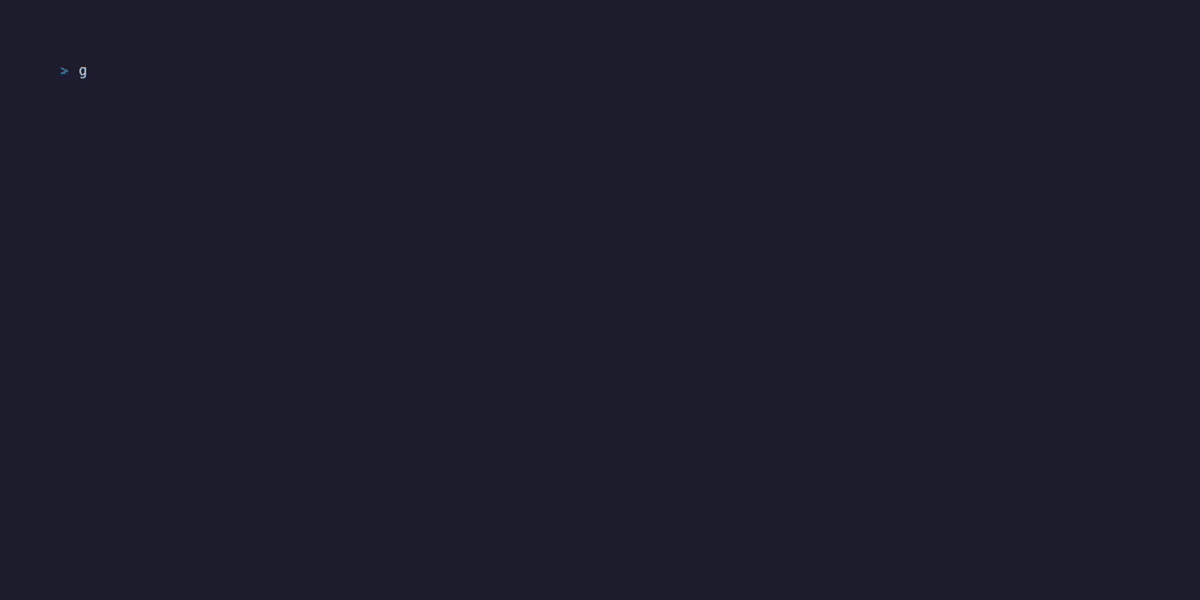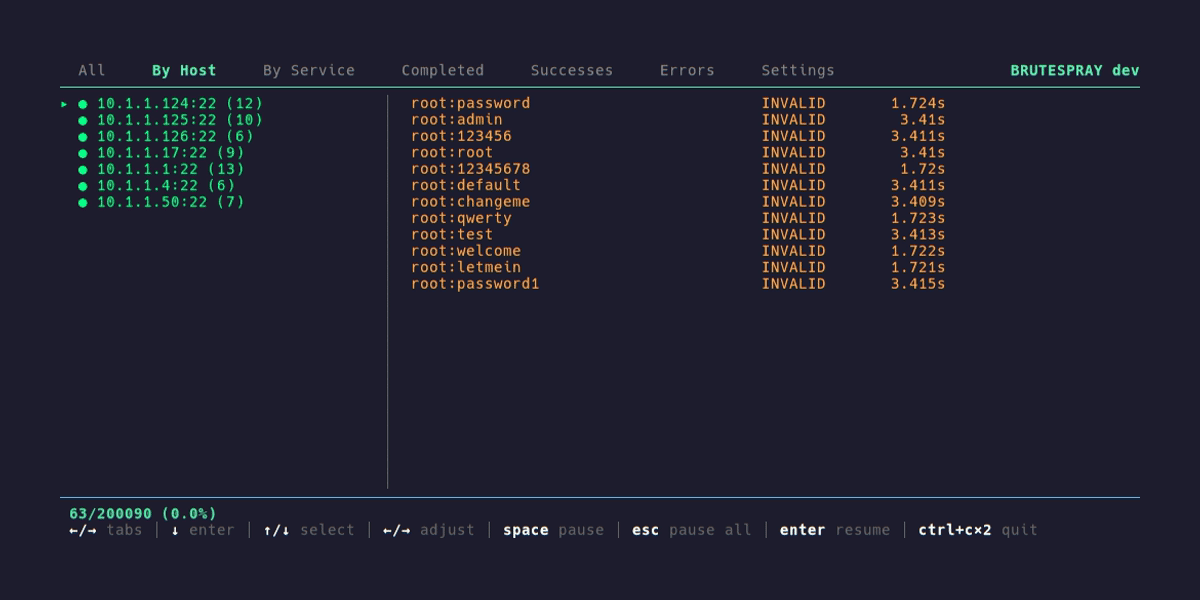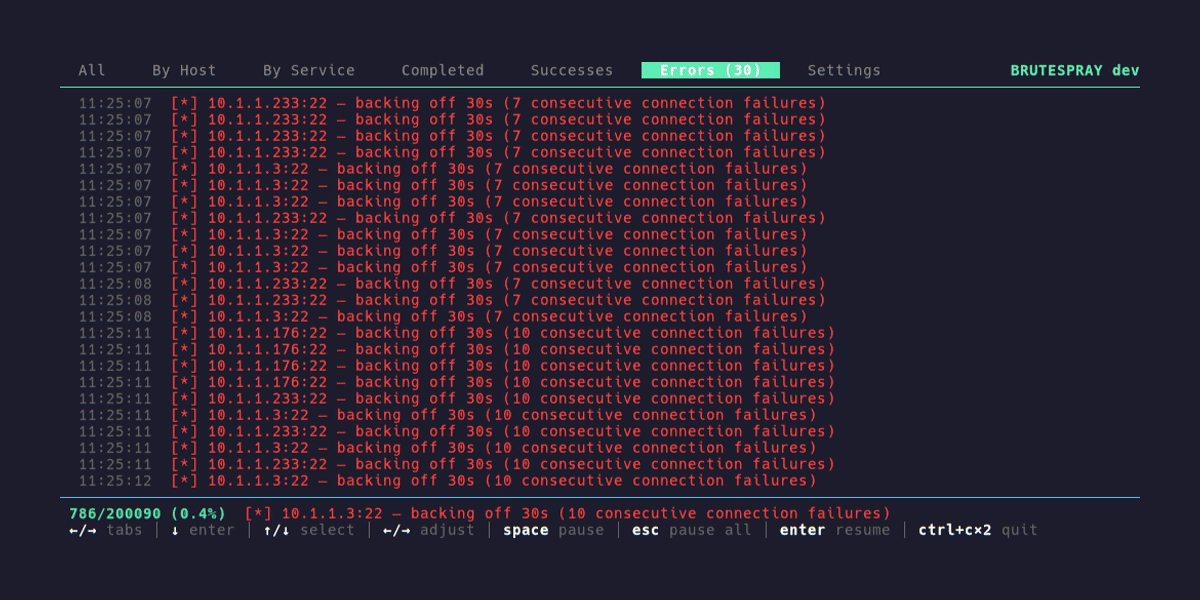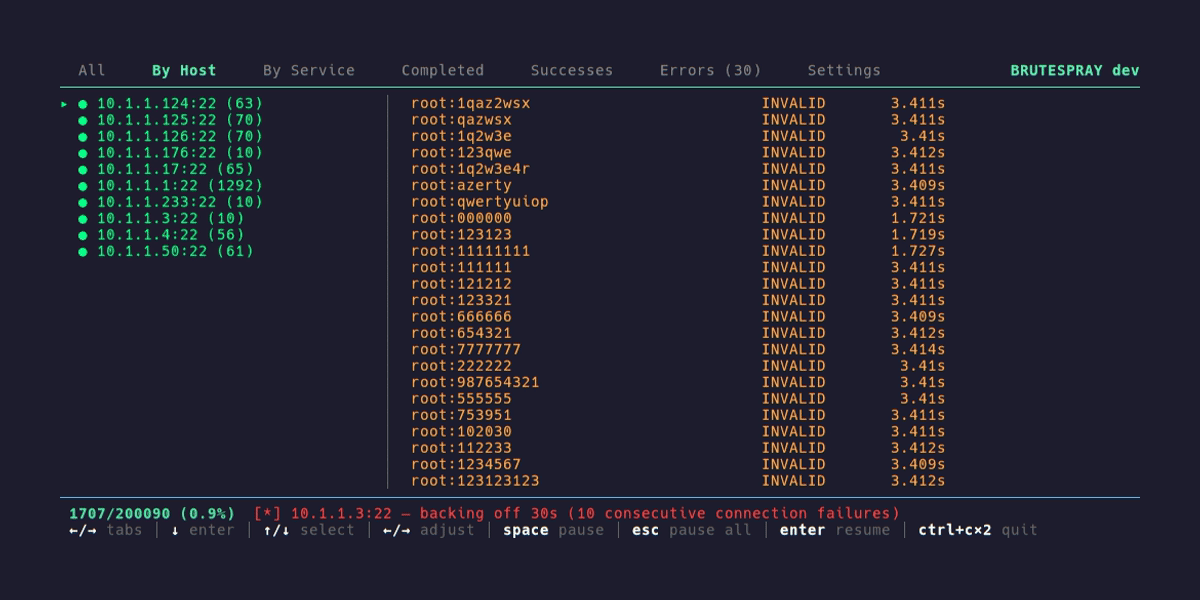
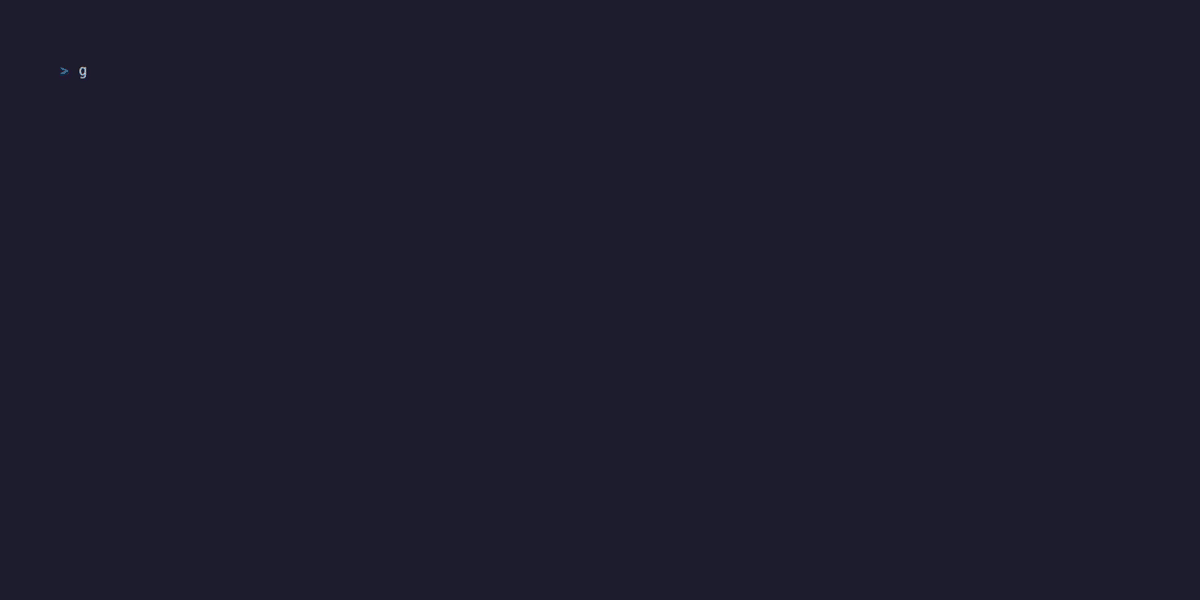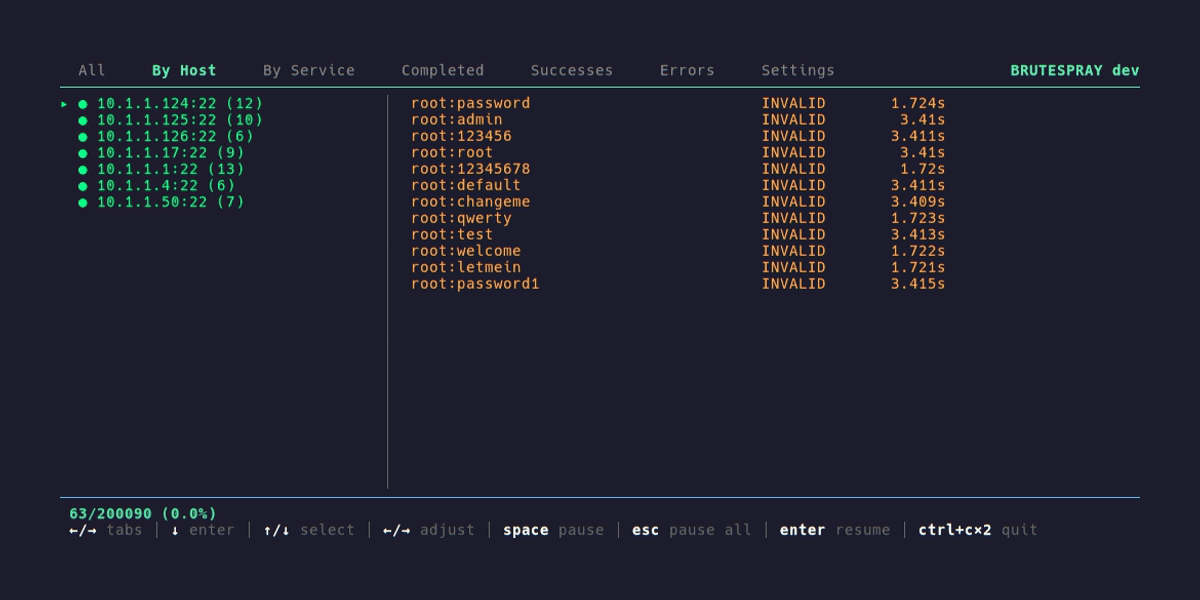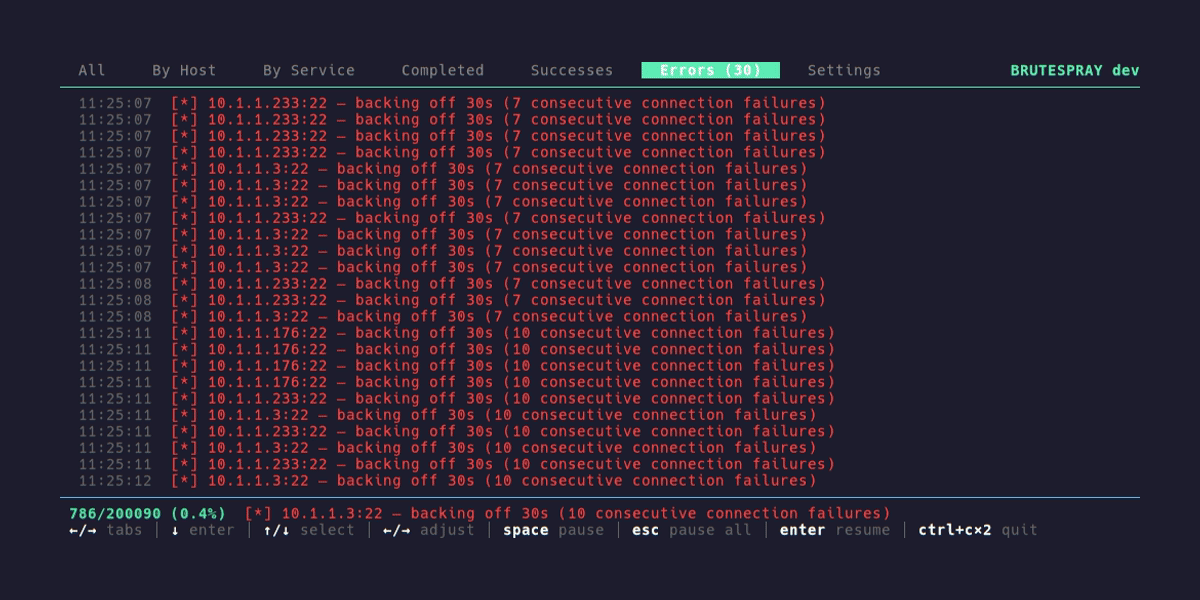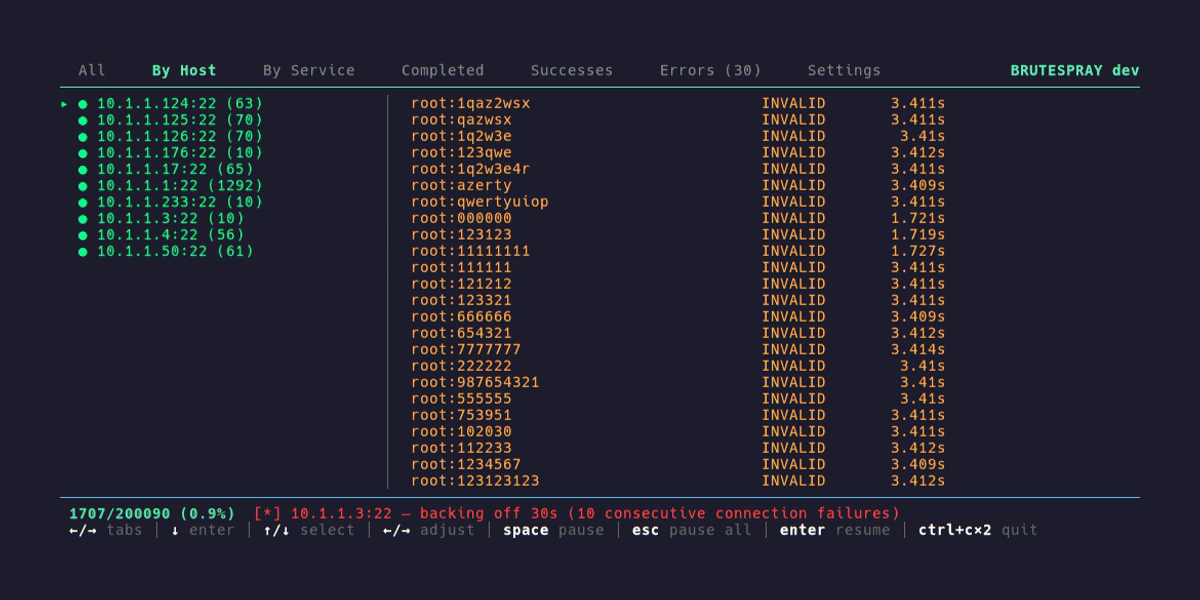
Brutespray automatically attempts default credentials on discovered services. It takes scan output from Nmap (GNMAP/XML), Nessus, Nexpose, JSON, and lists, then brute-forces credentials across 40+ protocols in parallel. Built in Go with an interactive terminal UI, embedded wordlists, and resume capability.
go install github.com/x90skysn3k/brutespray/v2@latest
Release Binaries | Build from Source | Docker
# From Nmap scan output
brutespray -f nmap.gnmap -u admin -p password

# Target a specific host
brutespray -H ssh://192.168.1.1:22 -u admin -p passlist.txt

# CIDR range
brutespray -H ssh://10.1.1.0/24:22 -u root -p passlist.txt

# Combo credentials
brutespray -H ssh://10.0.0.1:22 -C root:root
See all examples for more usage patterns.
-m KEY:VALUE (auth type, target path, NTLM domain, etc.)| Feature | brutespray | hydra | medusa | ncrack | brutus |
|---|---|---|---|---|---|
| Single static binary | ✅ | ❌ | ❌ | ❌ | ✅ |
| Interactive TUI | ✅ | ❌ | ❌ | ❌ | ❌ |
| Checkpoint / resume | ✅ | ❌ | ❌ | ✅ | ❌ |
| Spray mode (lockout-aware) | ✅ | ❌ | ❌ | ❌ | ❌ |
| Per-attempt JSONL output | ✅ | ⚠️ | ❌ | ❌ | ❌ (success-only) |
| SOCKS5 + proxy rotation | ✅ | ⚠️ | ❌ | ❌ | ❌ |
| Embedded SSH bad-keys (CVE-tagged) | ✅ | ❌ | ❌ | ❌ | ✅ |
| Pipeline stdin (naabu / fingerprintx / masscan) | ✅ | ❌ | ❌ | ❌ | ✅ |
| Pre-auth RDP recon (NLA / sticky-keys) | ✅ | ❌ | ❌ | ❌ | ✅ |
| Nmap/Masscan gnmap + XML / Nessus / Nexpose import | ✅ | ⚠️ | ❌ | ❌ | ⚠️ (nmap only) |
Per-module params (-m KEY:VAL) | ✅ | ❌ | ❌ | ❌ | partial |
| Service count | 41 | 50+ | 34 | 14 | 23 |
Symbols reflect documented behavior at PR time. Competing tools change quickly.
ssh ftp ftps telnet smtp smtp-vrfy imap pop3 mysql postgres mssql mongodb redis vnc snmp smbnt rdp http https vmauthd teamspeak asterisk nntp oracle xmpp ldap ldaps winrm rexec rlogin rsh wrapper
Full details and service-specific notes: docs/services.md
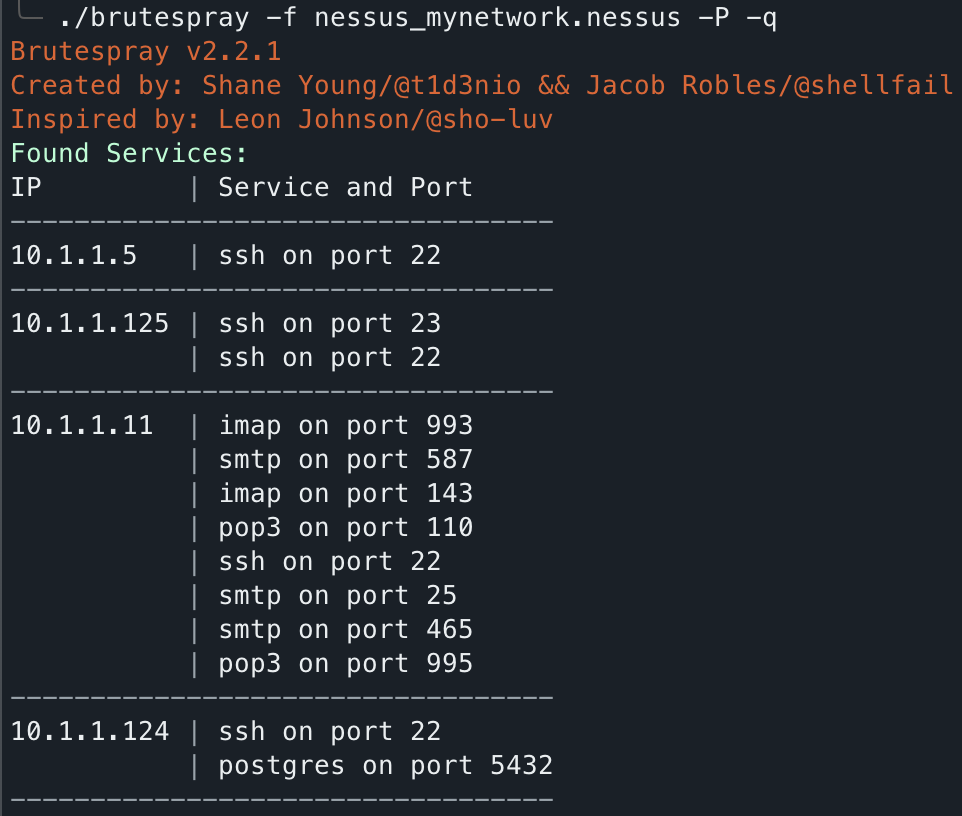
Print discovered services from a scan file with -P -q:
| Guide | Description |
|---|---|
| Installation | Go install, release binaries, build from source, Docker |
| Usage | CLI flags, config files, input formats |
| Services | All 40+ protocols with ports, status, and notes |
| Examples | Common usage patterns and recipes |
| Interactive TUI | Keybindings, tabs, Findings, live settings |
| Advanced | Spray mode, proxy, resume, performance tuning |
| Wordlists | Manifest system, layers, overrides, customization |
| Output & Reporting | Summary reports, Metasploit/NetExec integration |








