Python 対応:
OS 対応:
WSS: 開発モード中!!!

index of" inurl:wp-content/                      7,370,000 results
inurl:"/wp-content/plugins/wp-shopping-cart/"    281,000 results
inurl:wp-content/plugins/wp-dbmanager/"          11,000 results
WSS はブラックボックスの WordPress 脆弱性スキャナーで、リモートの WordPress インストールをスキャンしてセキュリティ問題を発見します。専門の IT や専門家を購入できないすべての企業に推奨されます!


$ git clone https://github.com/nu11secur1ty/WSS.git wss
$ cd wss
$ pip3 install -r requirements.txt
$ python wss.py
python3 wss.py --url https://www.xxxxxxx.com --verbose
[ + ] Target: http://localhost/wordpress/
[ + ] Starting: 07:23:02

[ + ] Server: Apache/2.4.58 (Win64) OpenSSL/3.1.3 PHP/8.2.12
[ i ] Checking Full Path Disclosure...
[ i ] Checking wp-config backup file...
[ + ] wp-config.php available at: http://localhost/wordpress/wp-config.php
[ i ] Checking common files...
[ + ] LICENSE.txt file was found at: http://localhost/wordpress/LICENSE.txt
[ + ] readme.html file was found at: http://localhost/wordpress/readme.html
[ i ] Checking directory listing...
[ + ] Dir "/wp-admin/css" listing enable at: http://localhost/wordpress/wp-admin/css/
[ + ] Dir "/wp-admin/images" listing enable at: http://localhost/wordpress/wp-admin/images/
[ + ] Dir "/wp-admin/includes" listing enable at: http://localhost/wordpress/wp-admin/includes/
[ + ] Dir "/wp-admin/js" listing enable at: http://localhost/wordpress/wp-admin/js/
[ + ] Dir "/wp-content/uploads" listing enable at: http://localhost/wordpress/wp-content/uploads/
[ + ] Dir "/wp-includes/" listing enable at: http://localhost/wordpress/wp-includes/
[ + ] Dir "/wp-includes/js" listing enable at: http://localhost/wordpress/wp-includes/js/
[ + ] Dir "/wp-includes/Text" listing enable at: http://localhost/wordpress/wp-includes/Text/
[ + ] Dir "/wp-includes/css" listing enable at: http://localhost/wordpress/wp-includes/css/
[ + ] Dir "/wp-includes/images" listing enable at: http://localhost/wordpress/wp-includes/images/
[ + ] Dir "/wp-includes/pomo" listing enable at: http://localhost/wordpress/wp-includes/pomo/
[ + ] Dir "/wp-includes/theme-compat" listing enable at: http://localhost/wordpress/wp-includes/theme-compat/
[ i ] Checking wp-loging protection...
[ i ] Checking robots paths...
[ i ] Checking WordPress version...
[ + ] Running WordPress version: 6.7.1

[ i ] Passive enumeration themes...
[ + ] Name: twentytwentyfour
[ i ] Checking themes changelog...
[ i ] Checking themes full path disclosure...
[ i ] Checking themes license...
[ i ] Checking themes readme...
[ i ] Checking themes directory listing...
[ i ] Checking theme vulnerabilities...
  |   Not found vulnerabilities

[ i ] Passive enumeration plugins...
[ + ] Not found plugins with passive enumeration
[ i ] Enumerating users...
-------------------------
| ID | Username | Login |
-------------------------
|  0 | admin    | admin |
|  1 |          | admin |
-------------------------
python3 wss.py --url https://www.xxxxxxx.com --brute --user test --wordlist wordlist.txt --verbose
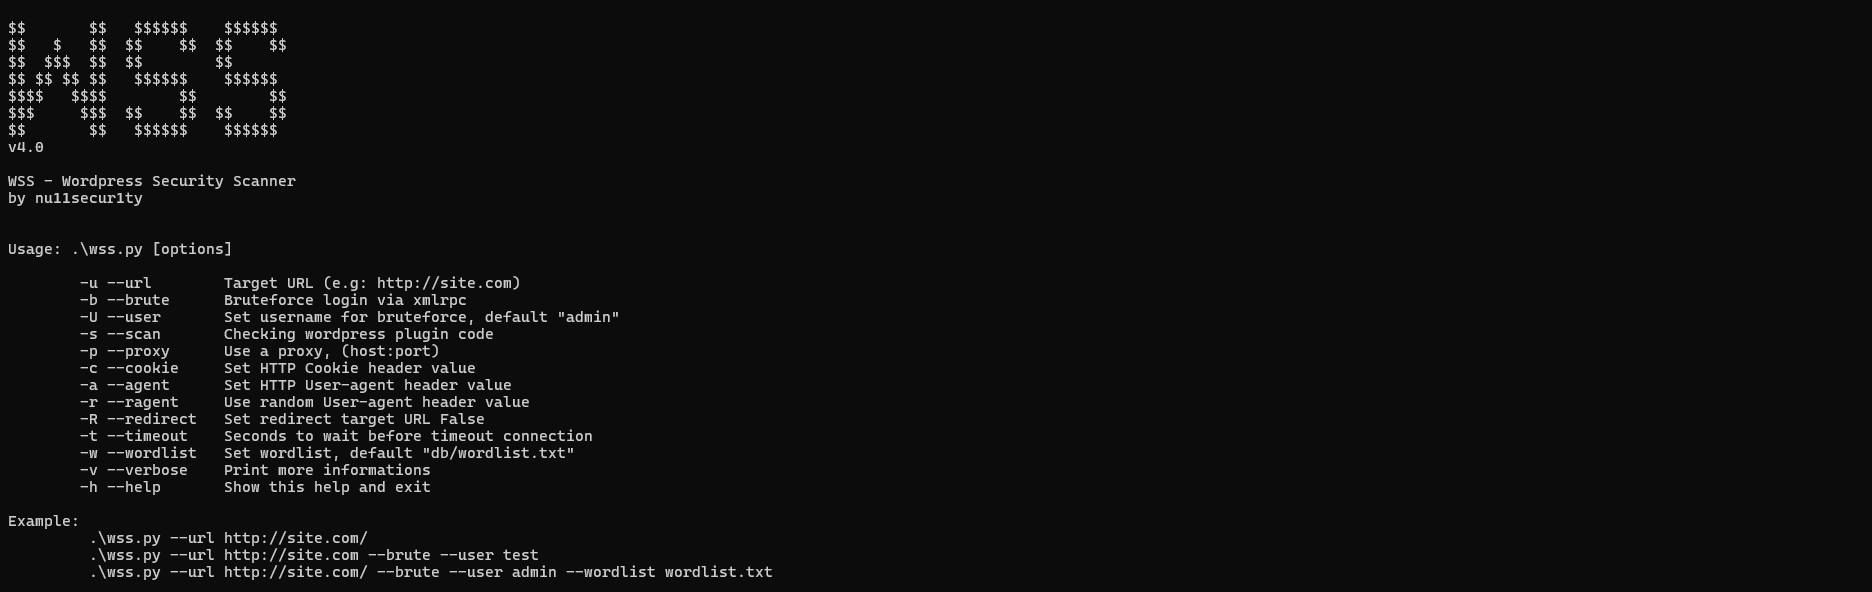
$$       $$   $$$$$$    $$$$$$
$$   $   $$  $$    $$  $$    $$
$$  $$$  $$  $$        $$
$$ $$ $$ $$   $$$$$$    $$$$$$
$$$$   $$$$        $$        $$
$$$     $$$  $$    $$  $$    $$
$$       $$   $$$$$$    $$$$$$
v4.0

WSS - Wordpress Security Scanner
by nu11secur1ty


[ + ] Target: http://localhost/wordpress/
[ + ] Starting: 07:25:58

[ + ] Brute Forcing Login via XMLRPC...When you see any valid credentials press Ctrl + C to exit.
[ i ] Setting user: admin
[ + ] Valid Credentials:

-----------------------
| Username | Passowrd |
-----------------------
| admin    | password |
-----------------------
python3 wss.py --scan <dir/file> --verbose
注記: Akismet ディレクトリプラグインのテスト https://plugins.svn.wordpress.org/akismet
----------------------------------------
$$       $$   $$$$$$    $$$$$$
$$   $   $$  $$    $$  $$    $$
$$  $$$  $$  $$        $$
$$ $$ $$ $$   $$$$$$    $$$$$$
$$$$   $$$$        $$        $$
$$$     $$$  $$    $$  $$    $$
$$       $$   $$$$$$    $$$$$$
v4.0

WSS - Wordpress Security Scanner
by nu11secur1ty
----------------------------------------