「自分の nginx は HTTP/2 RCE のペアに晒されているか?」を 0.06 秒で答えます — コマンド 1 つ、ネットワーク呼び出しゼロ、依存関係ゼロ。
標準ライブラリのみを使った Python CLI で、ホストが CVE-2026-123007 と CVE-2026-123633 に晒されているかを決める 2 つの要素、すなわち nginx のバージョンと、設定で HTTP/2 が有効になっているかどうかをチェックします。実際のチェックは中央値 0.062 秒(7 回実行、2026-11-19 にこのマシンで計測)— アドバイザリのページを開くより速いです。ペイロードなし、ネットワークスキャンなし、エクスプロイトコードなし:防御的なチェッカーだけです。
2026-11-18、Wiz、Ikotas Labs、Metnir、Rapid7、Xint は nginx の HTTP/2 処理における 2 つの未認証リモートコード実行脆弱性を公表しました — CVE-2026-123007(HTTP/2 フロー制御における整数アンダーフロー)と CVE-2026-123633(プロキシ接続における HTTP/2 の use-after-free)です。どちらも CVSS 4.0 9.2(CVSS 3.1 8.1)で、nginx.org は 123007 を「major」、123633 を「medium」と評価しています。この話題は **2026-11-19 に Hacker News の 1 位(約 1,152 ポイント)**に達し、nginx は 2 億 2,500 万以上のウェブサイトを支えています — つまりパッチ適用の猶予は週単位ではなく時間単位で測られます。
以下の情報源から確認できたこと:
http2 off はこの 2 件に対する暫定措置であり、アップグレードの代替ではありません。情報源:Wiz の解説記事 · deploybase の解説 · IFIN アドバイザリ概要 · nginx.org セキュリティアドバイザリ
git clone https://github.com/Mahgal/nginx-http2-rce-check.git
cd nginx-http2-rce-check
python3 nginx_http2_check.py              # check this machine
pip install は不要、依存関係もなし — Python 3 だけで動作します。nginx をインストールせずに試すこともできます:
python3 nginx_http2_check.py --demo      # labelled fixtures: 1 vulnerable, 1 patched
python3 nginx_http2_check.py --version 1.31.8 --config examples/nginx-http2-on.conf
python3 nginx_http2_check.py --version 1.30.7 --config examples/nginx-http2-on.conf
python3 nginx_http2_check.py --nginx-path examples/fake-nginx-vulnerable.sh --config examples/nginx-http2-on.conf
python3 nginx_http2_check.py --json      # machine-readable output for CI
クリーンなコピー(/tmp での新規チェックアウト、2026-11-19)で検証済み: --demo は実行され、テストスイート全体が合格、40/40、終了コード 0。
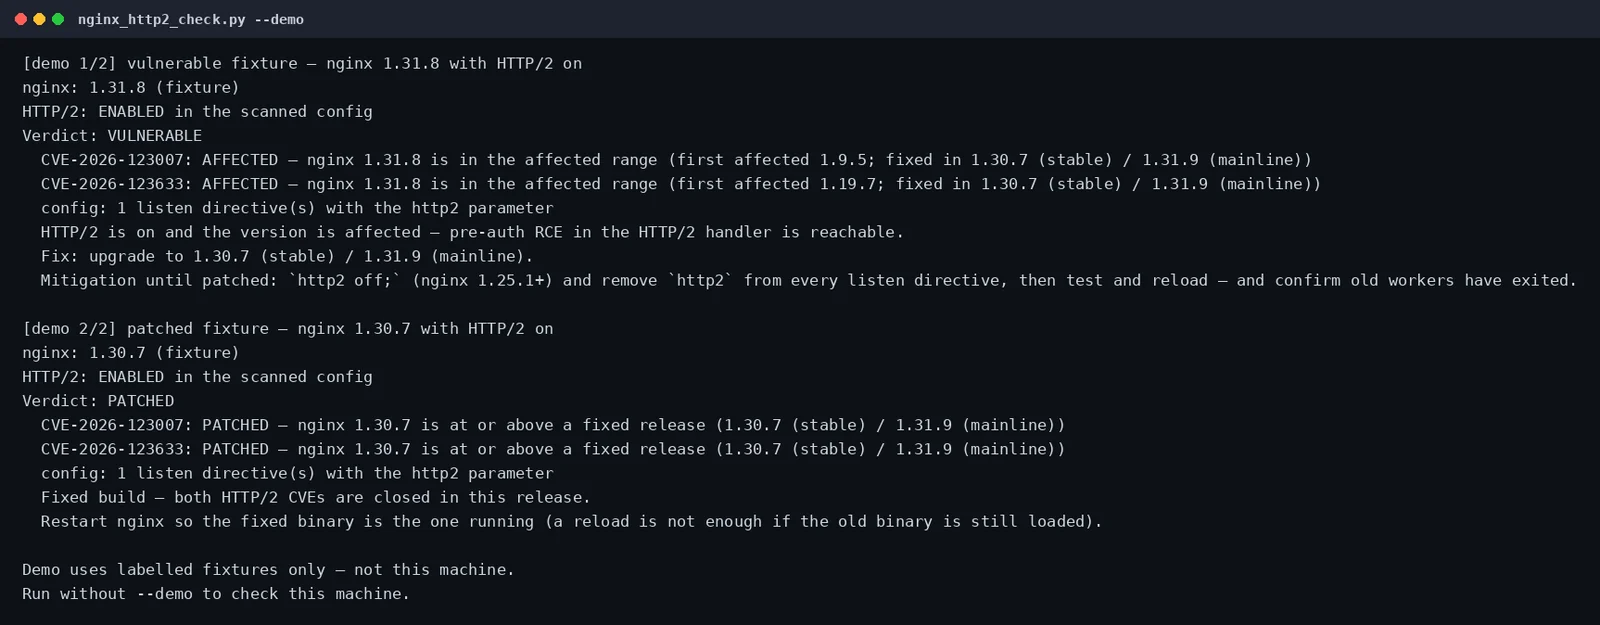
python3 nginx_http2_check.py --demo の実際の出力(demo.txt にそのままキャプチャ済み。再実行してもバイト単位で同一の結果が再現され、sha256 は e6a50babb87a98a704b802b3bbab6d5db6da256b45a45b9628ab1a930eae7f27):
[demo 1/2] vulnerable fixture — nginx 1.31.8 with HTTP/2 on
nginx: 1.31.8 (fixture)
HTTP/2: ENABLED in the scanned config
Verdict: VULNERABLE
  CVE-2026-123007: AFFECTED — nginx 1.31.8 is in the affected range (first affected 1.9.5; fixed in 1.30.7 (stable) / 1.31.9 (mainline))
  CVE-2026-123633: AFFECTED — nginx 1.31.8 is in the affected range (first affected 1.19.7; fixed in 1.30.7 (stable) / 1.31.9 (mainline))
  config: 1 listen directive(s) with the http2 parameter
  HTTP/2 is on and the version is affected — pre-auth RCE in the HTTP/2 handler is reachable.
  Fix: upgrade to 1.30.7 (stable) / 1.31.9 (mainline).
  Mitigation until patched: `http2 off;` (nginx 1.25.1+) and remove `http2` from every listen directive, then test and reload — and confirm old workers have exited.

[demo 2/2] patched fixture — nginx 1.30.7 with HTTP/2 on
nginx: 1.30.7 (fixture)
HTTP/2: ENABLED in the scanned config
Verdict: PATCHED
  CVE-2026-123007: PATCHED — nginx 1.30.7 is at or above a fixed release (1.30.7 (stable) / 1.31.9 (mainline))
  CVE-2026-123633: PATCHED — nginx 1.30.7 is at or above a fixed release (1.30.7 (stable) / 1.31.9 (mainline))
  config: 1 listen directive(s) with the http2 parameter
  Fixed build — both HTTP/2 CVEs are closed in this release.
  Restart nginx so the fixed binary is the one running (a reload is not enough if the old binary is still loaded).

Demo uses labelled fixtures only — not this machine.
Run without --demo to check this machine.
実際のフラグに対する同じケース:
$ python3 nginx_http2_check.py --version 1.31.8 --config examples/nginx-http2-on.conf
Verdict: VULNERABLE        # exit 1 — HTTP/2 on, version affected
$ python3 nginx_http2_check.py --version 1.30.7 --config examples/nginx-http2-on.conf
Verdict: PATCHED           # exit 0 — same config, fixed build
$ python3 nginx_http2_check.py --version 1.31.8 --config examples/nginx-http2-off.conf
Verdict: NOT_AFFECTED      # exit 0 — HTTP/2 off closes both flaws
$ python3 nginx_http2_check.py --version 1.24.0-0ubuntu1 --config examples/nginx-http2-on.conf
Verdict: UNKNOWN           # exit 3 — distro package: version string says nothing
1.30.7 は修正済みですが、1.31.0~1.31.8 は依然として脆弱です。 素朴なチェック——「バージョンが 1.30.7 以上なら安全」——では、1.31.8 を安全と判定してしまいます。しかし実際は安全ではありません。このツールは明示的なブランチごとの範囲と比較し、単純な数値しきい値を使うことはありません:
| バージョン | CVE-2026-123007 | CVE-2026-123633 |
|---|---|---|
| < 1.9.5 | 影響なし | 影響なし |
| 1.9.5 – 1.19.6 | 影響あり | 影響なし |
| 1.19.7 – 1.30.6 | 影響あり | 影響あり |
| 1.30.7 (stable 修正) | 修正済み | 修正済み |
| 1.31.0 – 1.31.8 | 影響あり | 影響あり |
| 1.31.9+ / 1.32.0+ (mainline 修正) | 修正済み | 修正済み |
| 判定 | 意味 |
|---|---|
VULNERABLE | バージョンが影響範囲内にあり、かつスキャンした設定で HTTP/2 が有効になっています。今すぐアップグレードしてください。 |
PATCHED | バージョンが修正版リリース以上です。修正済みバイナリが実際に動作するよう nginx を再起動してください。 |
NOT_AFFECTED | バージョンが両方の脆弱性より前であるか、スキャンした設定で HTTP/2 が無効になっています。 |
UNKNOWN | nginx が見つからない、バージョン文字列を解析できない、ビルドがディストリビューションのパッケージである (下記参照)、Plus のトレインに公開された修正がない、またはバージョンが影響を受ける状態で HTTP/2 の状態を判定できなかった、のいずれかです。安全だと決めつけないでください。 |
| コード | 意味 |
|---|---|
0 | PATCHED または NOT_AFFECTED |
1 | VULNERABLE — 設計上、CI ゲートとして機能するようにしています |
2 | 使用エラー (不正なフラグ、読み取れない --nginx-path / --config パス) |
3 | UNKNOWN (このツール独自のコード — 判定を参照) |
| 製品 | CVE-2026-123007 | CVE-2026-123633 |
|---|---|---|
| NGINX OSS | 1.9.5 – 1.31.8 | 1.19.7 – 1.31.8 |
| 修正済み (OSS) | 1.30.7 stable / 1.31.9 mainline | 1.30.7 stable / 1.31.9 mainline |
| NGINX Plus | R33+ | R33+ |
| 修正済み (Plus) | 37.0.8.1 / 37.3.0.1 | 37.0.7.1 / 37.2.0.1 |
| Plus、修正なし | R33–R36 (37.x トレインに移行) | R33–R36 (37.x トレインに移行) |
37.0.8.1 と 37.3.0.1 は両方の CVE を修正します。37.0.7.1 と 37.2.0.1 は 123633 のみを修正し、123007 に対しては依然として脆弱です。37.1 トレインにはどちらの CVE に対する公開された修正もなく、UNKNOWN と報告されます。
1.24.0 のようなバージョン文字列は、ディストリビューションのパッケージ由来であれば、どちらの意味も持ちません。 Debian、Ubuntu、Alpine などは古いバージョン番号にセキュリティ修正をバックポートするため、nginx/1.24.0-0ubuntu1 はすでに修正済みかもしれませんし、そうでないかもしれません。このツールは推測を拒否します: パッケージのサフィックス (-0ubuntu1、~deb12u1、-1、(Ubuntu)) を含むバージョン文字列は、説明とお使いのディストリビューションの CVE トラッカーへの参照を添えて UNKNOWN と報告されます。トラッカーを確認するか、アップストリームのビルド (1.30.7 / 1.31.9) をインストールして再実行してください。
http2 off; (nginx 1.25.1+) およびすべての listen ディレクティブから http2 を削除し、テスト、リロードして、古いワーカーが終了したことを確認してください。