
高速モジュラーWebインターフェースブルートフォーサー
python3 -m pip install -r requirements.txt
$ python3 web-brutator.py -h

 __      __      ___.            __________                __          __
/  \    /  \ ____\_ |__          \______   \_______ __ ___/  |______ _/  |_  ___________
\   \/   // __ \| __ \   ______ |    |  _/\_  __ \  |  \   __\__  \   __\ /  _ \_  _ _\
 \        /\  ___/| \_\ \ /_____/ |    |   \ |  | \/  |  /|  |  / __ \|  | (  <_> )  | \/
  \__/\  /  \___  >___  /         |______  / |__|  |____/ |__| (____  /__|  \____/|__|
       \/       \/    \/                 \/                         \/
                                                                        Version 0.2

usage: web-brutator.py [-h] [--url URL] [--target TYPE] [-u USERNAME]
                       [-U USERLIST] [-p PASSWORD] [-P PASSLIST]
                       [-C COMBOLIST] [-t THREADS] [-s] [-v] [-e MAX_ERRORS]
                       [--timeout TIMEOUT] [-l]

optional arguments:
  -h, --help                   show this help message and exit
  --url URL                    Target URL
  --target TYPE                Target type
  -u, --username USERNAME      Single username
  -U, --userlist USERLIST      Usernames list
  -p, --password PASSWORD      Single password
  -P, --passlist PASSLIST      Passwords list
  -C, --combolist COMBOLIST    Combos username:password list
  -t, --threads THREADS        Number of threads [1-50] (default: 10)
  -s, --stoponsuccess          Stop on success
  -v, --verbose                Print every tested creds
  -e, --max-errors MAX_ERRORS  Number of accepted consecutive errors (default: 10)
  --timeout TIMEOUT            Time limit on the response (default: 20s)
  -l, --list-modules           Display list of modules
例:
python3 web-brutator.py --target jenkins --url https://mytarget.com -U ./usernames.txt -P ./passwords.txt -s -t 40
注意:一部の製品では、デフォルトで一定回数の認証失敗後にアカウントロックアウトが実装されています(例:Weblogic、Tomcat...)。
web-brutatorはブルートフォース攻撃の開始時に該当する場合にユーザーに通知します。そのようなターゲットに対してブルートフォースを開始する前に、これを考慮に入れてください。
web-brutatorは標準のWeb認証フォームを自動的に検出し、自動的にブルートフォースを実行できます。
この機能はstandardformモジュールで利用可能ですが、まだ実験的であり、複数のヒューリスティックに基づいているため、誤検出/見逃しが発生する可能性があります。
サポートされていません:
例:
python3 web-brutator.py --target standardform --url https://mytarget.com -U ./usernames.txt -P ./passwords.txt -s -t 40 -v
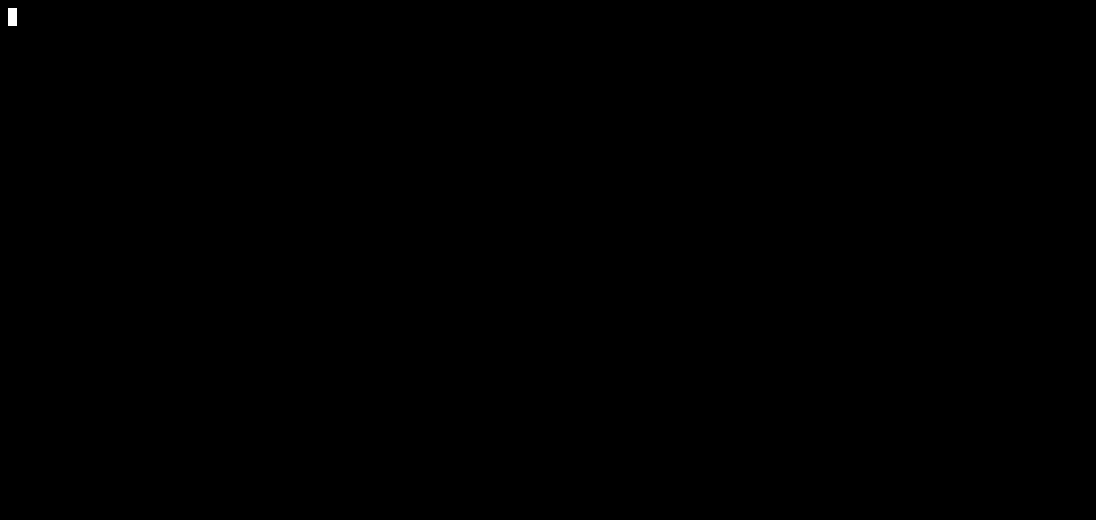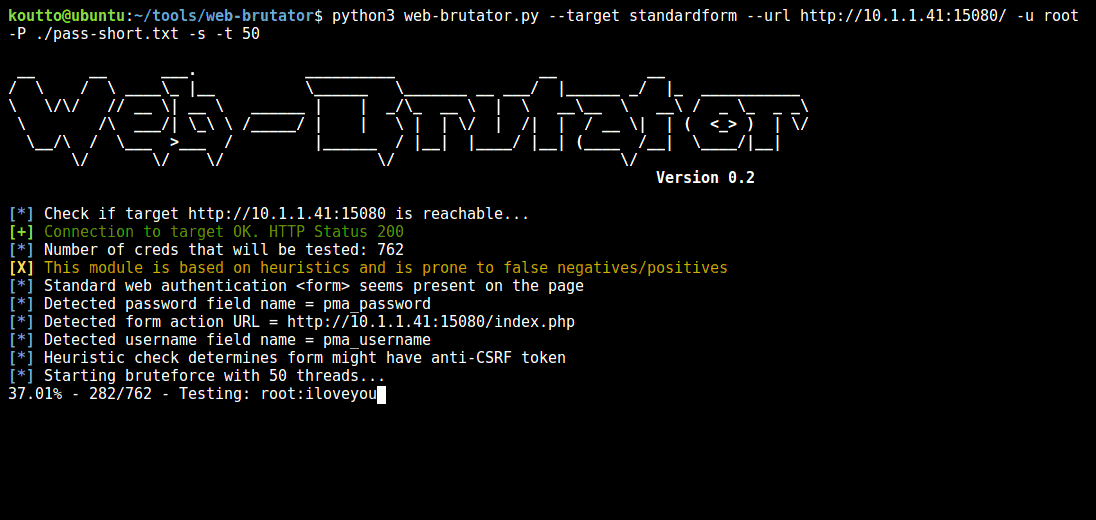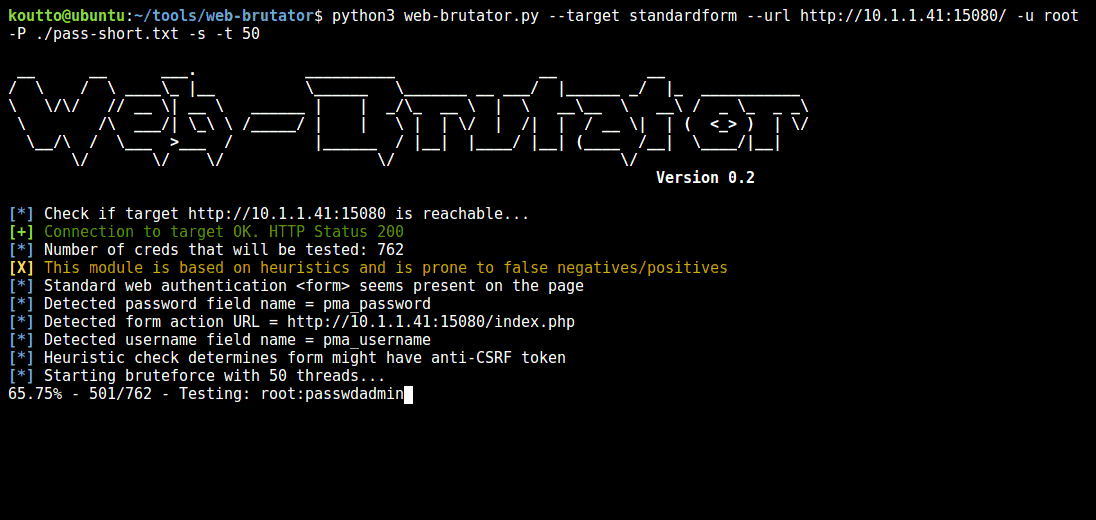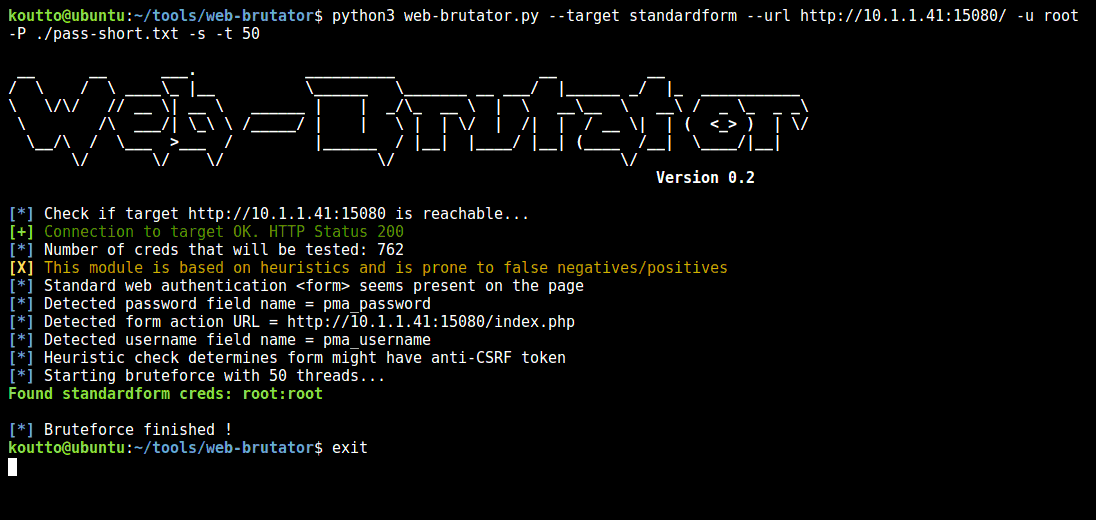 このデモはphpMyAdminインターフェースに対するものです
新しい認証ブルートフォースモジュールの追加は非常に簡単です:
lib/core/modules/の下に適切な名前の新しいファイルを作成します。lib/core/modules/の下にある既存のモジュールを例として確認してください。HTTPリクエストはRequesterクラスが提供する静的メソッド(Requester.get()、Requester.post()、Requester.http_auth())を介して行う必要があることに注意してください。#!/usr/bin/env python3
# -*- coding: utf-8 -*-
from lib.core.Exceptions import AuthException, RequestException
from lib.core.Logger import logger
from lib.core.Requester import AuthMode, Requester
class Mymodule:
def __init__(self, url, verbose=False):
self.url = url
# Other self variables can go here
def check(self):
"""
This method is used to detect the presence of the targeted authentication
interface.
:return: Boolean indicating if the authentication interface has been detected
"""
# Implement code here
def try_auth(self, username, password):
"""
This method is used to perform one authentication attempt.
:param str username: Username to check
:param str password: Password to check
:return: Boolean indicating authentication status
:raise AuthException:
"""
# Implement code here
-lオプションで確認)。






